written · keys for issuing and validating an X.509 certificate
Public Key Infrastructure
Why PKI is needed (can you trust a public key?), digital certificates (X.509), the certificate life cycle and revocation lists, the PKI players (CA, RA, repositories), certificate policy, and certificates in SSL/TLS. Final 221 B asked where to find revoked certificates and which keys sign and validate an X.509 certificate.
How to read this page
Every original slide is shown unchanged. Yellow marks on a slide point to a numbered note: hover or tap a mark to jump to its note, and hover a note to see its marks. Questions tagged Past exam appeared on a real paper; Prediction questions are likely angles, not confirmed. Pick an answer to each question: a wrong pick tells you why it is wrong, so you can try again.
All 19 slides
- 1 Public Key Infrastructure
- 2 Agenda
- 3 Multiple Security Issues
- 4 The Critical Questions
- 5 Slide 5
- 6 Digital Certificates
- 7 Slide 7
- 8 Digital Certificates
- 9 Three states for cert. • In use
- 10 Certificate Revocation Lists
- 11 DC in reality
- 12 PKI Players
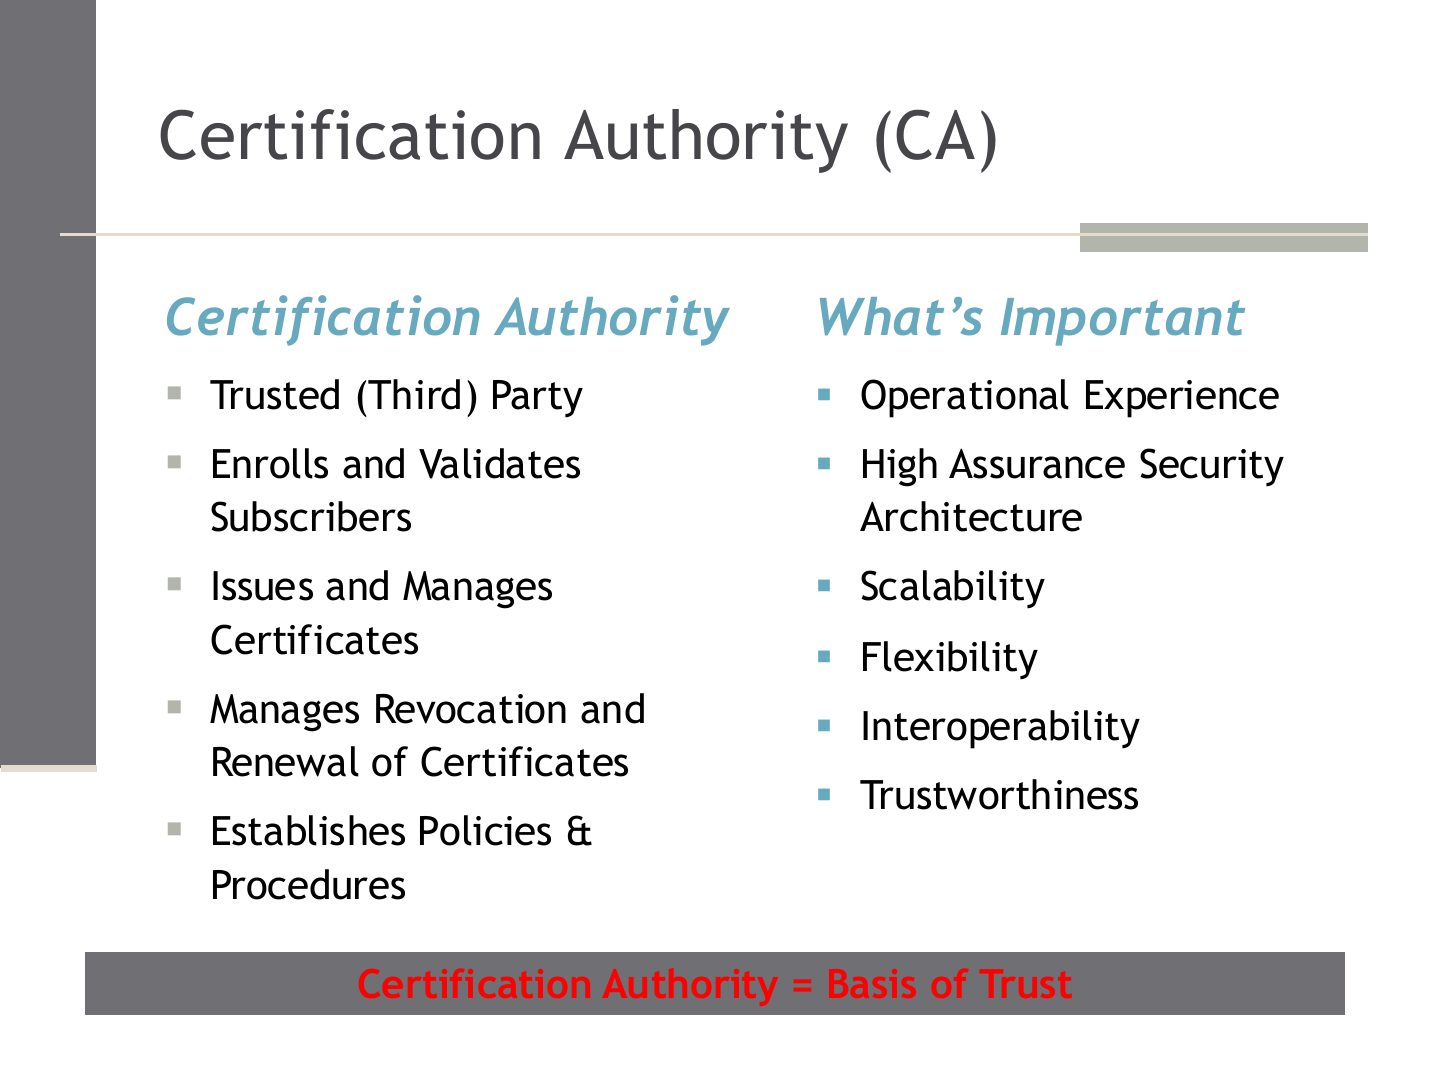
- 13 Certification Authority (CA)
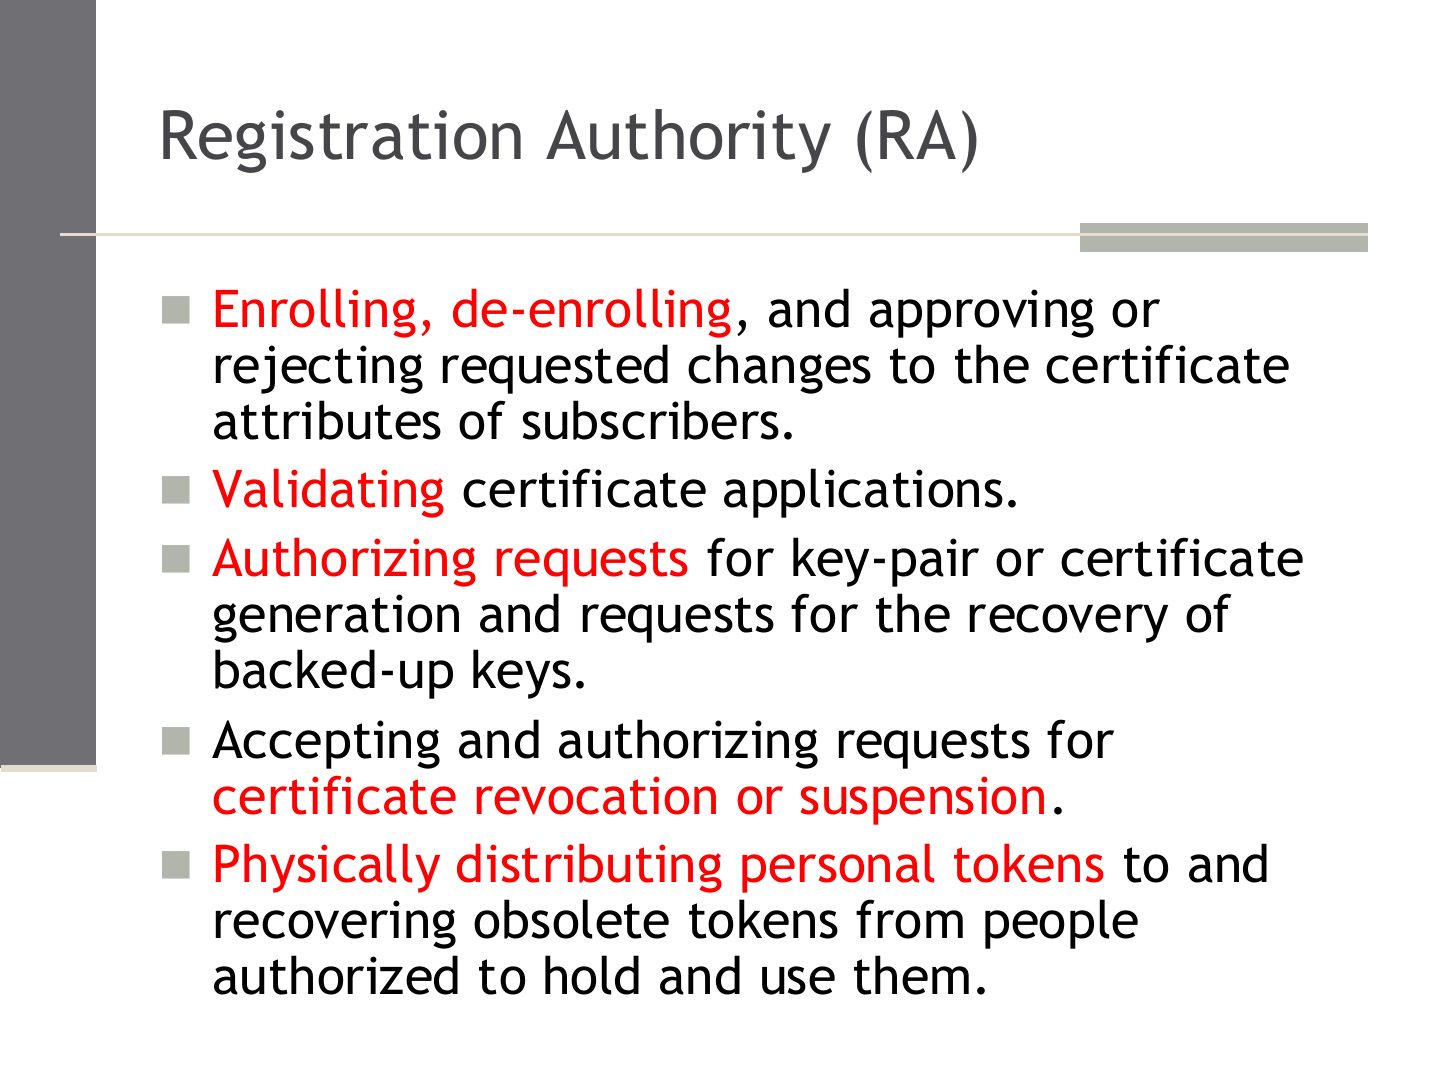
- 14 Registration Authority (RA)
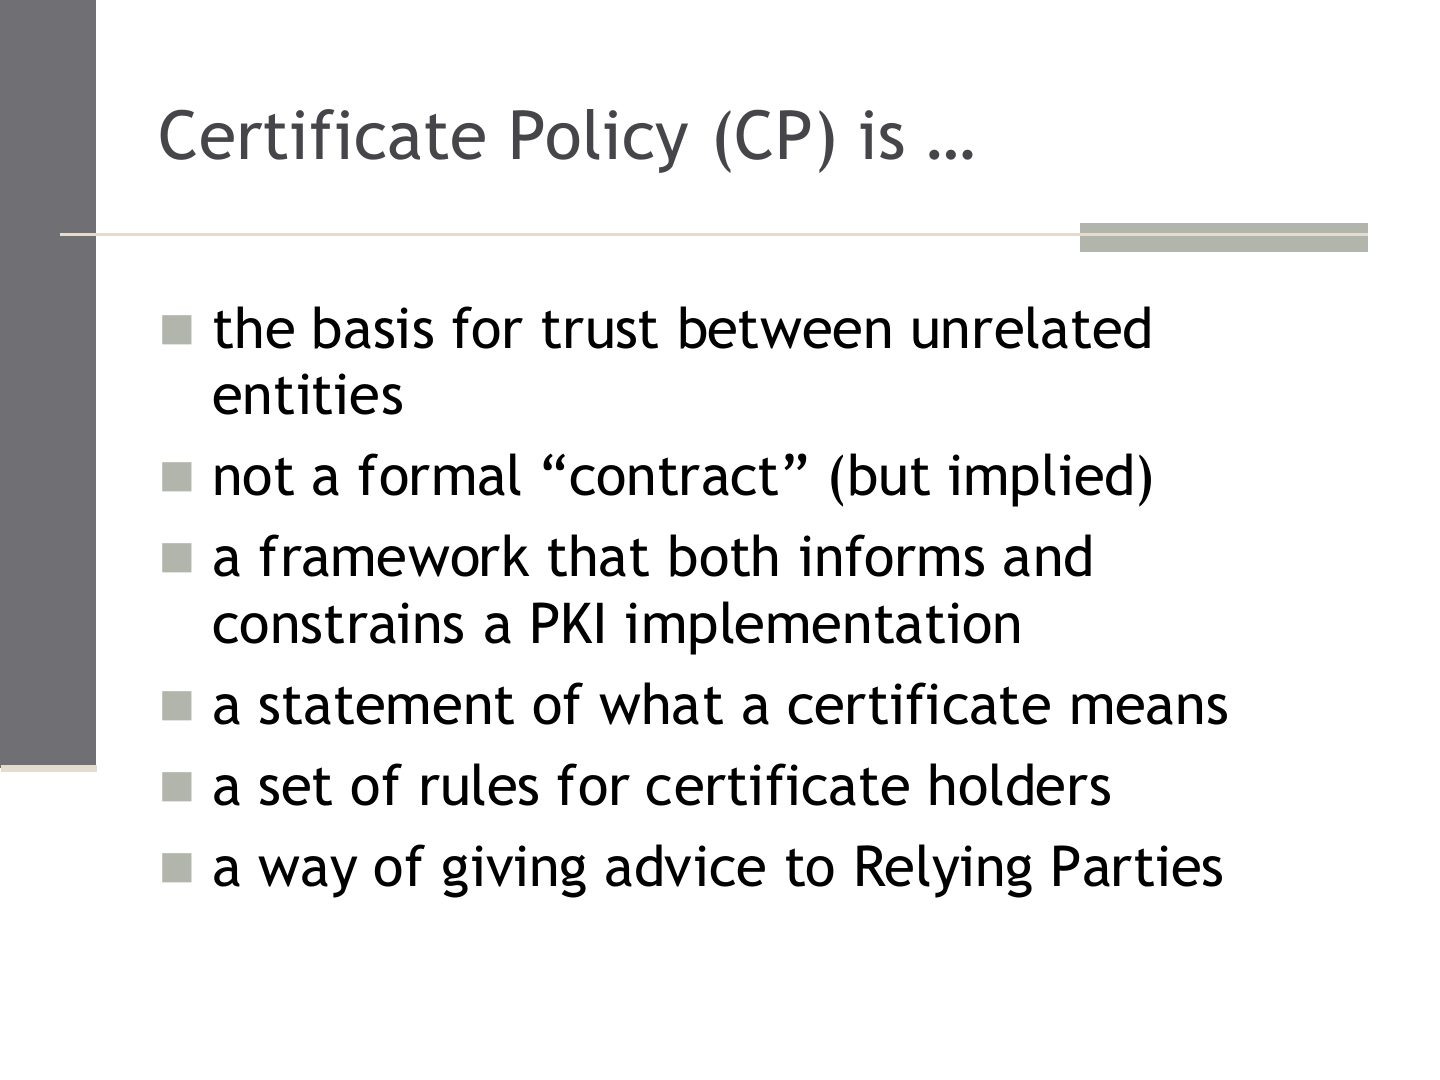
- 15 Certificate Policy (CP) is ...
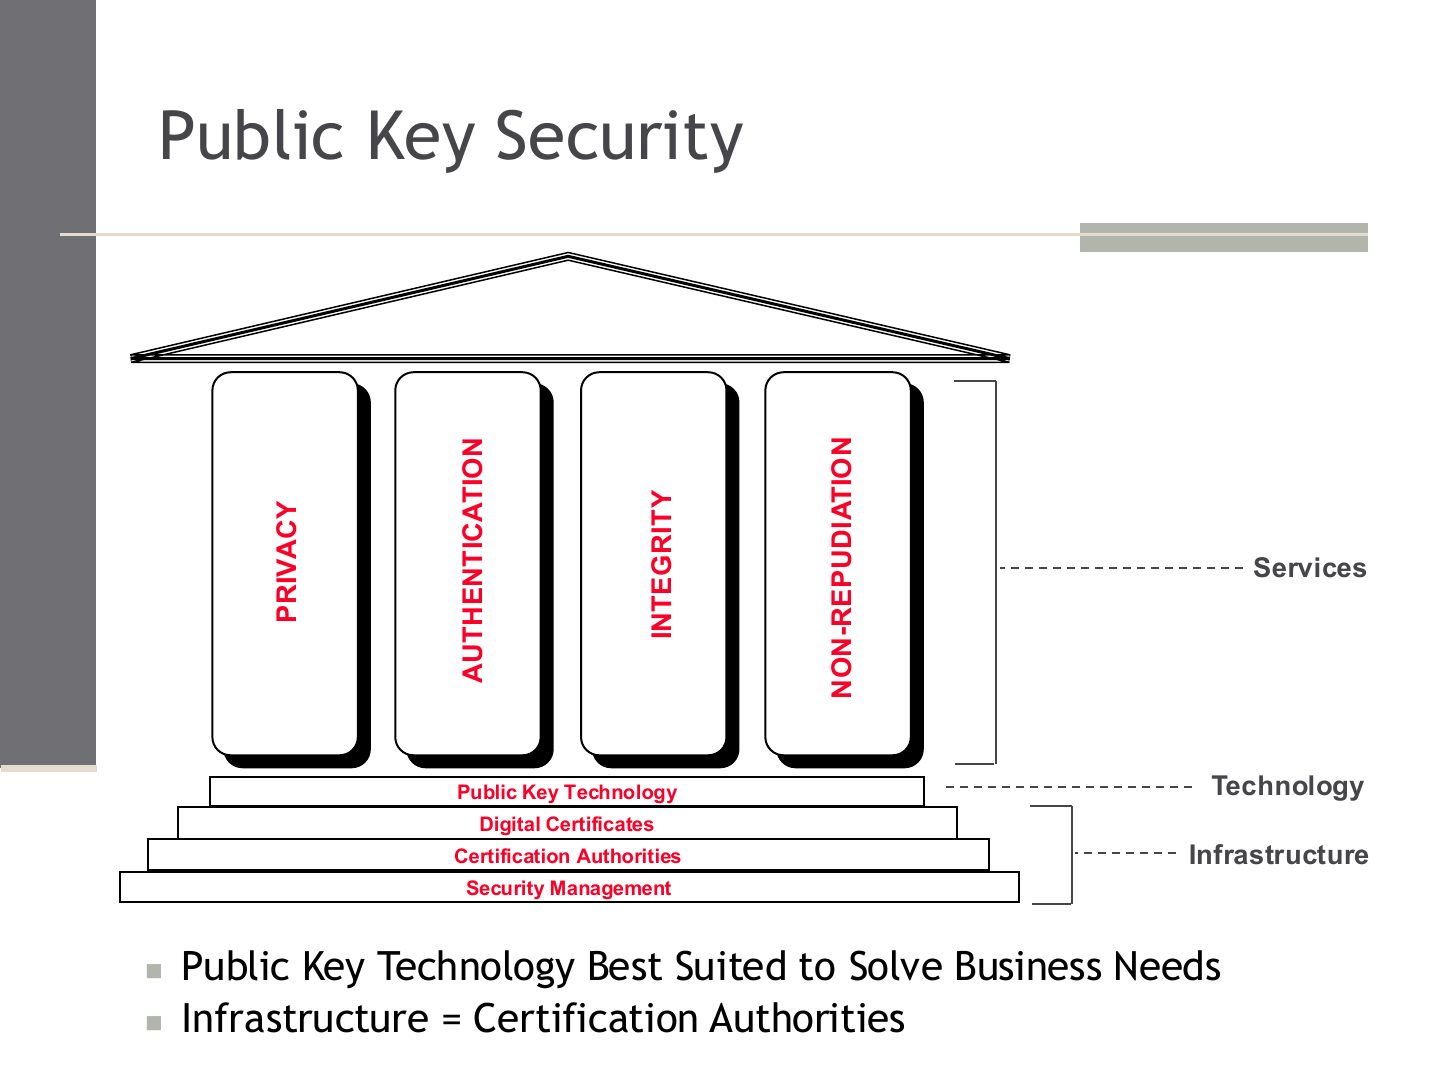
- 16 Public Key Security
- 17 Certificate and SSL
- 18 Certificate and SSL
- 19 End…
Public Key Infrastructure
Agenda
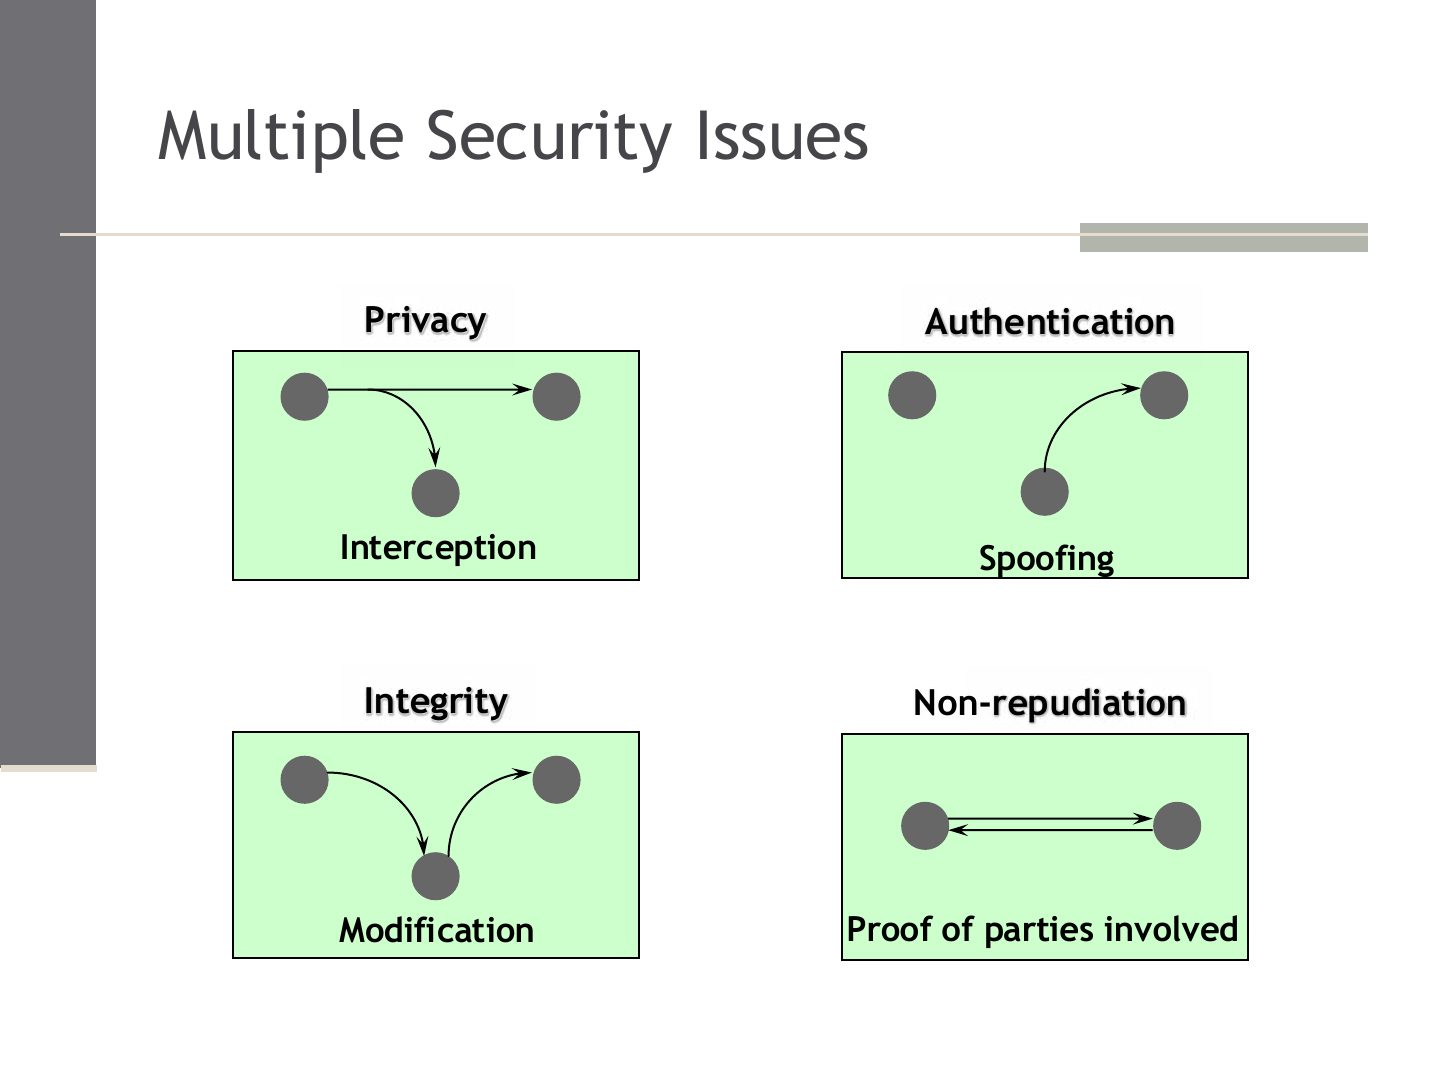
Multiple Security Issues
Notes
Seen again Ch 2, slide 29: Integrity methods
The Critical Questions
Notes
The critical question: how do I KNOW a public key really belongs to that person? → certificates from a trusted CA.
Slide 5
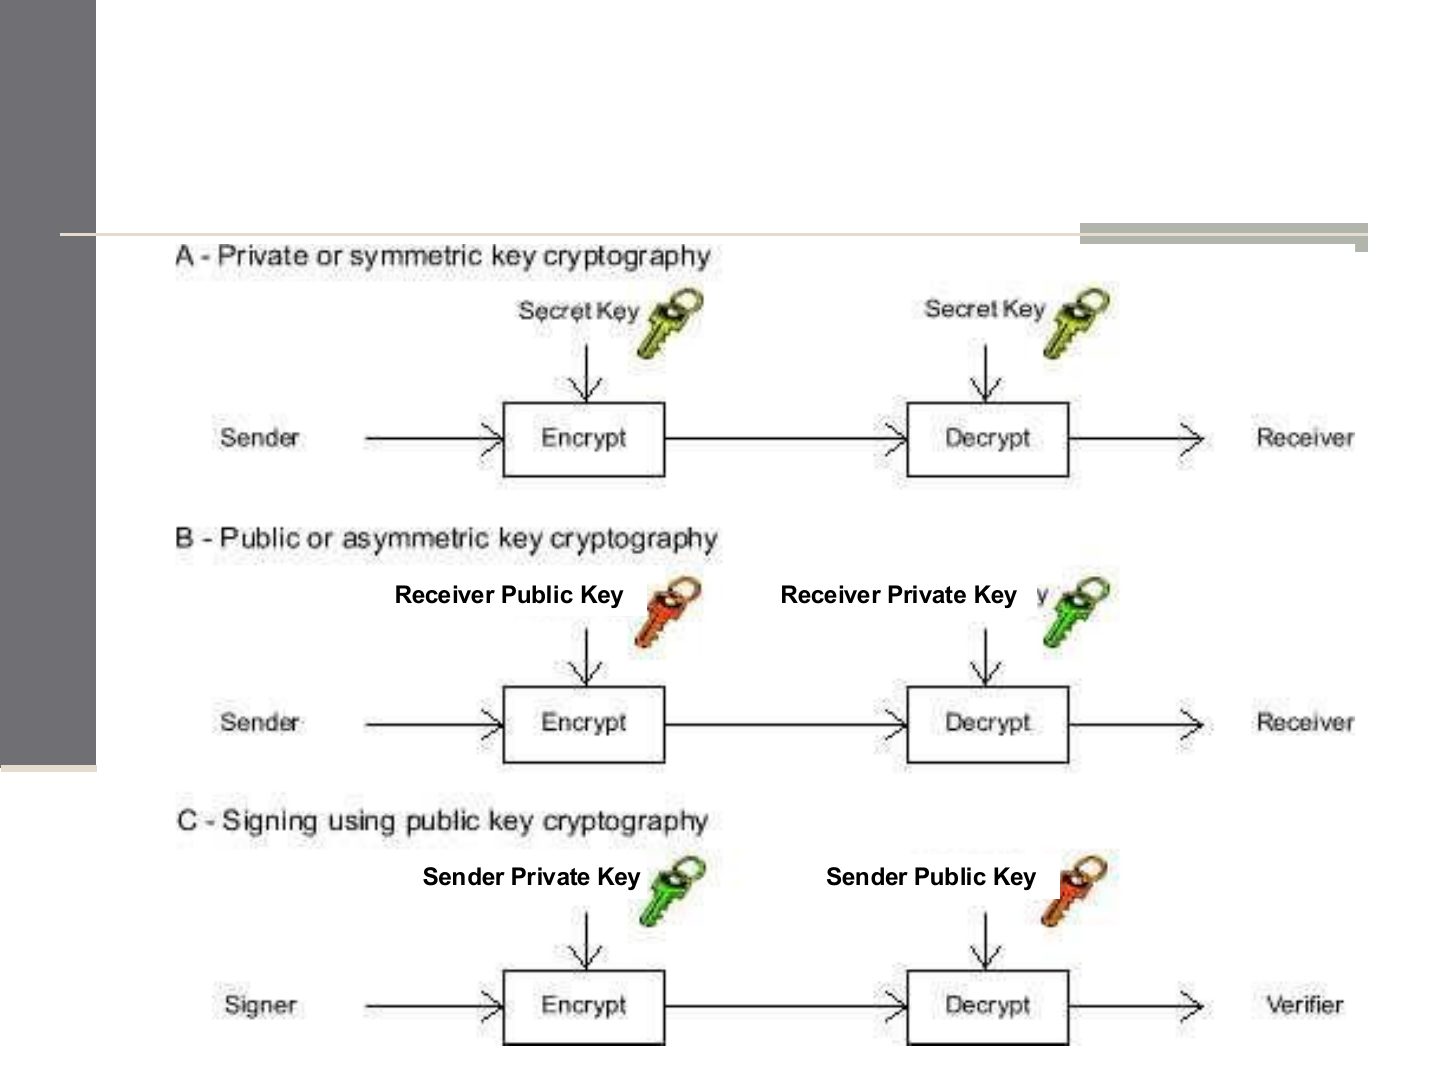
Digital Certificates
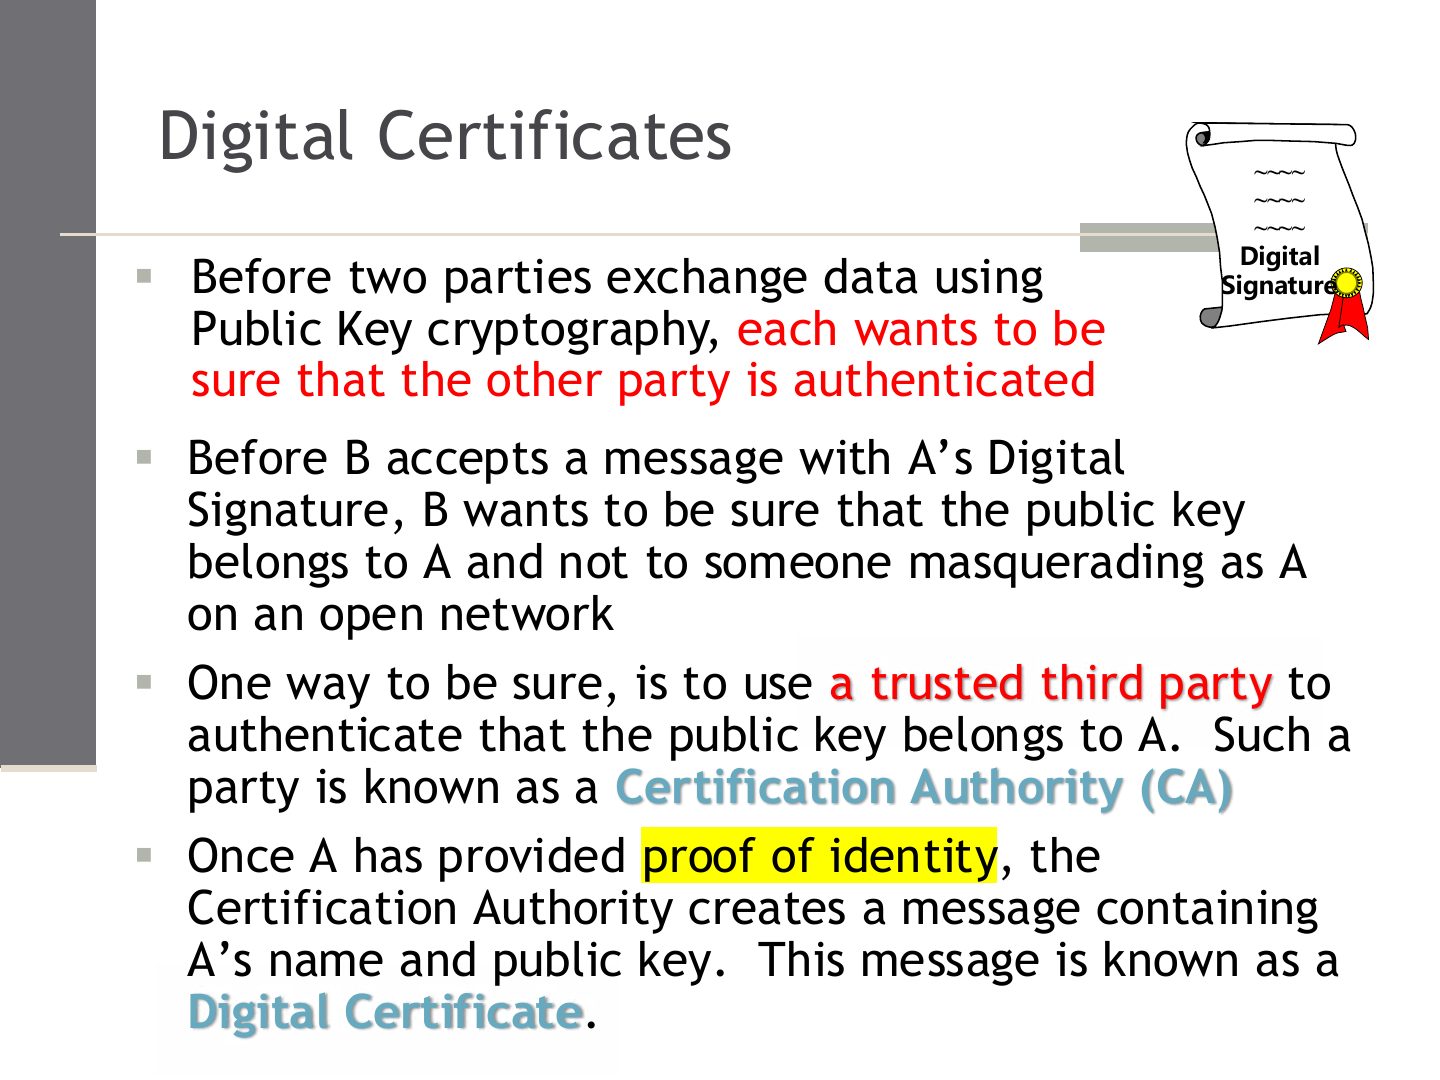
Slide 7
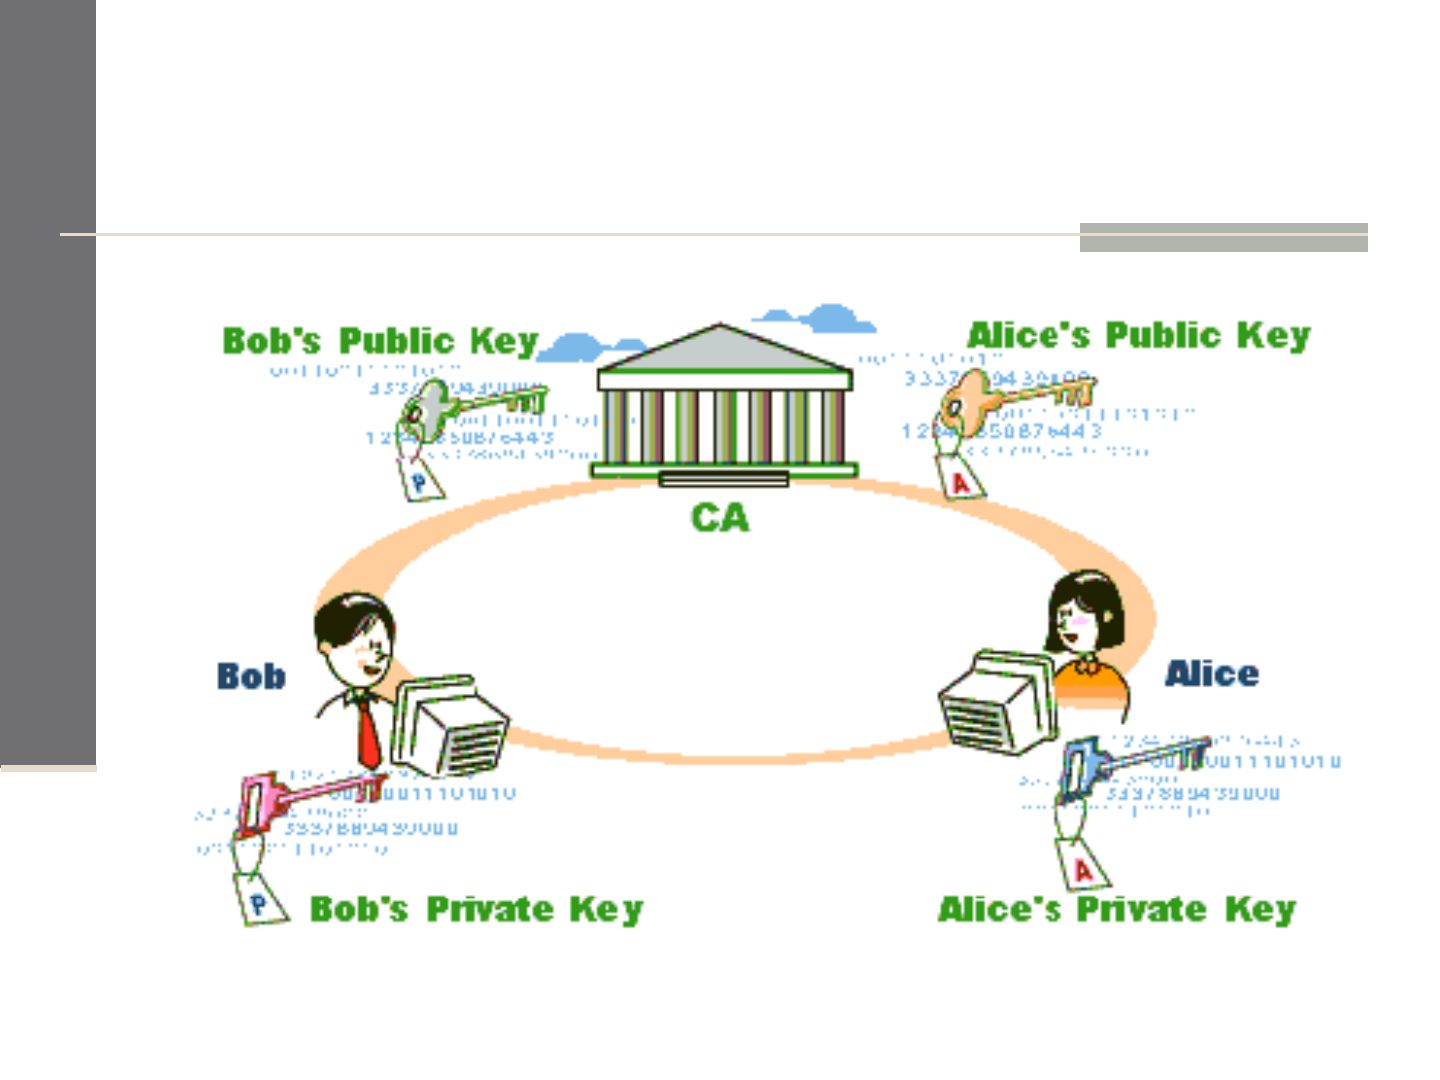
Notes
Certificate contents.
Digital Certificates
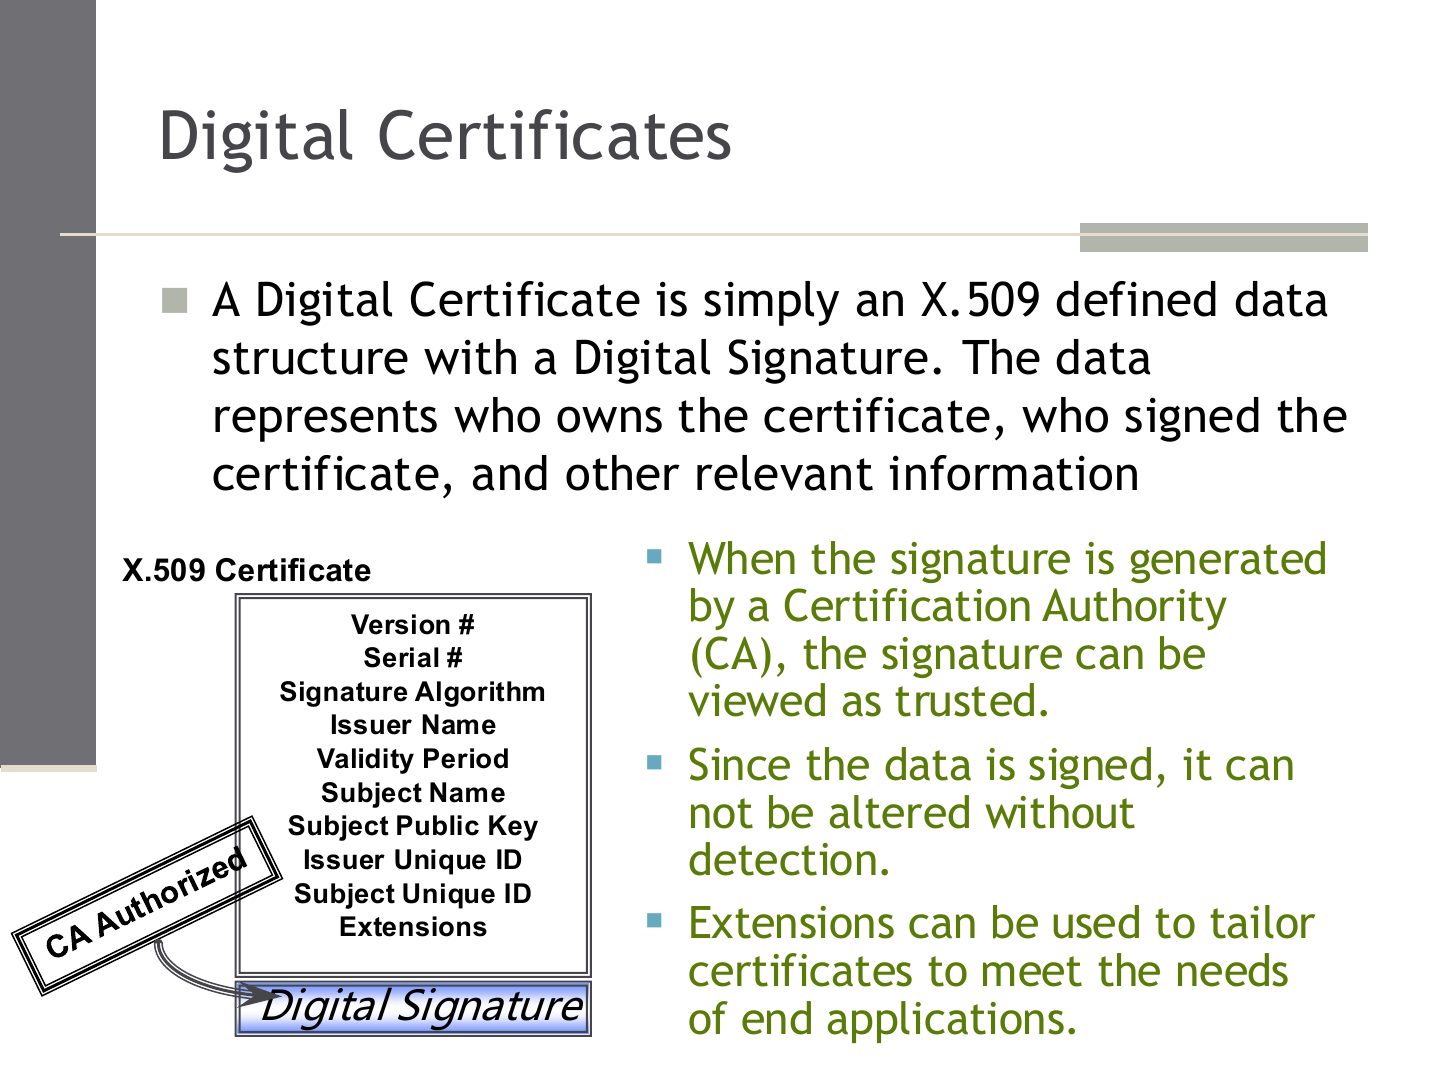
Notes
X.509 certificate: owner, issuer (CA), validity, public key, signed by the CA. The CA signs with ITS private key; anyone validates with the CA’s public key.
Exam angle
Which keys are used to issue and validate an X.509 certificate, and who issues it? (Final 221 B)
Compare with the model answer
The Certificate Authority issues it and signs it with the CA’s private key; anyone validates the signature with the CA’s public key.
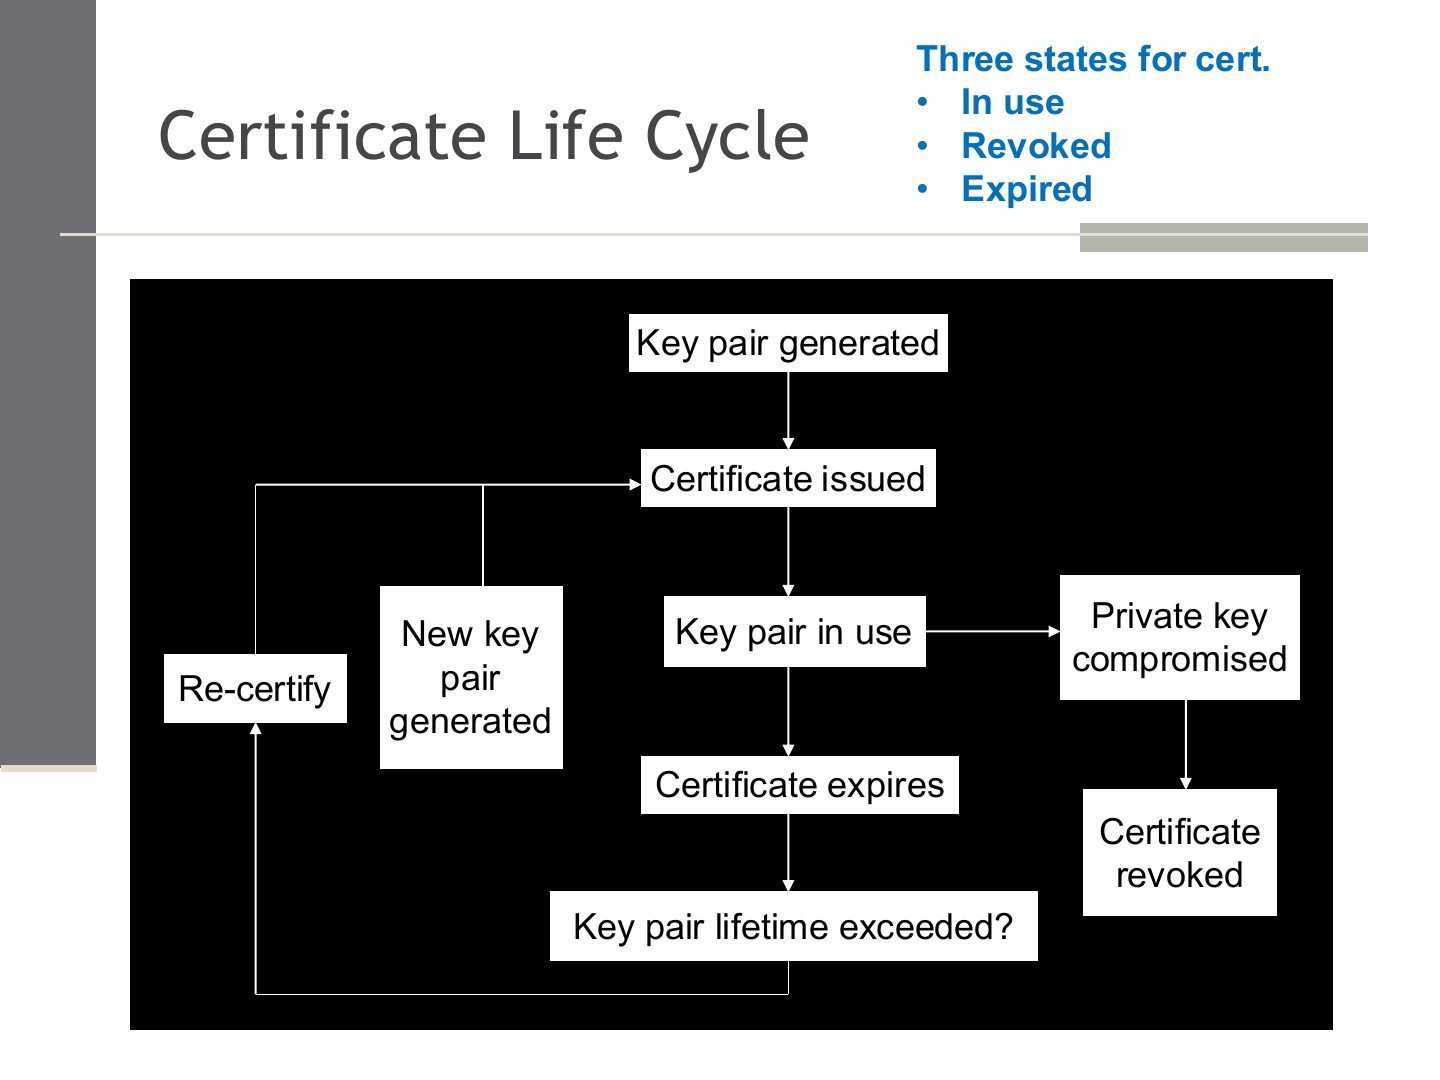
Three states for cert. • In use
Certificate Revocation Lists
Notes
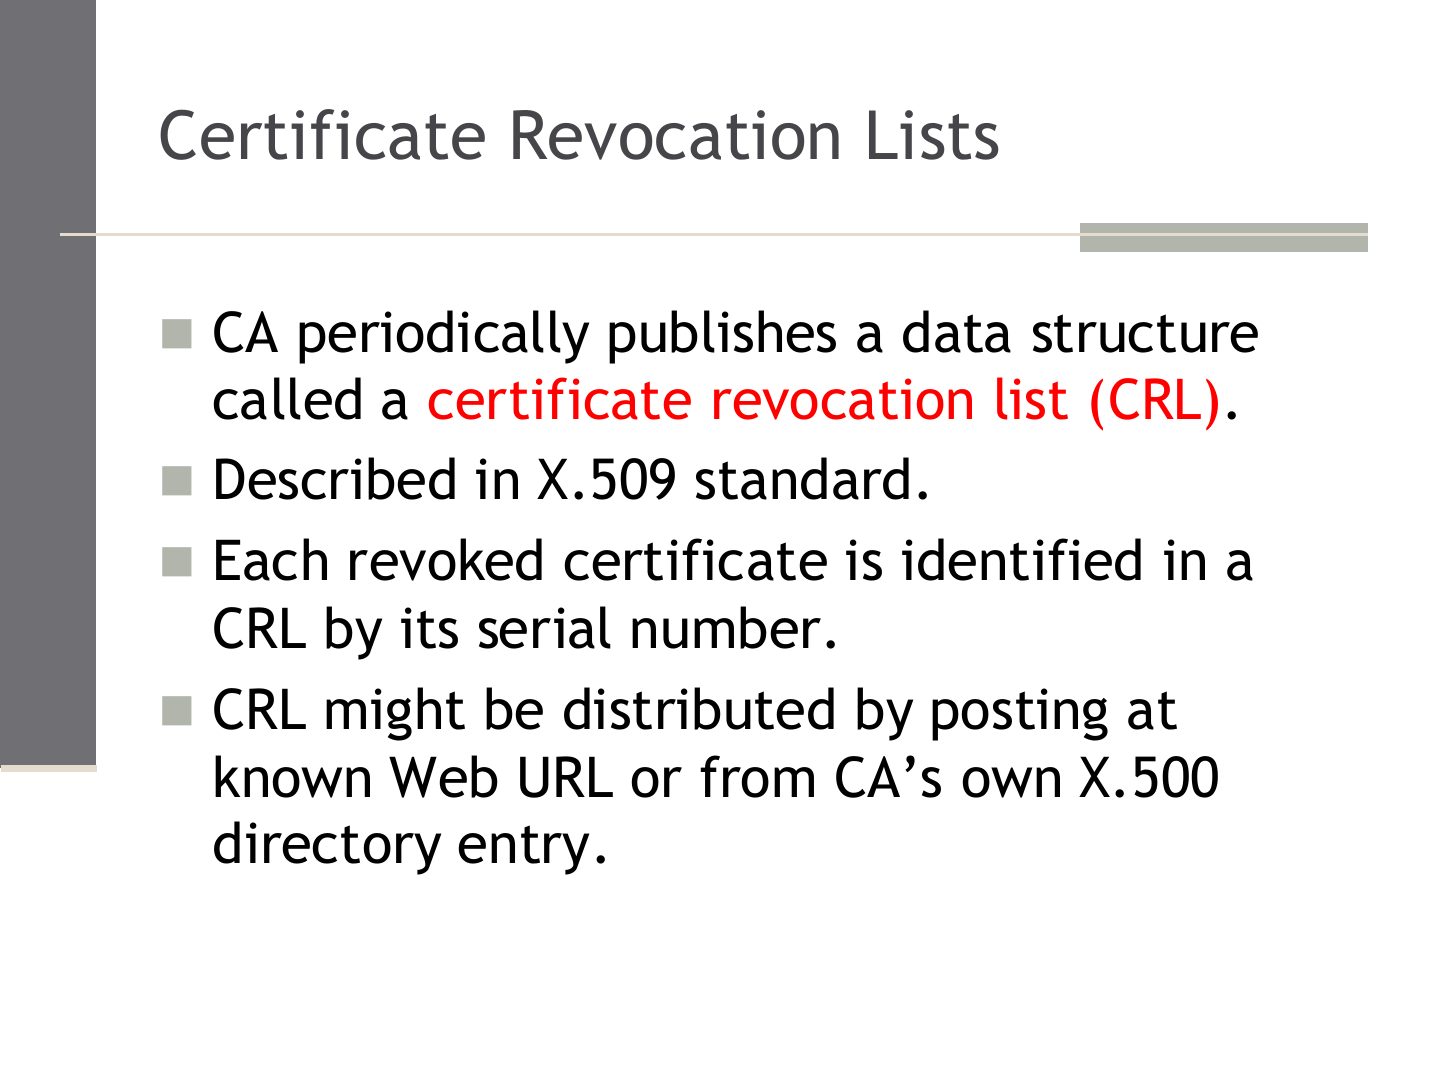
CRL (Certificate Revocation List): published periodically by the CA (X.509). Also OCSP for online checks.
Exam angle
written · where to search for a revoked certificate
MCQ · why a CA revokes a certificate
MCQ · reason not appropriate for revocation
Where can you search for a revoked certificate? (Final 221 B)
Compare with the model answer
In the Certificate Revocation List (CRL) that the CA periodically publishes (or by querying the CA’s OCSP responder).
A CA revokes a user’s certificate when:
- Major 181.
DC in reality
Notes
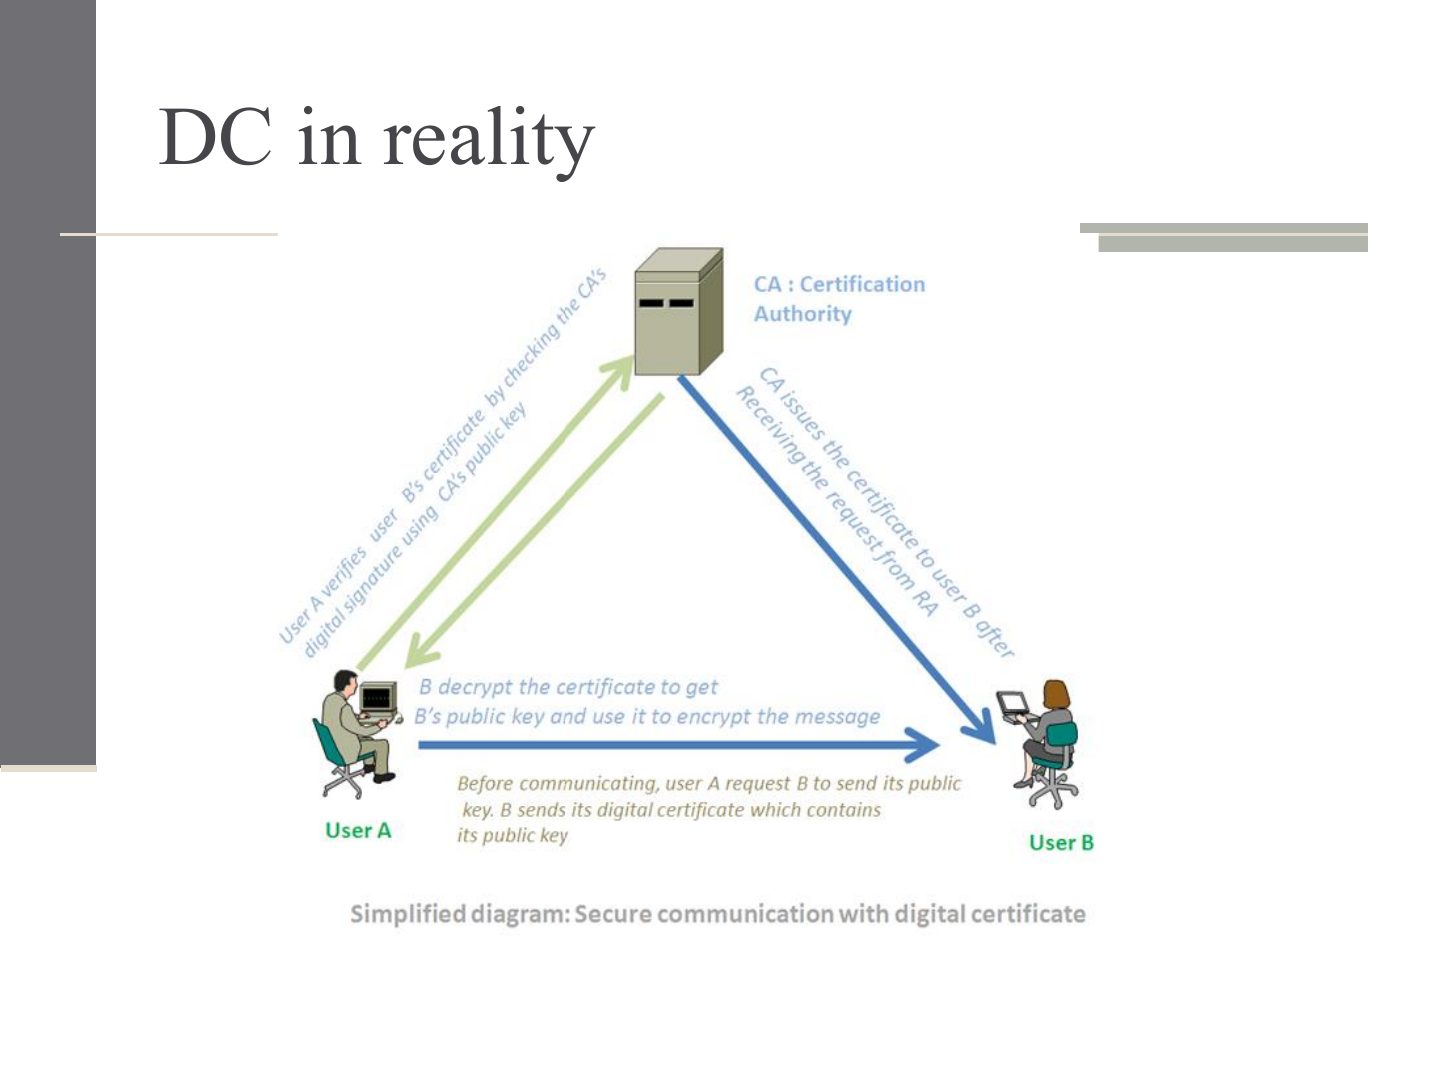
A real certificate viewed in a browser.
PKI Players
Exam angle
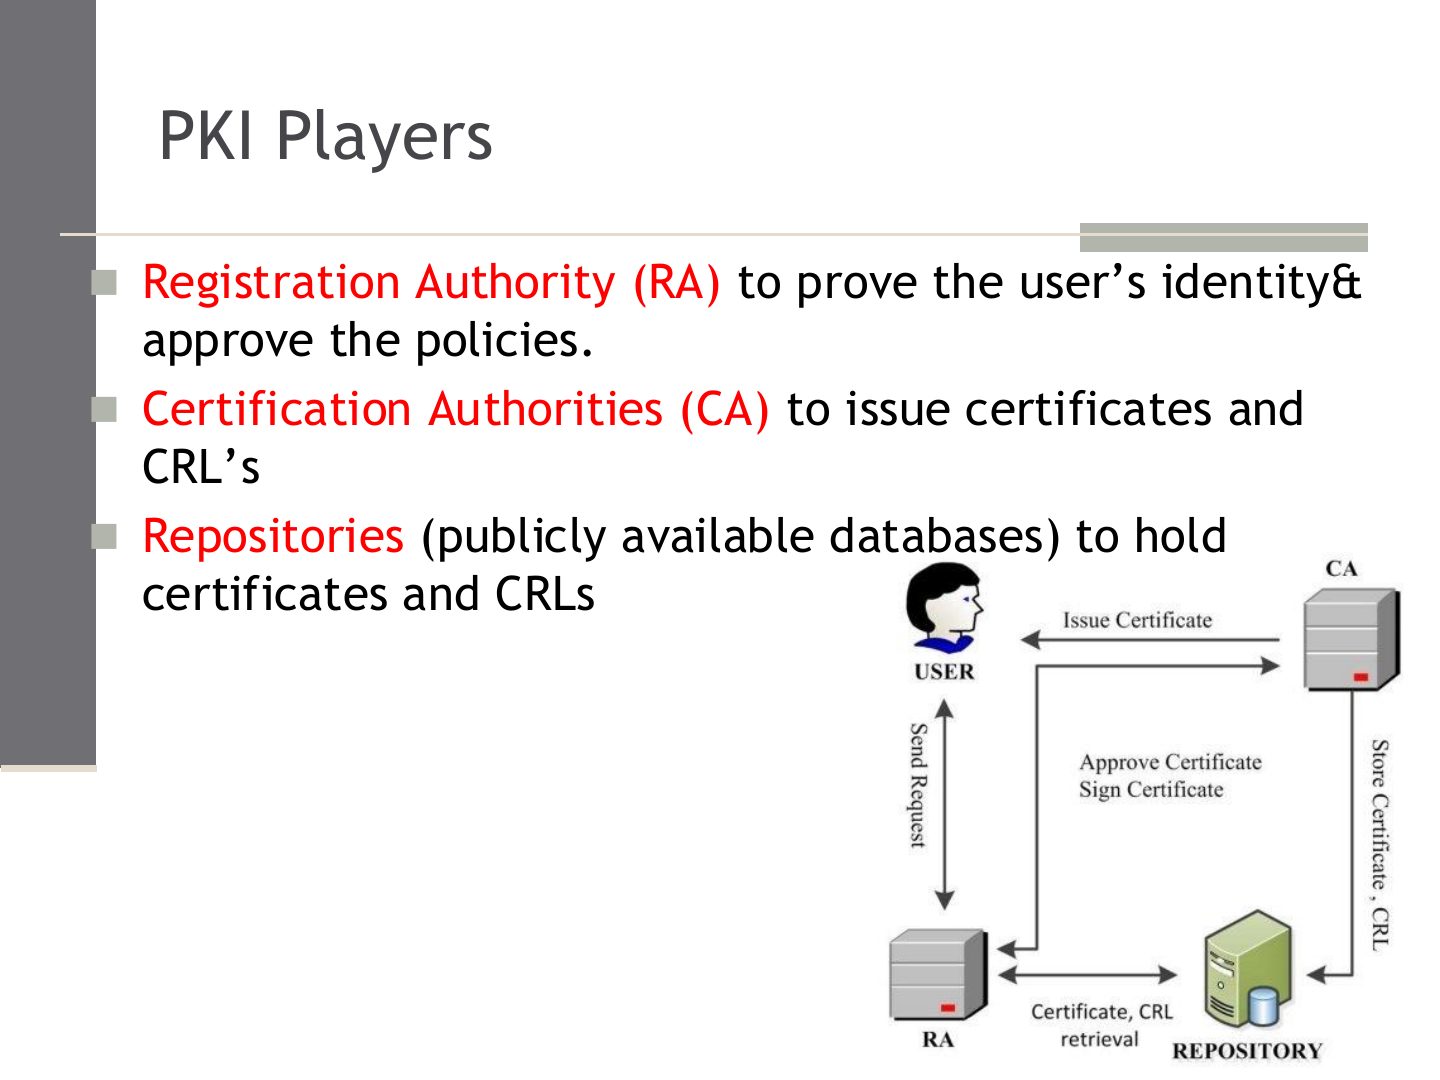
Which PKI component verifies a user’s identity before a certificate is issued?
Certification Authority (CA)
Registration Authority (RA)
Certificate Policy (CP) is ...
Public Key Security
Notes
Public-key security relies on the private key staying private.
Certificate and SSL
Notes
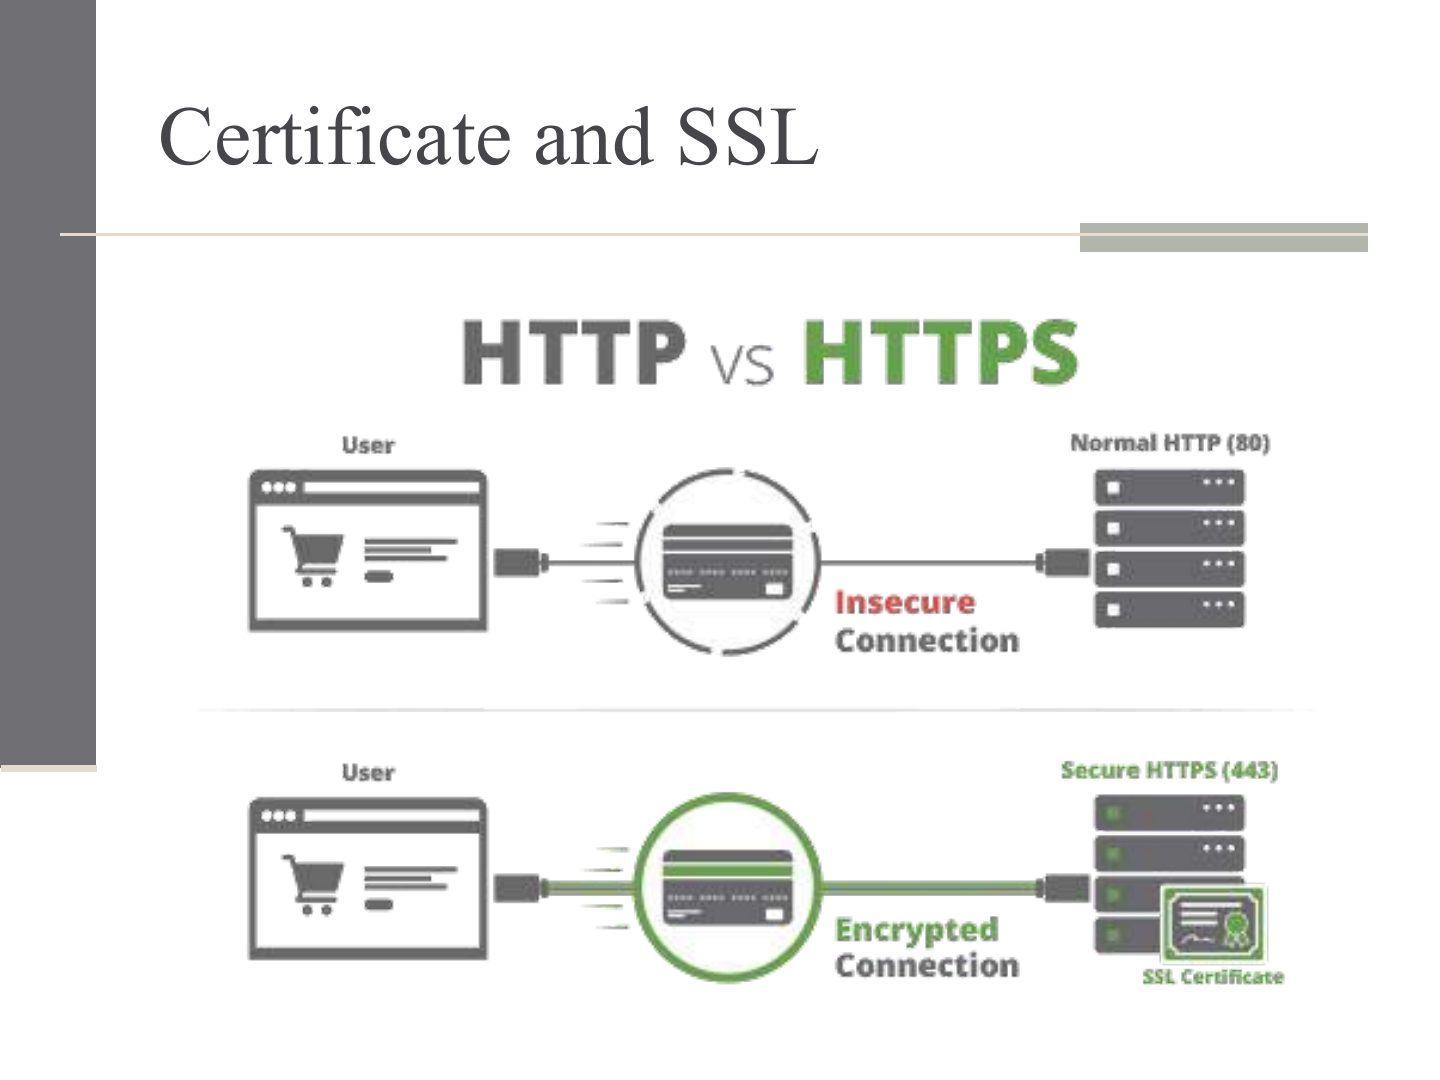
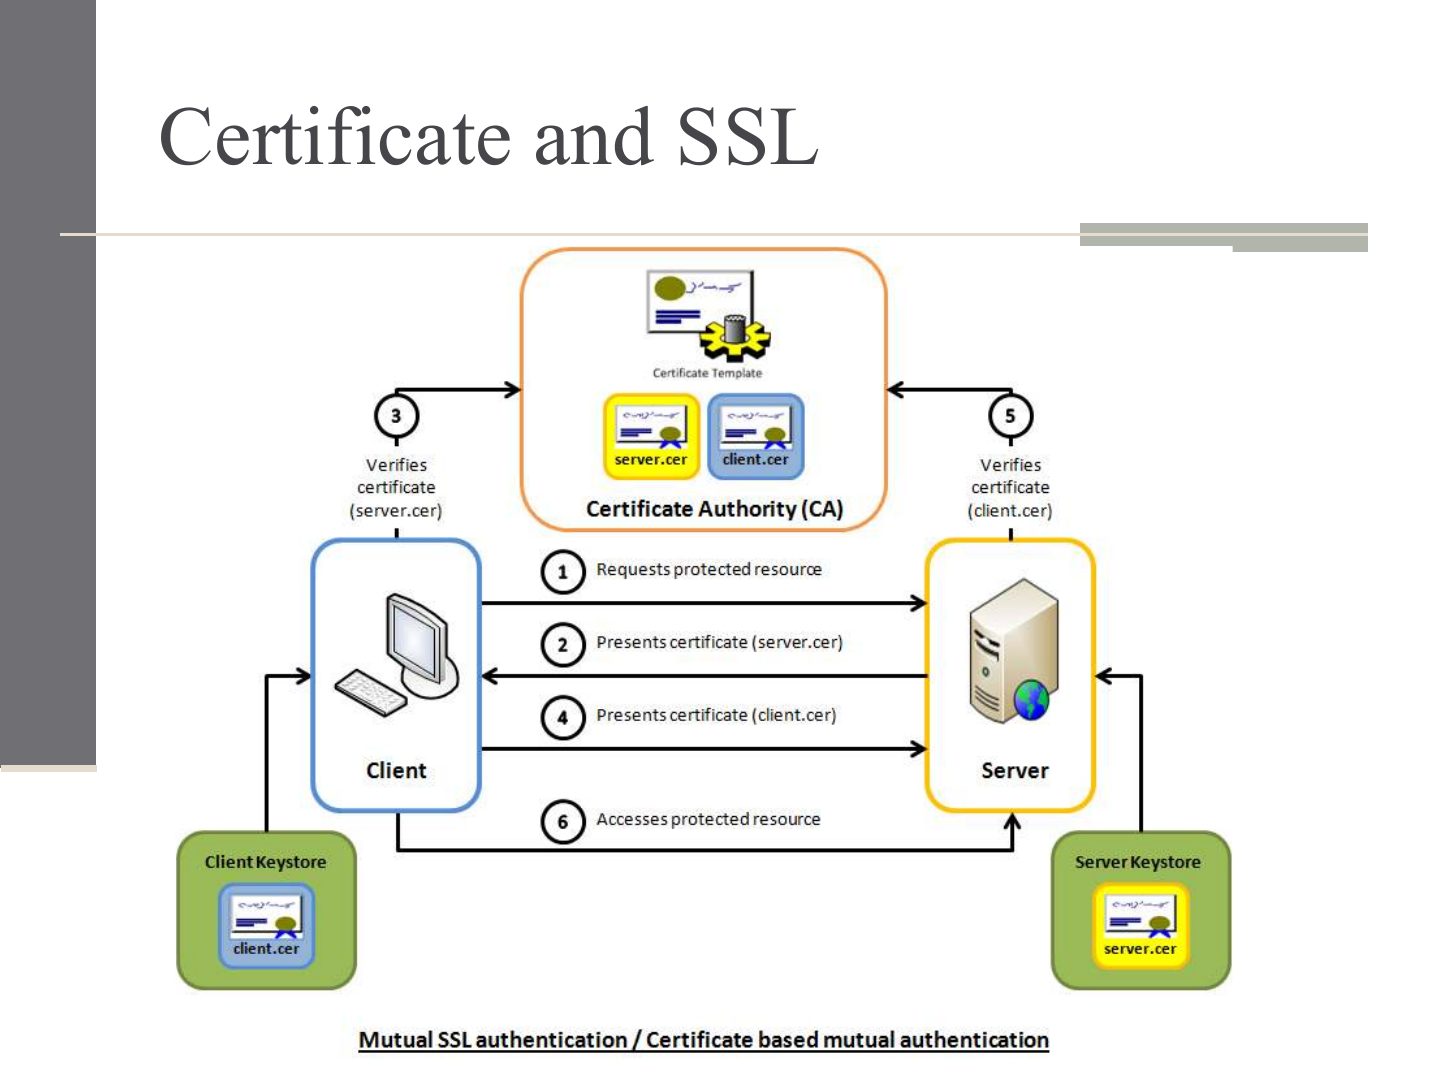
Certificates in SSL/TLS: the server sends its certificate; the browser checks it against trusted CAs.
Certificate and SSL
Notes
TLS handshake uses the certificate to set up a shared symmetric session key (hybrid encryption).
Exam angle
Related question: MCQ · S/MIME relies on certificates
End…
Notes
End.