A system that aggregates and correlates logs from many devices to raise alerts is a:
SIEM, UBA and Anti-Malware
Security Information and Event Management (architecture, functions, products), User Behavior Analytics, and anti-Trojan and antivirus software.
How to read this page
Every original slide is shown unchanged. Yellow marks on a slide point to a numbered note: hover or tap a mark to jump to its note, and hover a note to see its marks. Questions tagged Past exam appeared on a real paper; Prediction questions are likely angles, not confirmed. Pick an answer to each question: a wrong pick tells you why it is wrong, so you can try again.
All 15 slides
- 1 Slide 1
- 2 Module Objectives
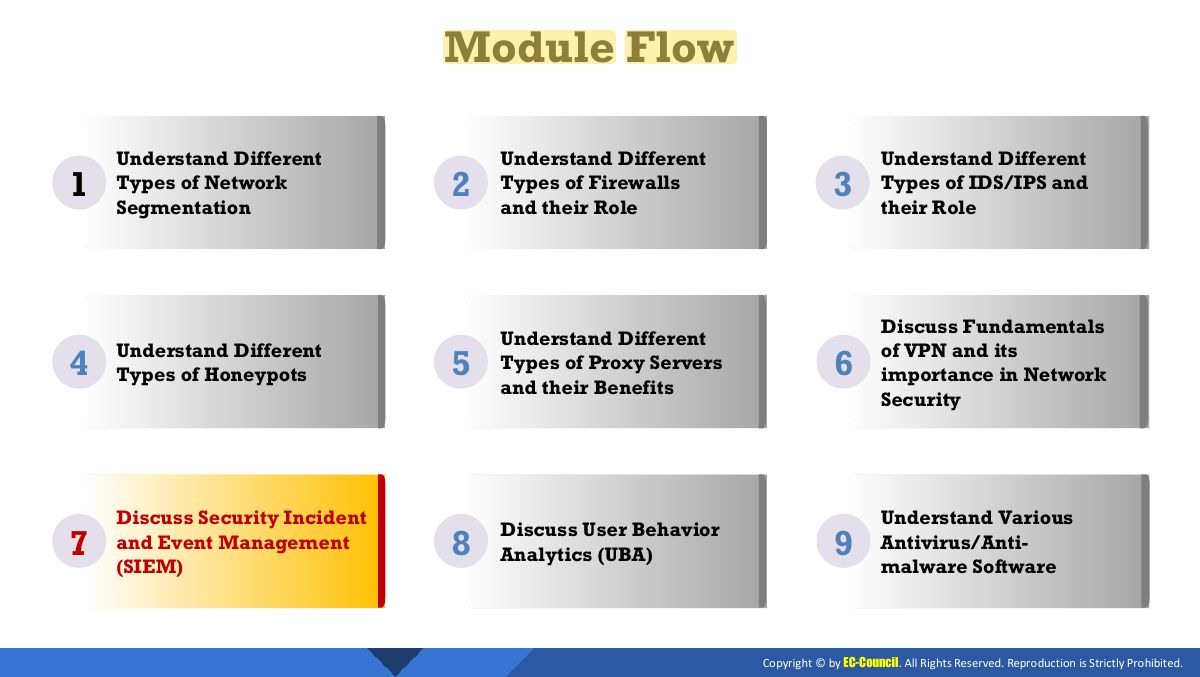
- 3 Module Flow
- 4 Security Incident and Event Management (SIEM)
- 5 SIEM Architecture
- 6 SIEM Functions
- 7 SIEM Solutions
- 8 Module Flow
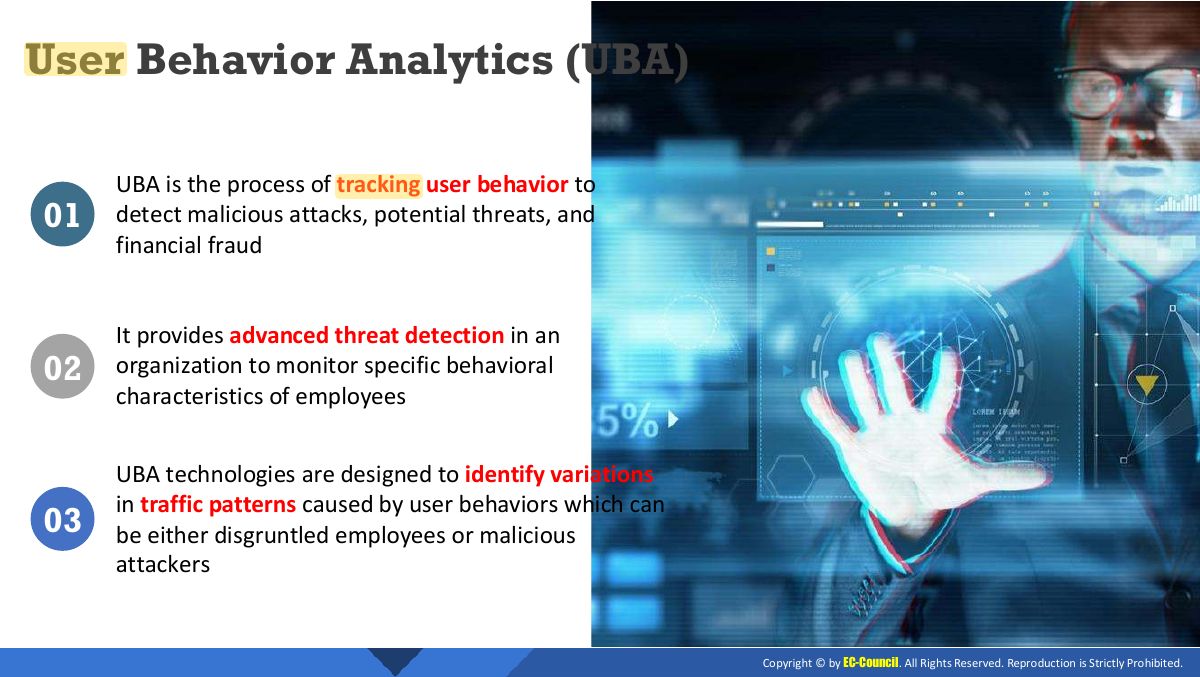
- 9 User Behavior Analytics (UBA)
- 10 Why User Behavior Analytics is Effective?
- 11 UBA/UEBA Tools
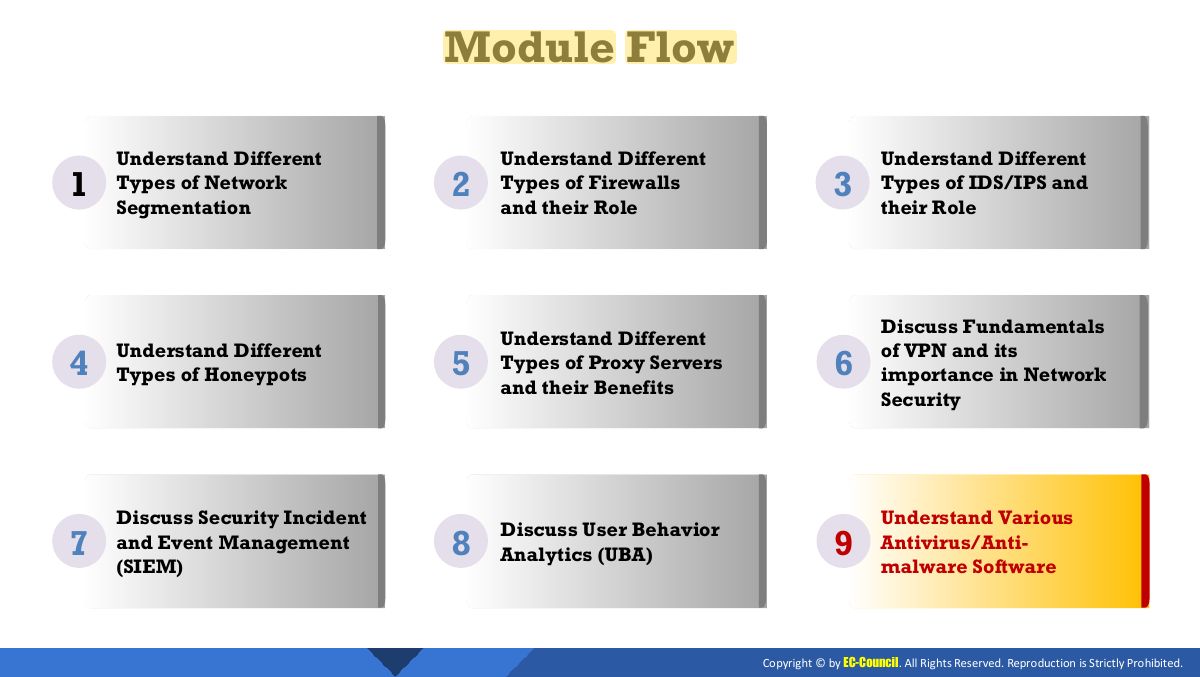
- 12 Module Flow
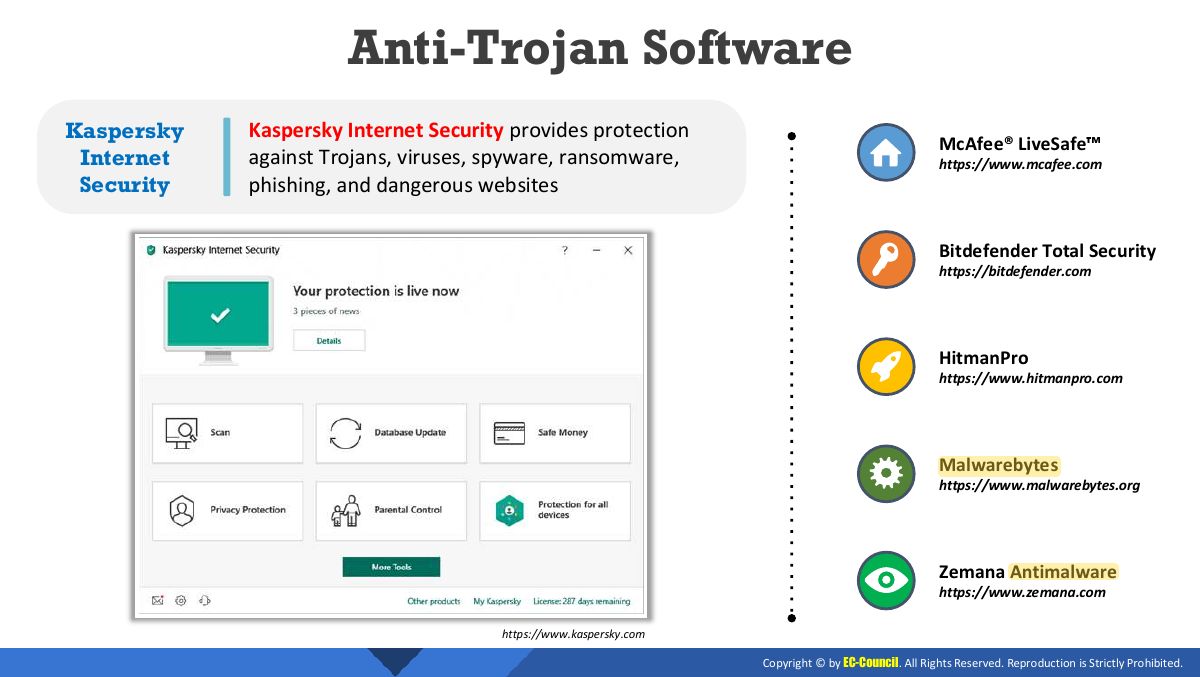
- 13 Anti-Trojan Software
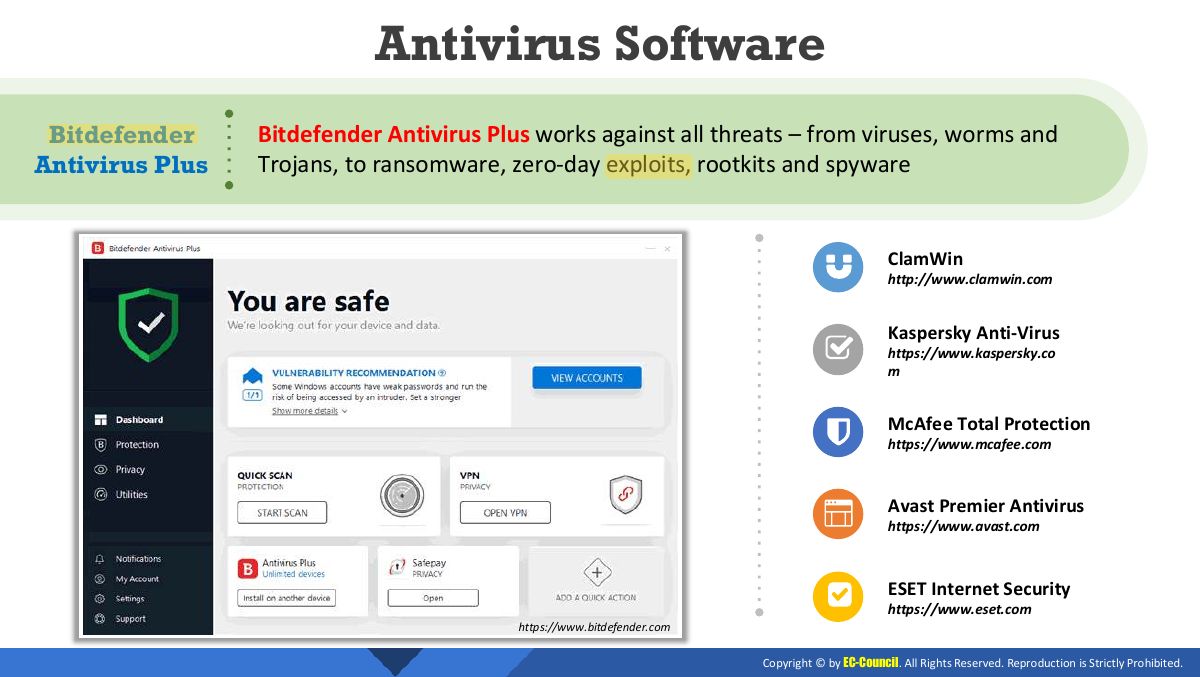
- 14 Antivirus Software
- 15 Module Summary
Slide 1
Module Objectives
Module Flow
Security Incident and Event Management (SIEM)
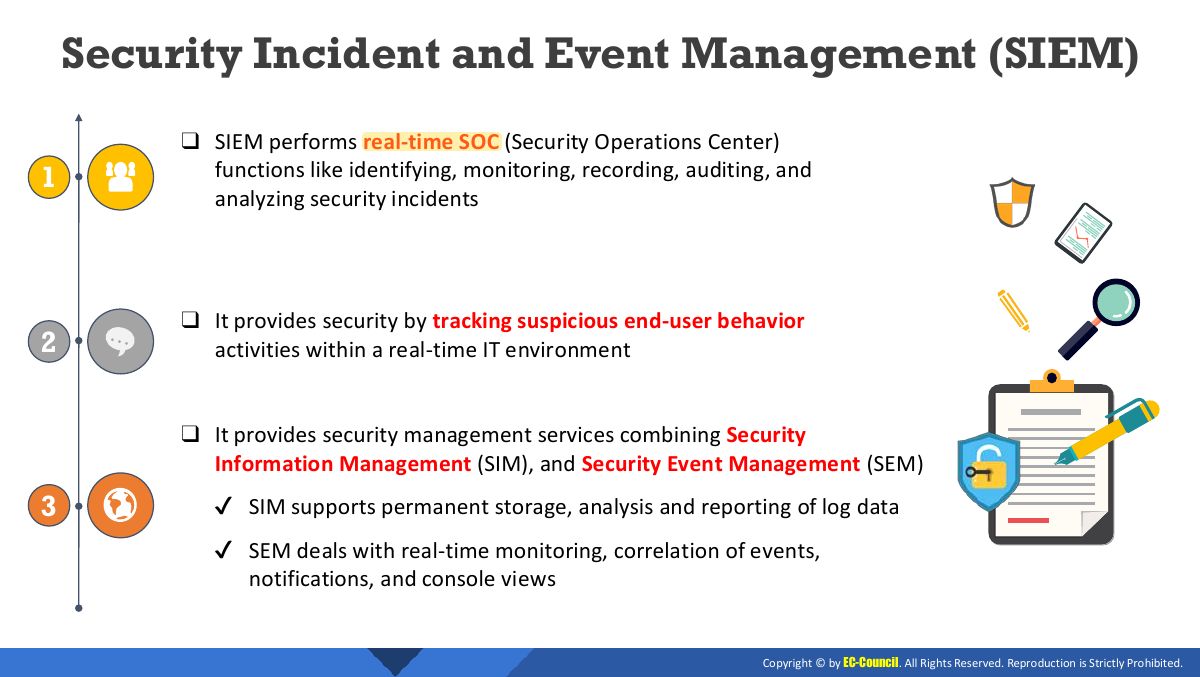
Notes
SIEM: collects and correlates logs and events from many sources in real time; alerts, dashboards, compliance reports.
Exam angle
SIEM Architecture
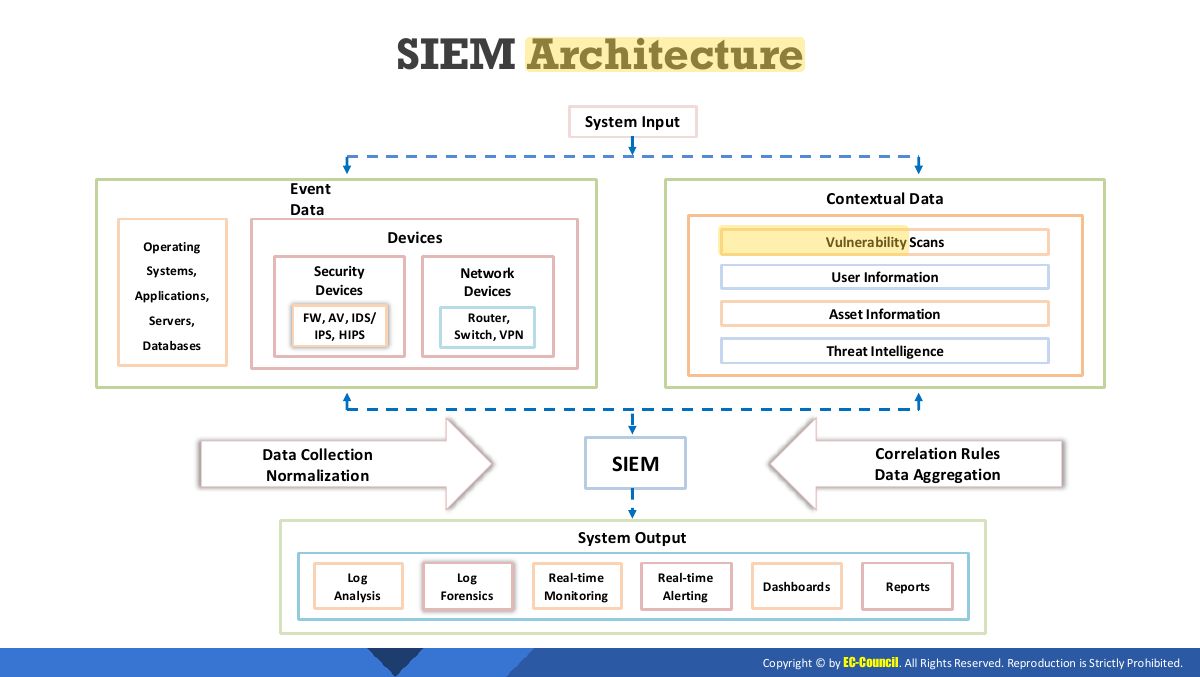
SIEM Functions
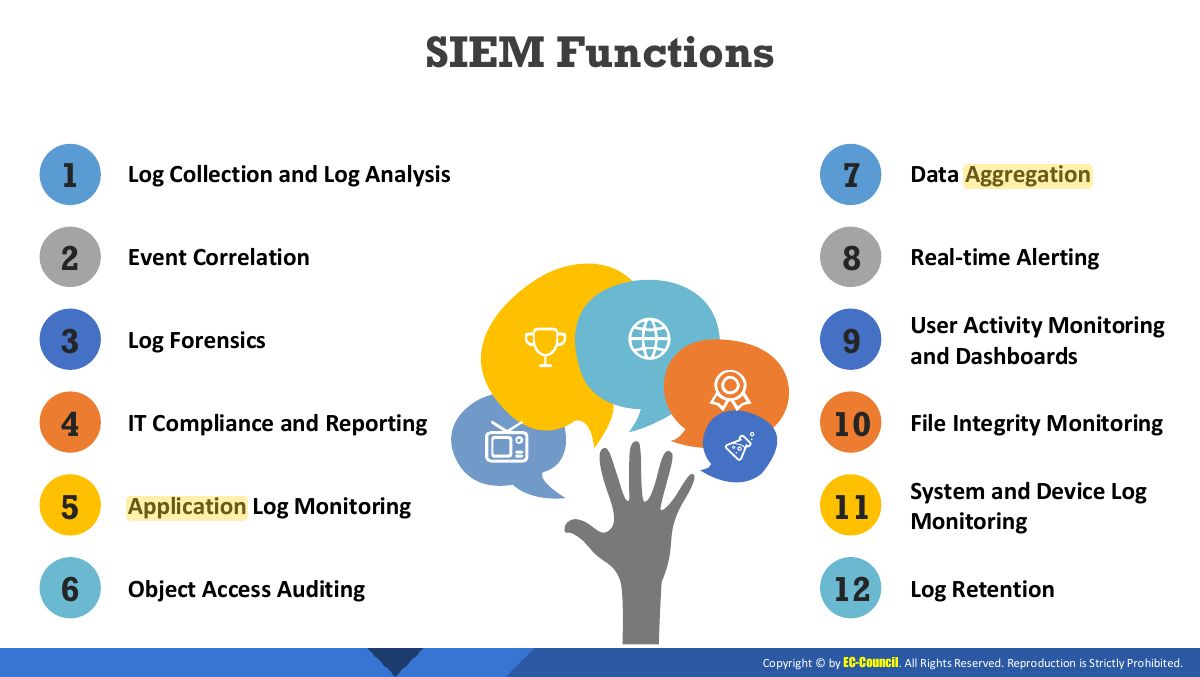
SIEM Solutions
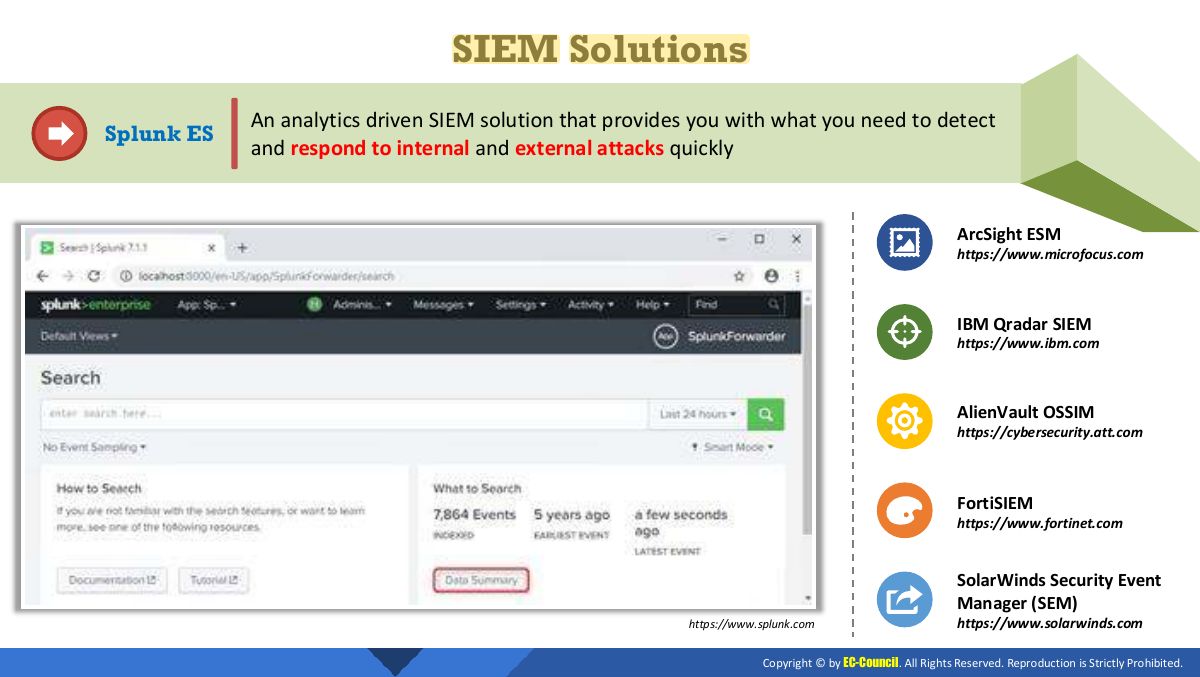
Module Flow
User Behavior Analytics (UBA)
Notes
UBA/UEBA: builds a baseline of normal user behaviour and flags anomalies (insider threats, compromised accounts).
Exam angle
An employee suddenly downloading gigabytes at 3 a.m. would most likely be flagged by:
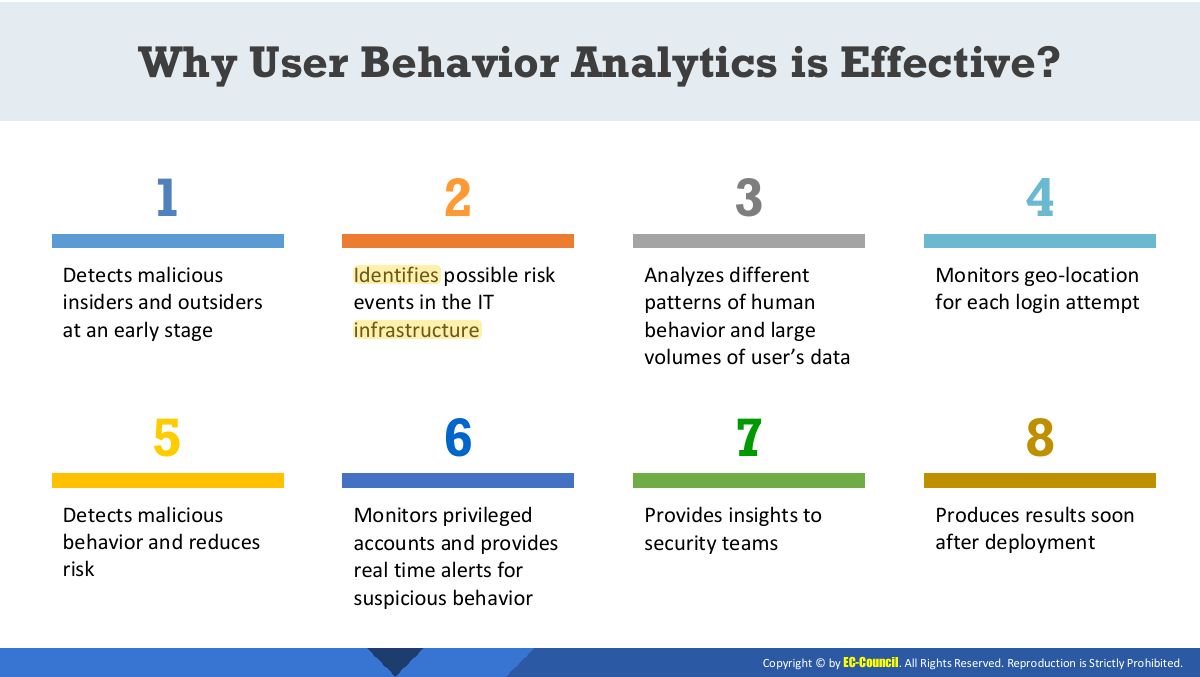
Why User Behavior Analytics is Effective?
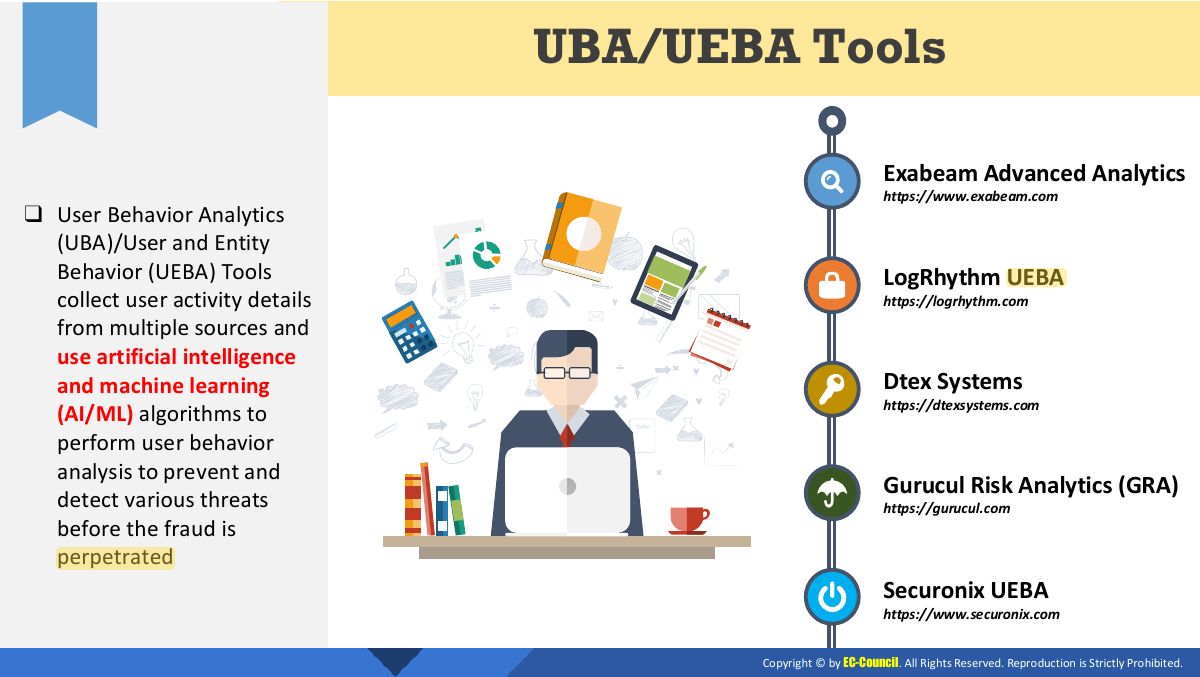
UBA/UEBA Tools
Module Flow
Anti-Trojan Software
Antivirus Software
Notes
Antivirus: signature, heuristic and behaviour-based detection; keep definitions updated.
Module Summary