"I’m the CEO and need this password NOW" exploits:
Social Engineering
What social engineering is and why it works, common targets and vulnerable behaviours, attack phases, human-, computer- and mobile-based techniques (impersonation, vishing, eavesdropping, phishing…), insider threats, countermeasures and social-engineering pen tests.
How to read this page
Every original slide is shown unchanged. Yellow marks on a slide point to a numbered note: hover or tap a mark to jump to its note, and hover a note to see its marks. Questions tagged Past exam appeared on a real paper; Prediction questions are likely angles, not confirmed. Pick an answer to each question: a wrong pick tells you why it is wrong, so you can try again.
All 47 slides
- 1 Slide 1
- 2 Slide 2
- 3 What is Social Engineering?
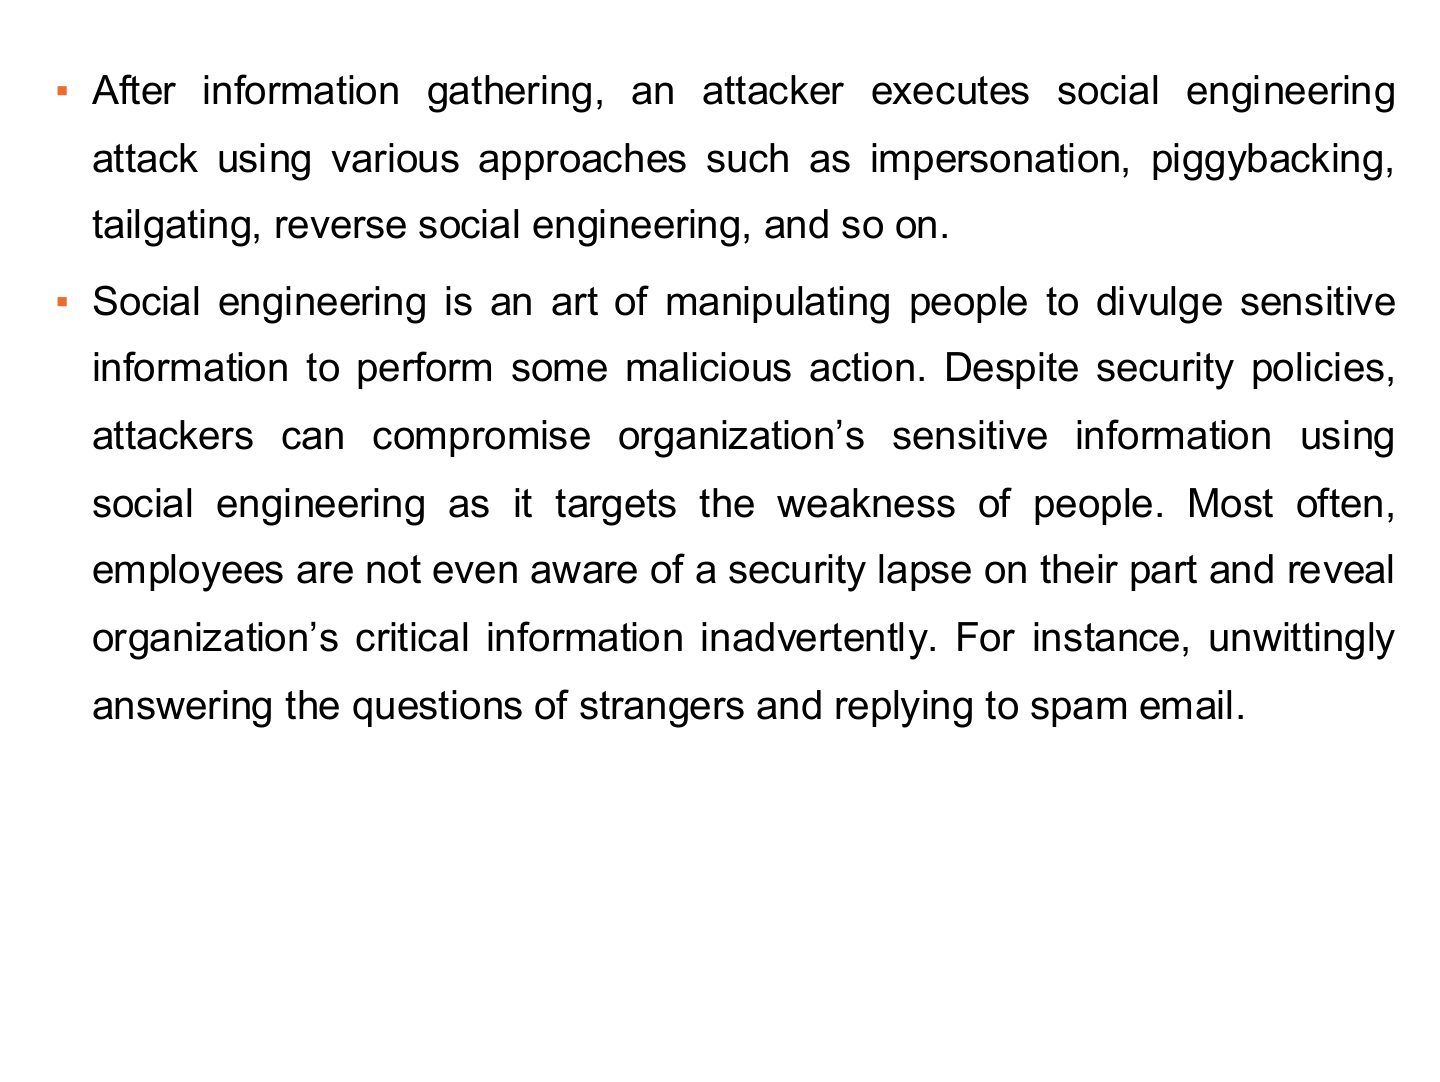
- 4 ▪ After information gathering, an attacker executes social engineering
- 5 Slide 5
- 6 Slide 6
- 7 Common Targets of Social Engineering
- 8 System Administrators: A system administrator in an organization is
- 9 Impact of Social Engineering Attack on Organization
- 10 Dangers of Terrorism: Terrorism and anti-social elements
- 11 Behaviors Vulnerable to Attacks
- 12 Behaviors Vulnerable to Attacks
- 13 Factors that Make Companies Vulnerable to Attacks
- 14 Several Organizational Units Some organizations have their units at
- 15 Why is Social Engineering Effective?
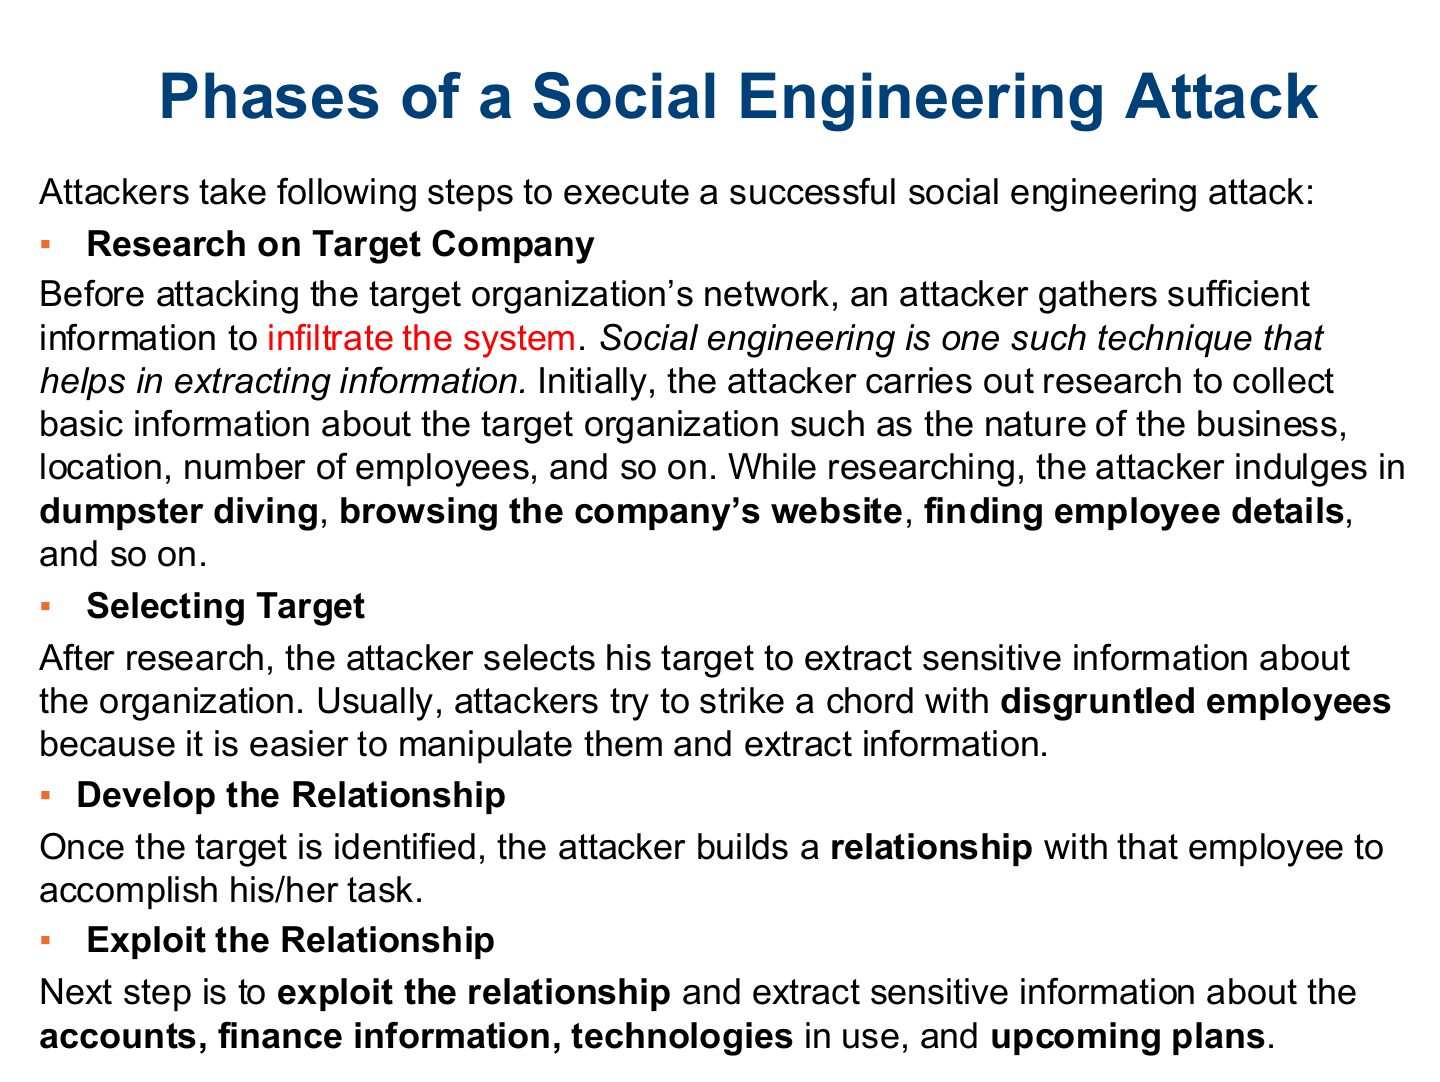
- 16 Phases of a Social Engineering Attack
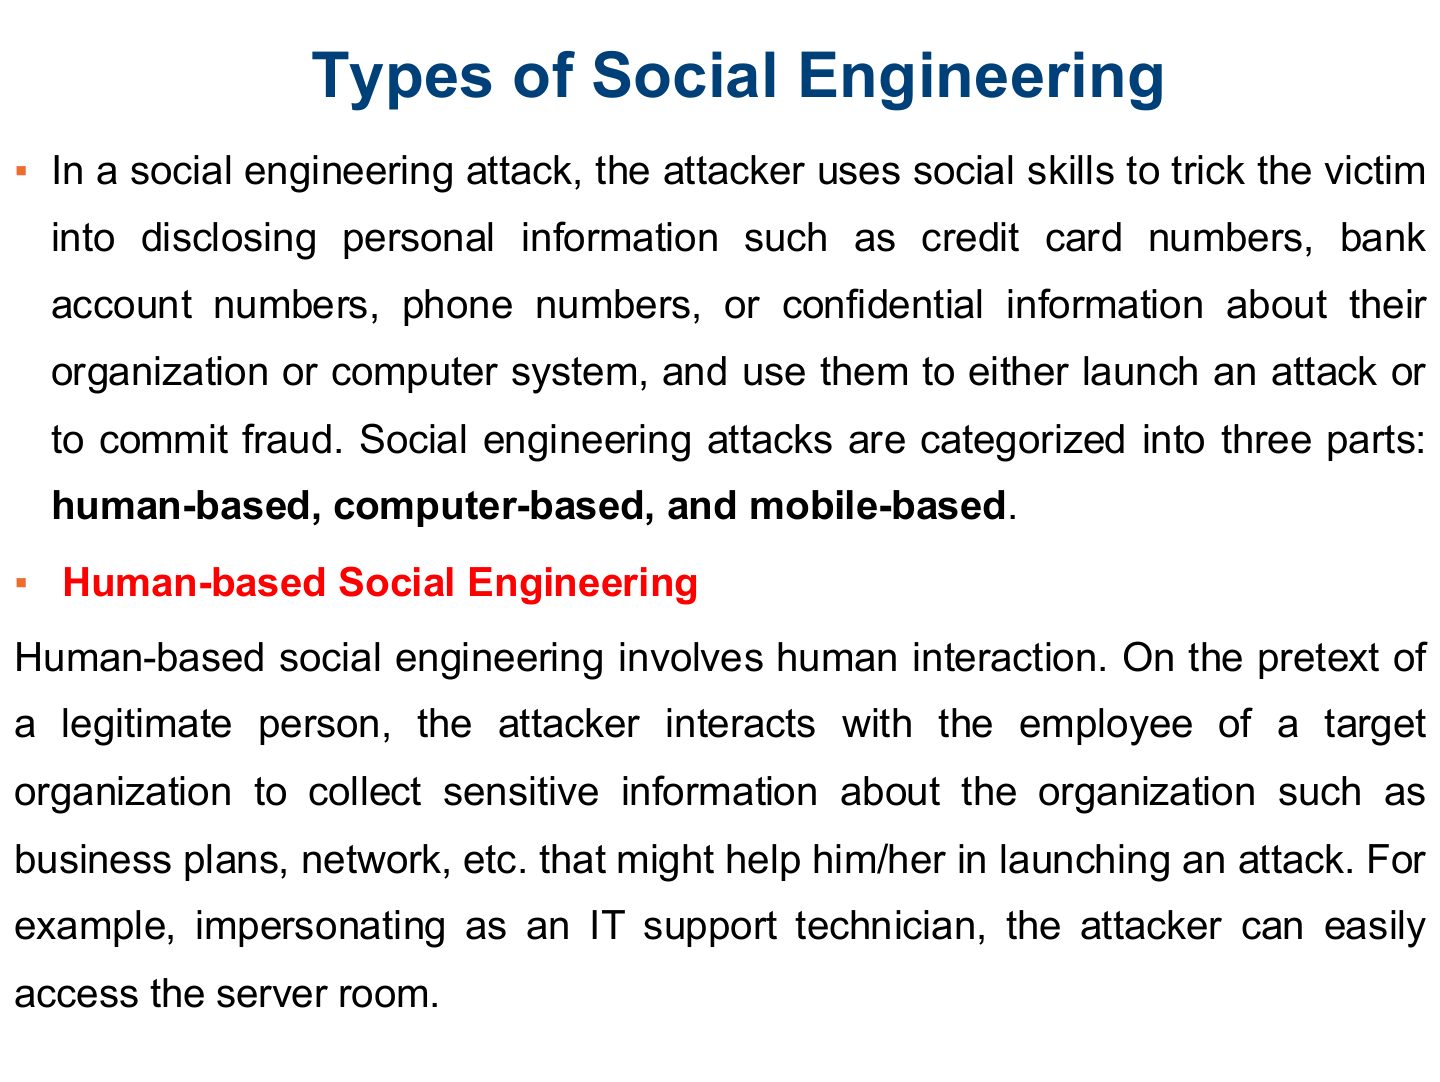
- 17 Types of Social Engineering
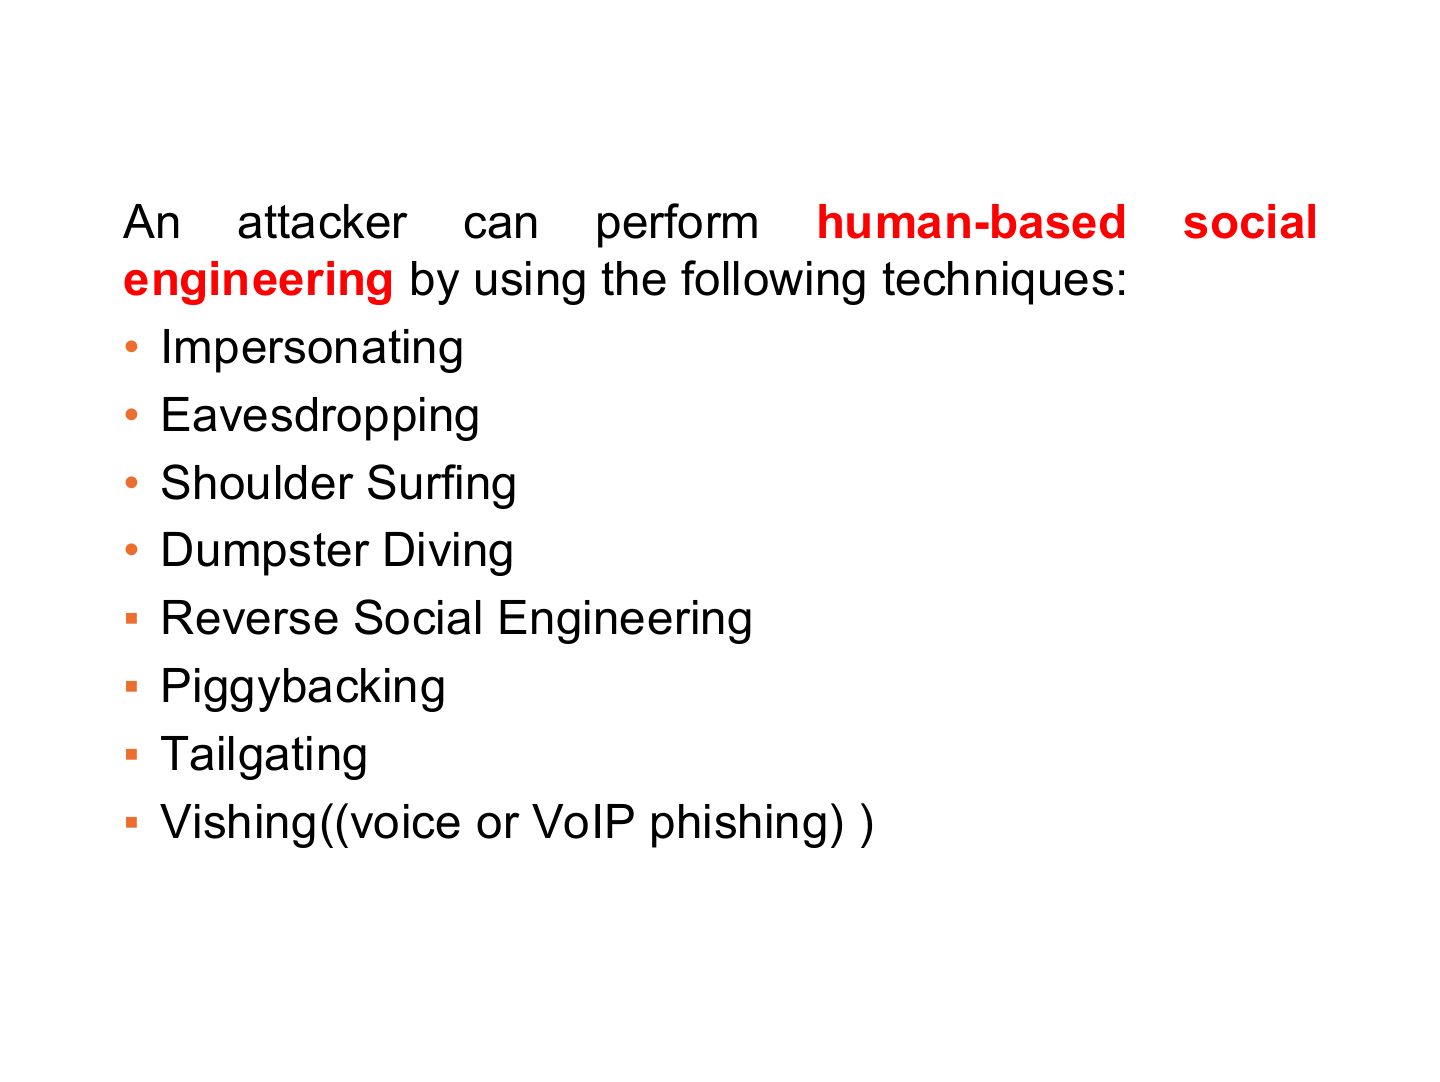
- 18 An attacker can perform human-based social engineering by using the following techniques: • Impersonating
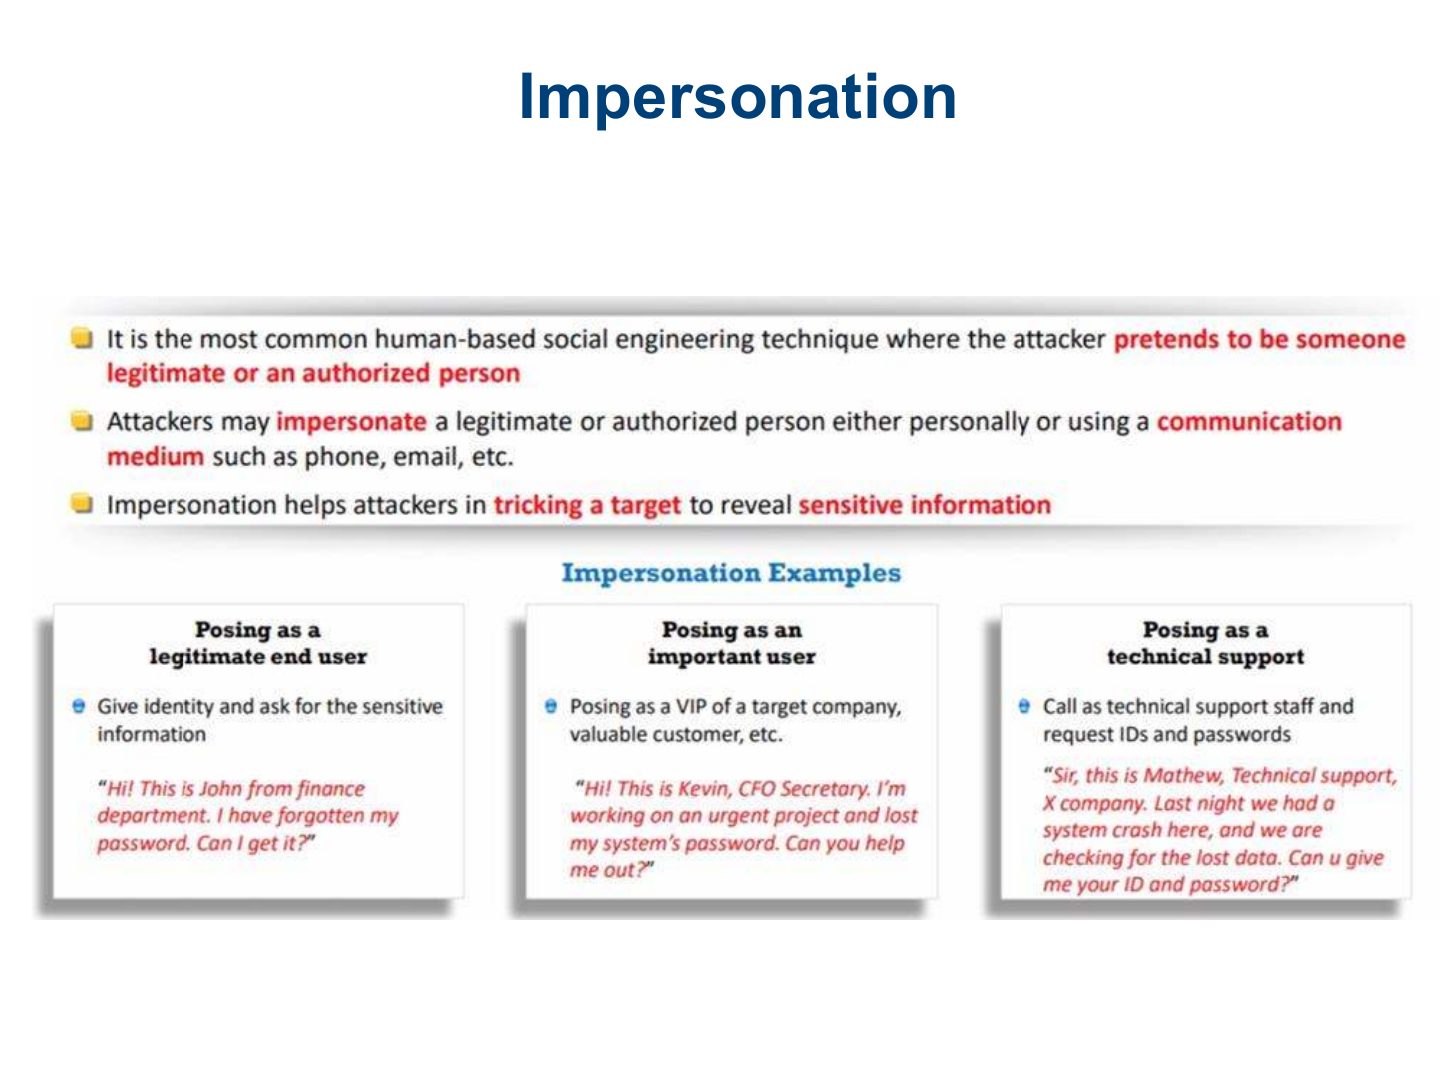
- 19 Impersonation
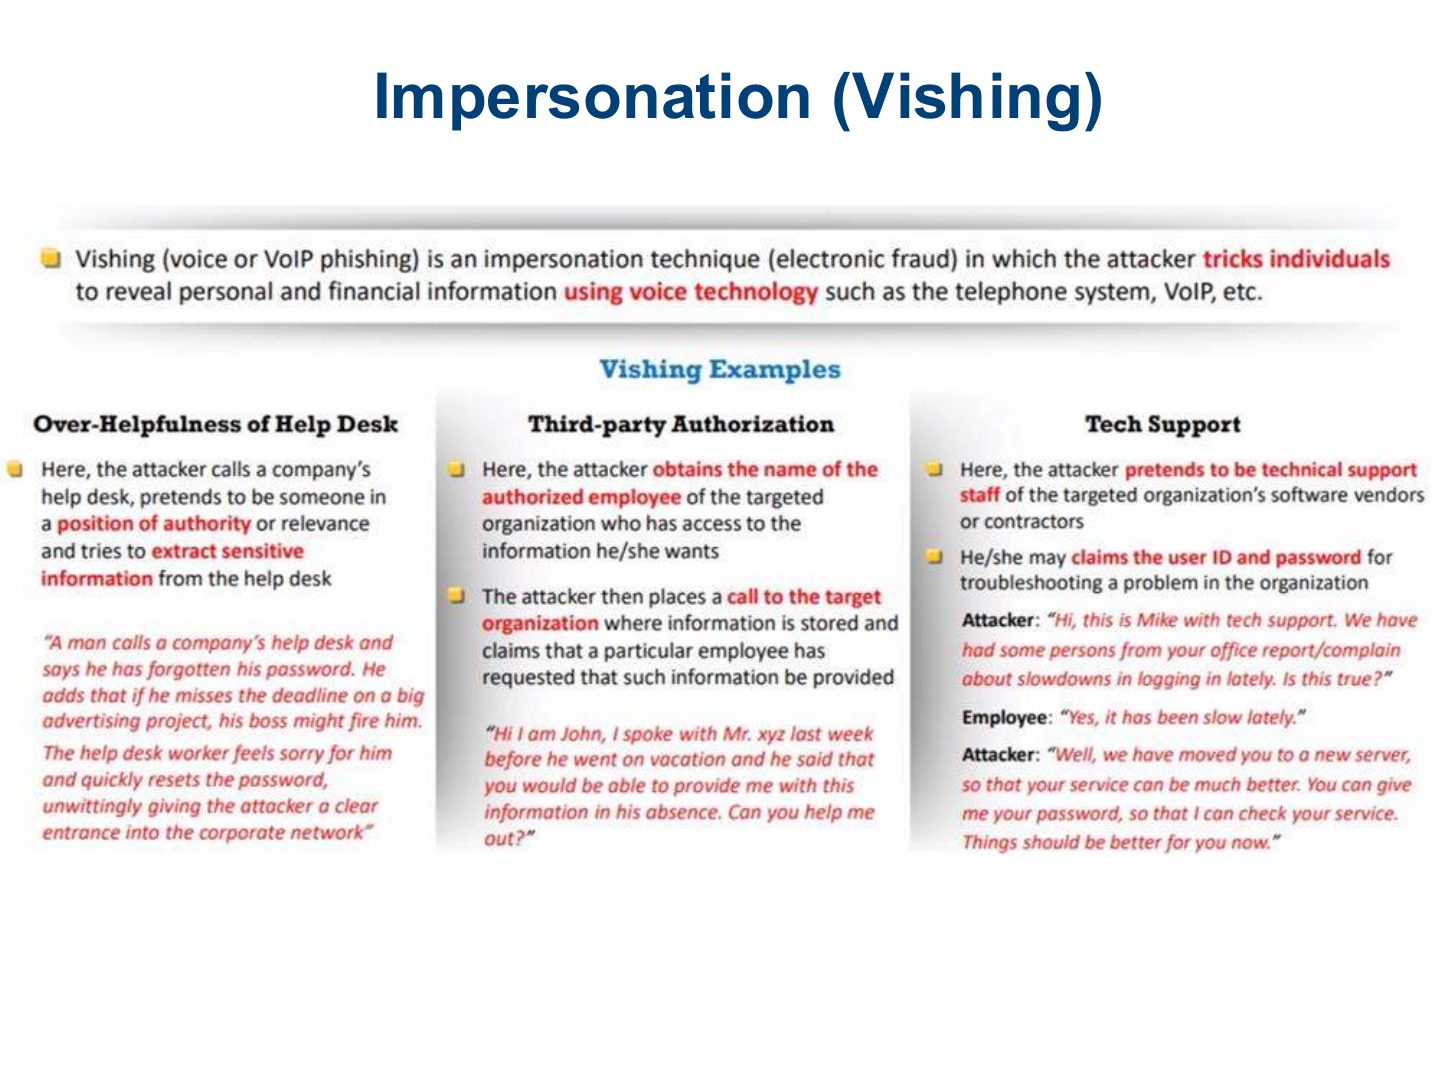
- 20 Impersonation (Vishing)
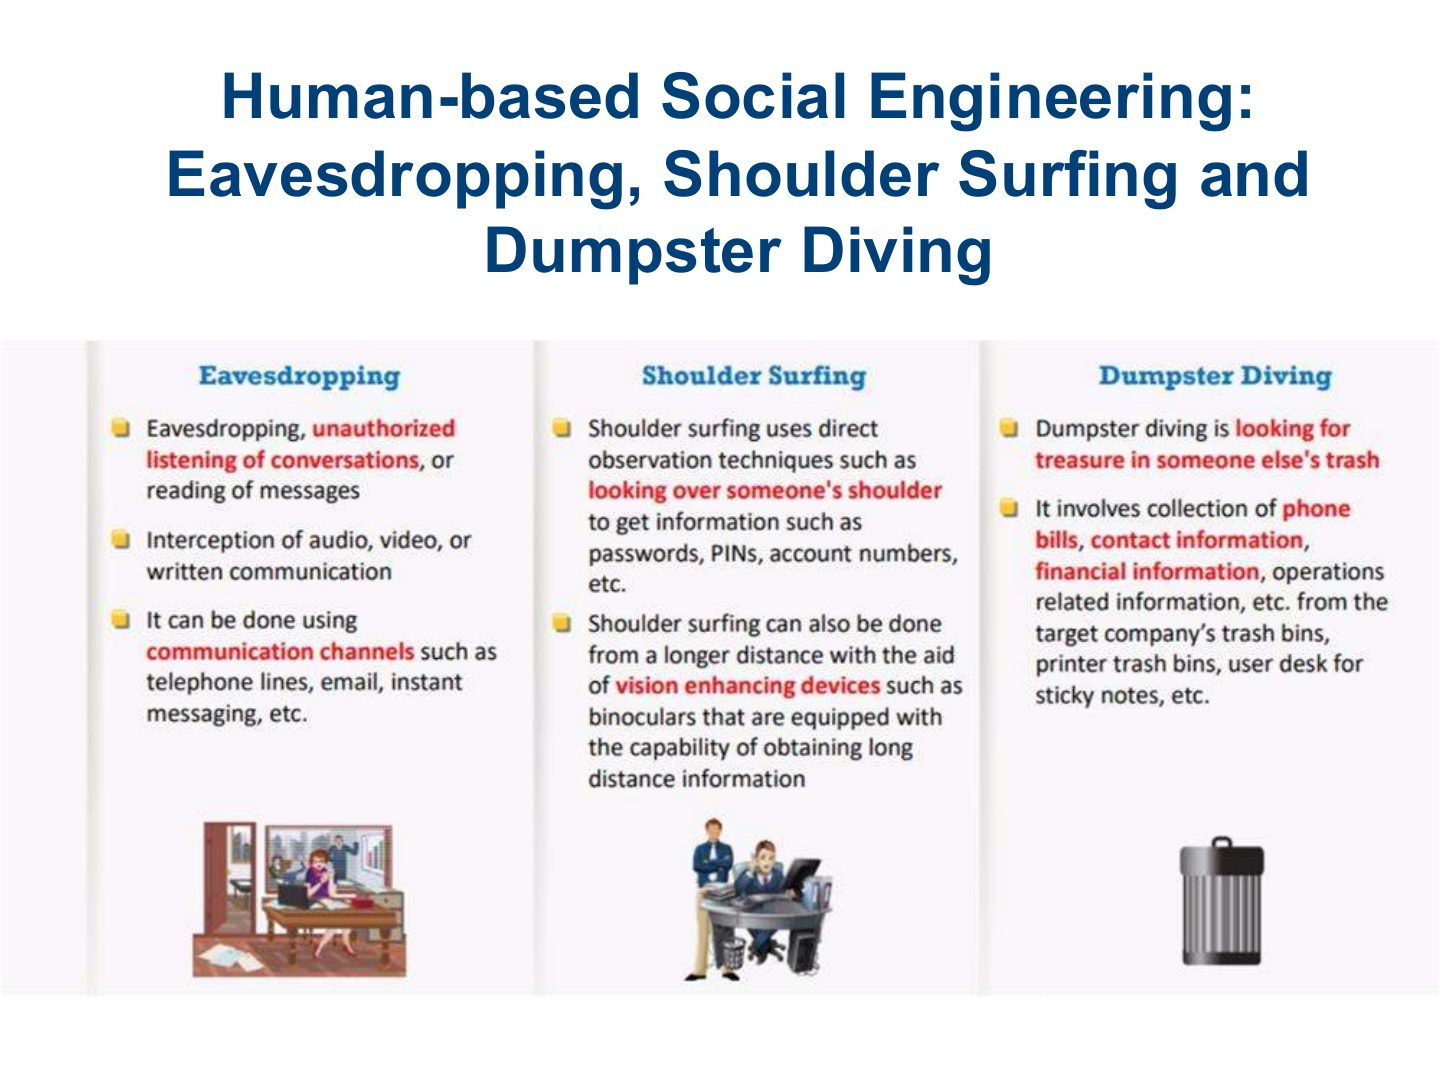
- 21 Human-based Social Engineering: Eavesdropping, Shoulder Surfing and Dumpster Diving
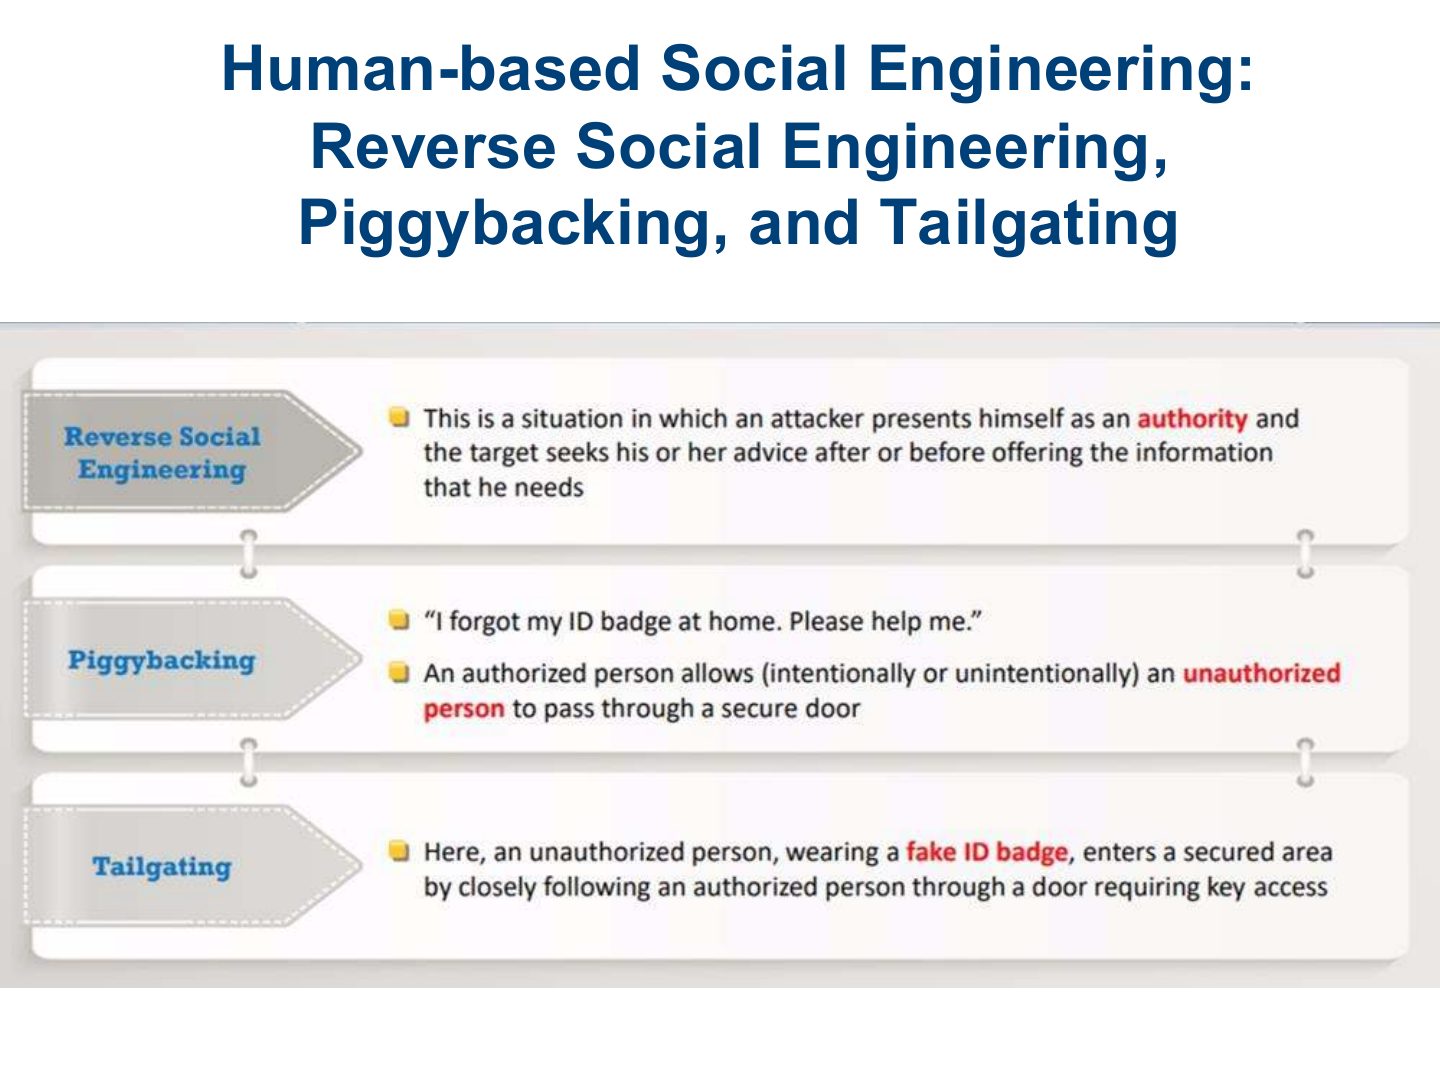
- 22 Human-based Social Engineering: Reverse Social Engineering, Piggybacking, and Tailgating
- 23 ▪ Computer-based Social Engineering
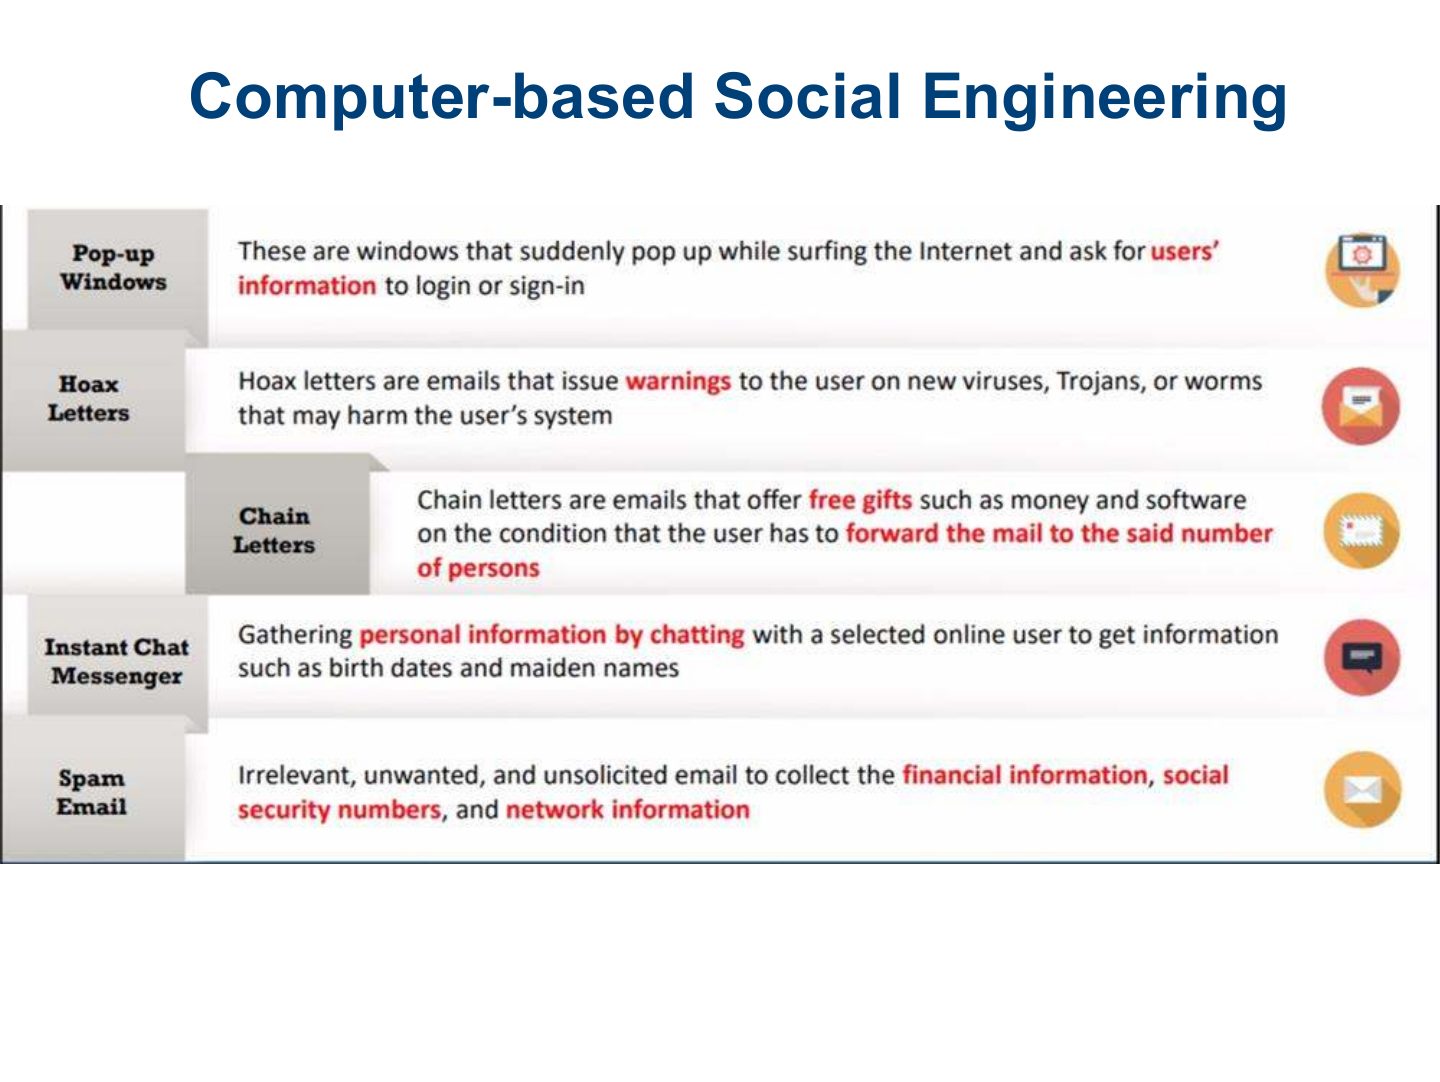
- 24 Computer-based Social Engineering
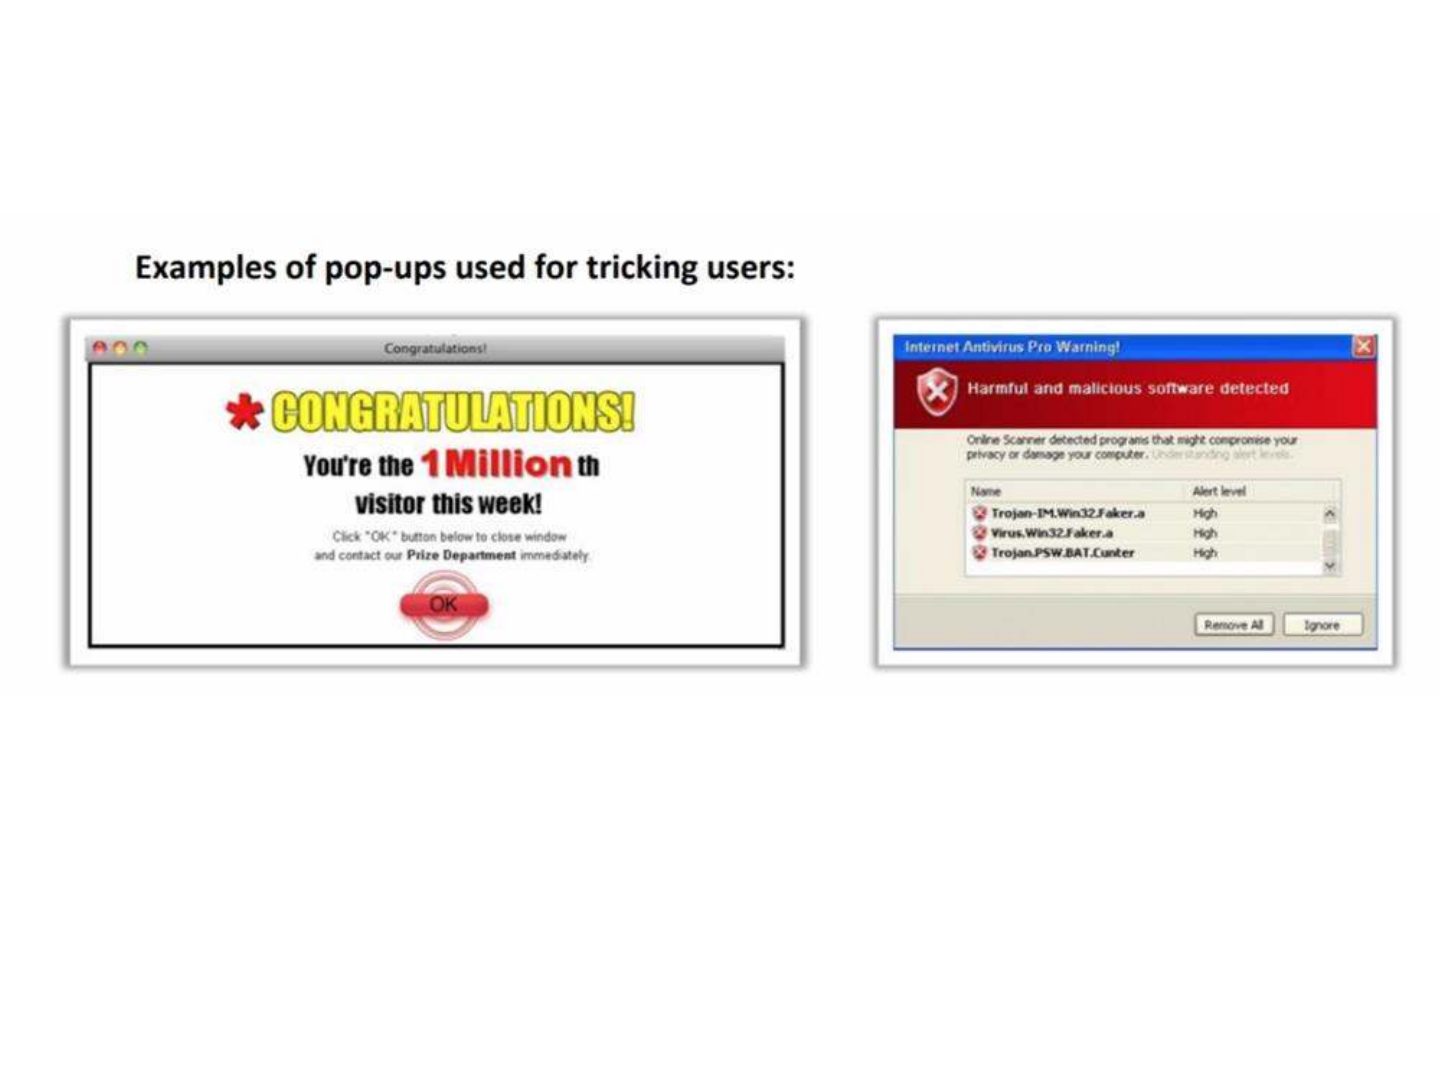
- 25 Slide 25
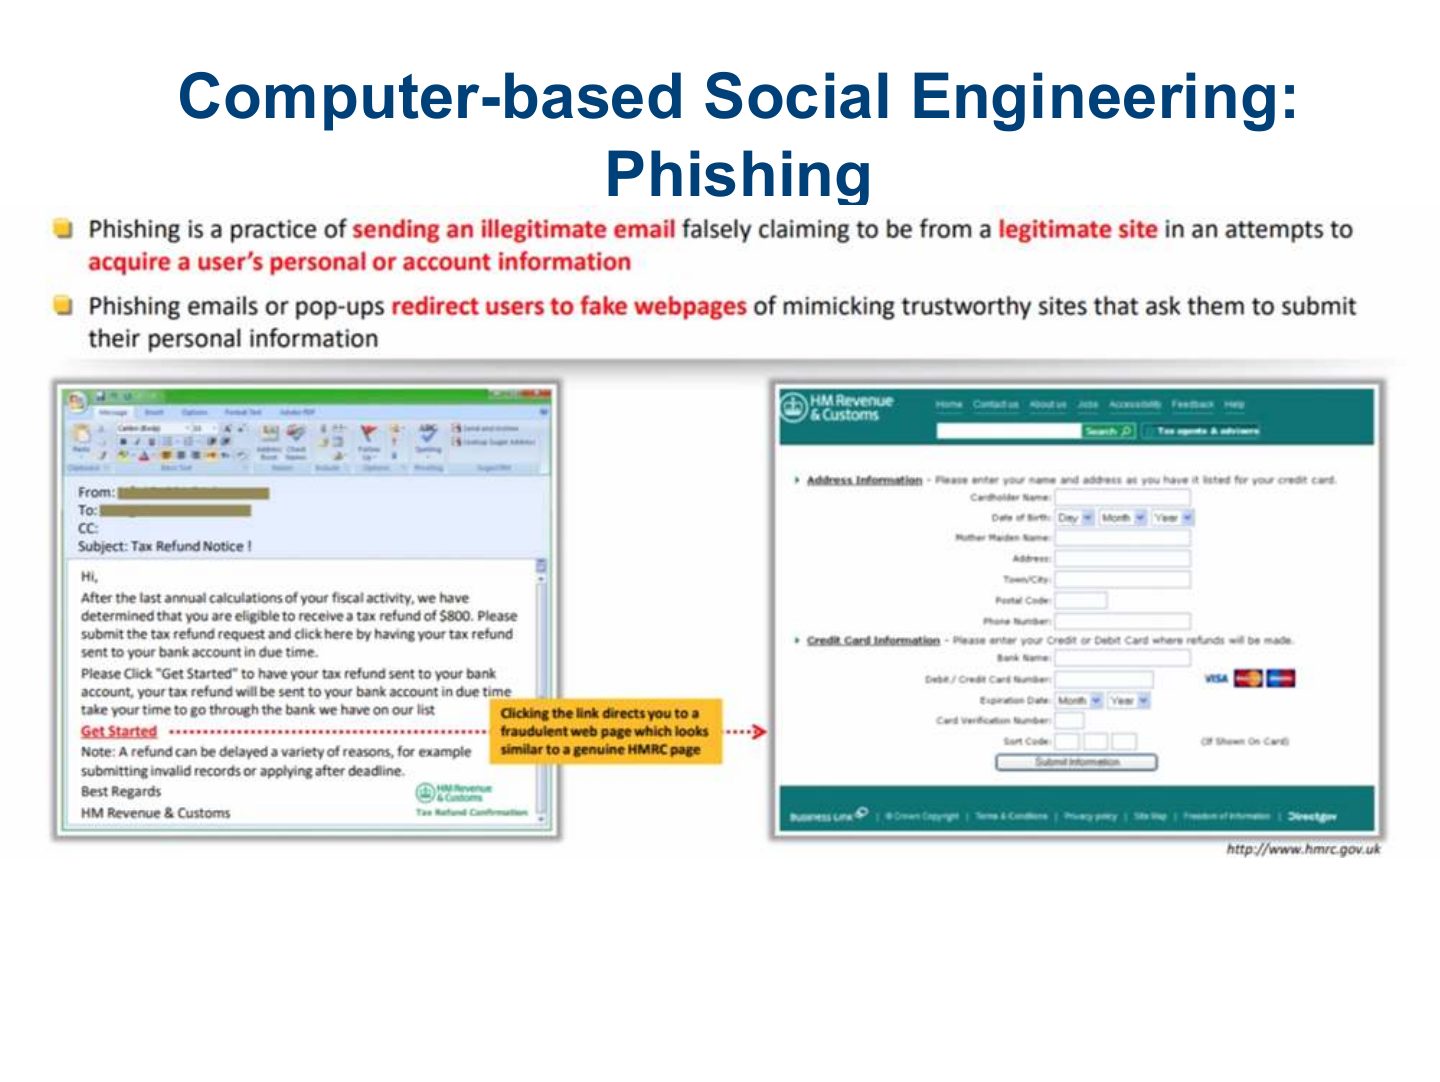
- 26 Computer-based Social Engineering: Phishing
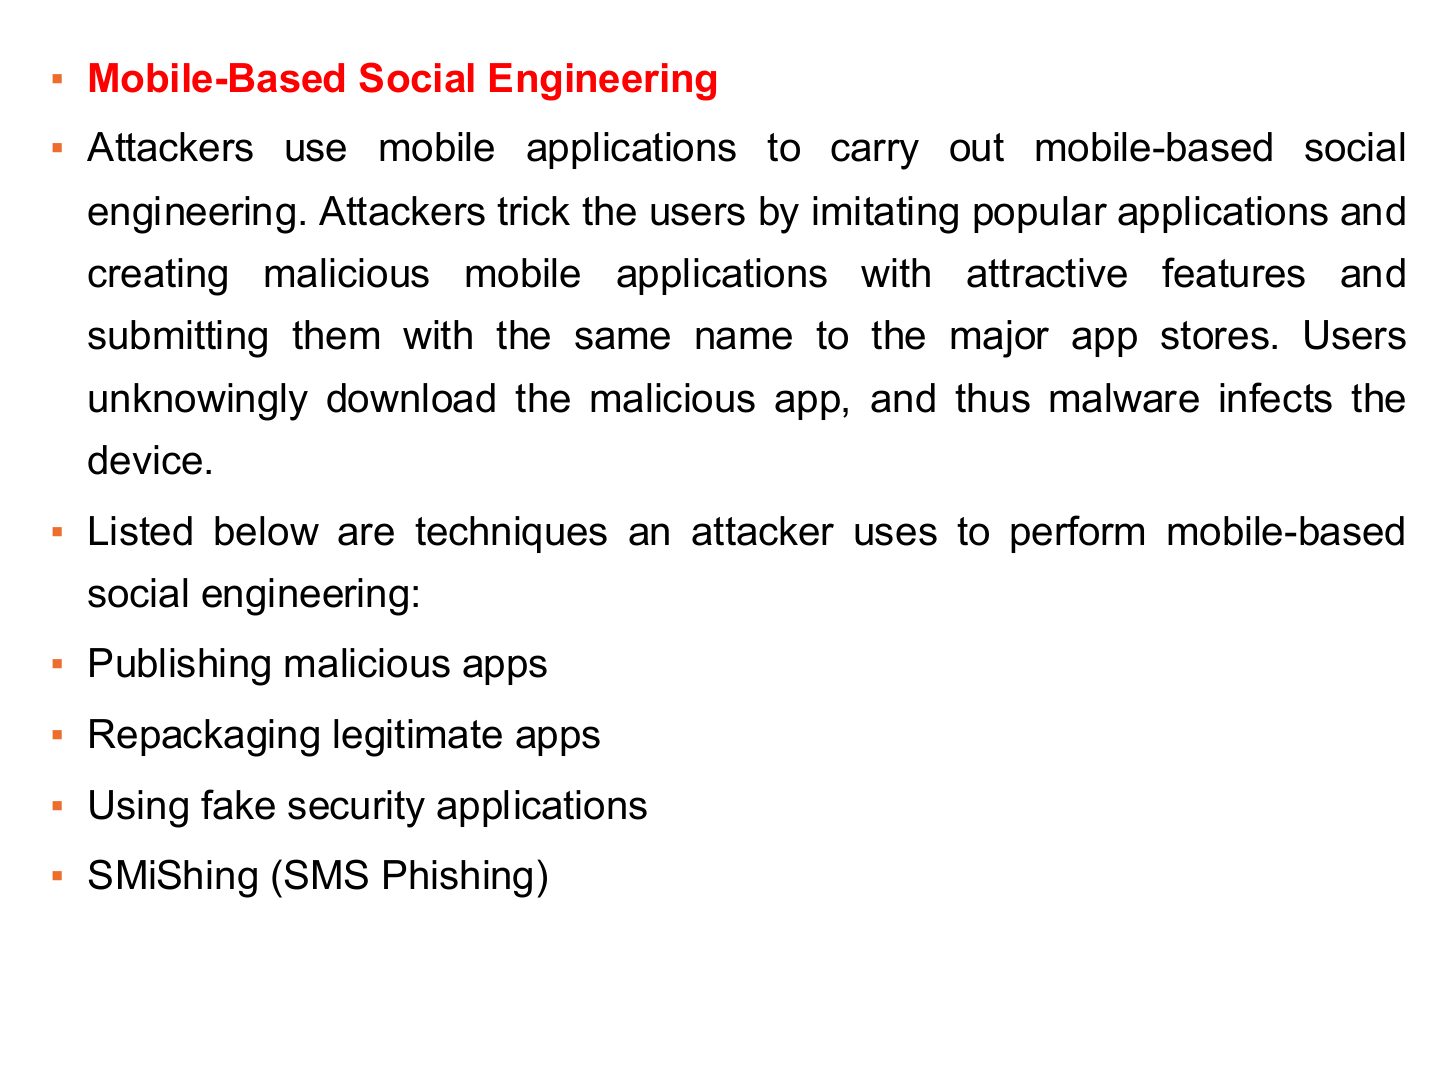
- 27 ▪ Mobile-Based Social Engineering
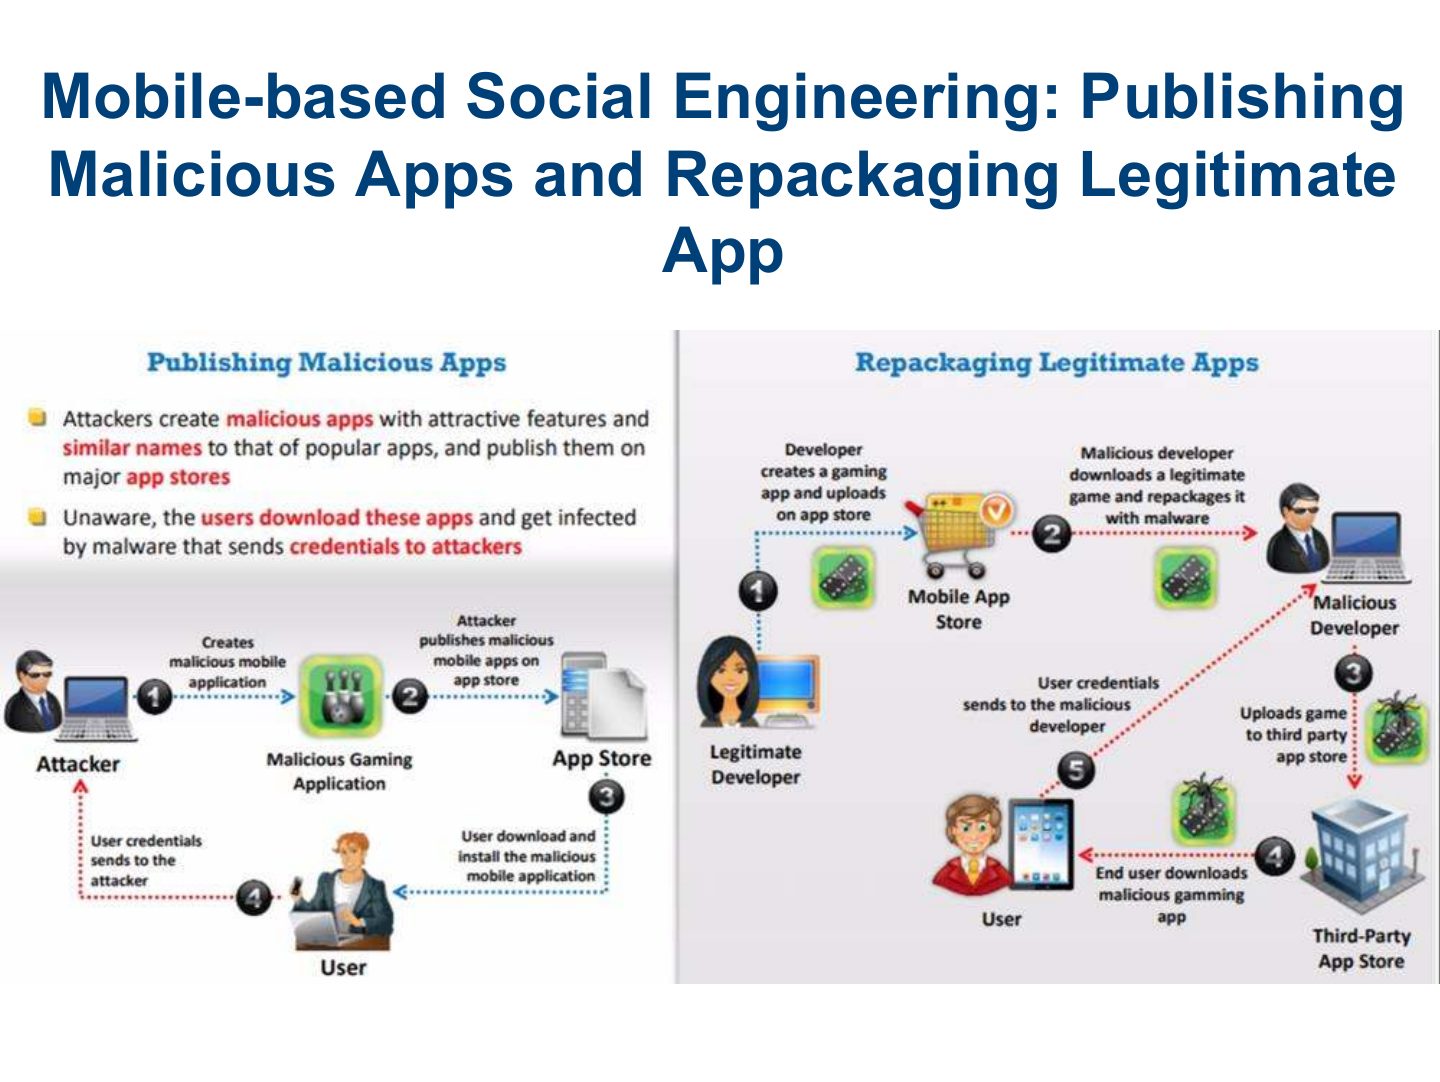
- 28 Mobile-based Social Engineering: Publishing Malicious Apps and Repackaging Legitimate App
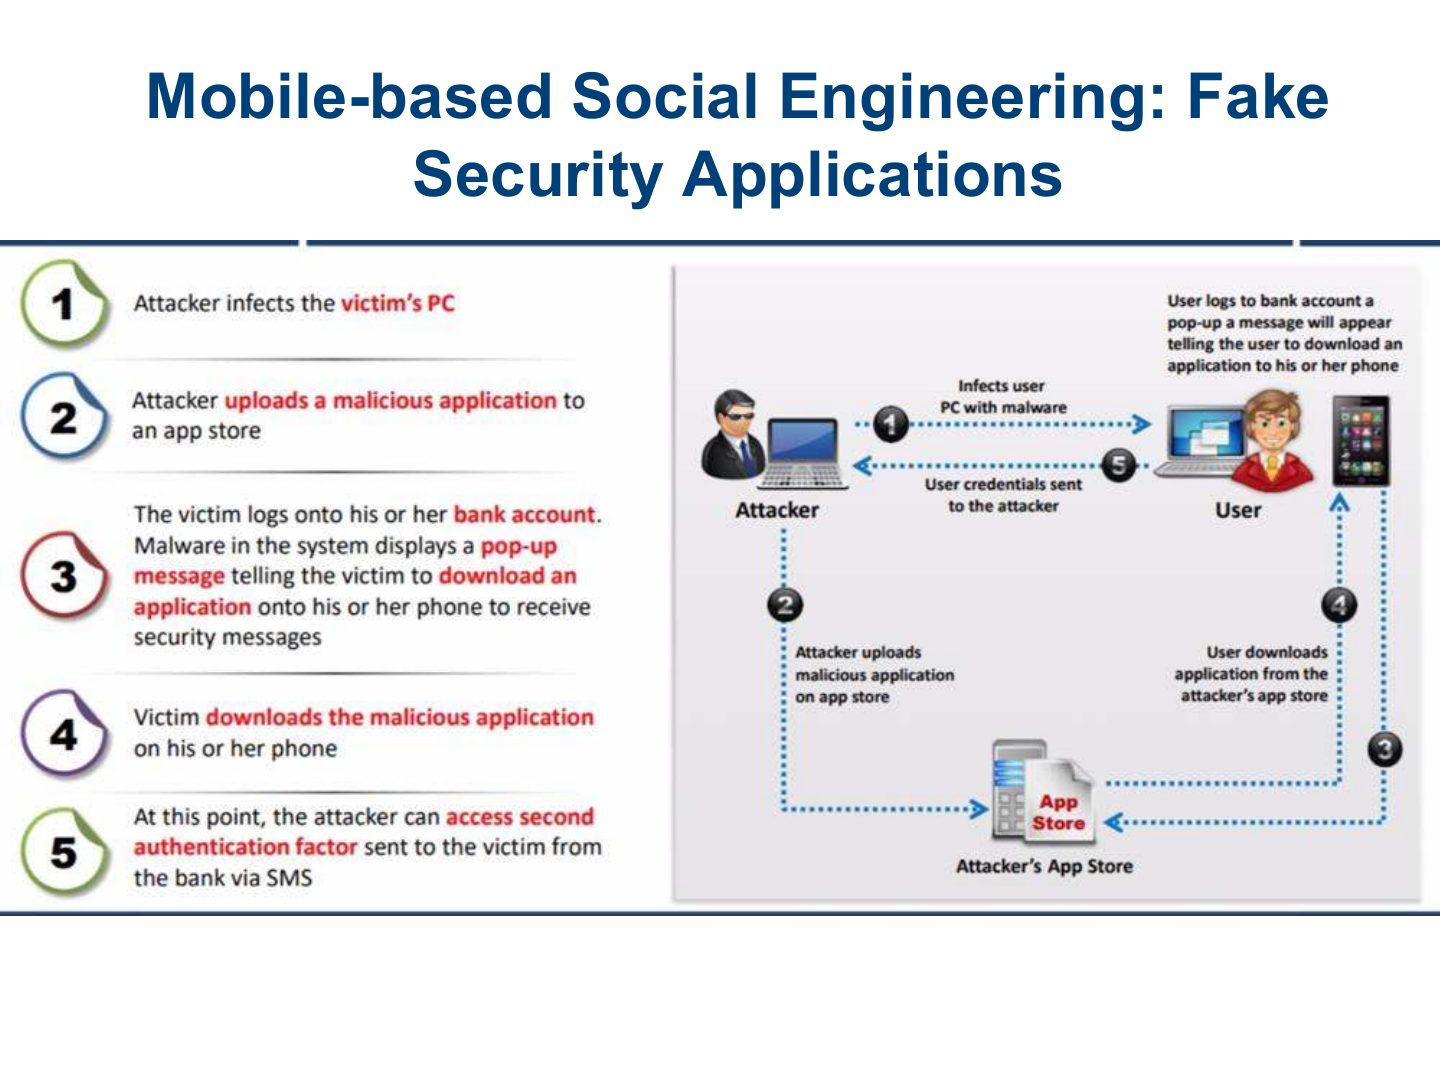
- 29 Mobile-based Social Engineering: Fake Security Applications
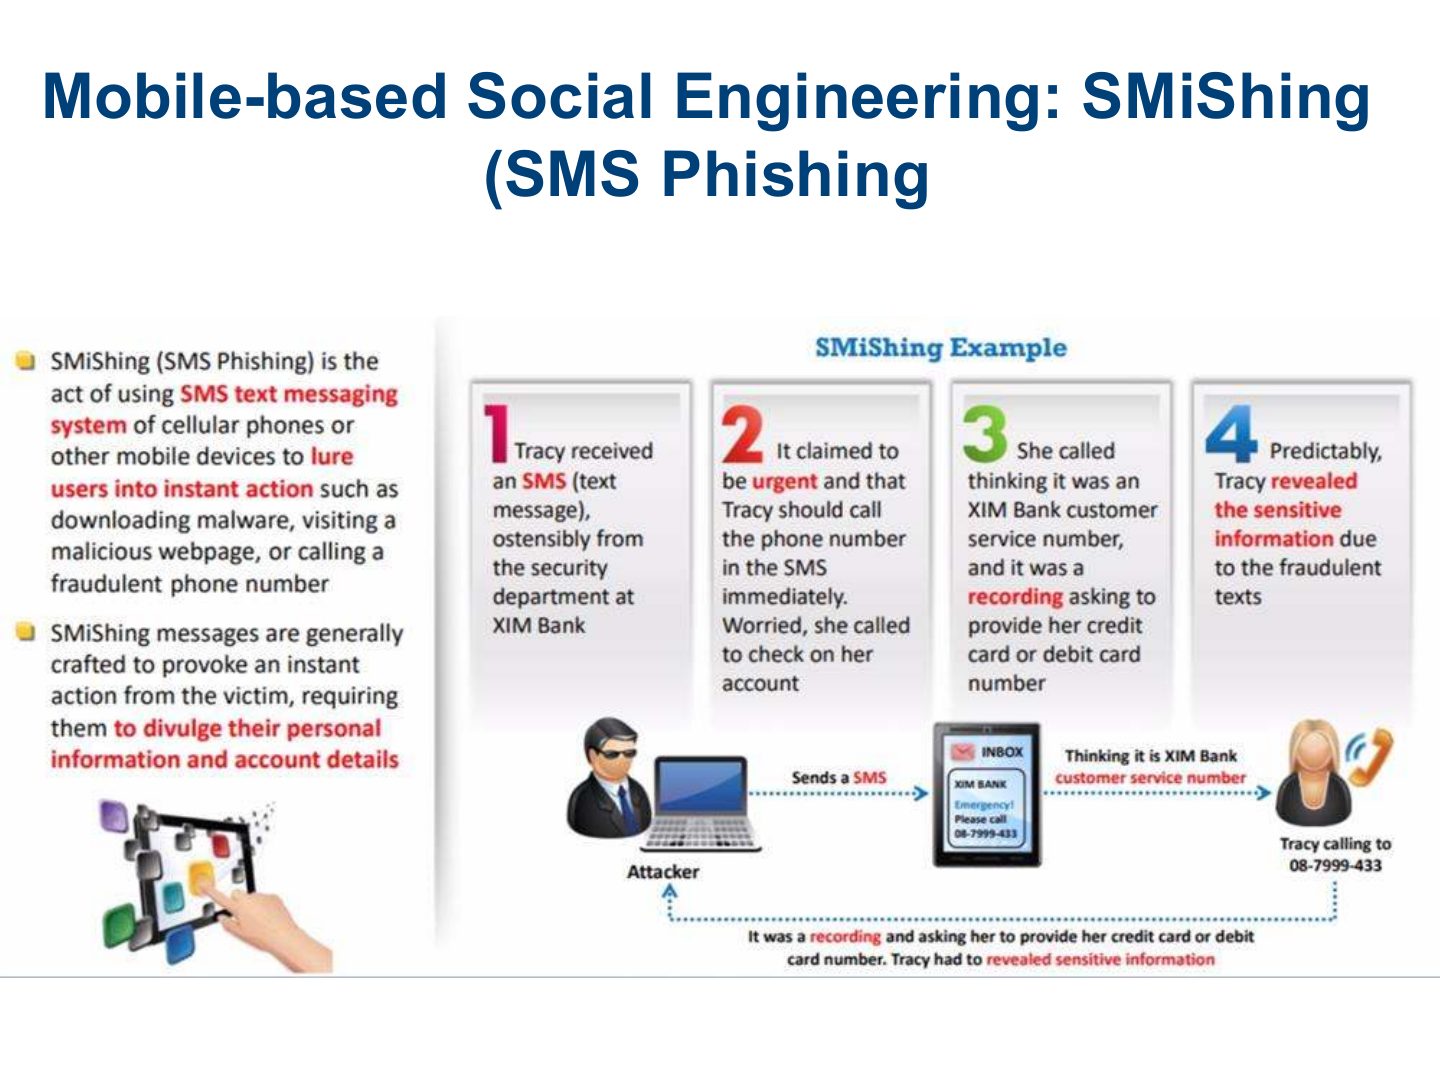
- 30 Mobile-based Social Engineering: SMiShing (SMS Phishing
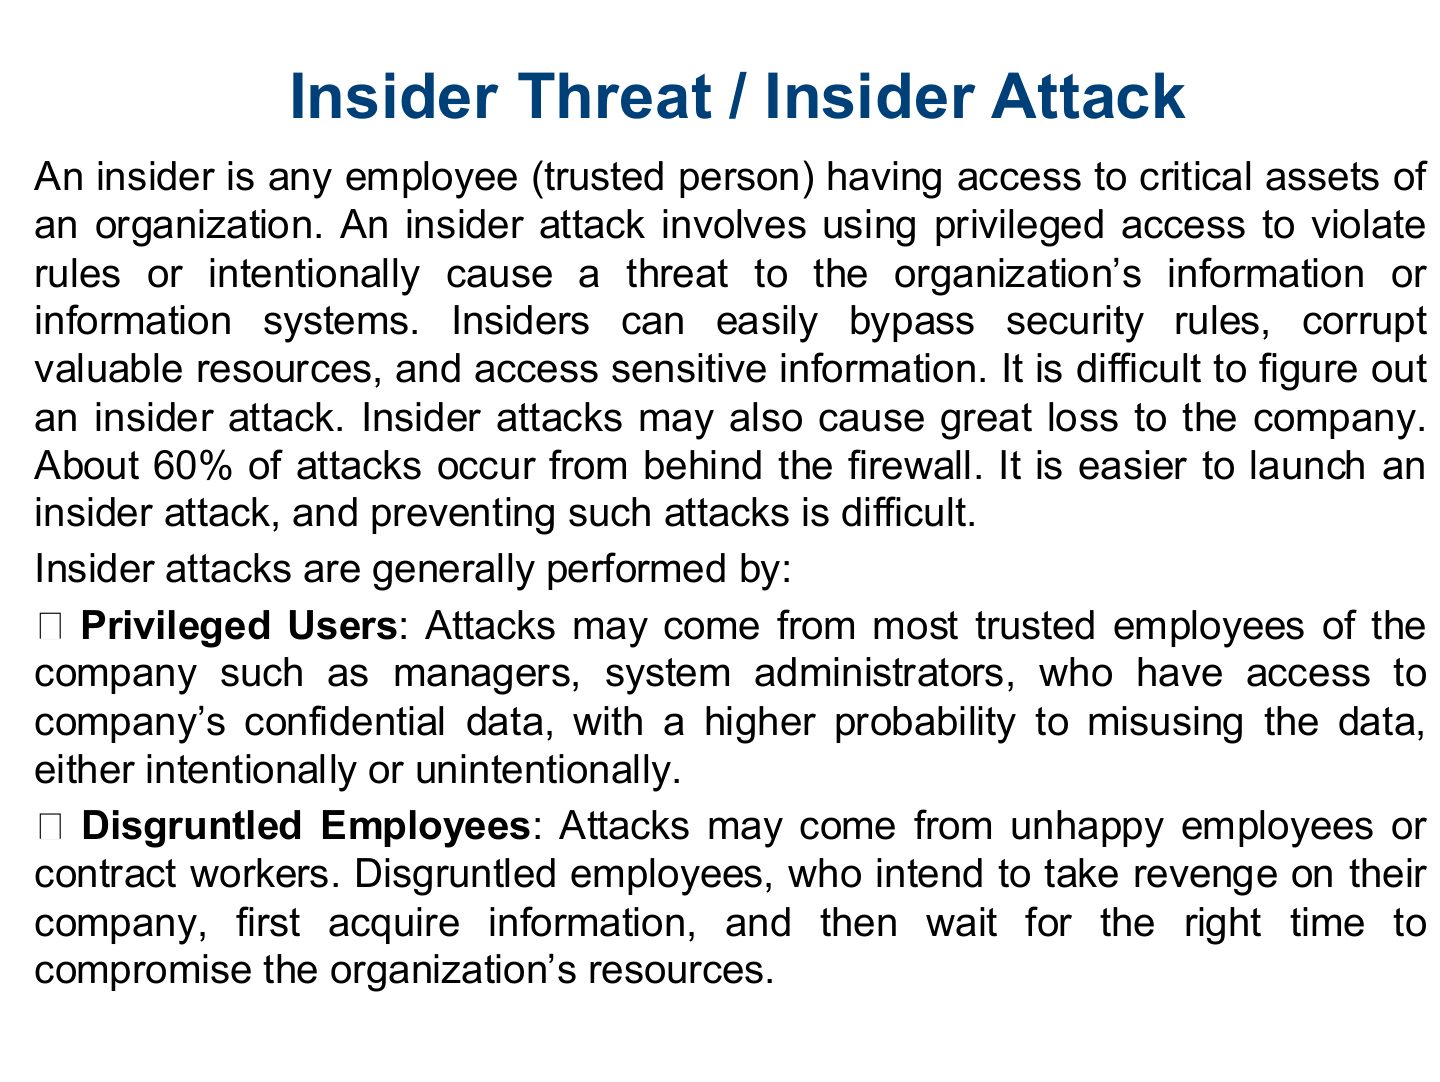
- 31 Insider Threat / Insider Attack
- 32 Terminated Employees : Some employees take valuable information about the company with them when terminated. These employees access company s data even after termination using backdoors, malware, or their old ’ credentials because they are not disabled.
- 33 Companies where insider attacks are common include credit card companies, health-care companies, network service providers, as well as financial and exchange service providers.
- 34 Become Future Competitor Current employees may plan to
- 35 Countermeasures
- 36 Social Engineering Countermeasures
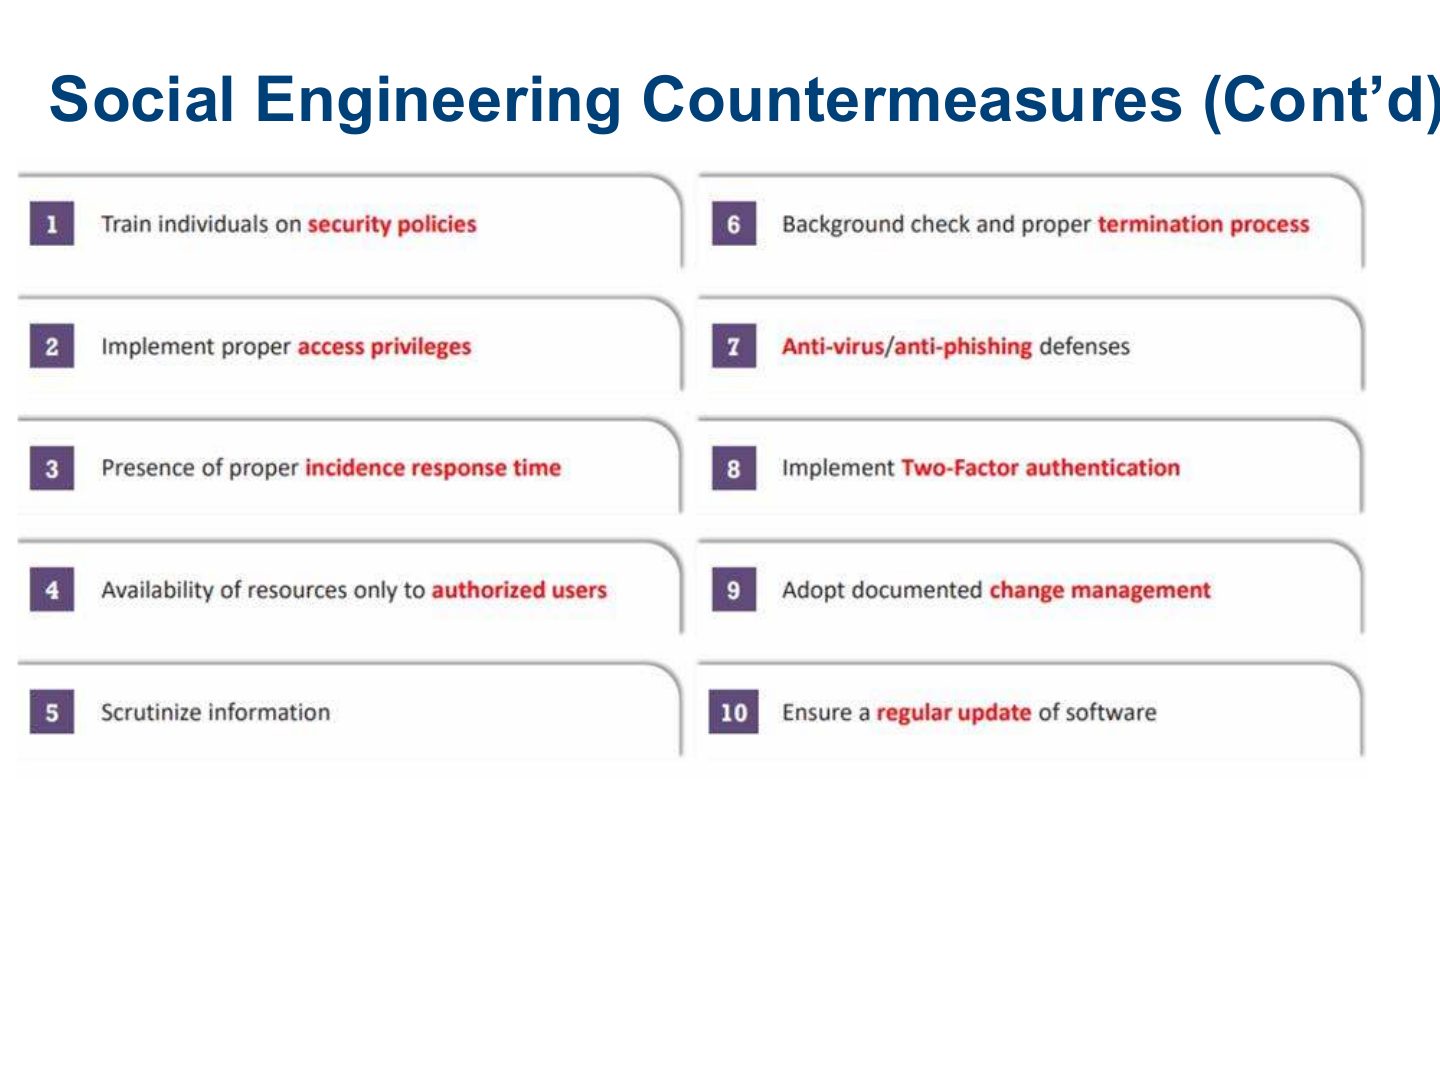
- 37 Social Engineering Countermeasures (Cont’d)
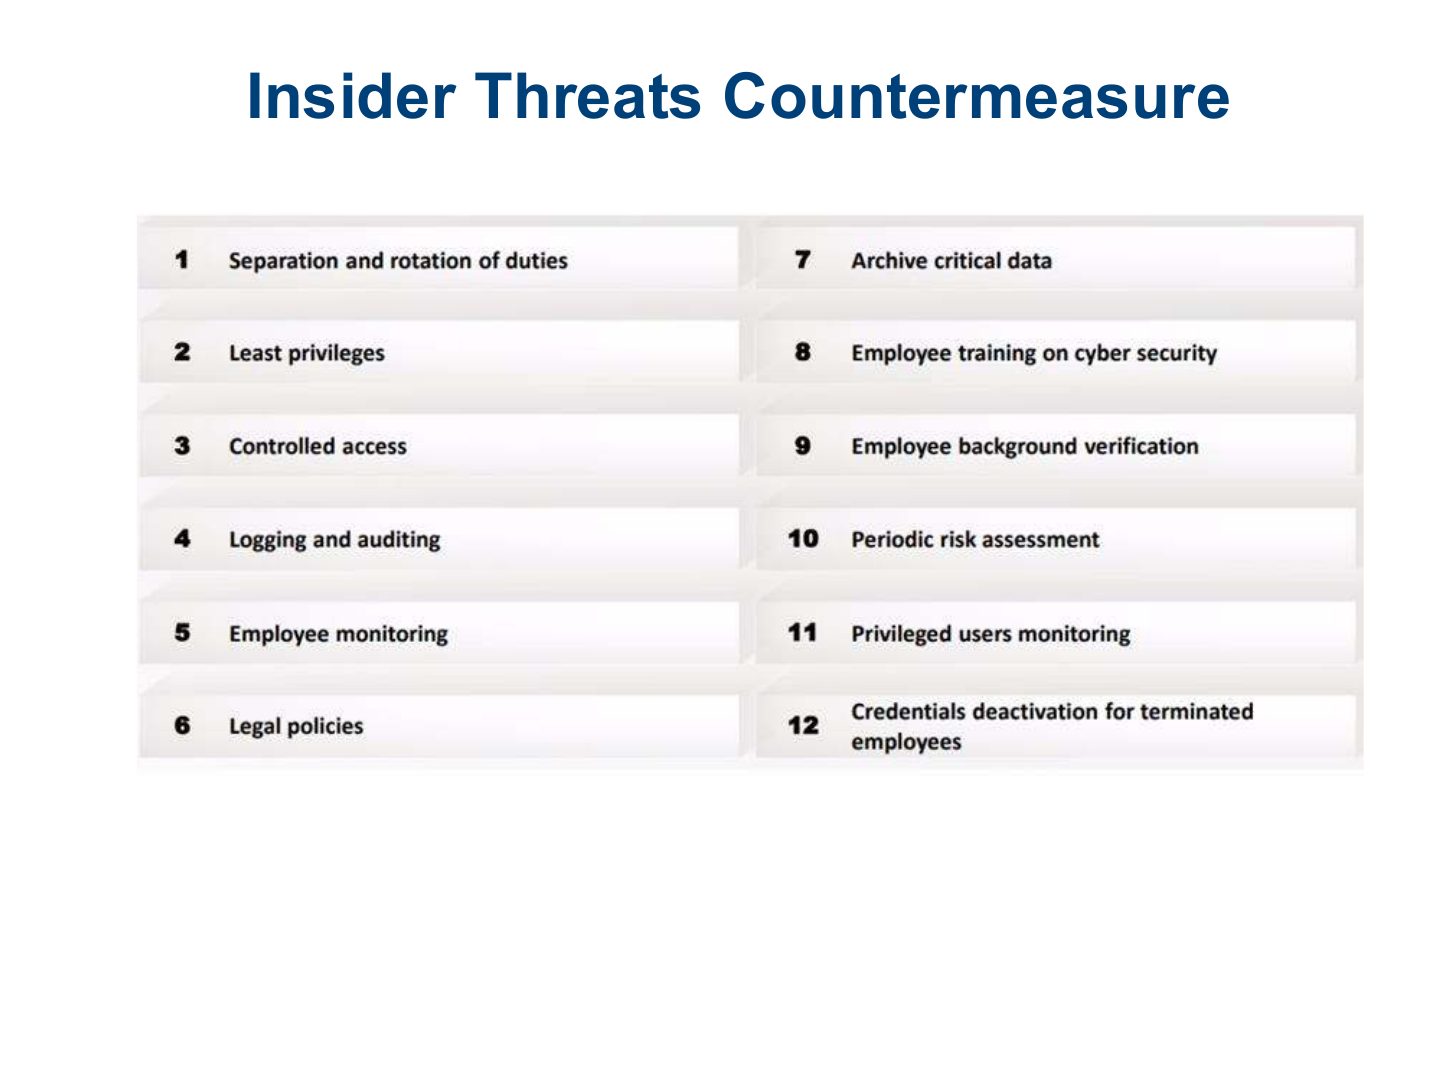
- 38 Insider Threats Countermeasure
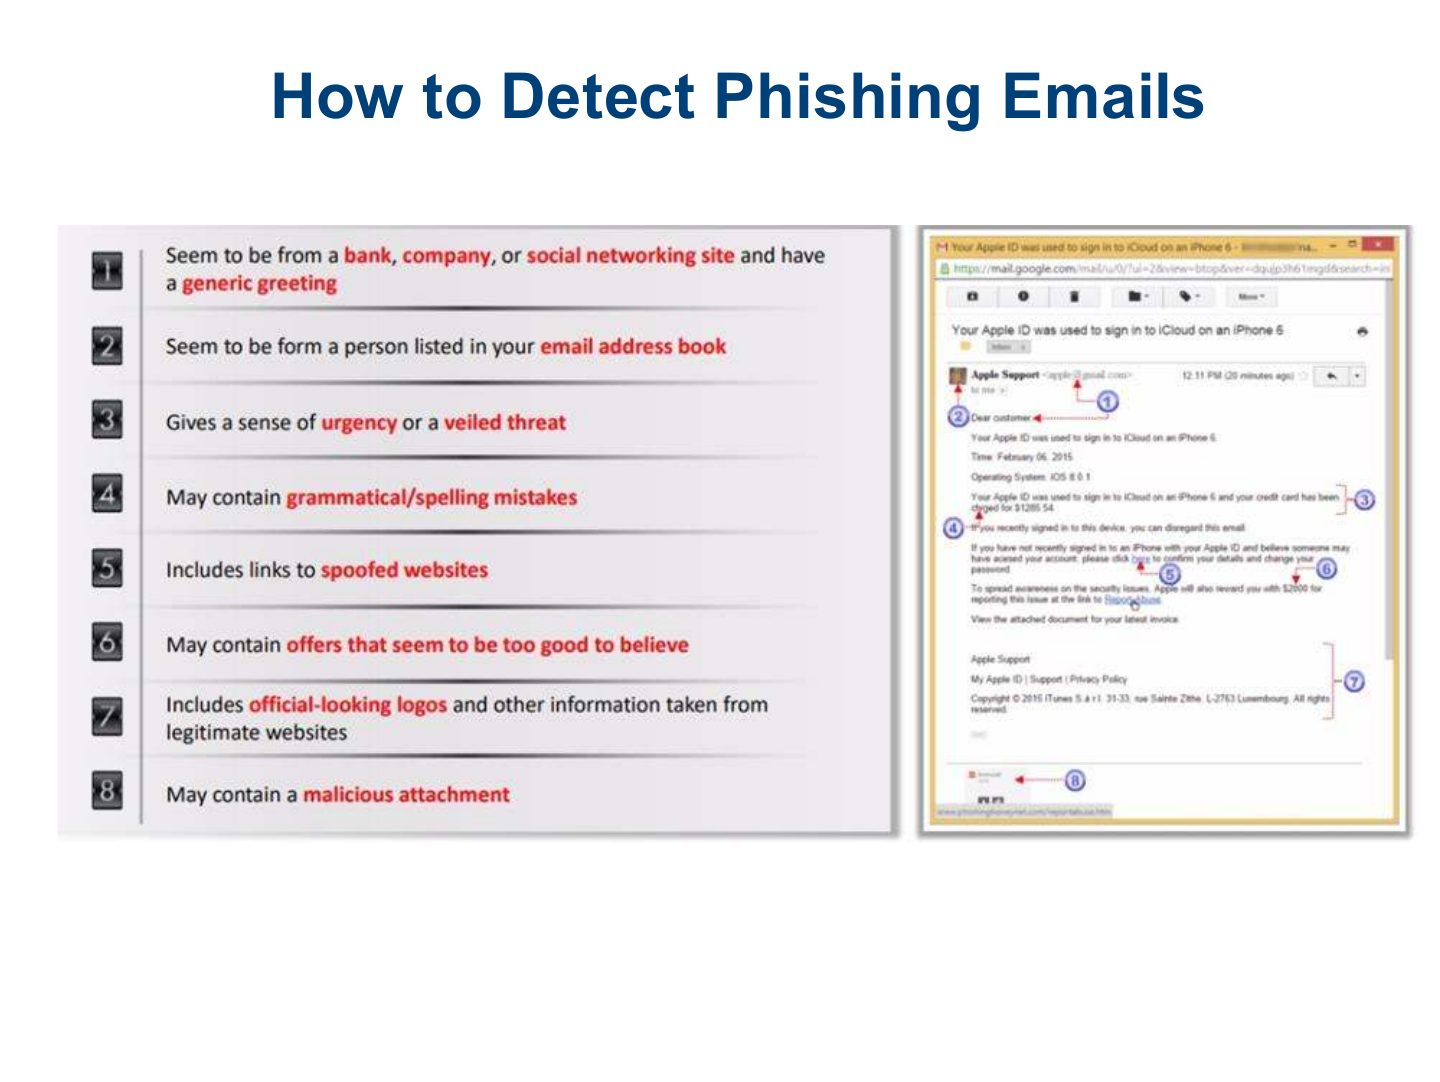
- 39 How to Detect Phishing Emails
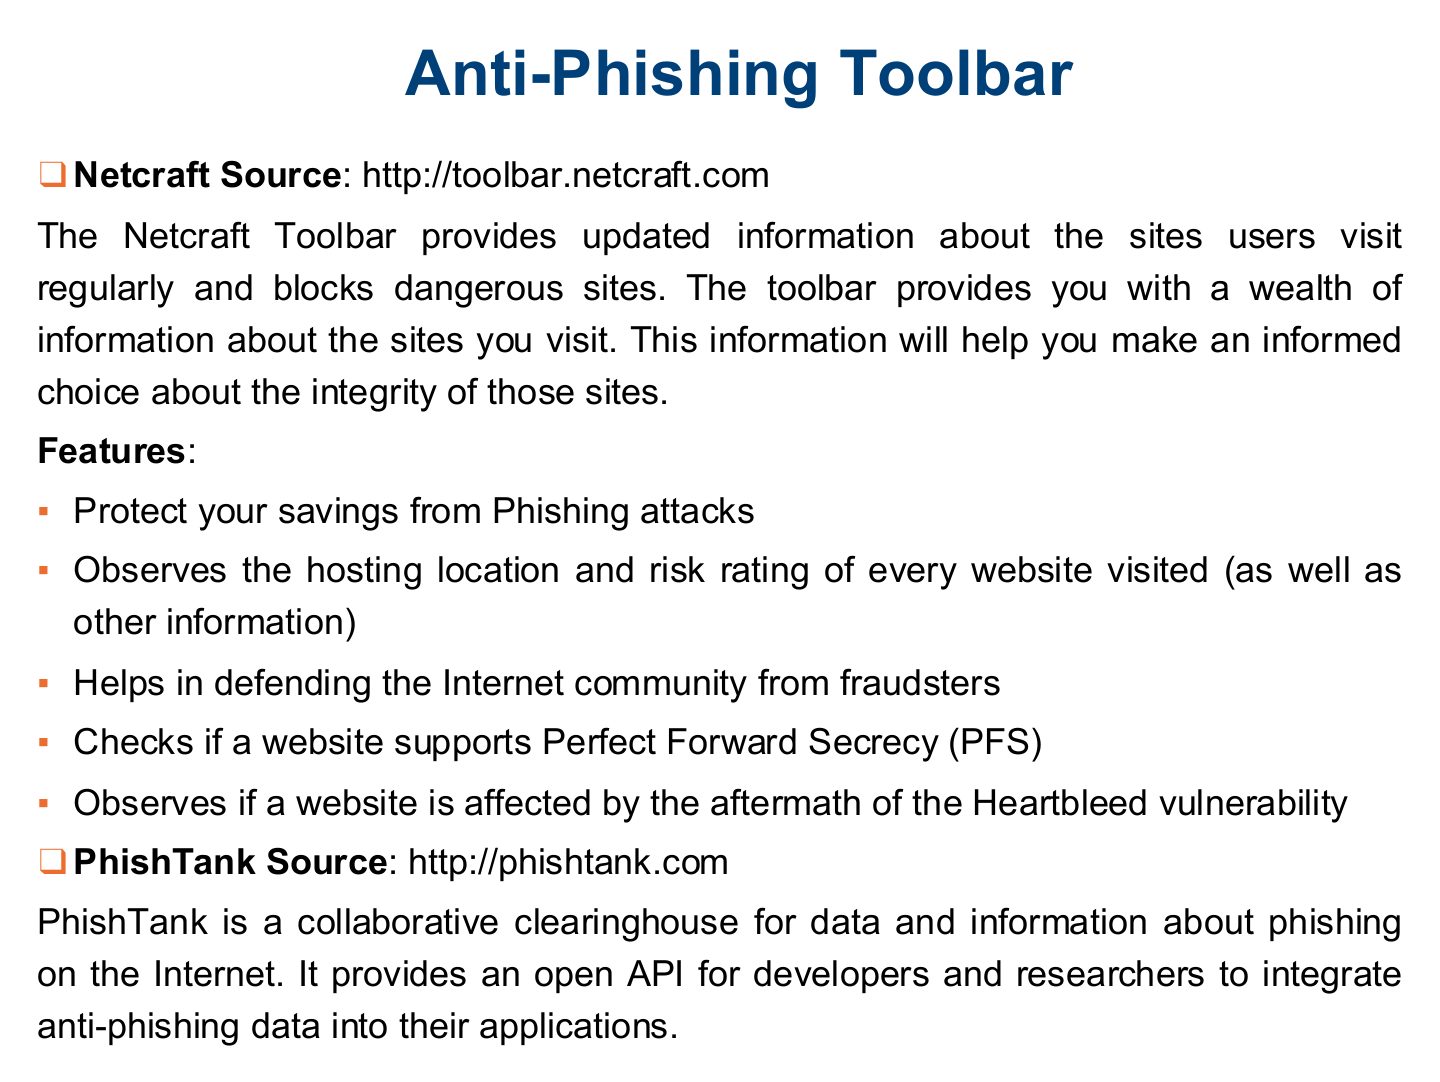
- 40 Anti-Phishing Toolbar
- 41 Social Engineering Pen Testing
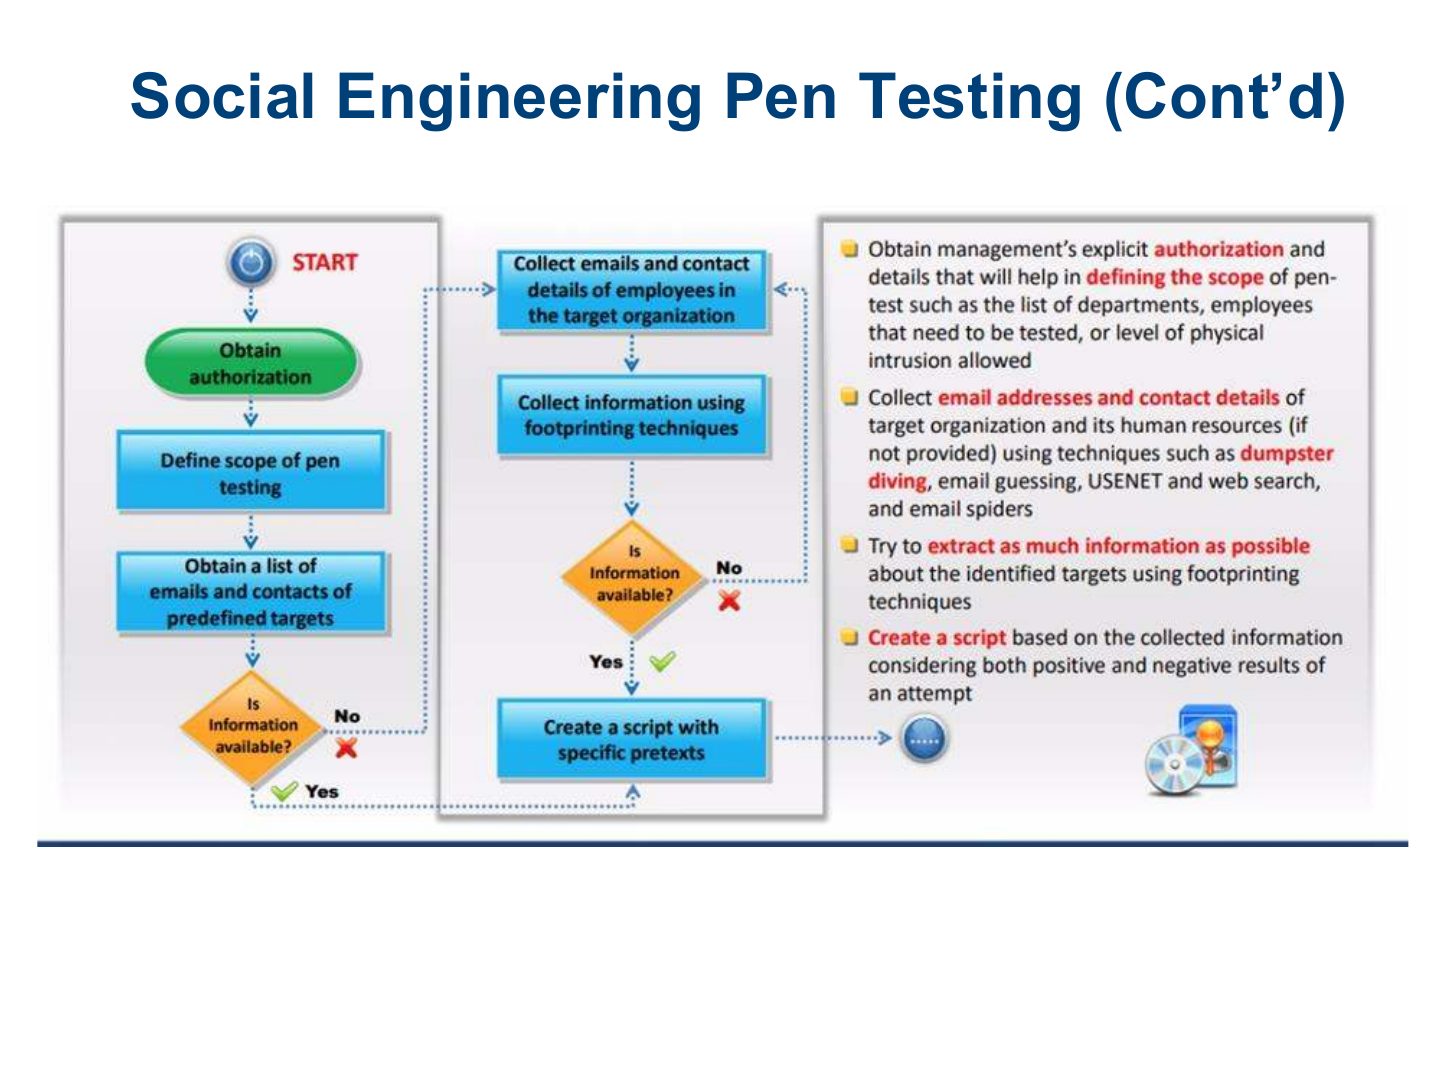
- 42 Social Engineering Pen Testing (Cont’d)
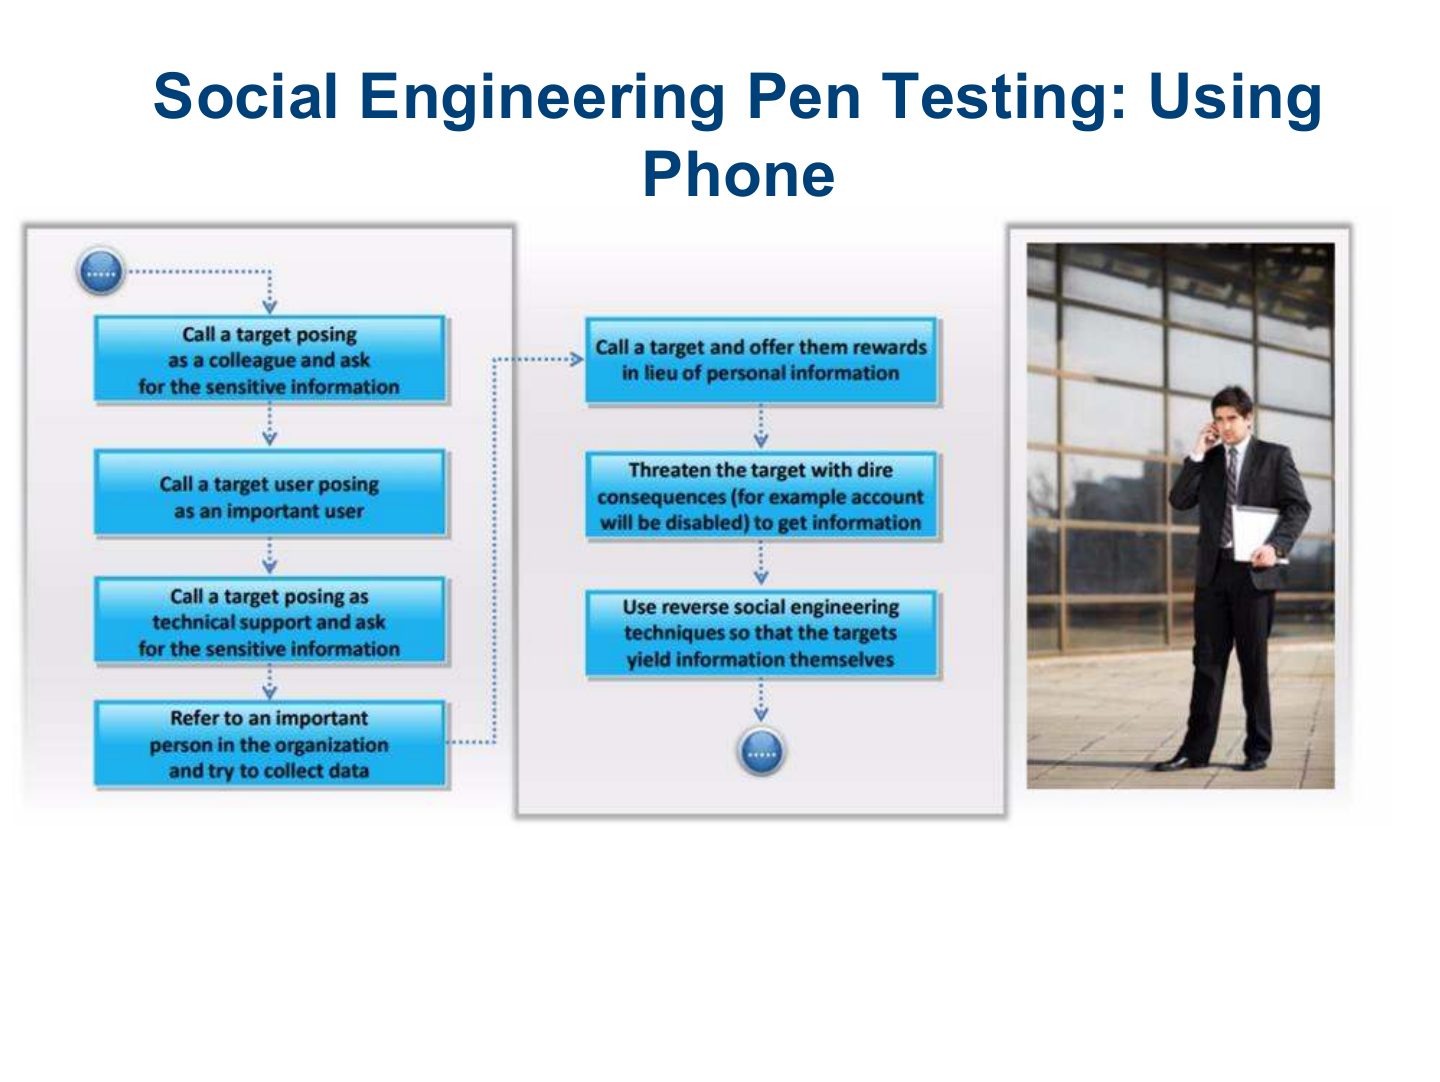
- 43 Social Engineering Pen Testing: Using Phone
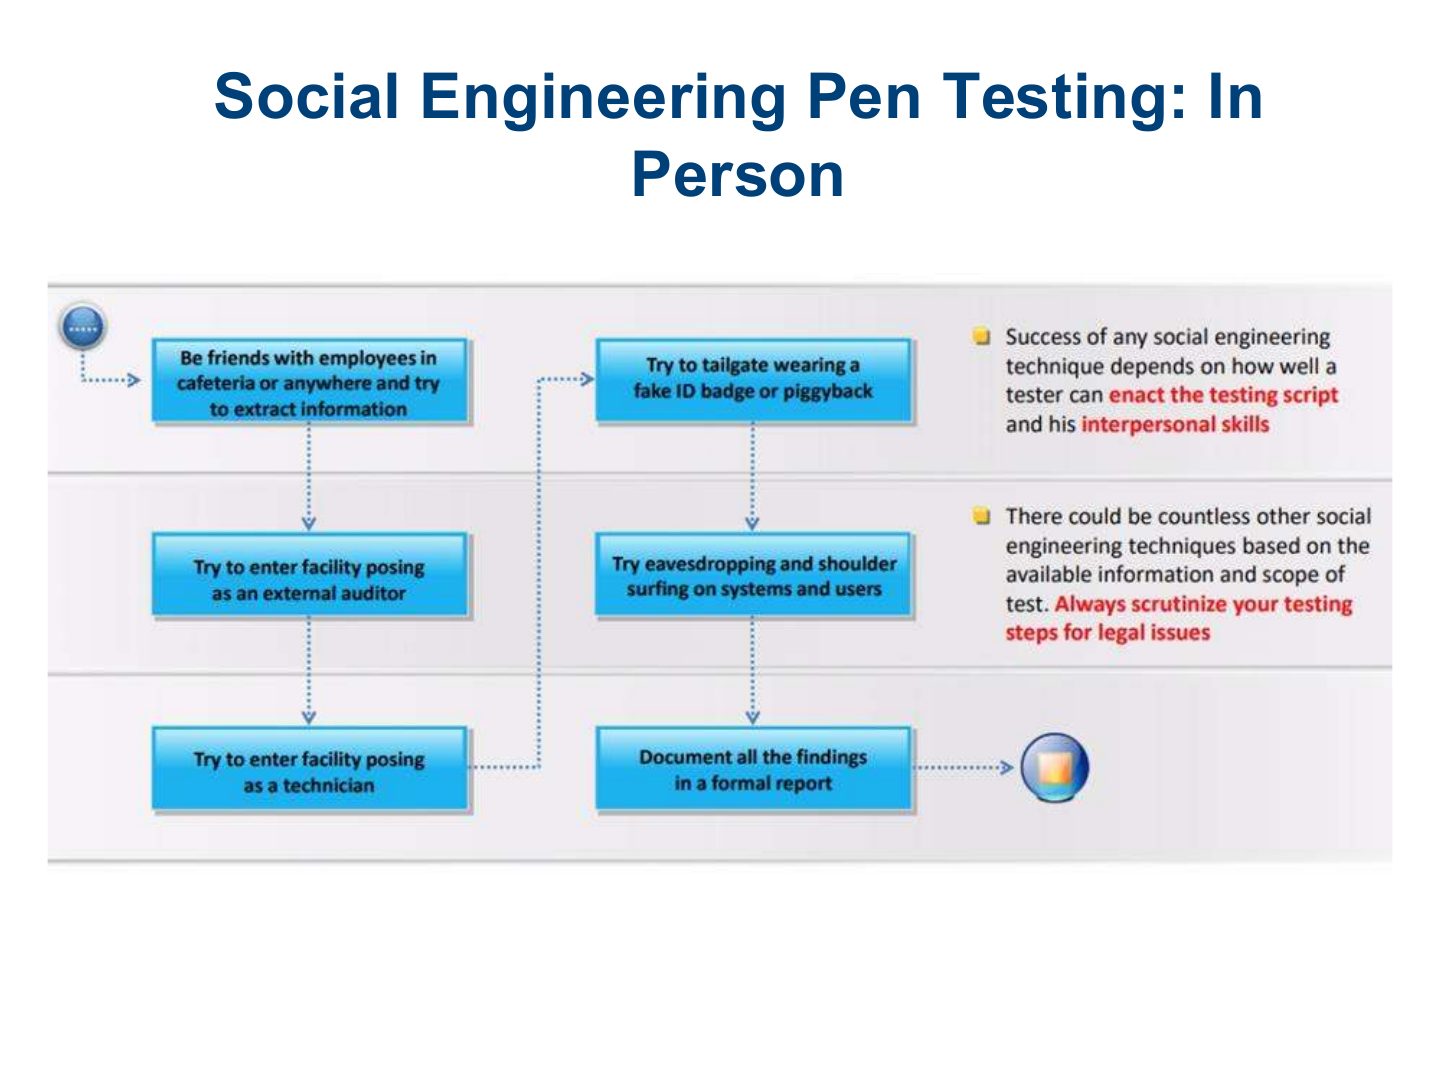
- 44 Social Engineering Pen Testing: In Person
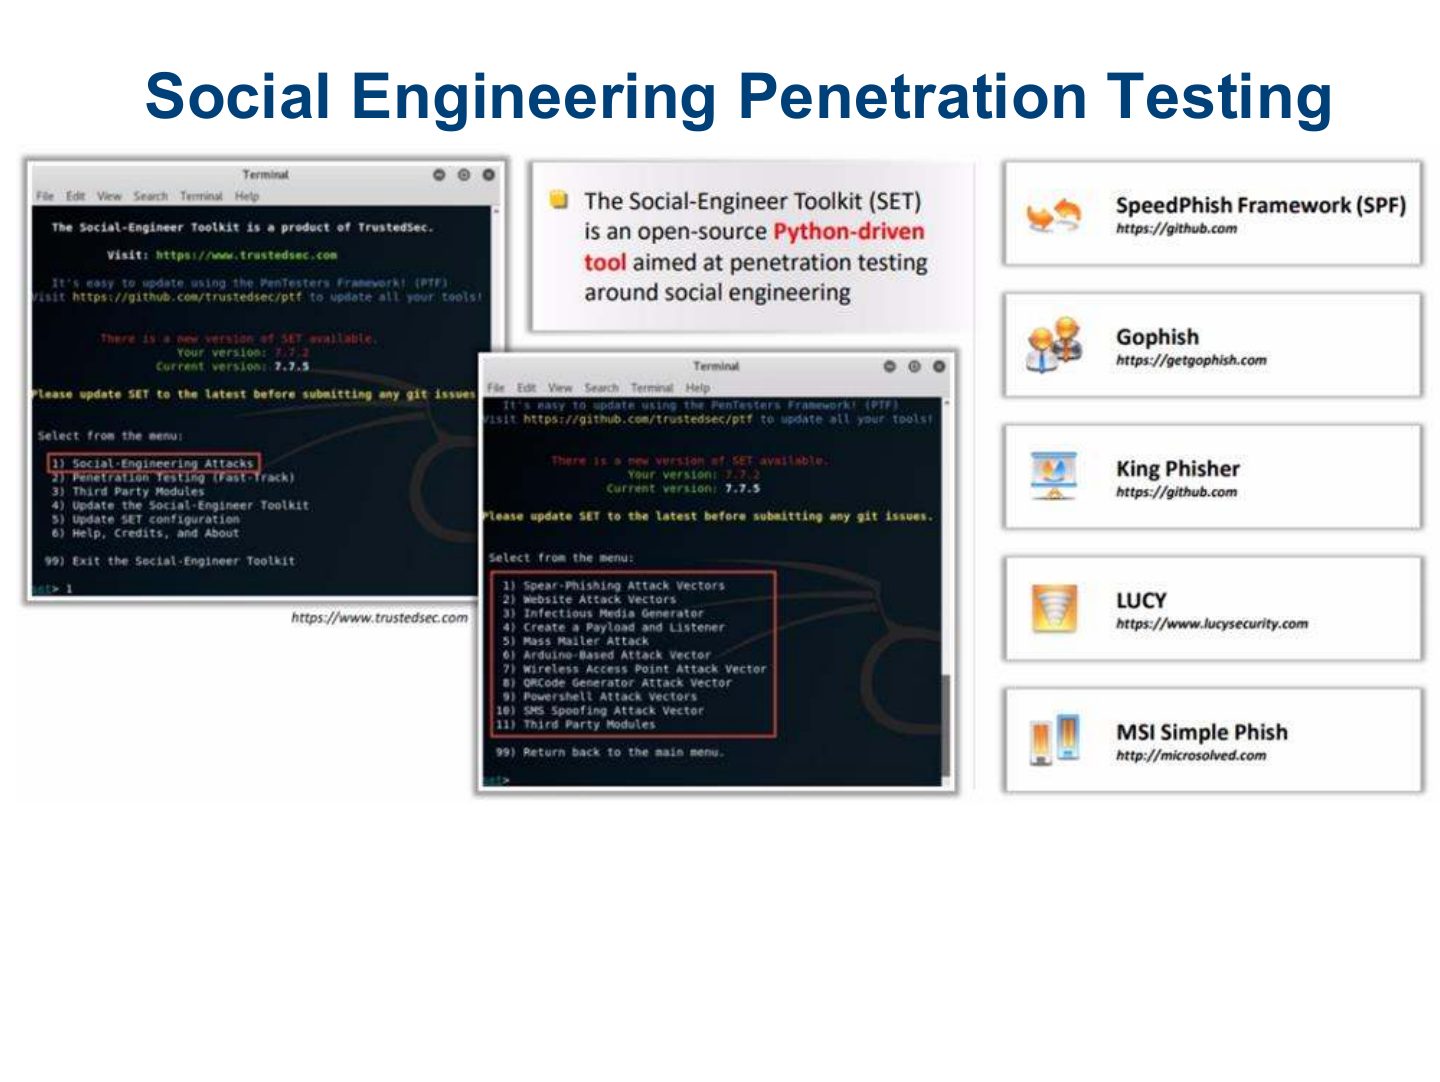
- 45 Social Engineering Penetration Testing Tool
- 46 Know What the Web Knows About You
- 47 Summary
Slide 1
Slide 2
What is Social Engineering?
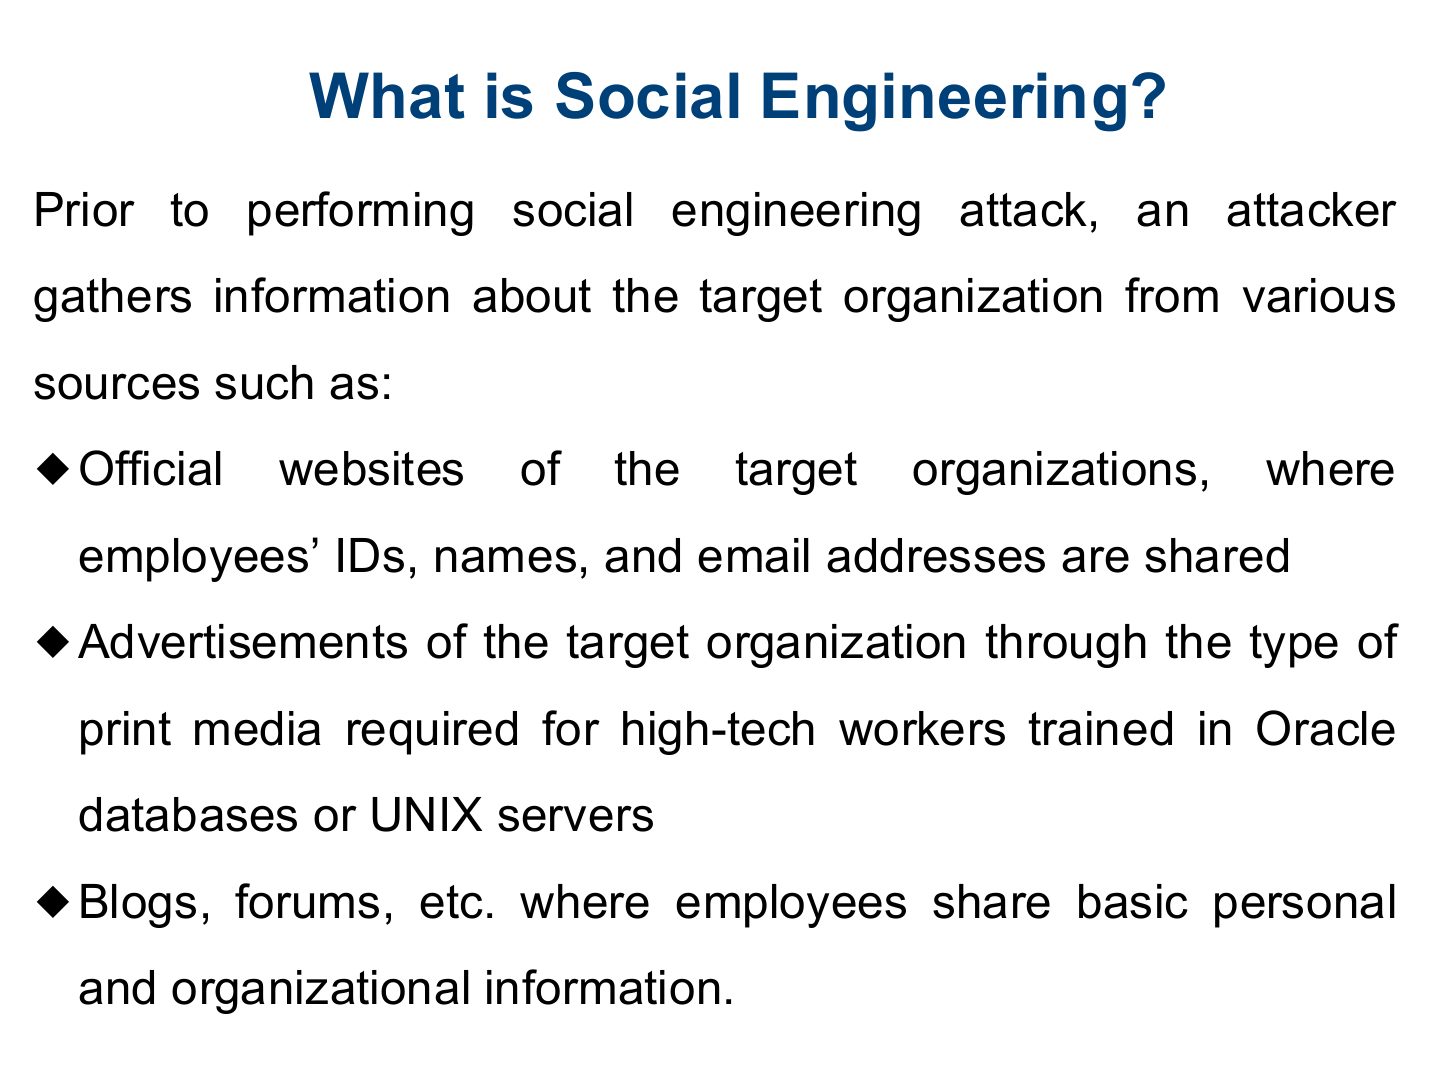
Notes
Social engineering: manipulating people into revealing information or performing actions. Exploits trust, not technology.
▪ After information gathering, an attacker executes social engineering
Slide 5
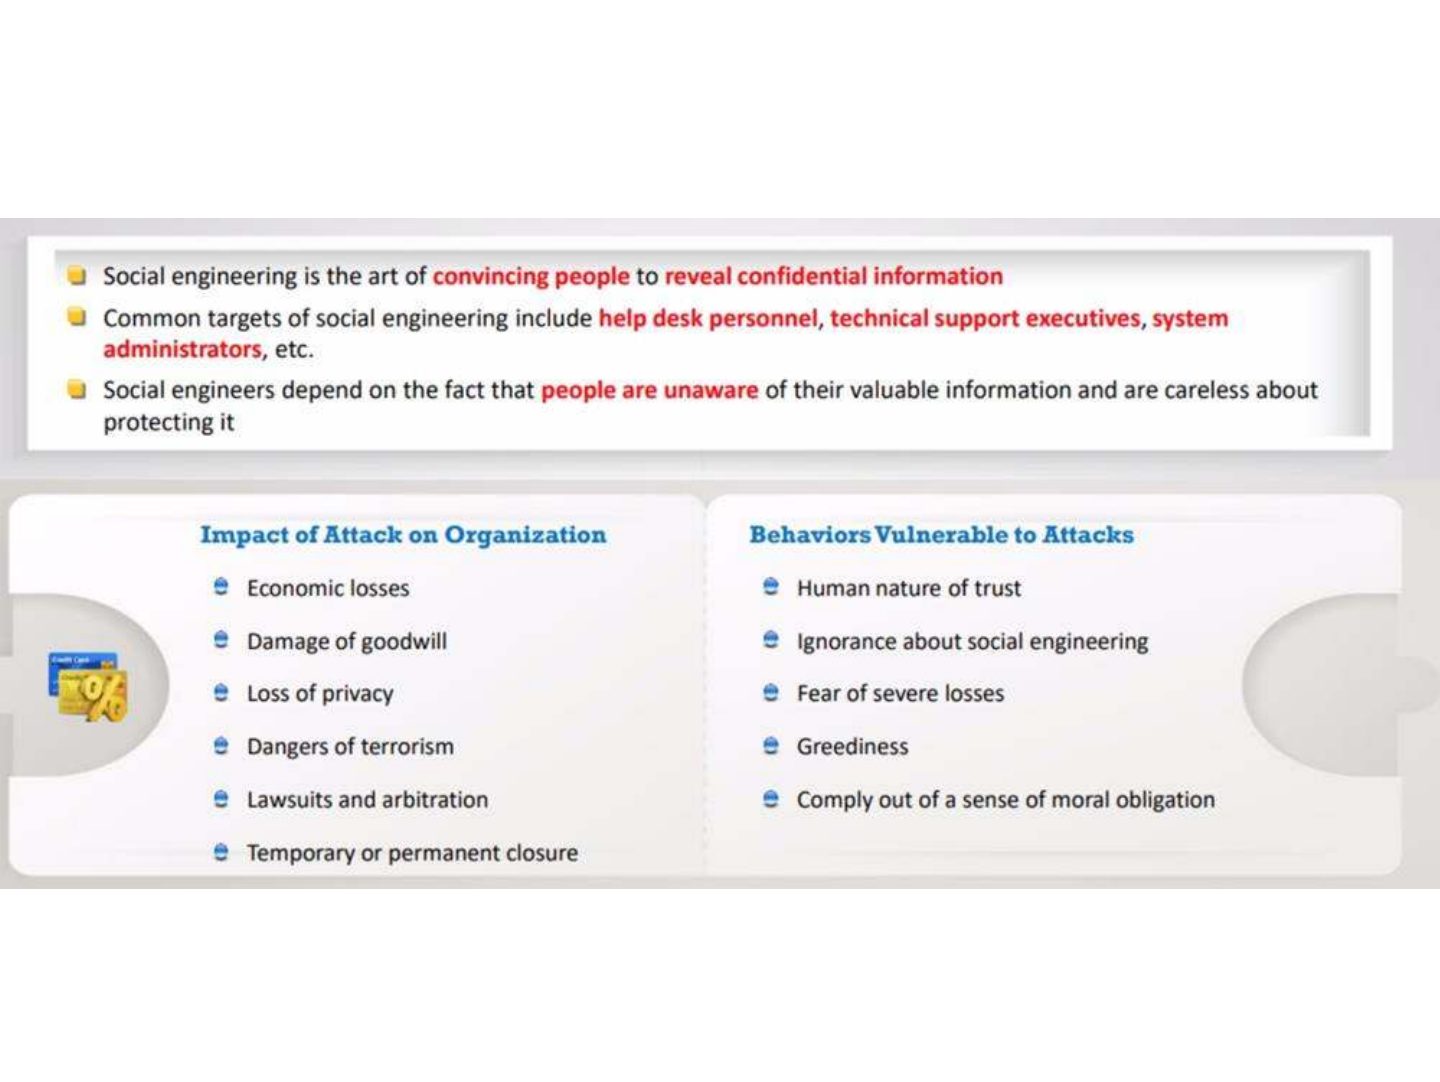
Slide 6
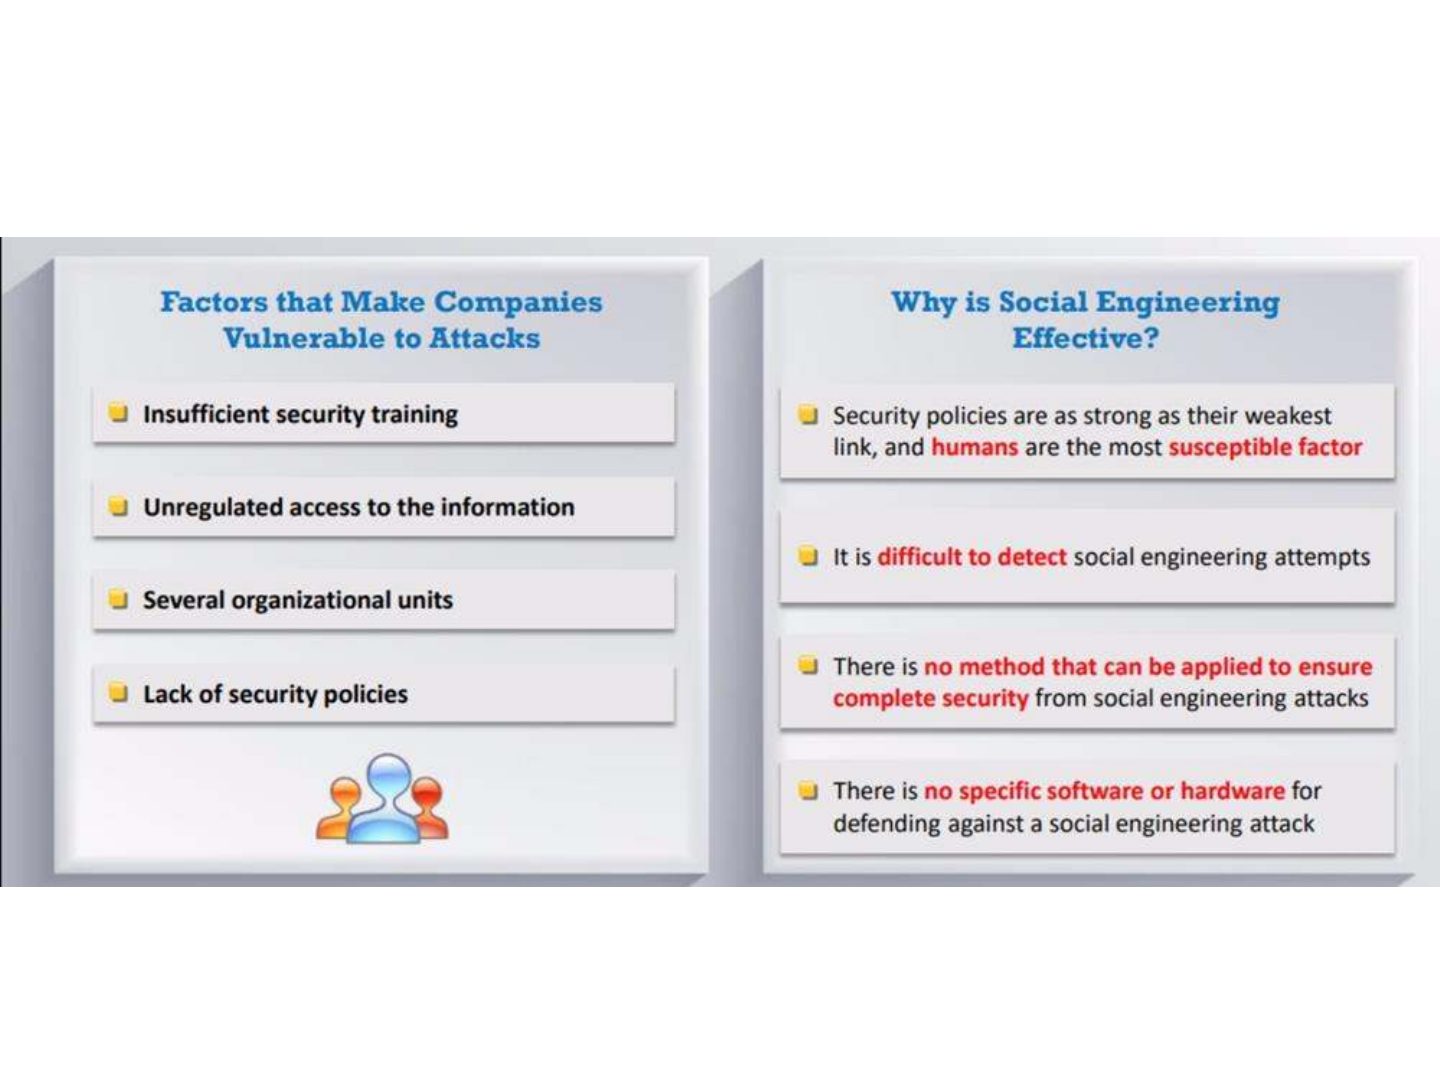
Common Targets of Social Engineering
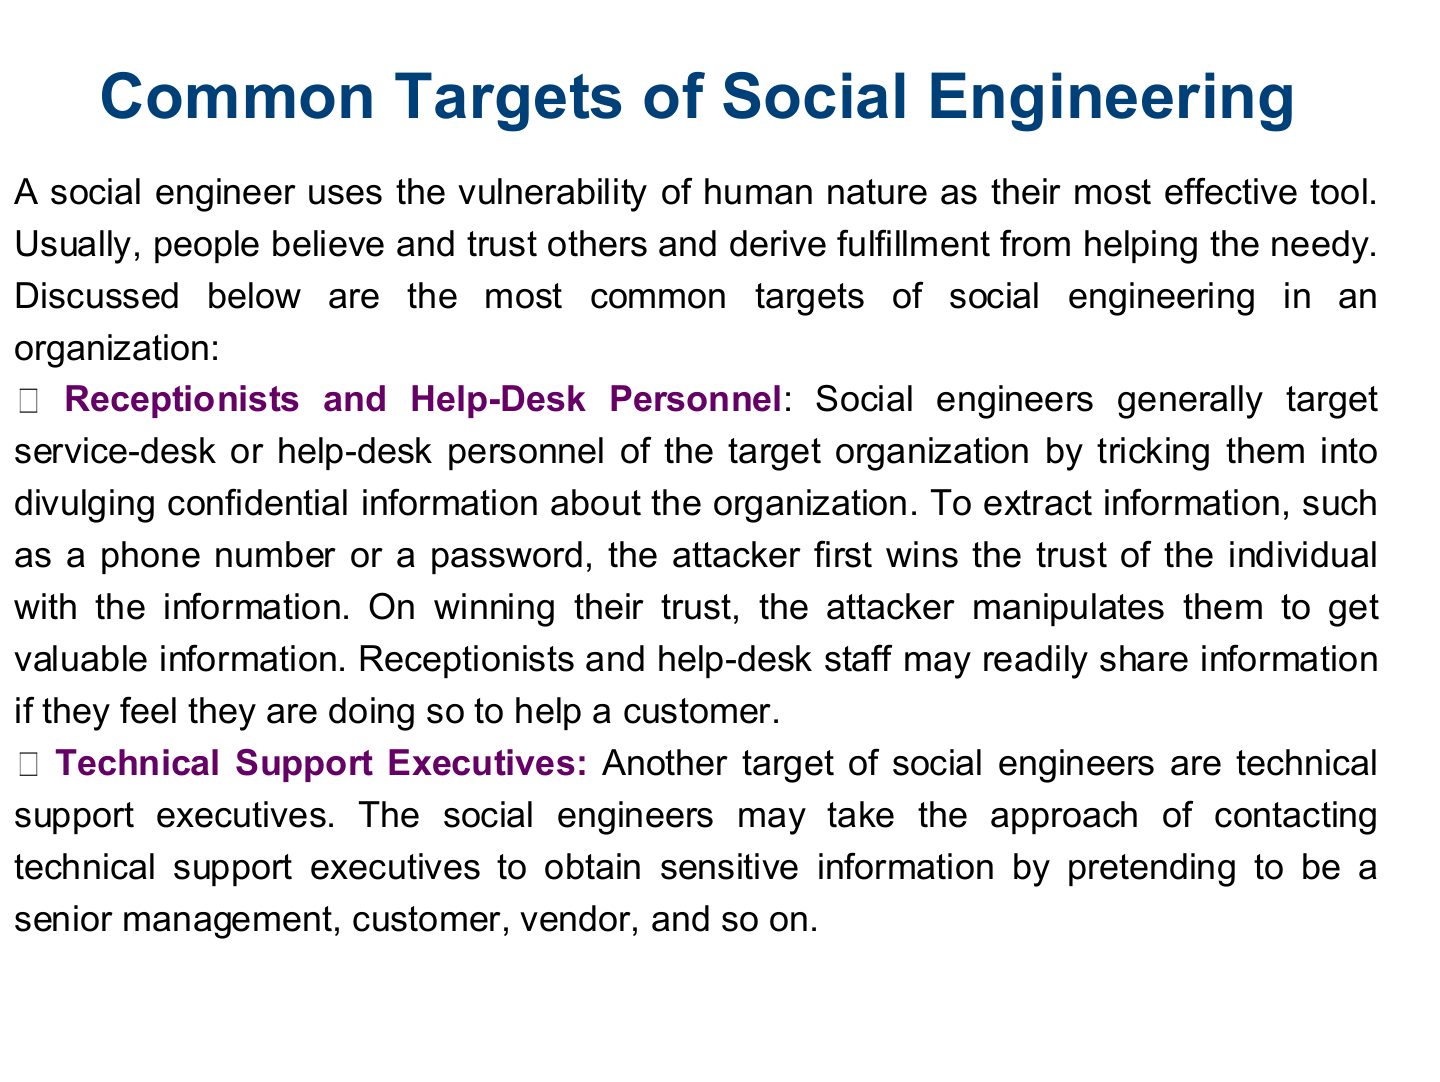
System Administrators: A system administrator in an organization is
Impact of Social Engineering Attack on Organization
Dangers of Terrorism: Terrorism and anti-social elements
Behaviors Vulnerable to Attacks
Notes
Behaviours exploited: authority, intimidation, consensus/social proof, scarcity, urgency, familiarity, trust, greed.
Exam angle
Behaviors Vulnerable to Attacks
Factors that Make Companies Vulnerable to Attacks
Several Organizational Units Some organizations have their units at
Why is Social Engineering Effective?
Notes
Why it works: no software stops it, people want to help, lack of training, no detection.
Phases of a Social Engineering Attack
Types of Social Engineering
An attacker can perform human-based social engineering by using the following techniques: • Impersonating
Impersonation
Notes
Impersonation: pretending to be someone (IT, a vendor, an executive). Vishing = voice phishing over the phone.
Impersonation (Vishing)
Human-based Social Engineering: Eavesdropping, Shoulder Surfing and Dumpster Diving
Notes
Eavesdropping, shoulder surfing, dumpster diving, tailgating (following someone through a door), piggybacking (with permission).
Trap Tailgating = without the employee’s consent; piggybacking = the employee knowingly lets you in.
Exam angle
Following an employee through a secure door without their knowledge is:
Human-based Social Engineering: Reverse Social Engineering, Piggybacking, and Tailgating
▪ Computer-based Social Engineering
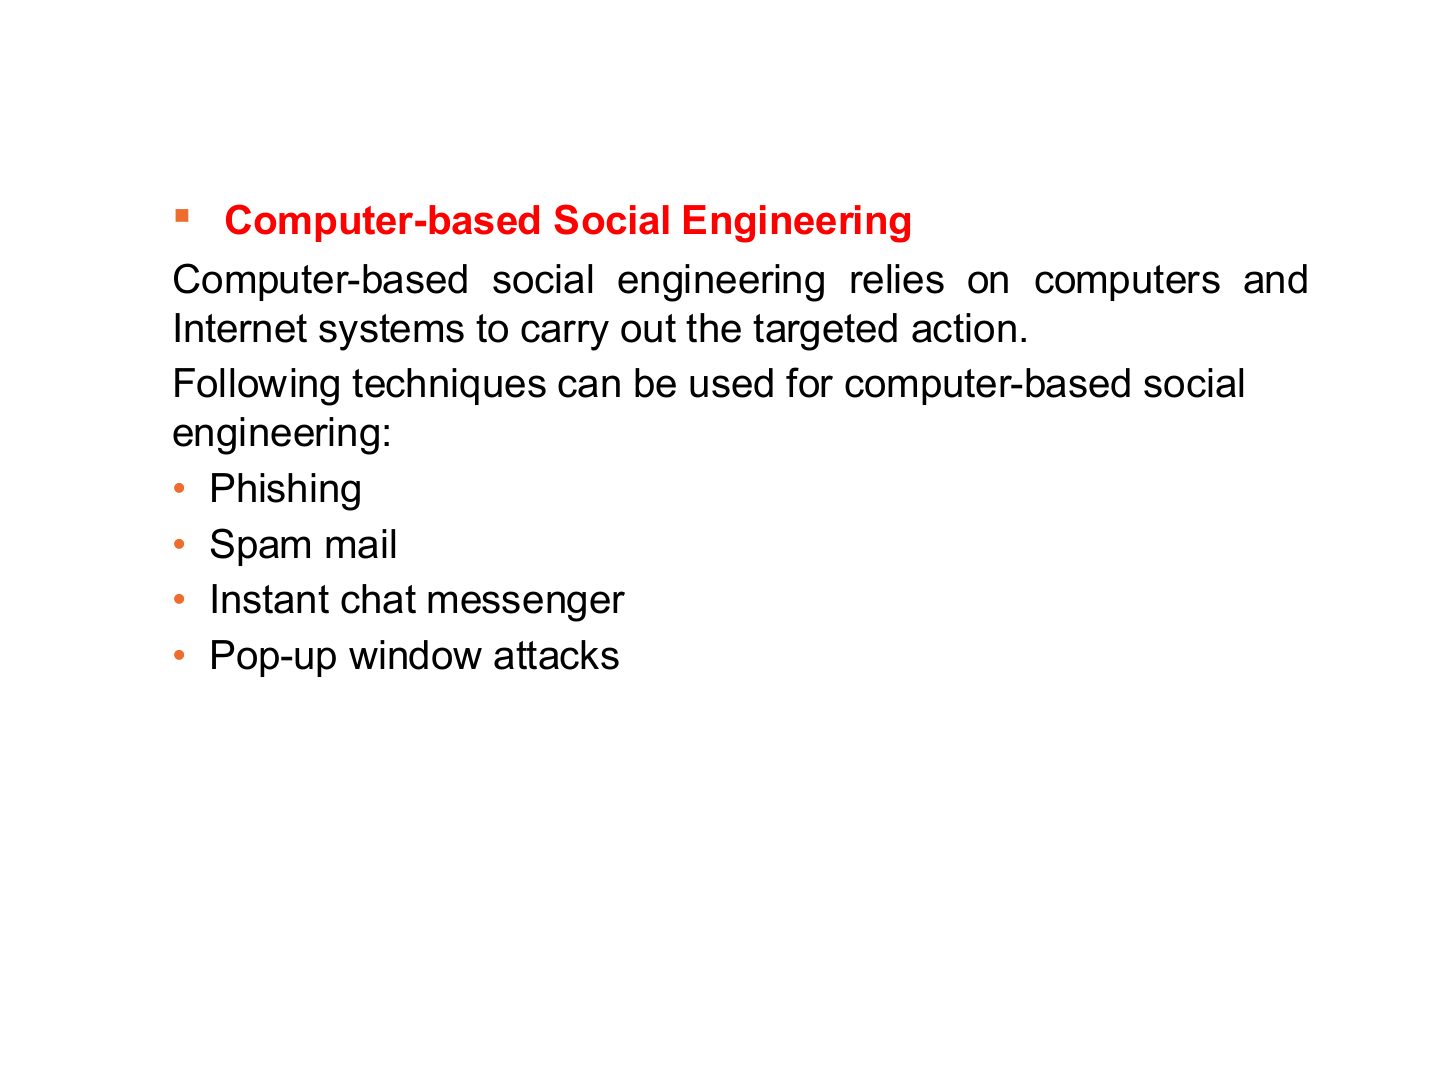
Computer-based Social Engineering
Notes
Computer-based: phishing (mass email), spear phishing (targeted), whaling (executives), pop-ups, fake software.
Exam angle
A phishing email crafted for one specific CFO is:
- Spear phishing aimed at an executive.
Slide 25
Computer-based Social Engineering: Phishing
▪ Mobile-Based Social Engineering
Mobile-based Social Engineering: Publishing Malicious Apps and Repackaging Legitimate App
Mobile-based Social Engineering: Fake Security Applications
Mobile-based Social Engineering: SMiShing (SMS Phishing
Insider Threat / Insider Attack
Notes
Insider threat: current or former employees, contractors with legitimate access: the hardest to detect.
Terminated Employees : Some employees take valuable information about the company with them when terminated. These employees access company s data even after termination using backdoors, malware, or their old ’ credentials because they are not disabled.
Companies where insider attacks are common include credit card companies, health-care companies, network service providers, as well as financial and exchange service providers.
Become Future Competitor Current employees may plan to
Countermeasures
Social Engineering Countermeasures
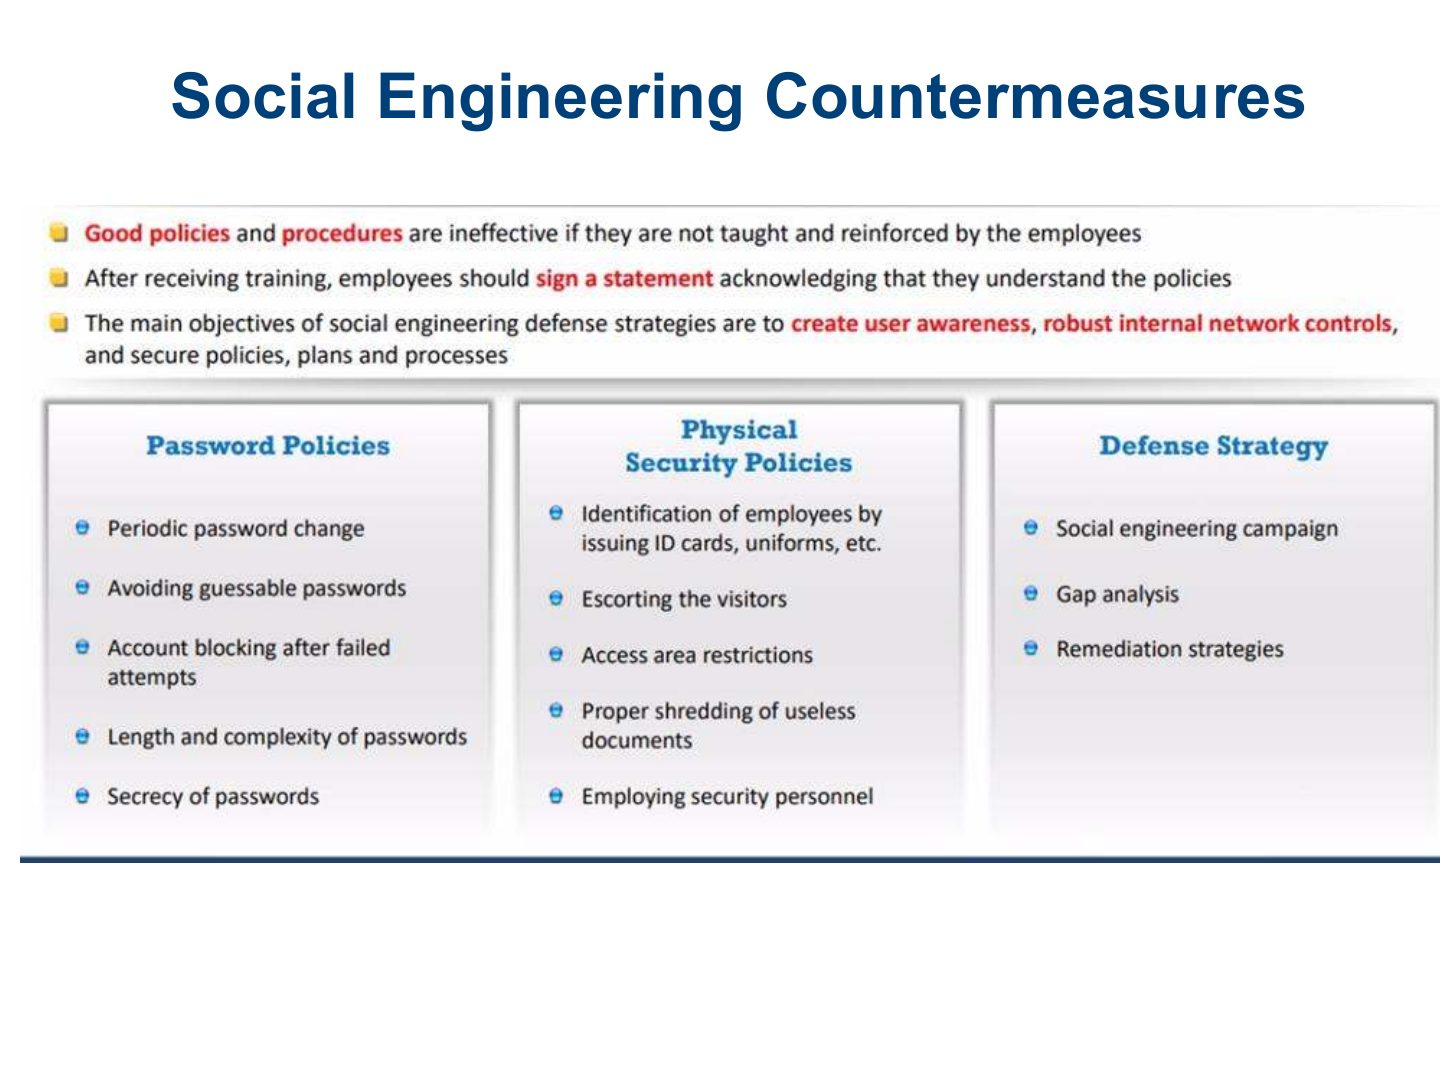
Notes
Countermeasures: training and awareness, policies, verification procedures, least privilege, physical controls, shredding.
Social Engineering Countermeasures (Cont’d)
Insider Threats Countermeasure
How to Detect Phishing Emails
Notes
Spot phishing: mismatched sender or link URLs, urgency, spelling errors, unexpected attachments, requests for credentials.
Anti-Phishing Toolbar
Social Engineering Pen Testing
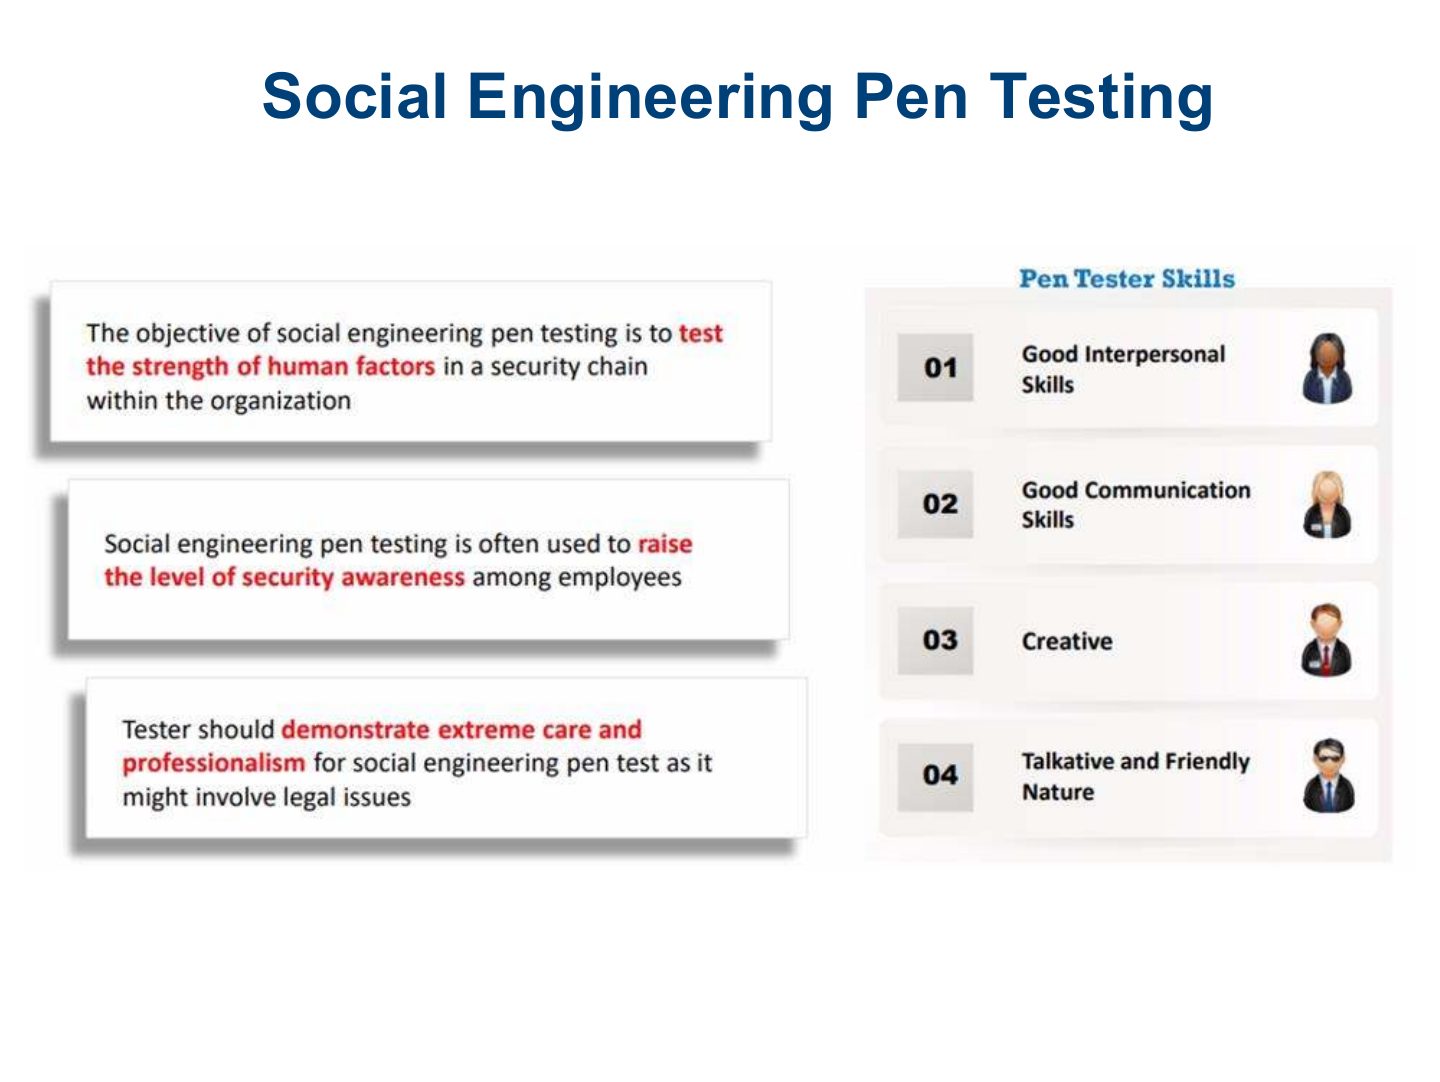
Notes
SE pen testing: phishing campaigns, phone pretexting, physical entry, USB drops (with written authorization).
Social Engineering Pen Testing (Cont’d)
Social Engineering Pen Testing: Using Phone
Social Engineering Pen Testing: In Person
Social Engineering Penetration Testing Tool
Know What the Web Knows About You
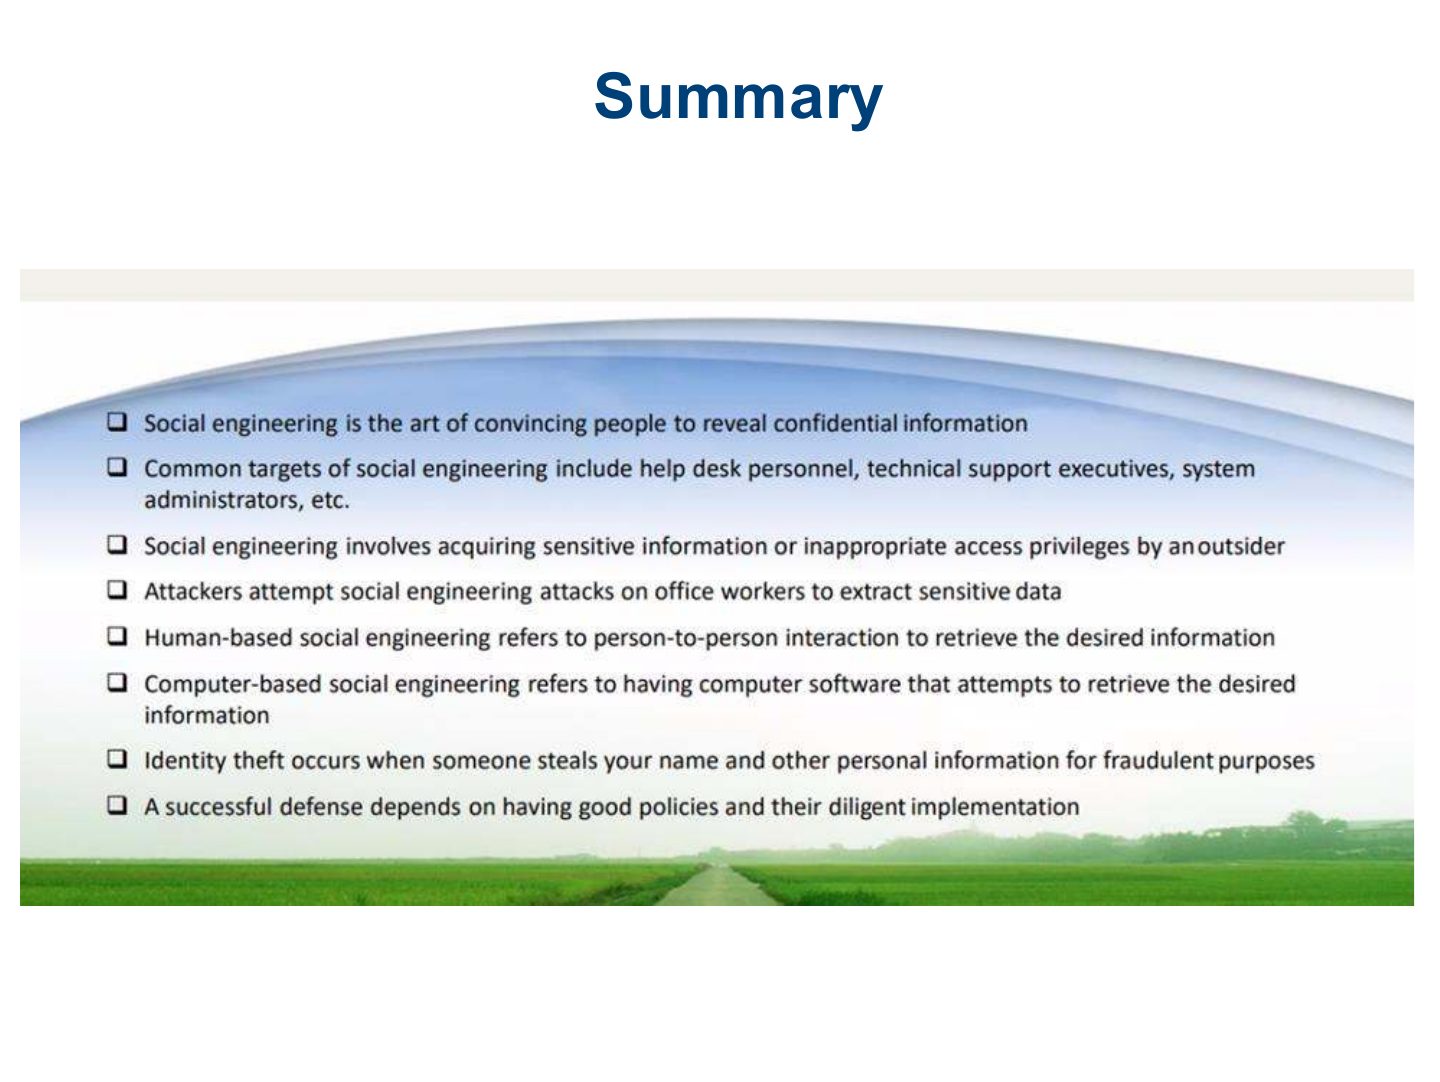
Summary