Trying every possible combination of characters is a:
System Hacking
Windows authentication (SAM, NTLM, Kerberos), the CEH system-hacking goals, password cracking (non-electronic, active online, passive online, offline rainbow-table attacks, defaults), defenses, privilege escalation, executing applications and keyloggers, and covering tracks.
How to read this page
Every original slide is shown unchanged. Yellow marks on a slide point to a numbered note: hover or tap a mark to jump to its note, and hover a note to see its marks. Questions tagged Past exam appeared on a real paper; Prediction questions are likely angles, not confirmed. Pick an answer to each question: a wrong pick tells you why it is wrong, so you can try again.
All 42 slides
- 1 Slide 1
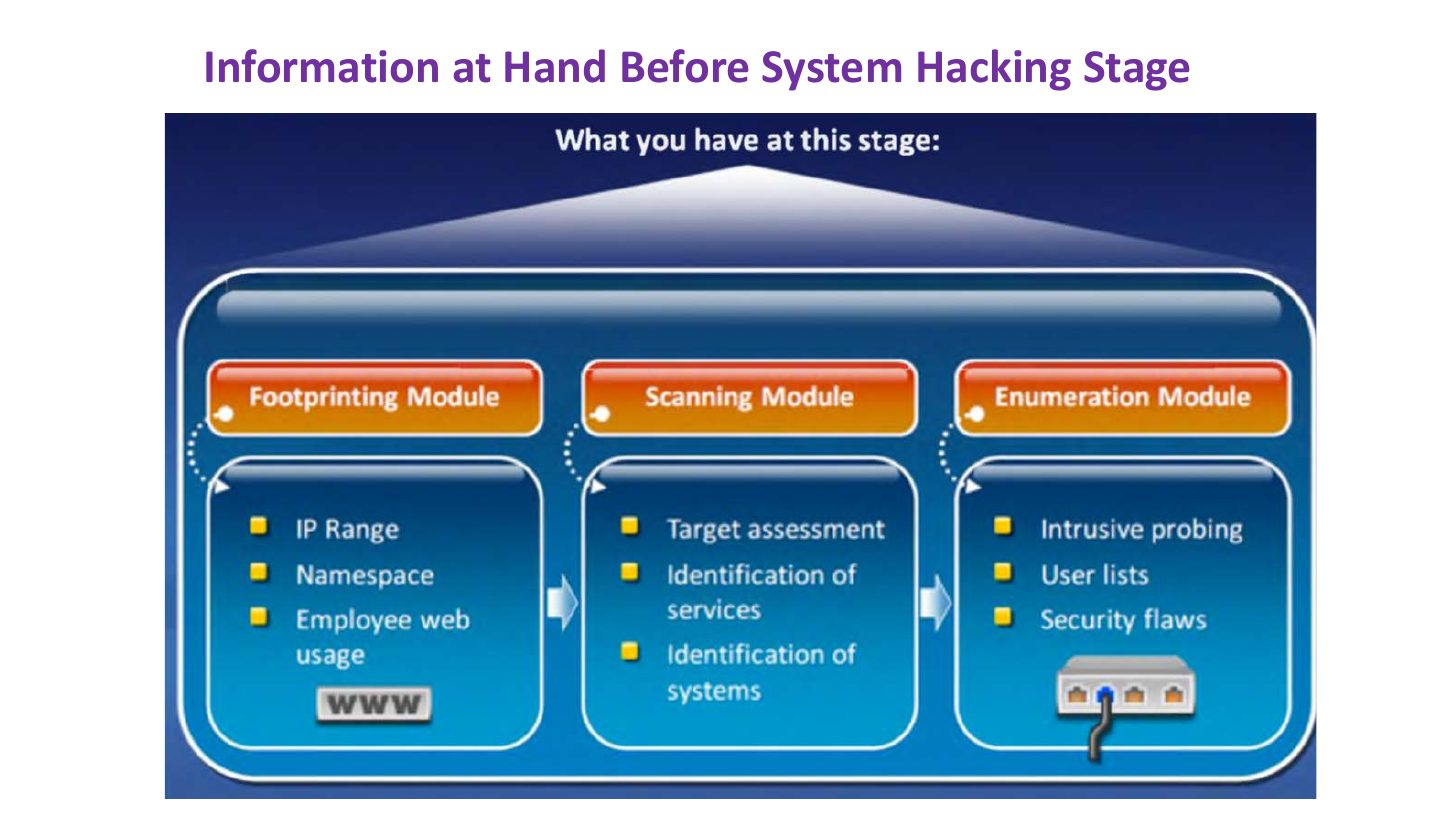
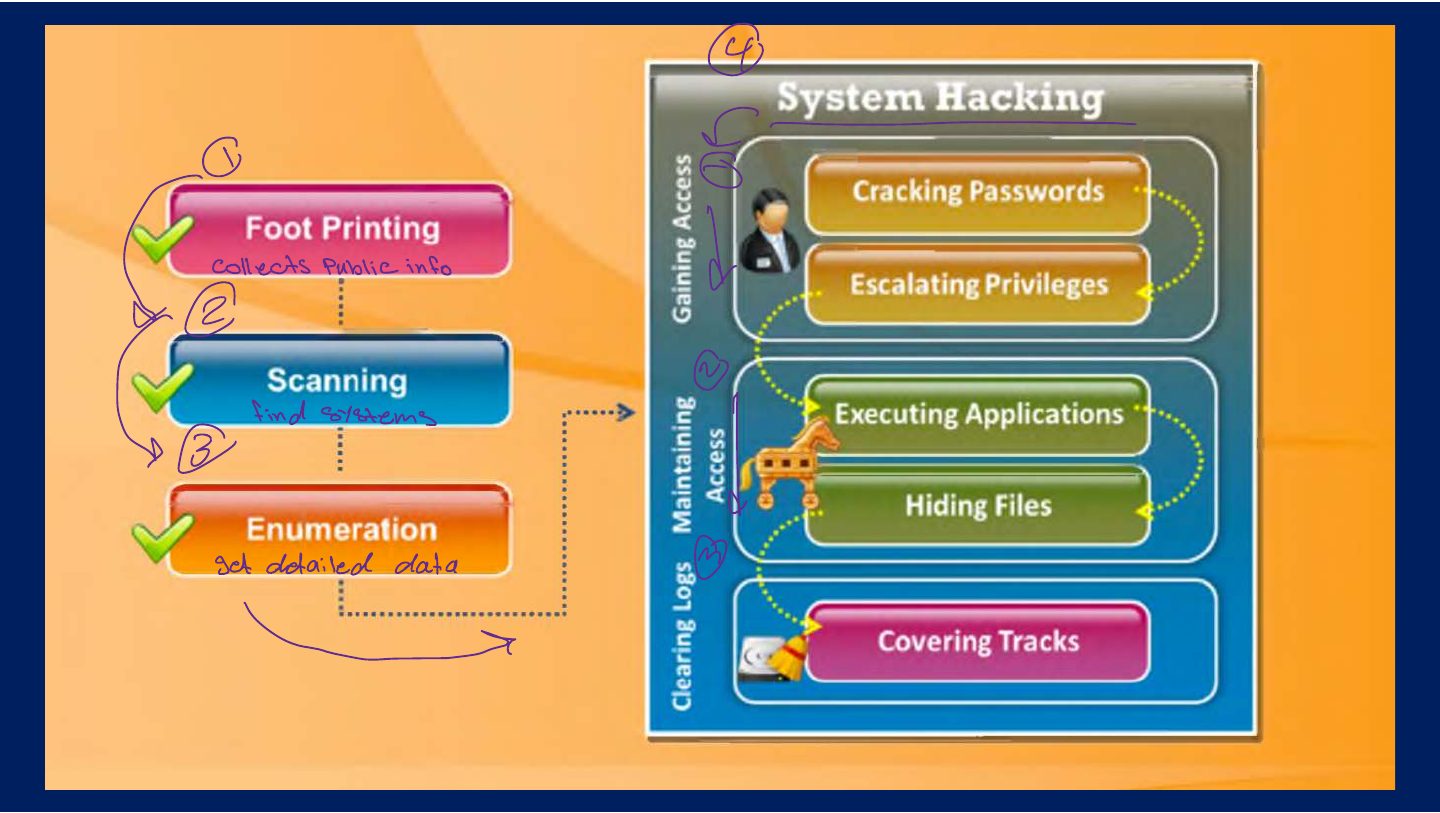
- 2 Information at Hand Before System Hacking Stage
- 3 Gaining Access
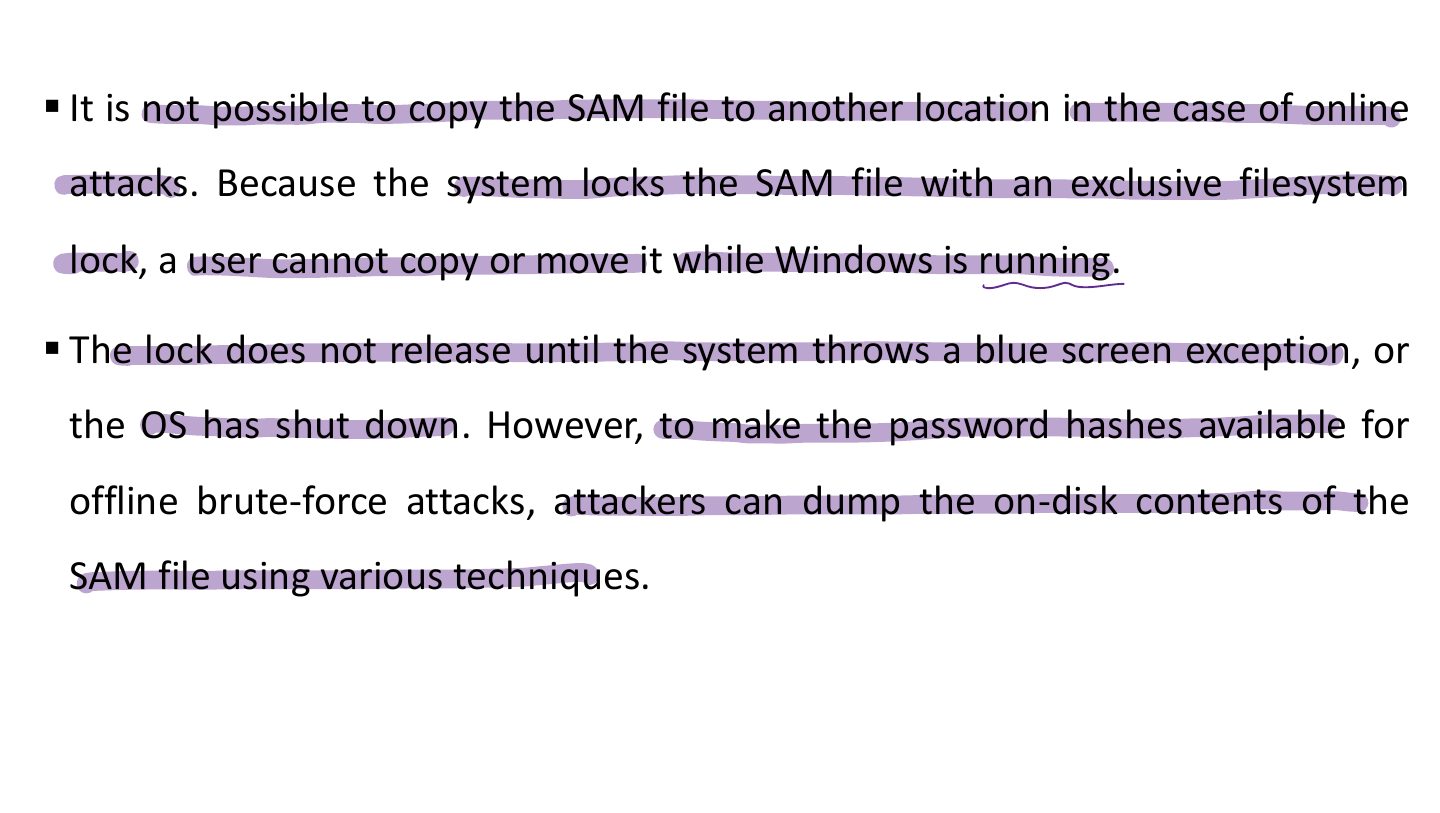
- 4 § It is not possible to copy the SAM file to another location in the case of online
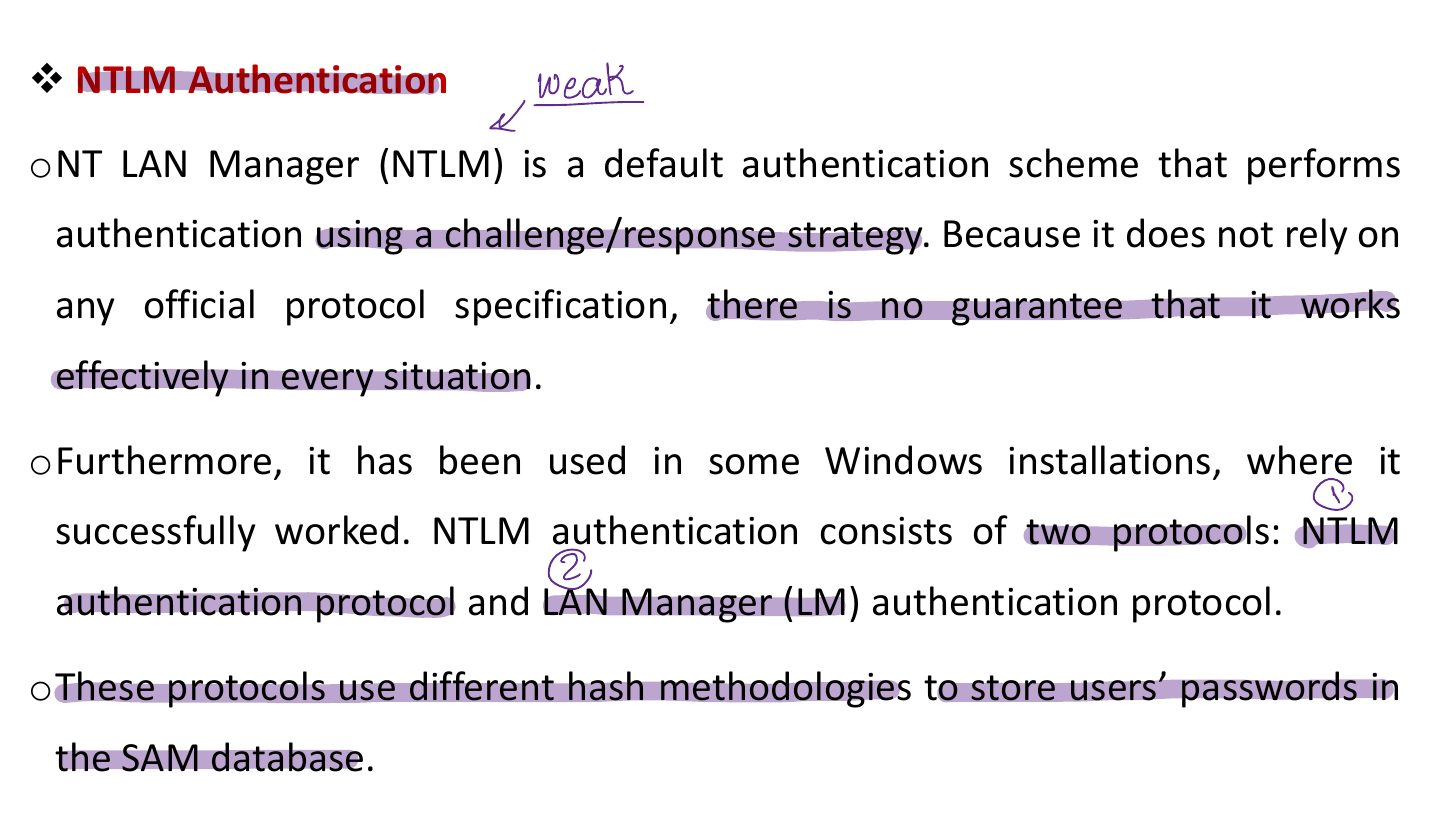
- 5 v NTLM Authentication
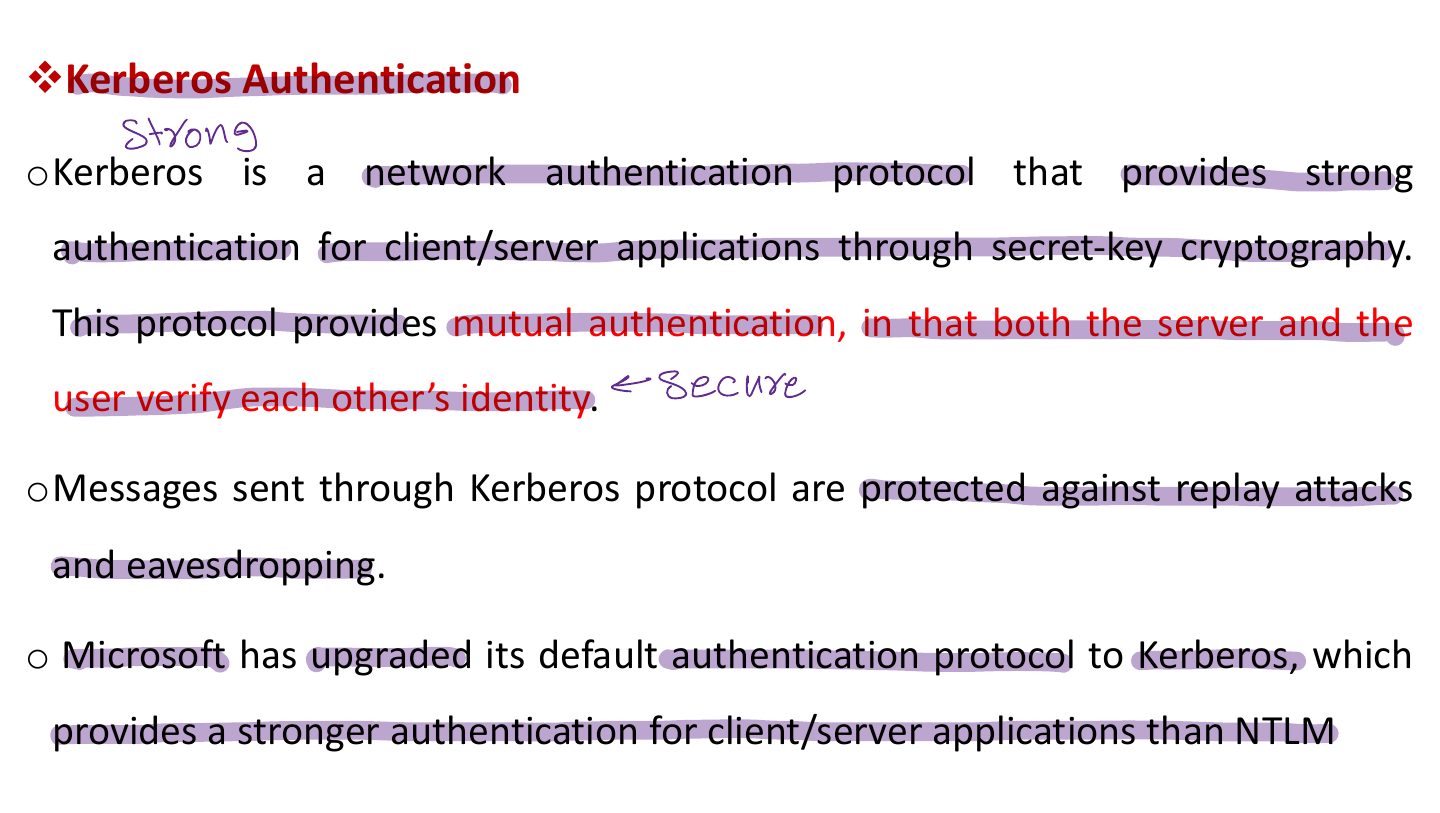
- 6 v Kerberos Authentication
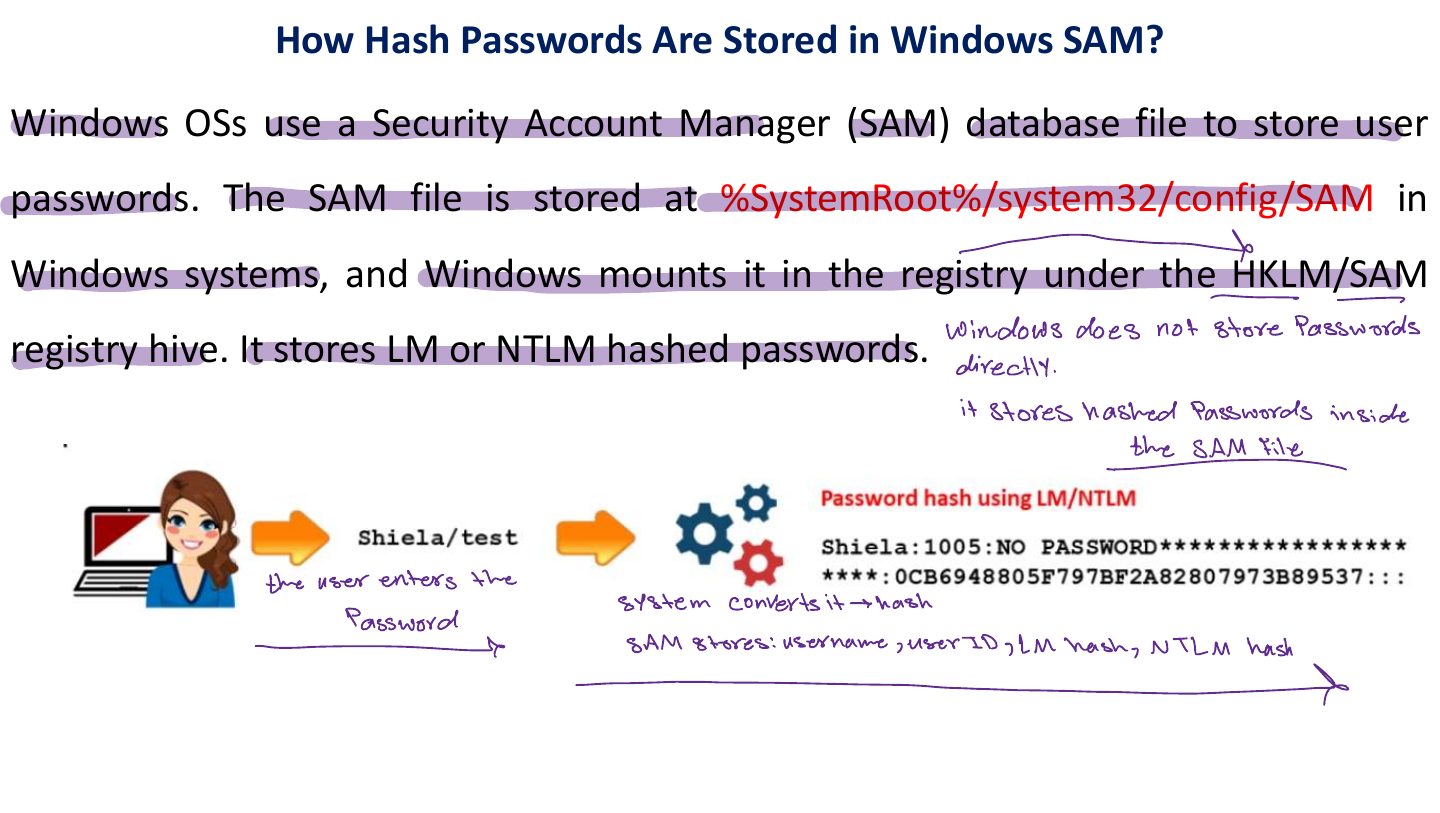
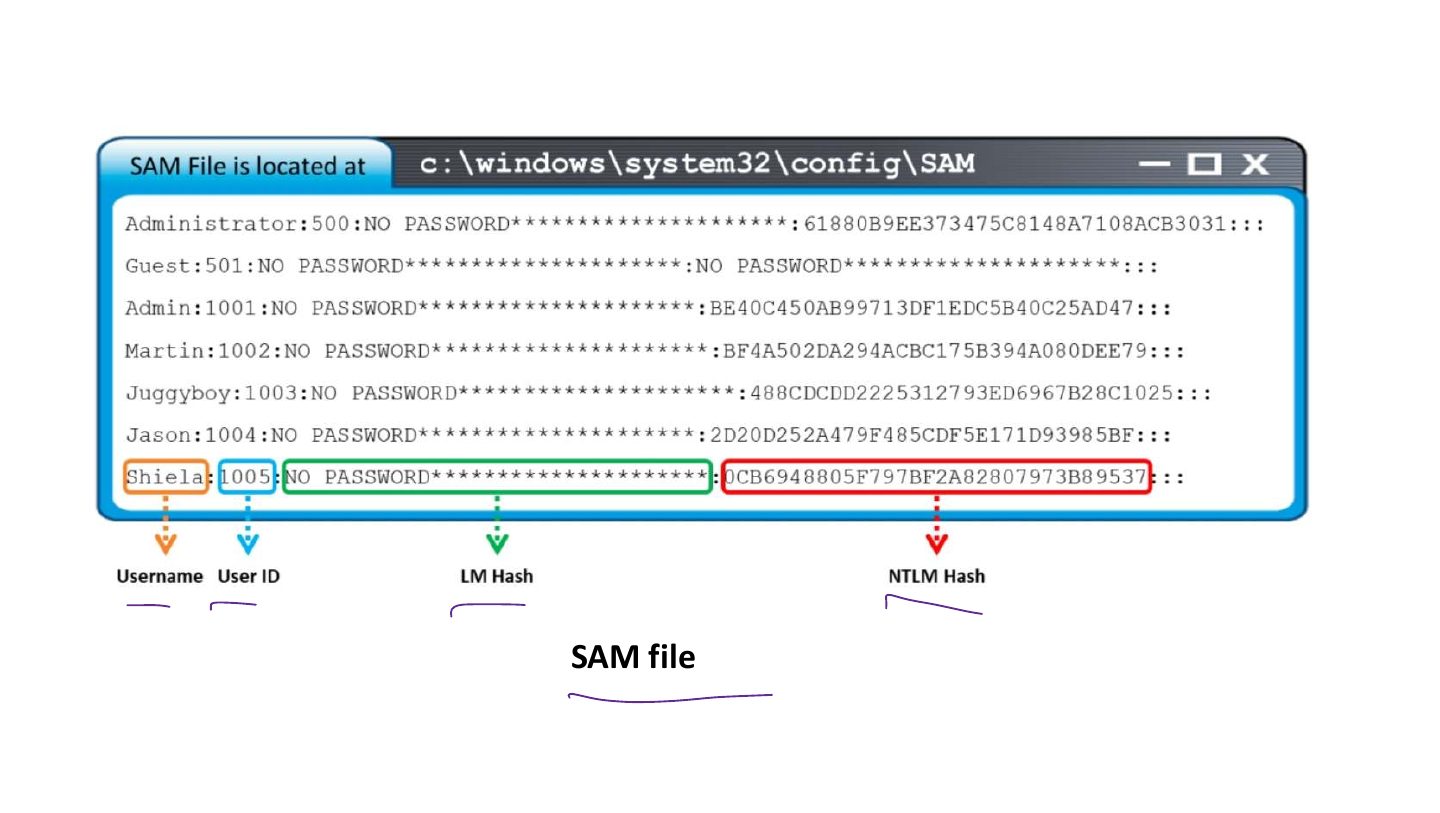
- 7 How Hash Passwords Are Stored in Windows SAM?
- 8 Slide 8
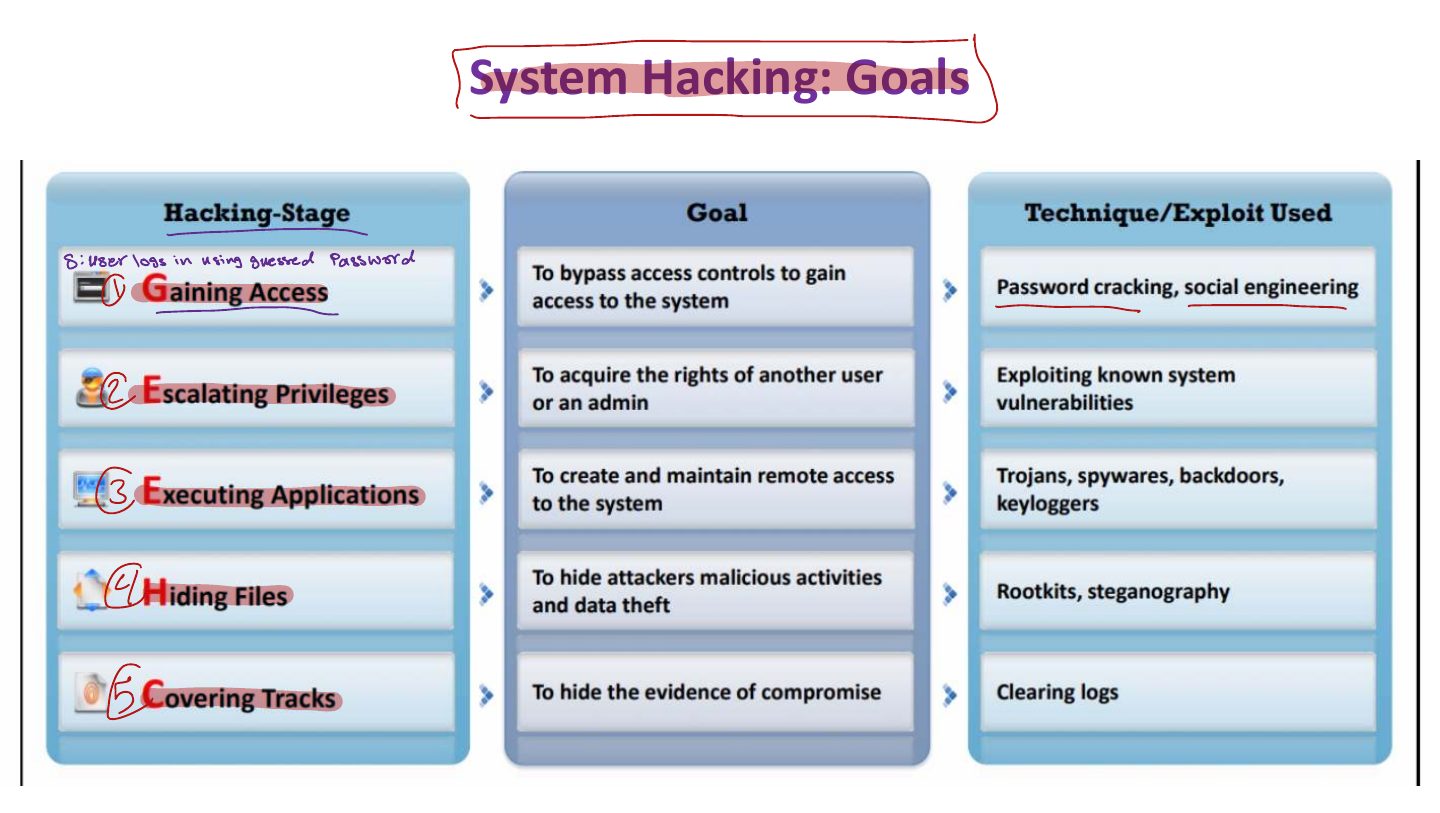
- 9 System Hacking: Goals
- 10 Gaining Access : CEH Hacking Methodology (CHM)
- 11 Slide 11
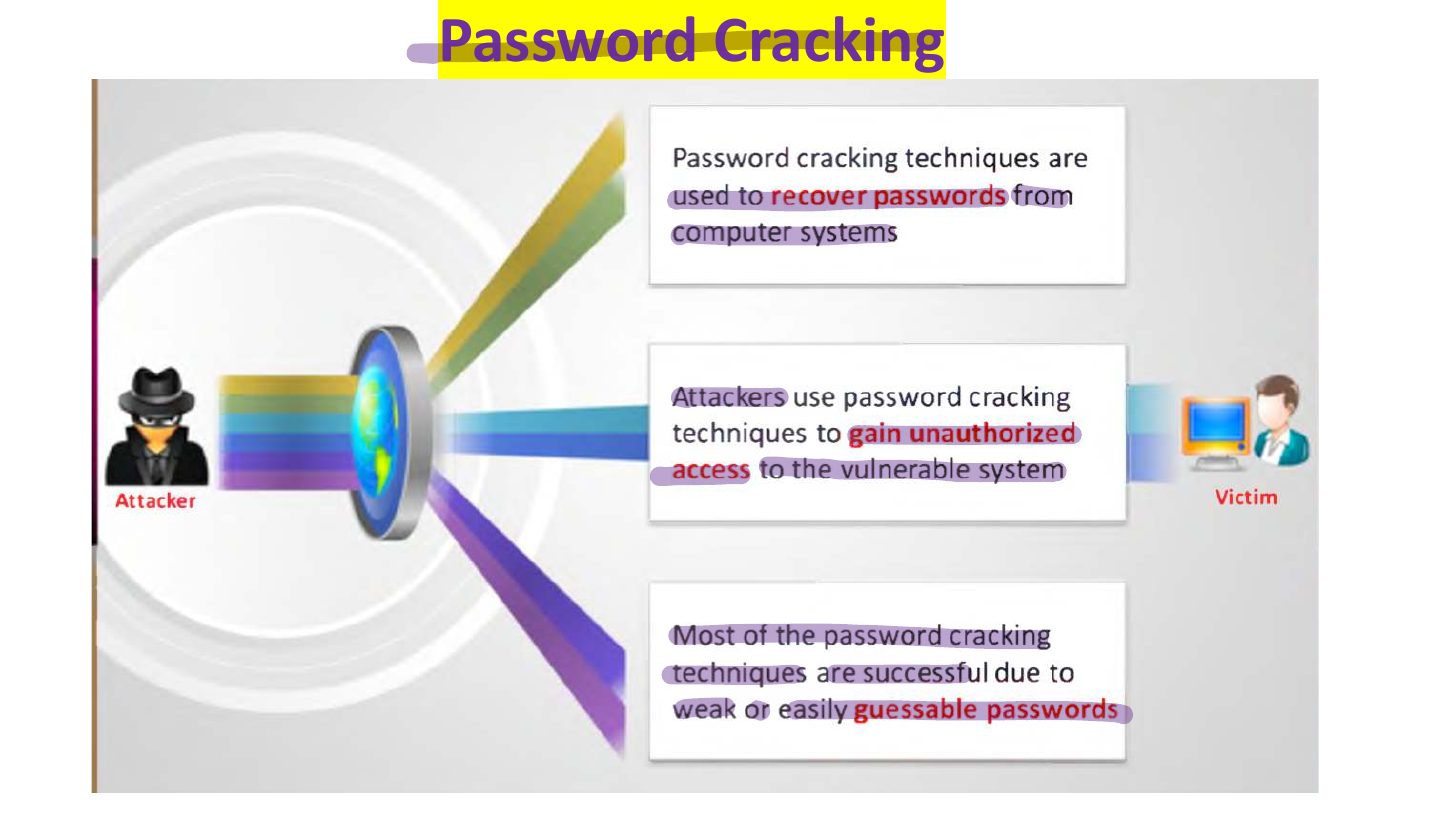
- 12 Password Cracking
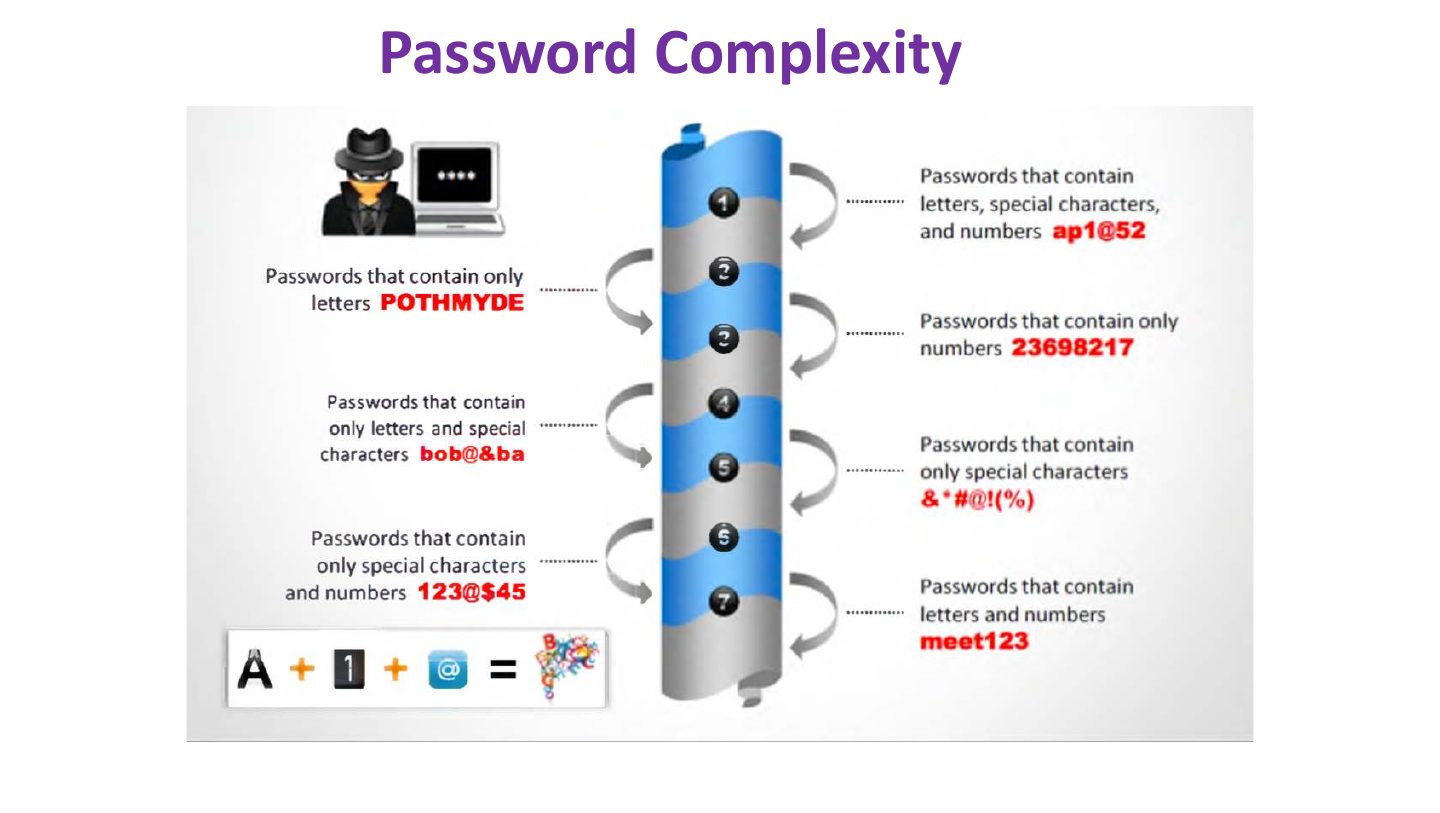
- 13 Password Complexity
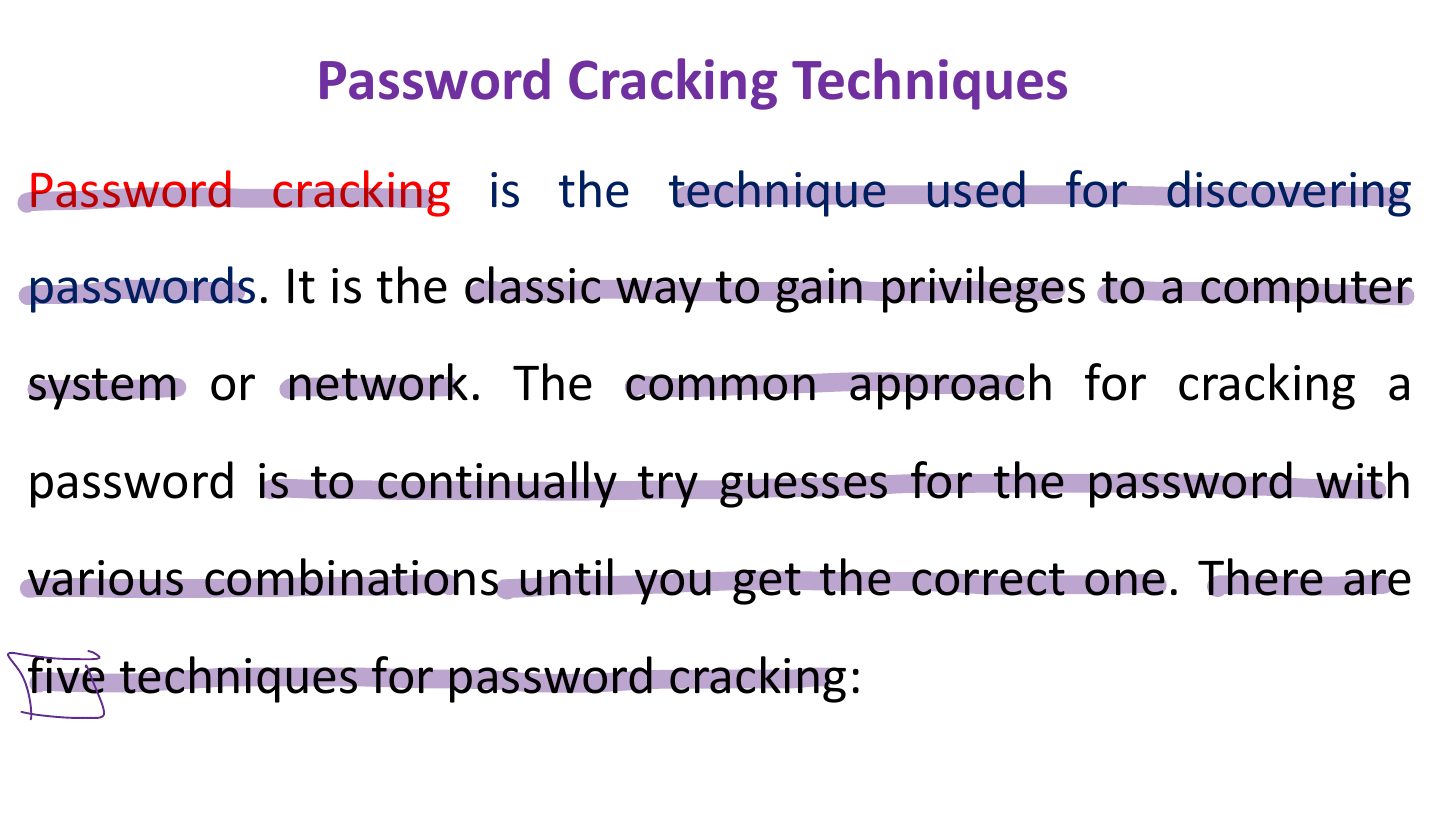
- 14 Password Cracking Techniques
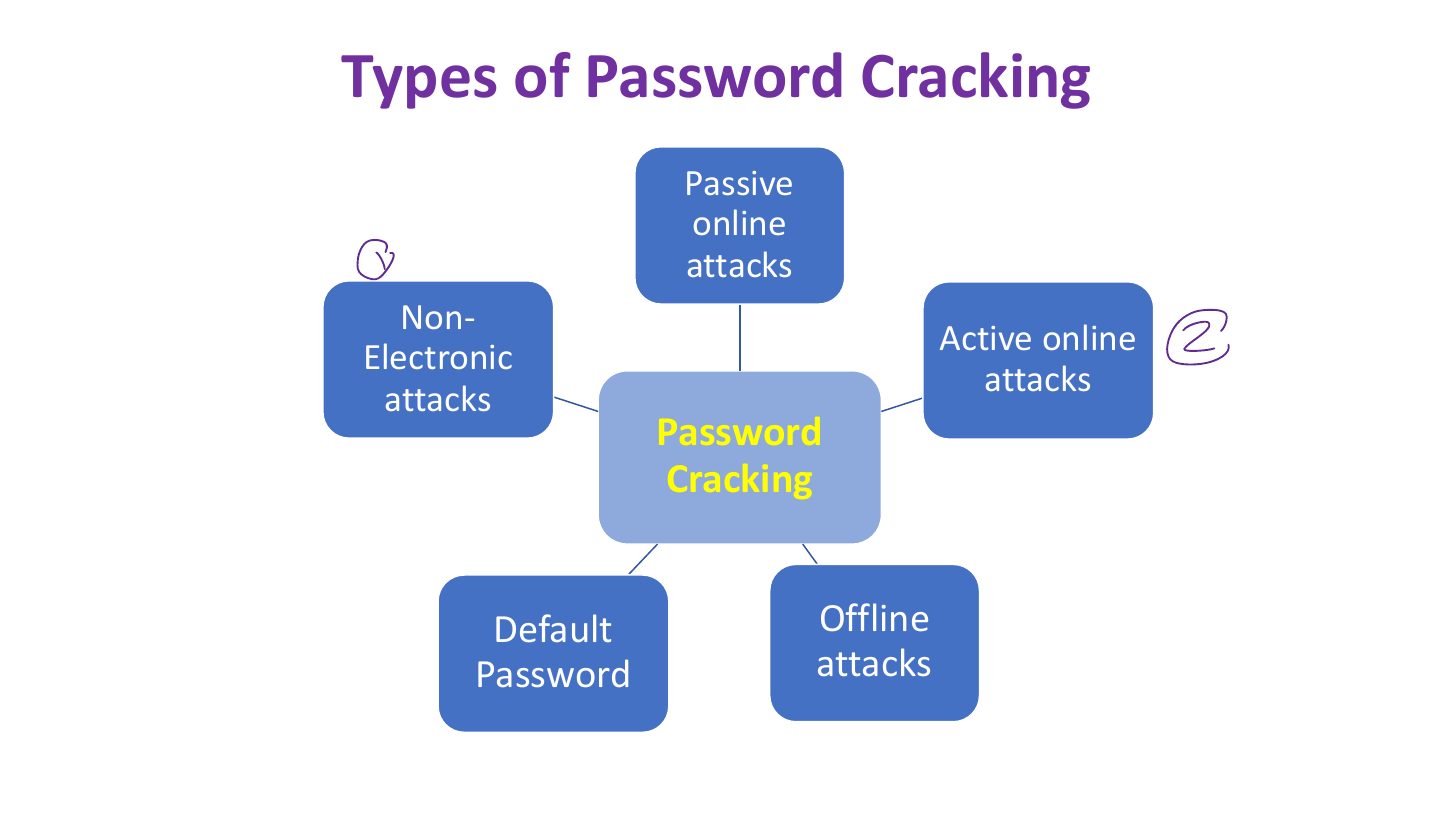
- 15 Types of Password Cracking
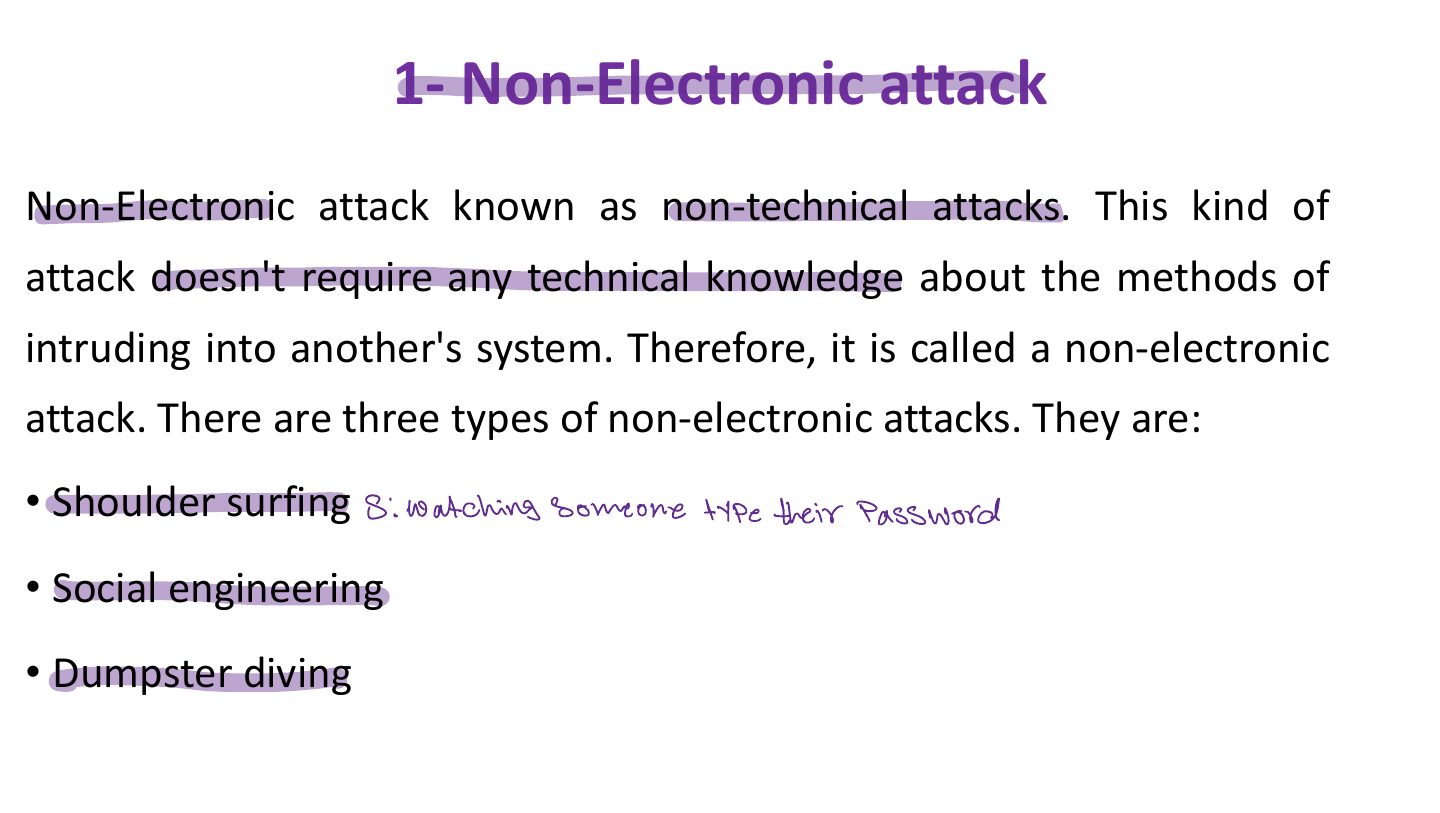
- 16 1- Non-Electronic attack
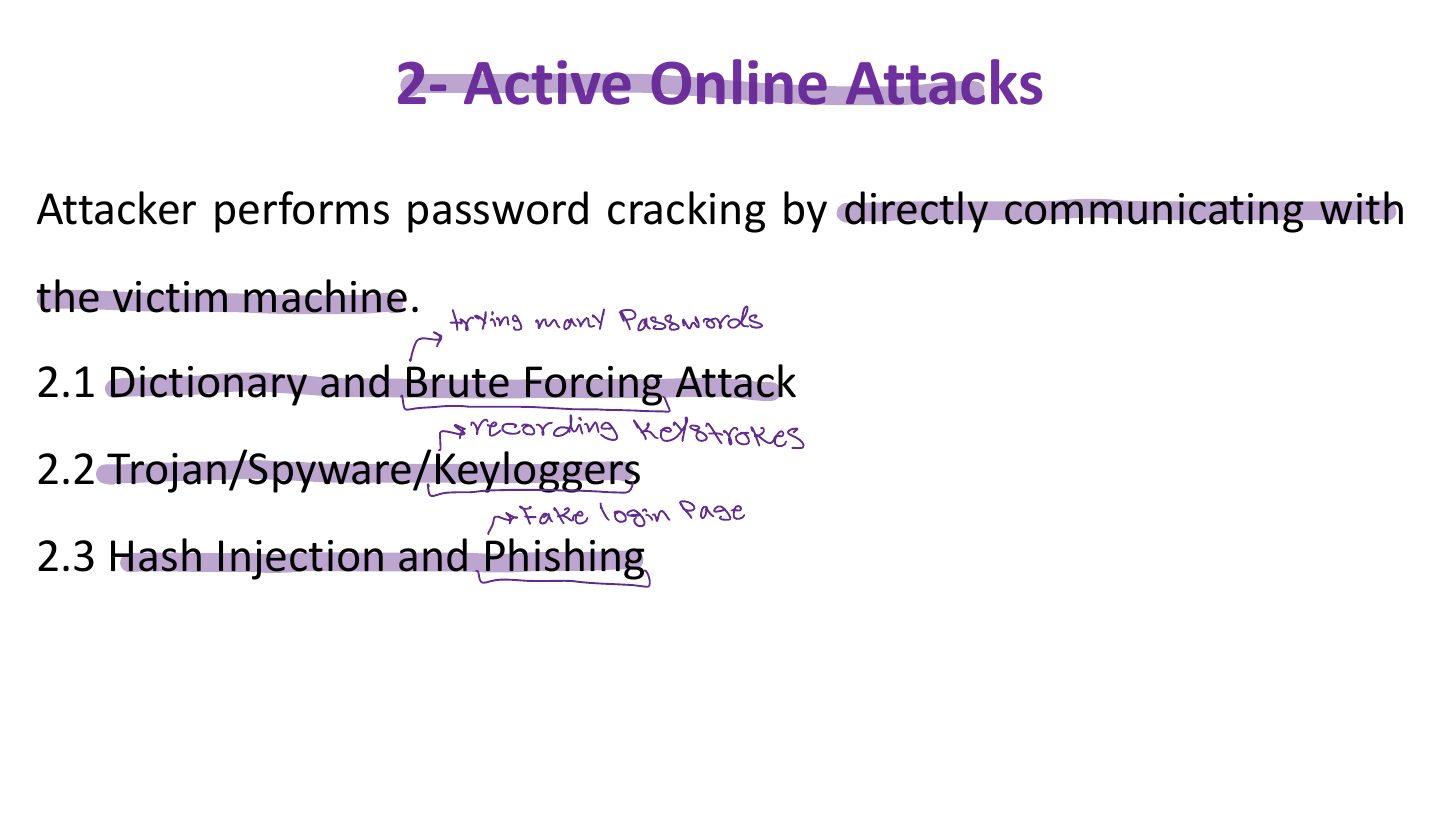
- 17 2- Active Online Attacks
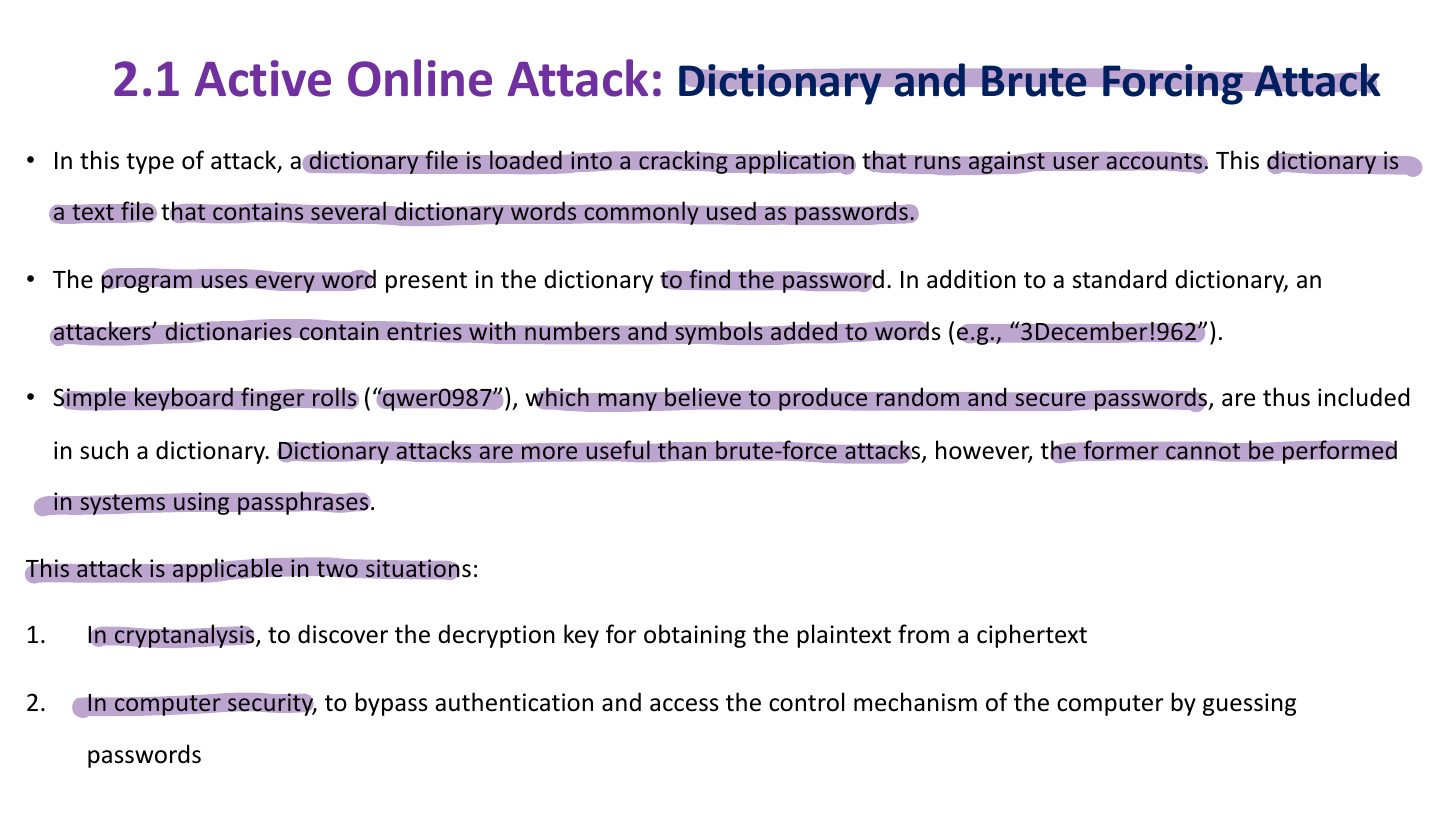
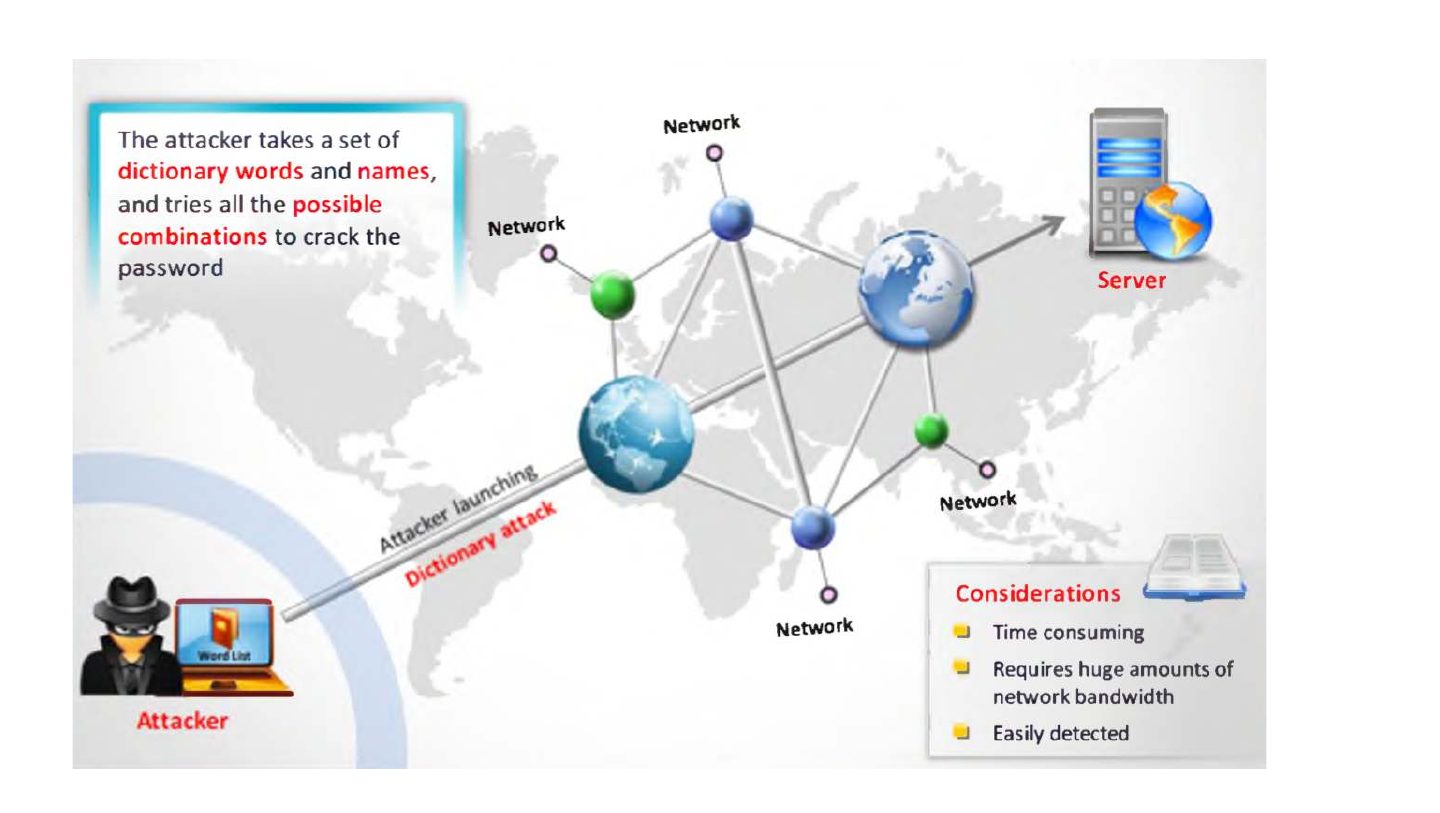
- 18 2.1 Active Online Attack: Dictionary and Brute Forcing Attack
- 19 Slide 19
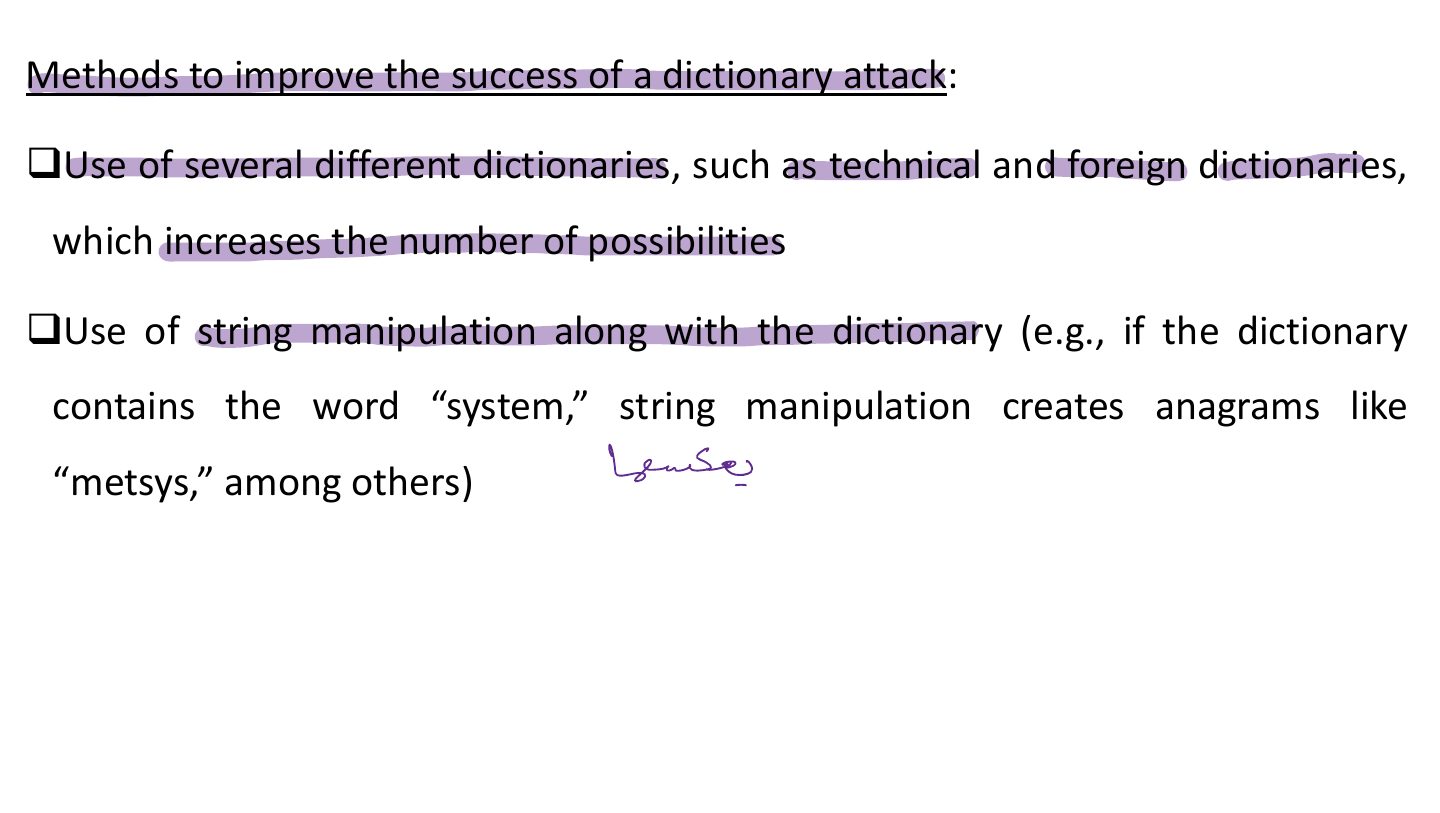
- 20 Methods to improve the success of a dictionary attack:
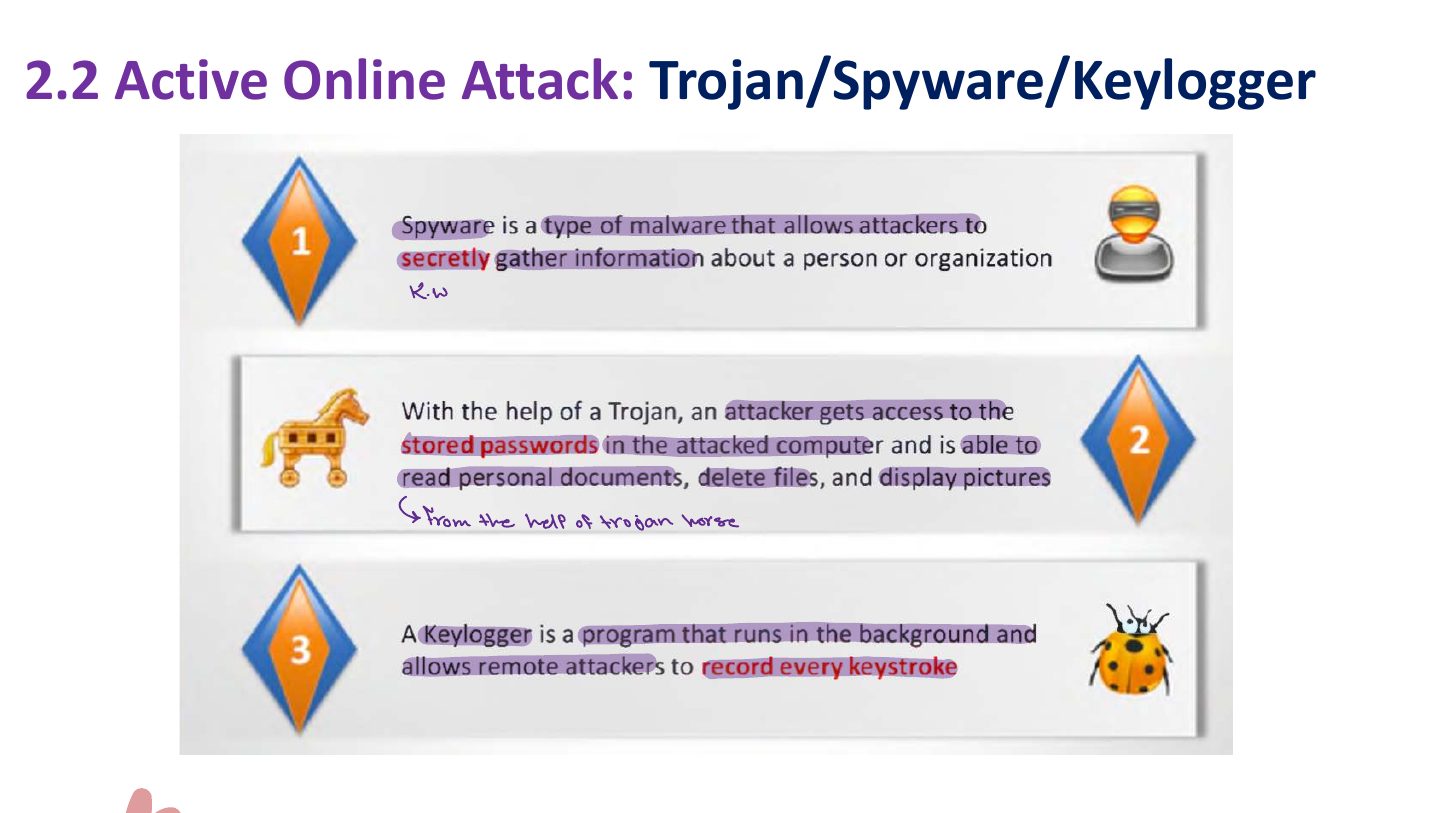
- 21 2.2 Active Online Attack: Trojan/Spyware/Keylogger
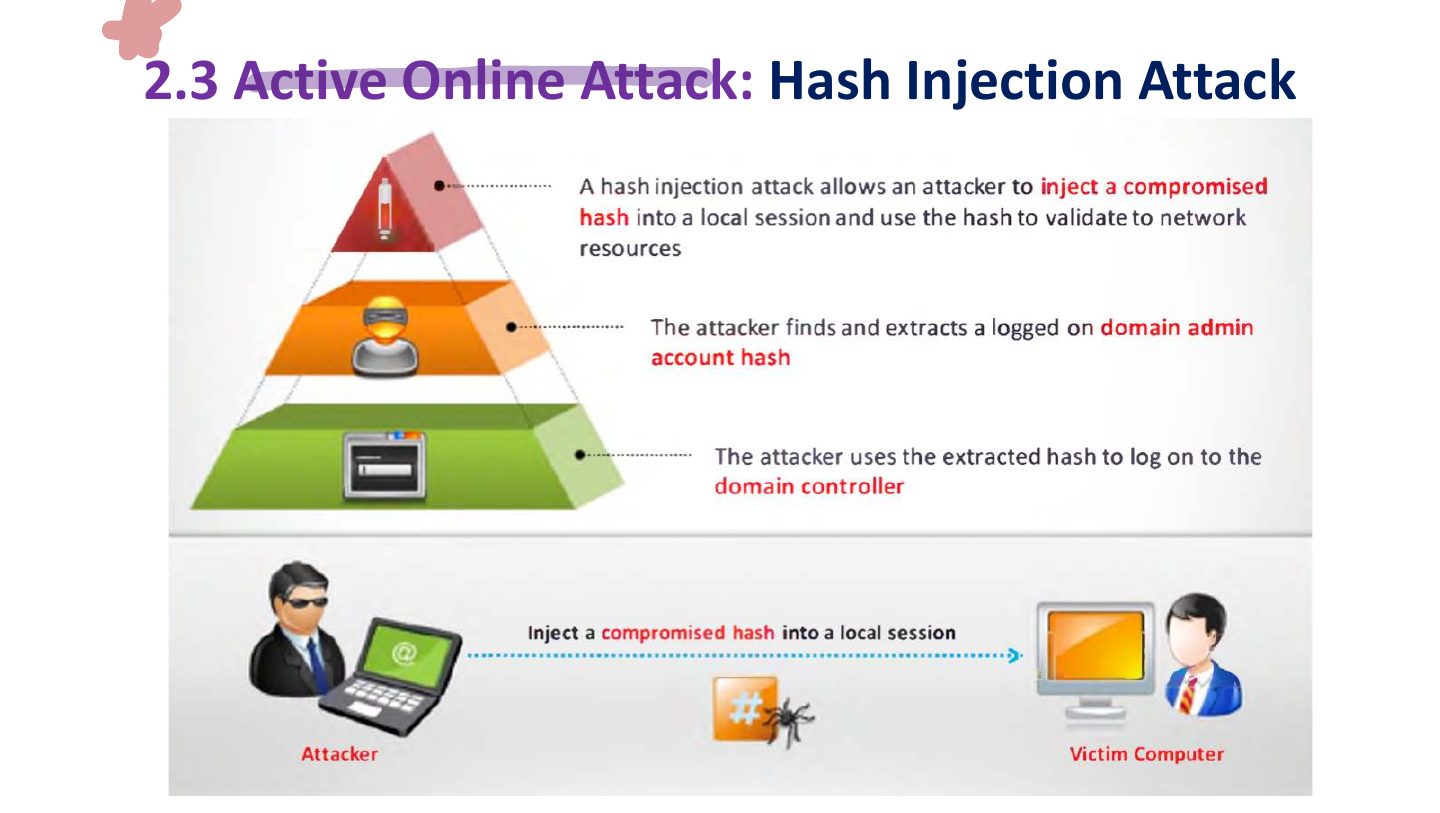
- 22 2.3 Active Online Attack: Hash Injection Attack
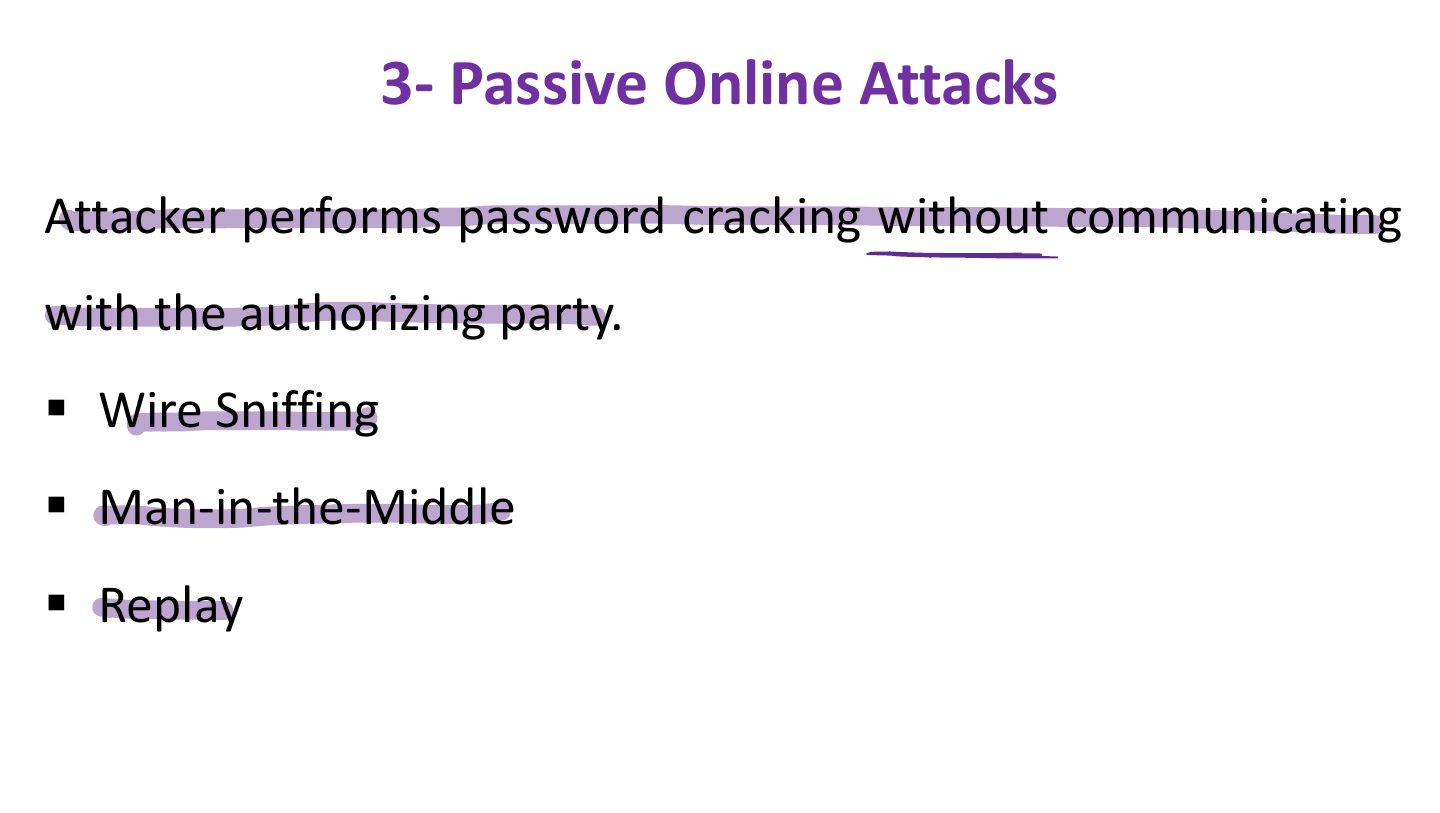
- 23 3- Passive Online Attacks
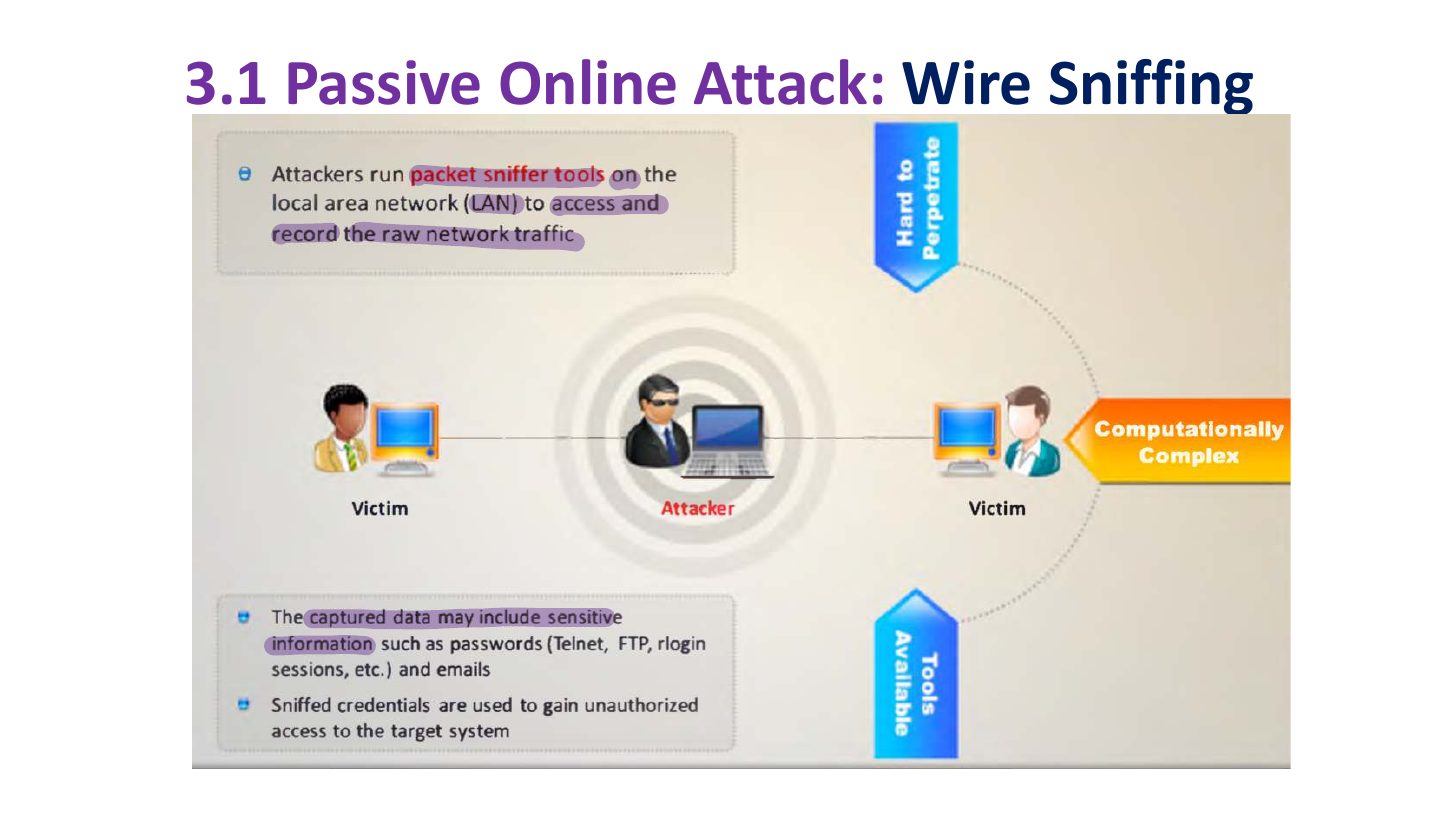
- 24 3.1 Passive Online Attack: Wire Sniffing
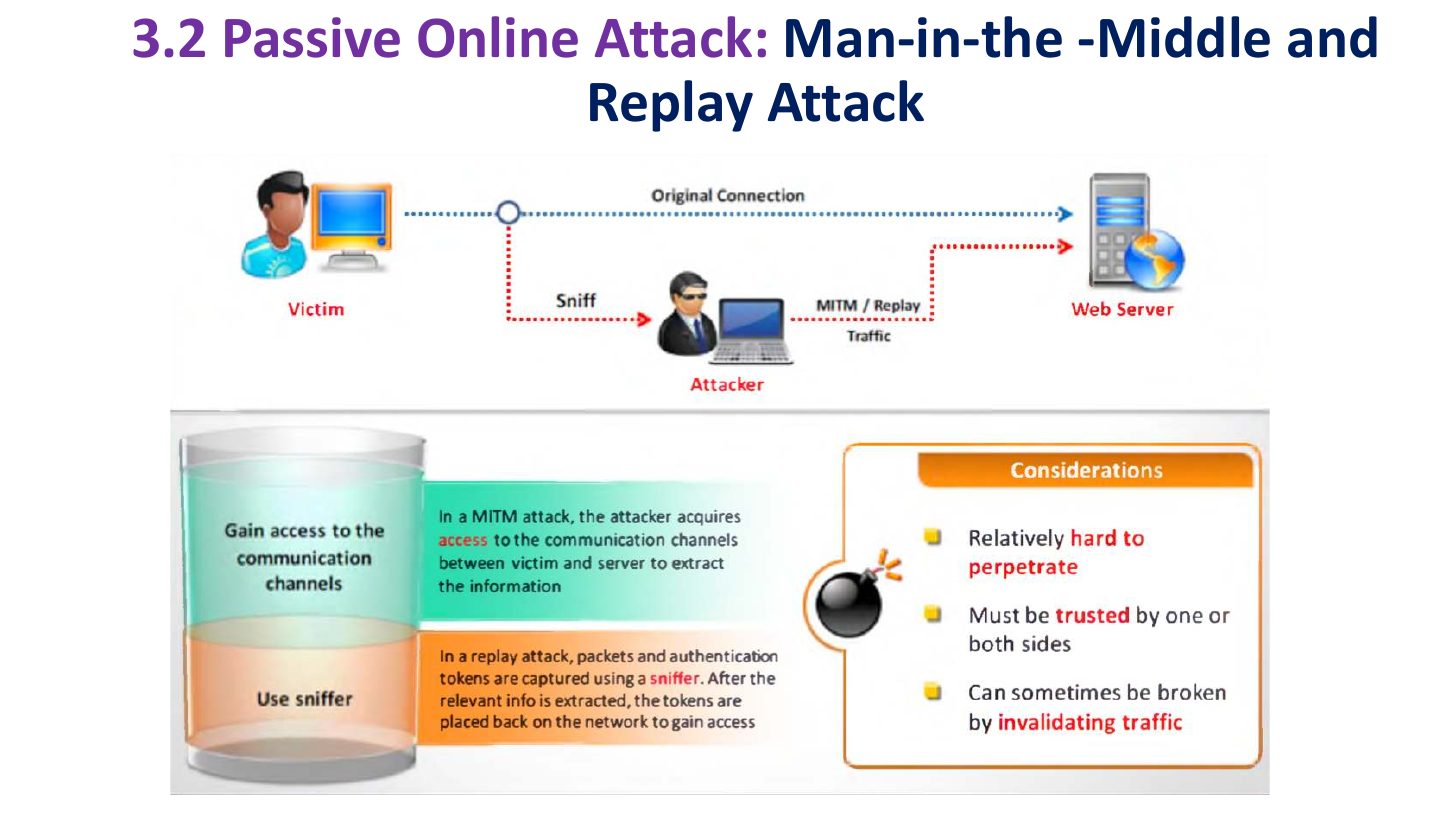
- 25 3.2 Passive Online Attack: Man-in-the -Middle and Replay Attack
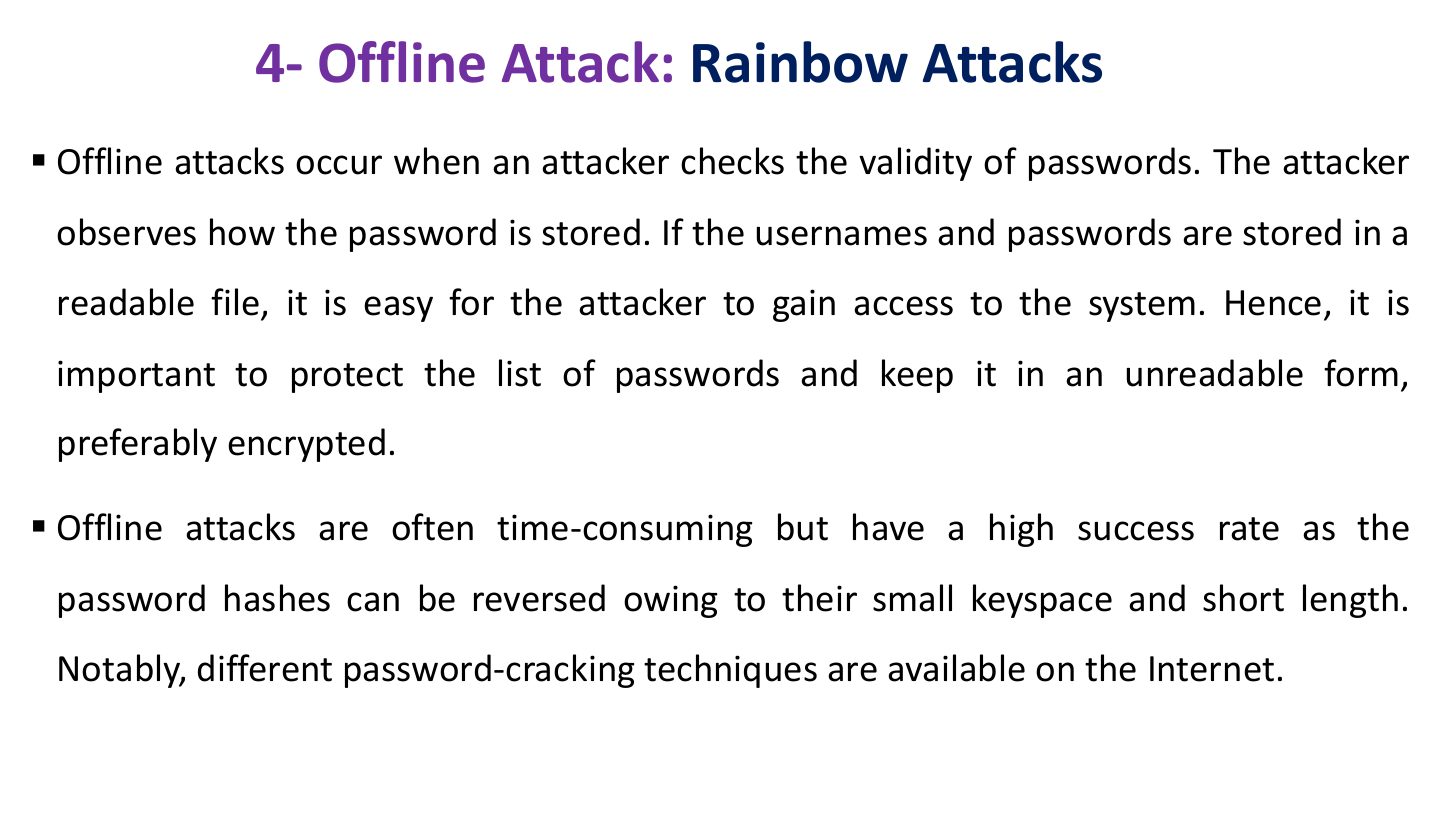
- 26 4- Offline Attack: Rainbow Attacks
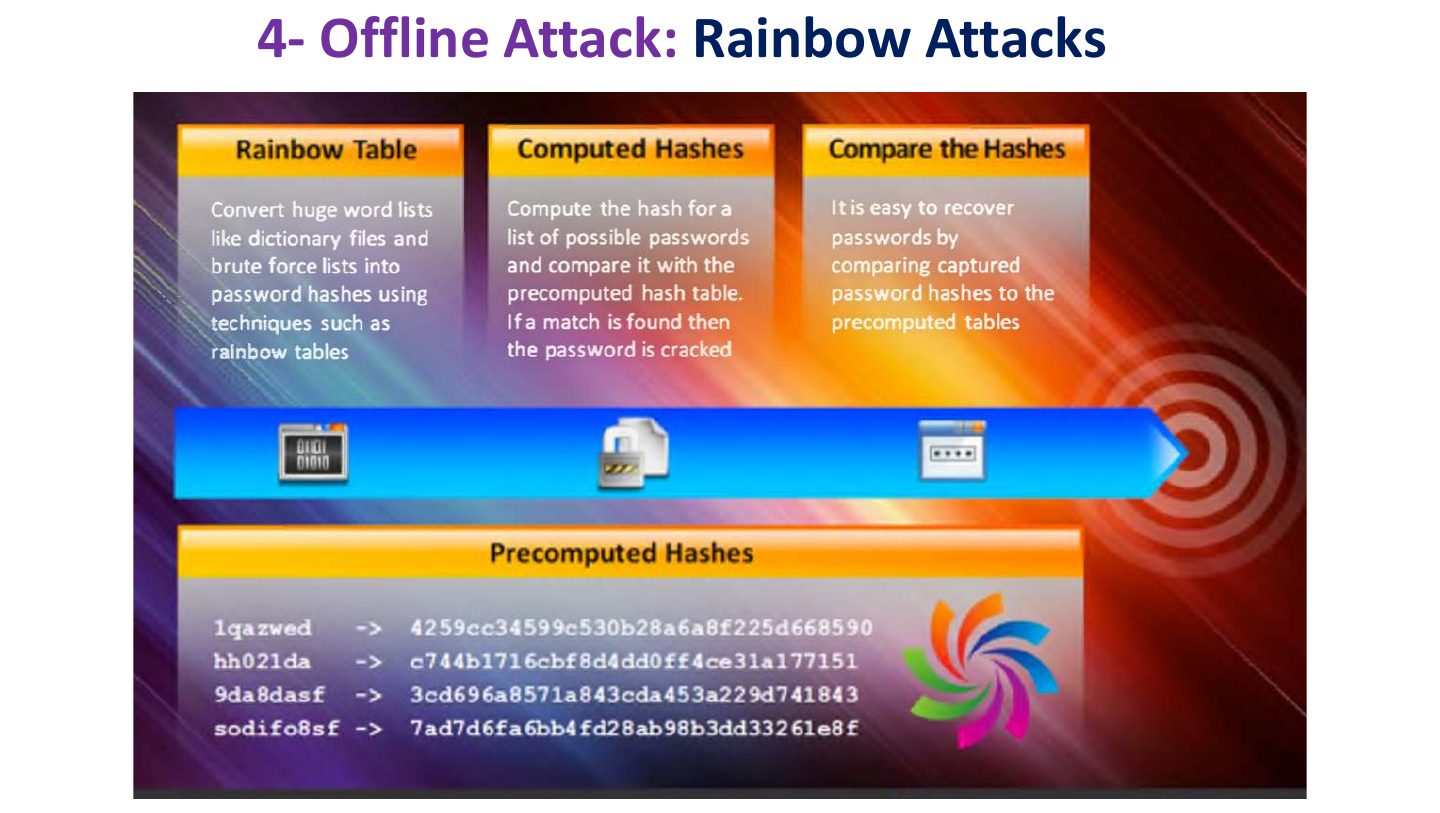
- 27 4- Offline Attack: Rainbow Attacks
- 28 5- Default Password
- 29 The following are some of the online tools to search default passwords:
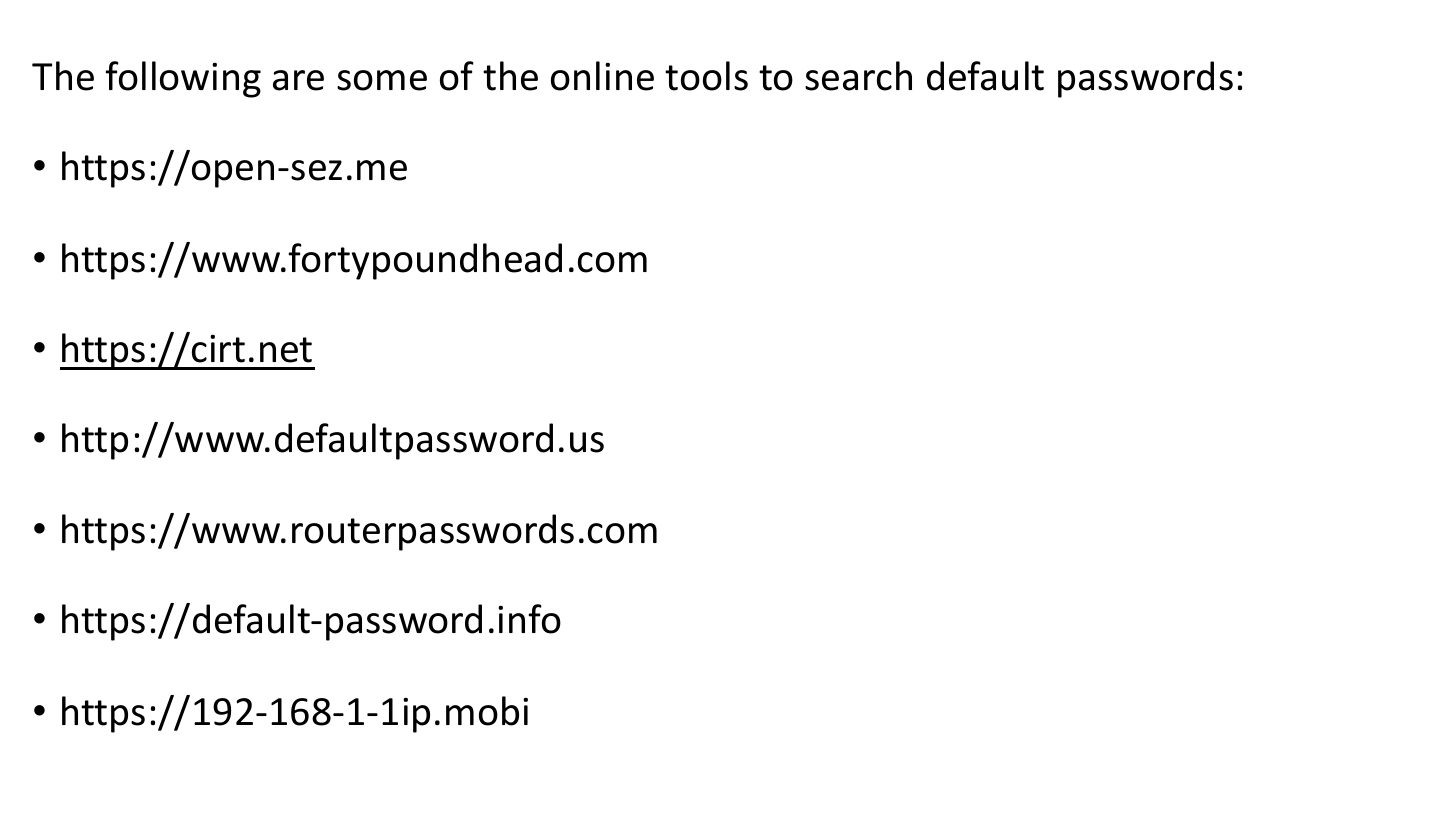
- 30 Using Password Cracking: Targets
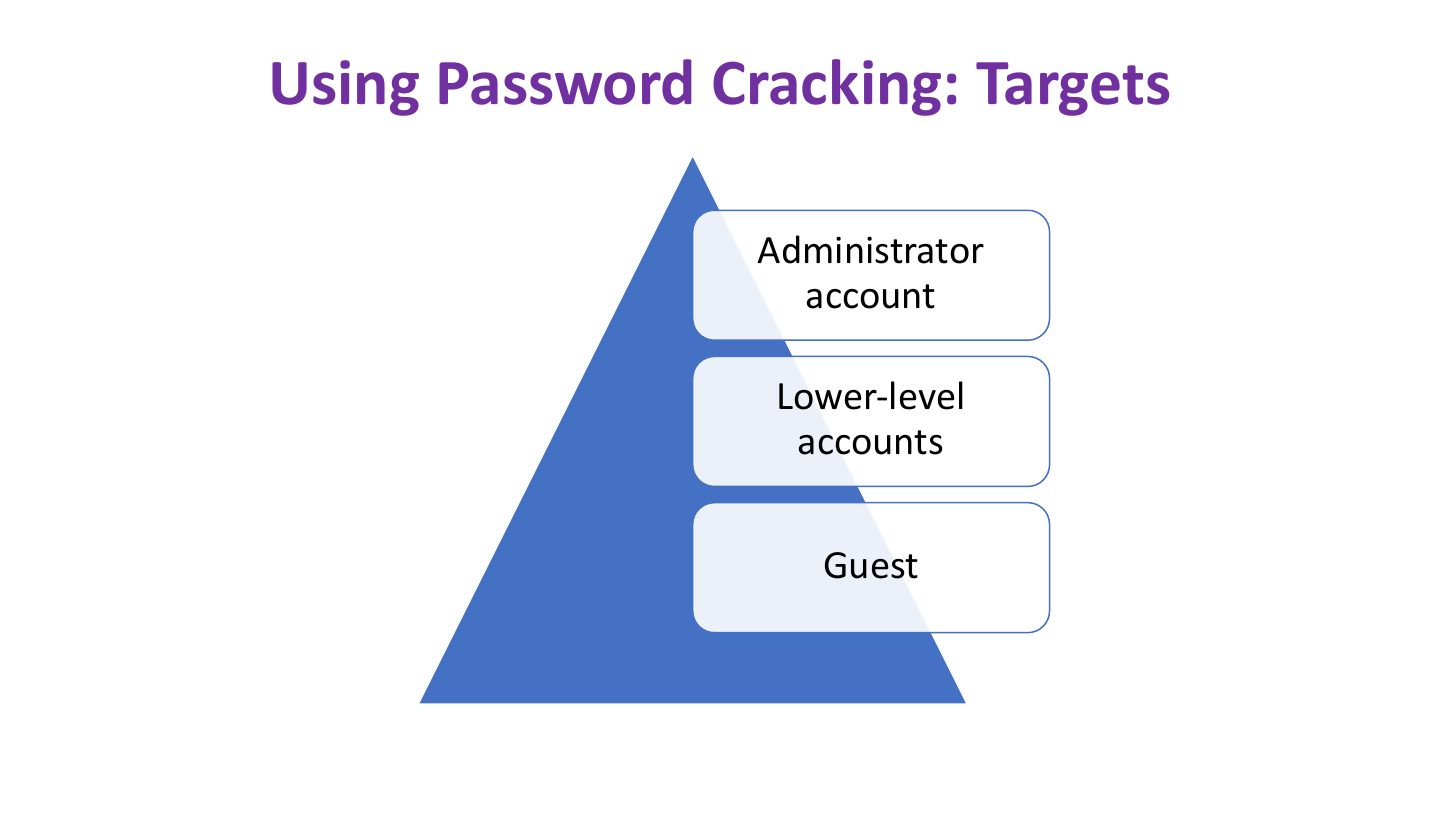
- 31 How to Defend against Password Cracking
- 32 Privilege Escalation
- 33 Types of Privilege Escalation :
- 34 Privilege Escalation Tools
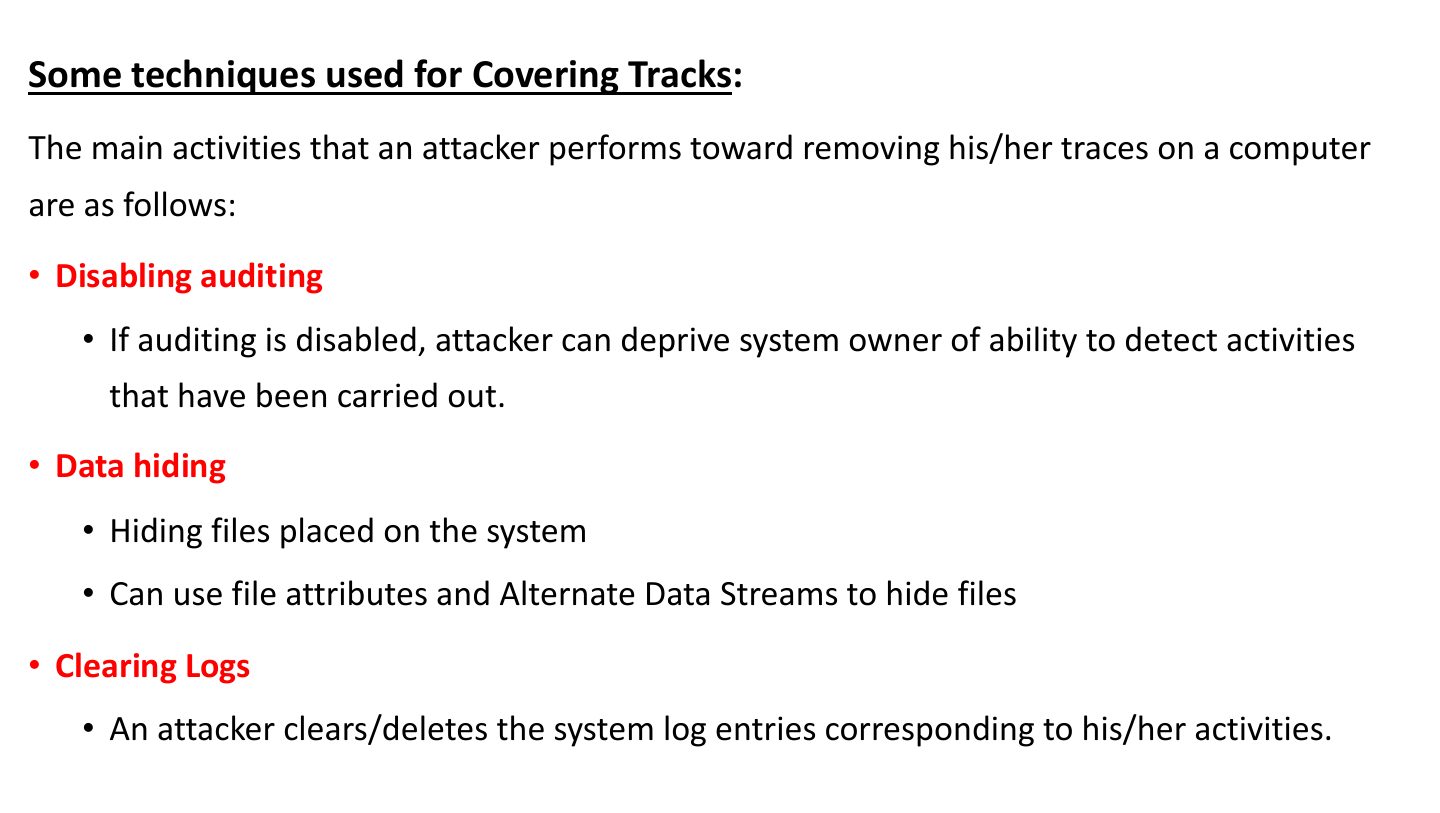
- 35 Maintaining Access
- 36 Executing Applications
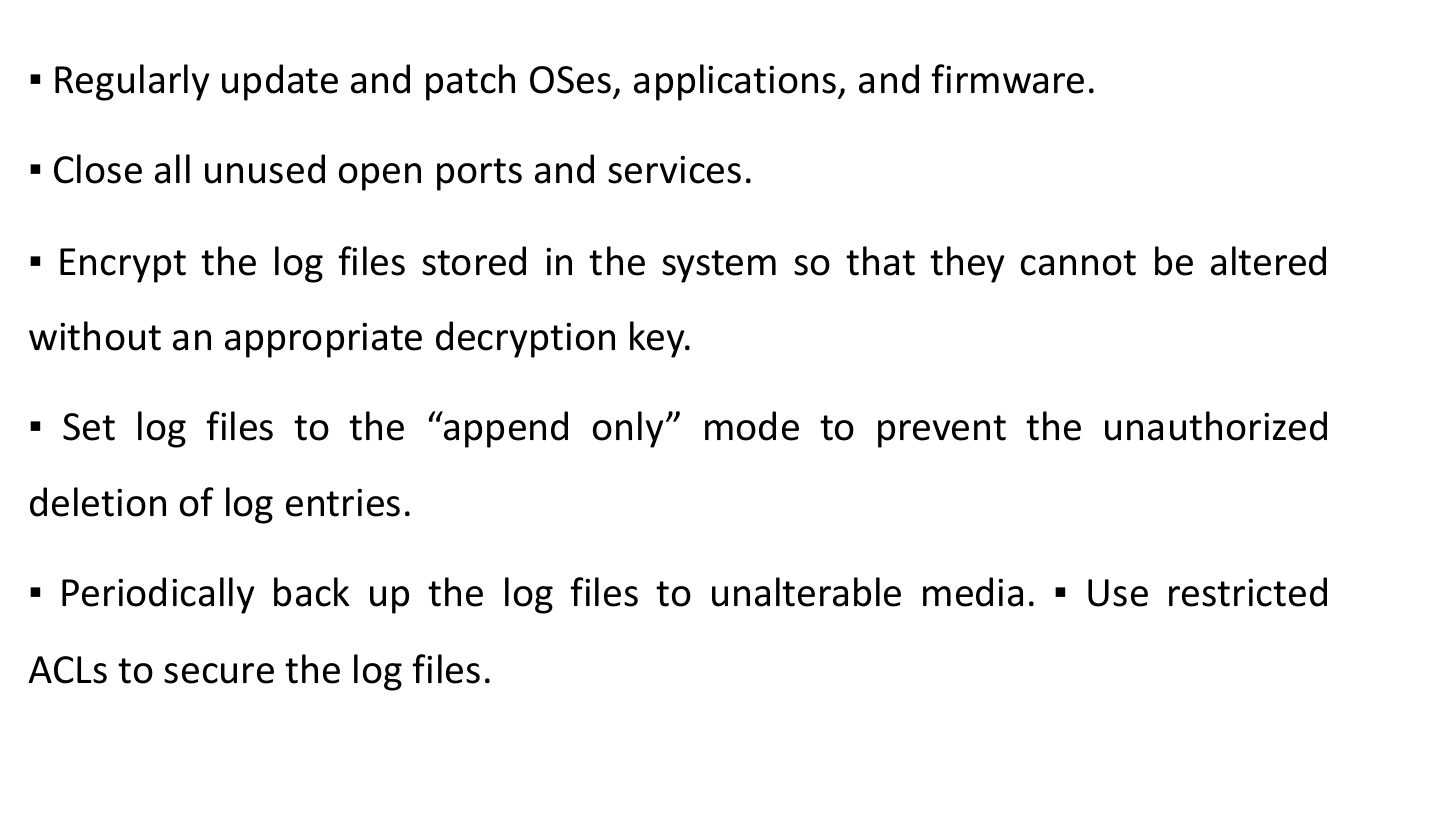
- 37 The malicious programs attackers execute on target systems can be:
- 38 Slide 38
- 39 Covering Tracks
- 40 Some techniques used for Covering Tracks:
- 41 Defending against Covering Tracks
- 42 ▪ Regularly update and patch OSes, applications, and firmware.
Slide 1
Information at Hand Before System Hacking Stage
Gaining Access
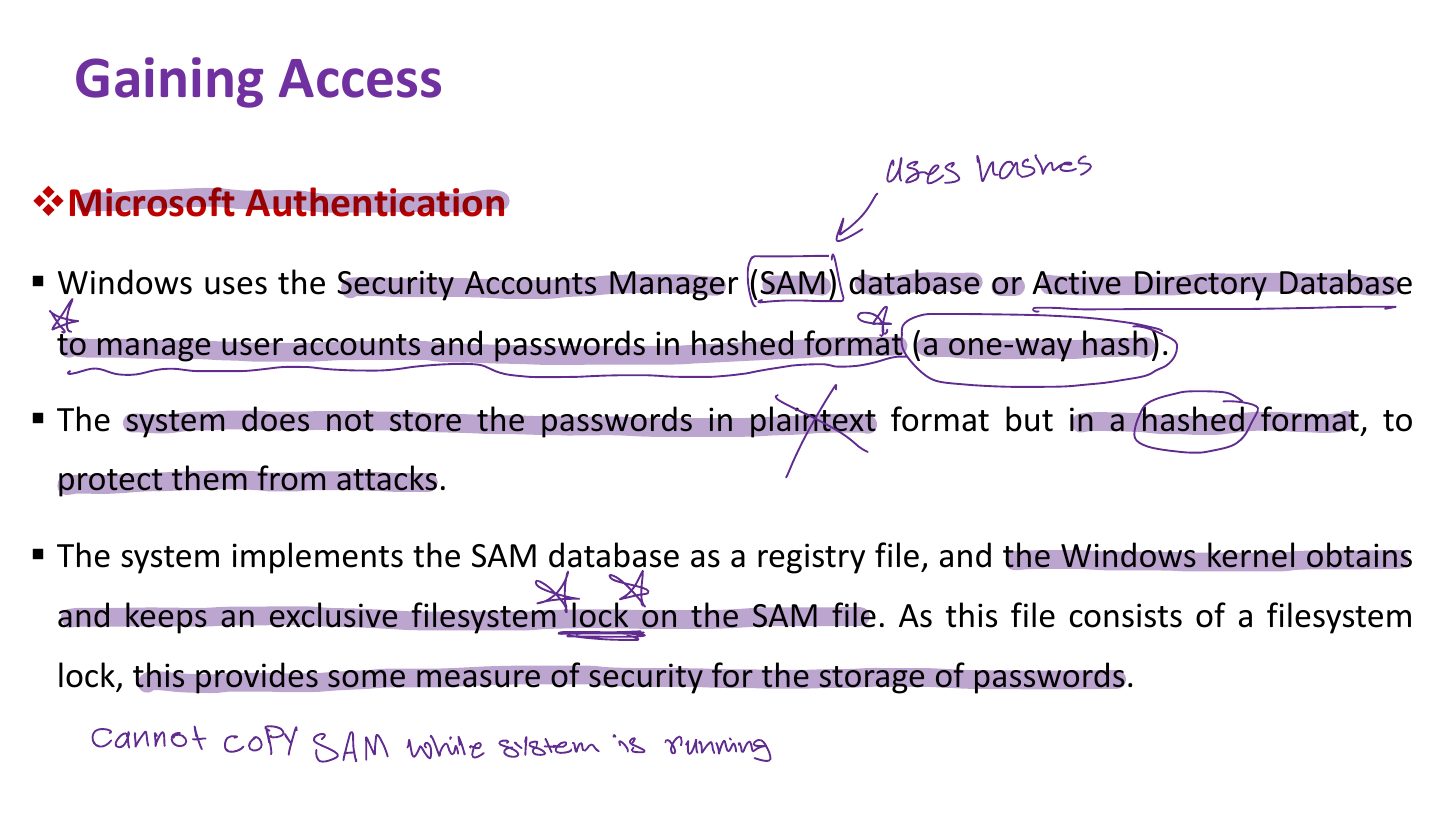
§ It is not possible to copy the SAM file to another location in the case of online
v NTLM Authentication
Notes
NTLM: challenge–response with the password hash. Kerberos (default in domains): tickets from a KDC.
v Kerberos Authentication
How Hash Passwords Are Stored in Windows SAM?
Notes
Windows stores password hashes (LM/NTLM) in the SAM file (C:\Windows\System32\config\SAM), locked while Windows runs.
Slide 8
System Hacking: Goals
Notes
Goals: gain access, escalate privileges, execute applications, hide files, cover tracks.
Gaining Access : CEH Hacking Methodology (CHM)
Slide 11
Password Cracking
Password Complexity
Password Cracking Techniques
Types of Password Cracking
Notes
Password attacks: non-electronic (shoulder surfing, social engineering, dumpster diving), active online, passive online, offline.
1- Non-Electronic attack
2- Active Online Attacks
2.1 Active Online Attack: Dictionary and Brute Forcing Attack
Notes
Dictionary attack: try words from a list. Brute force: every combination. Hybrid: words + numbers/symbols.
Exam angle
Slide 19
Methods to improve the success of a dictionary attack:
2.2 Active Online Attack: Trojan/Spyware/Keylogger
2.3 Active Online Attack: Hash Injection Attack
3- Passive Online Attacks
3.1 Passive Online Attack: Wire Sniffing
3.2 Passive Online Attack: Man-in-the -Middle and Replay Attack
4- Offline Attack: Rainbow Attacks
Notes
Rainbow tables: precomputed hash → password tables; fast lookups. Defeated by salting.
Memory trick Salt = a random value added before hashing, so the same password hashes differently and precomputed tables fail.
Exam angle
The best defense against rainbow-table attacks is:
4- Offline Attack: Rainbow Attacks
5- Default Password
The following are some of the online tools to search default passwords:
Using Password Cracking: Targets
How to Defend against Password Cracking
Notes
Defenses: long complex passwords, lockout policies, MFA, salted hashes, no defaults, monitoring.
Privilege Escalation
Notes
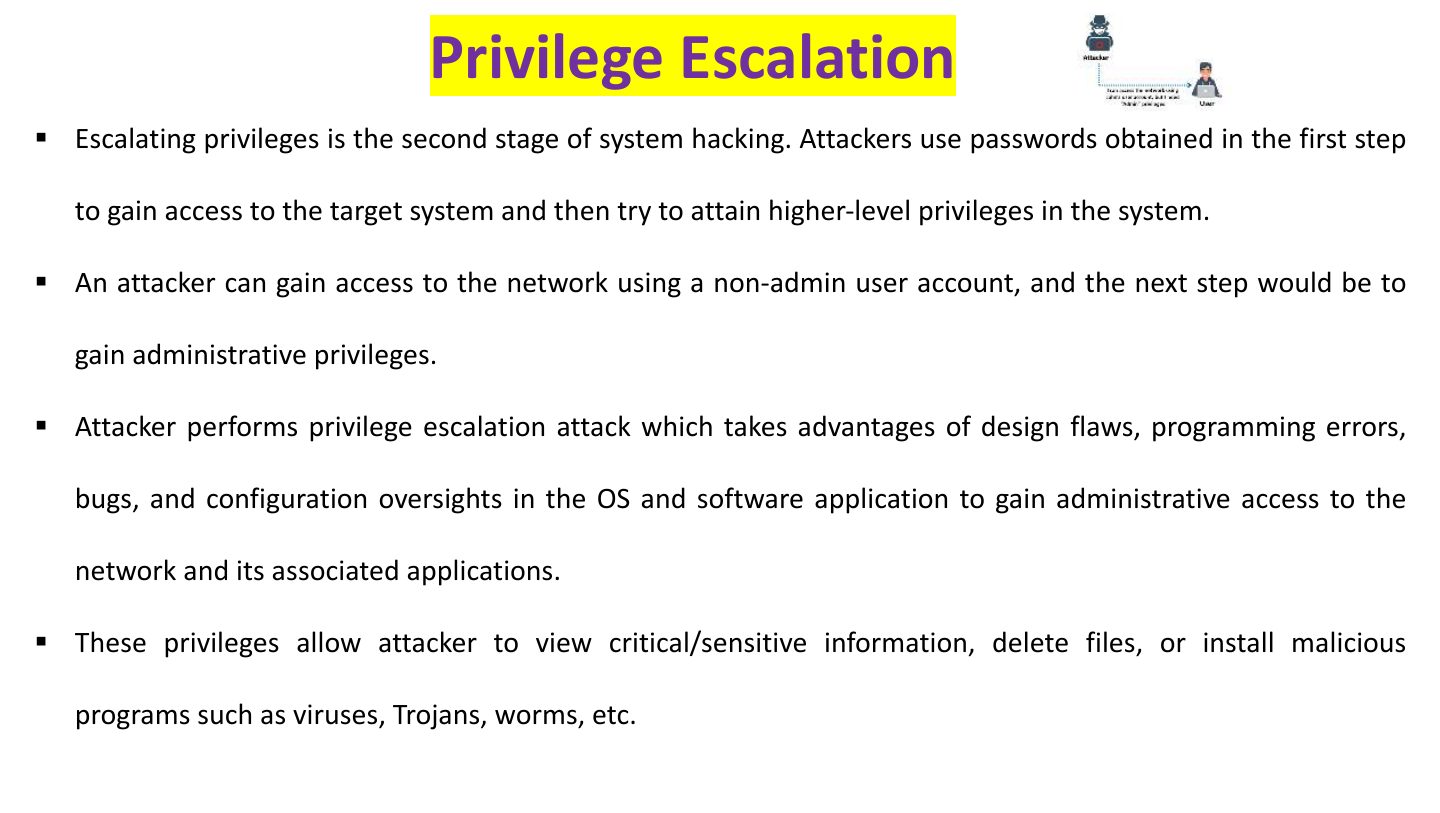
Privilege escalation: vertical (user → admin) or horizontal (access another user’s resources at the same level).
Exam angle
A normal user gaining administrator rights is:
Types of Privilege Escalation :
Privilege Escalation Tools
Maintaining Access
Executing Applications
The malicious programs attackers execute on target systems can be:
Notes
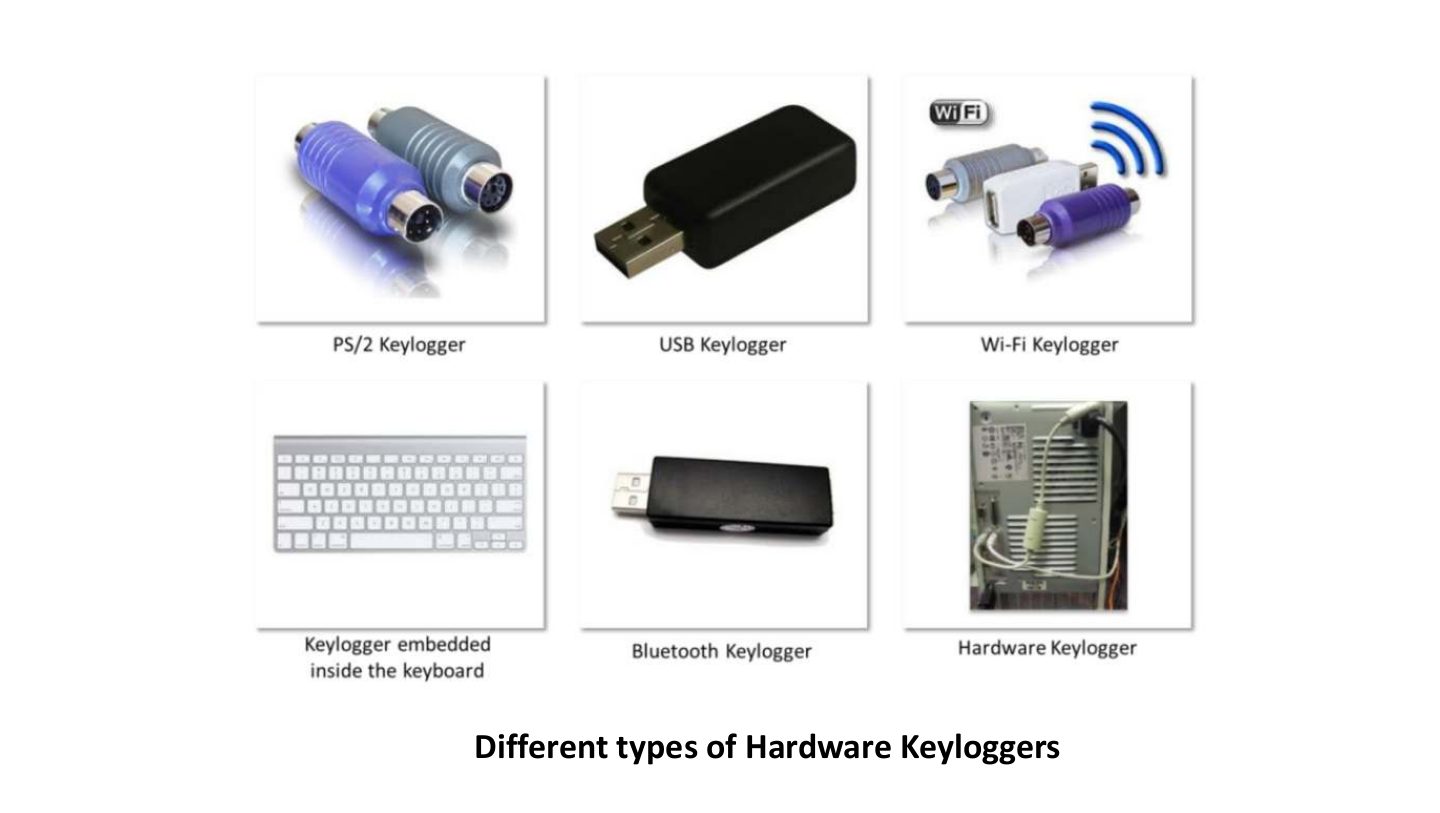
Keyloggers (hardware or software) record keystrokes; spyware hides and reports activity.
Slide 38
Covering Tracks
Notes
Covering tracks: clear or edit logs (auditpol, clearing event logs), hide files (ADS, steganography), rootkits.
Some techniques used for Covering Tracks:
Defending against Covering Tracks
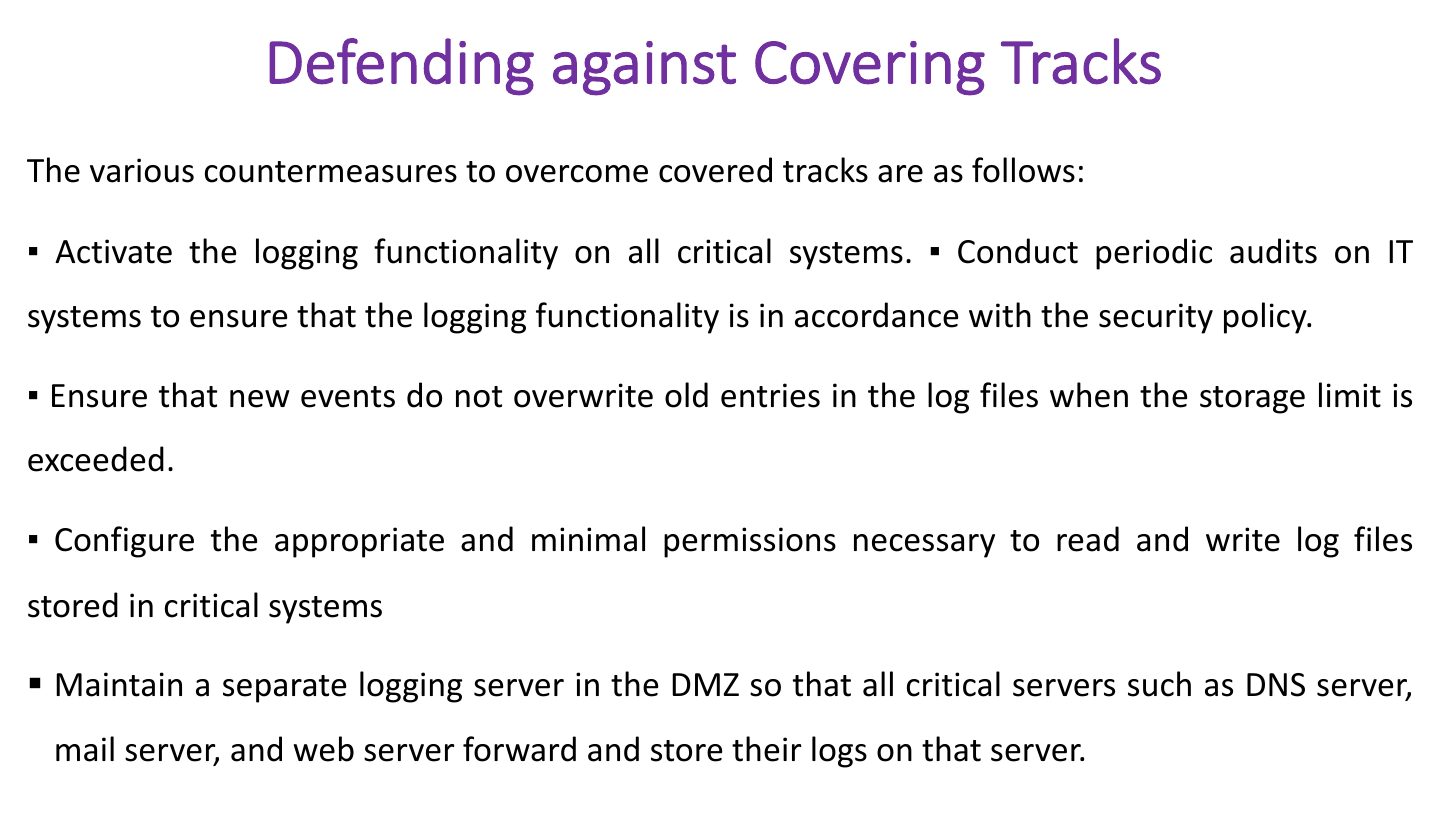
▪ Regularly update and patch OSes, applications, and firmware.