SQL injection’s threat type; what is not a threat
Threat and Vulnerability Management
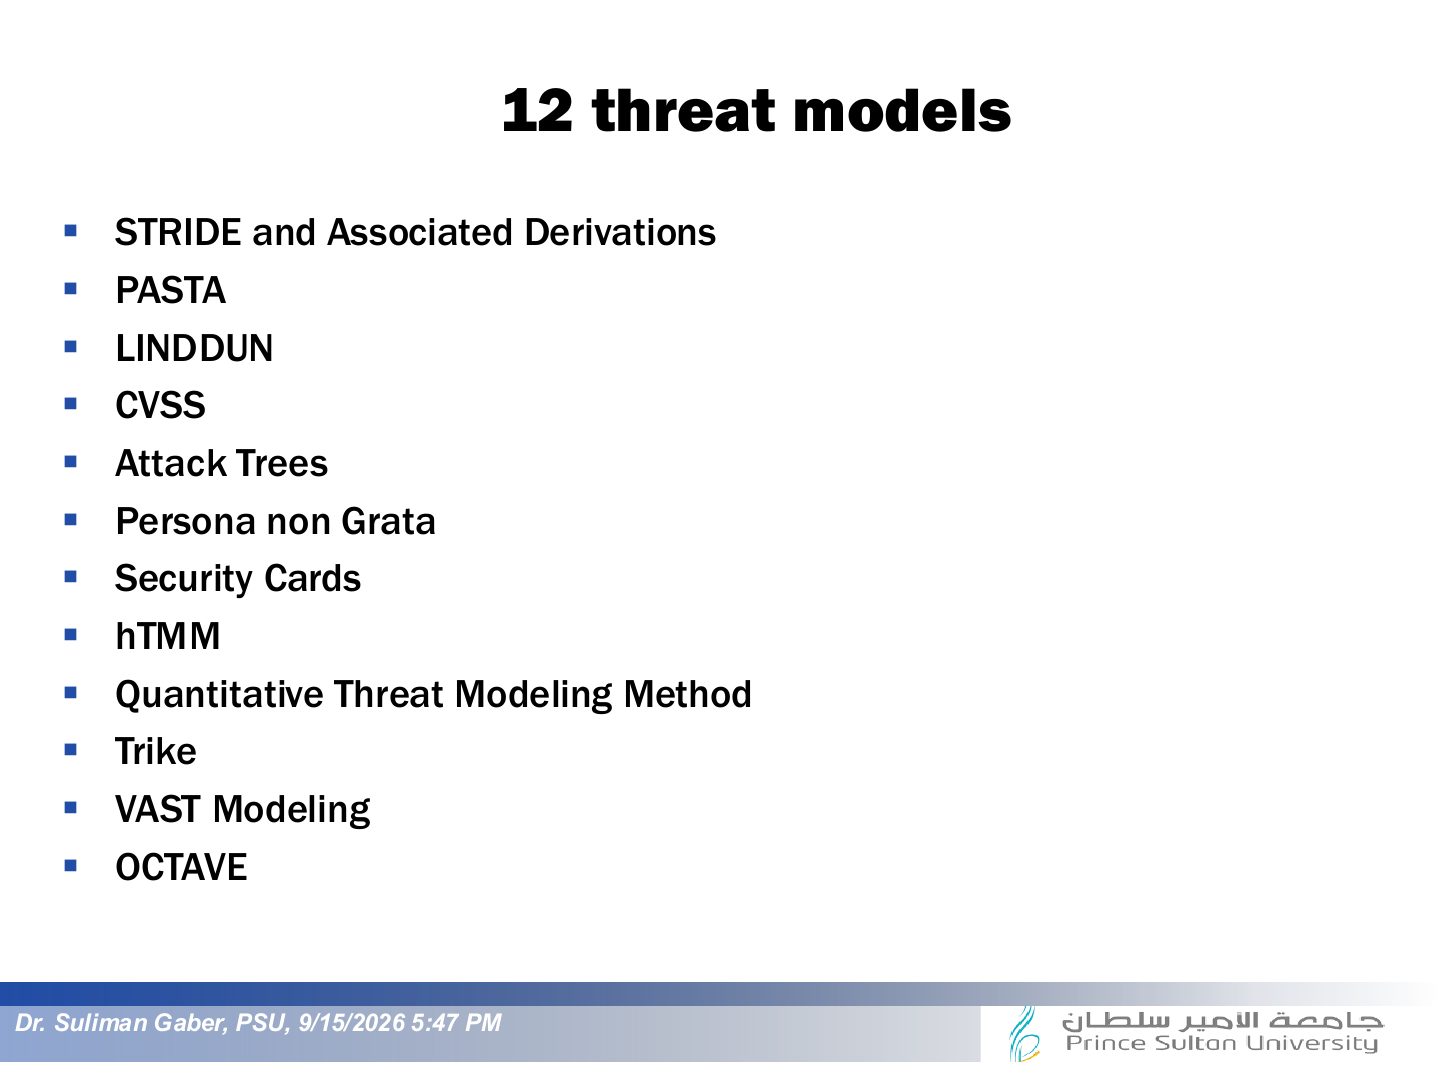
Threat sources and types (network, host, application), threat agents, common vulnerabilities and CVE, threat modeling methods (STRIDE, PASTA, LINDDUN, CVSS, attack trees, persona non grata, security cards, hTMM, Trike, VAST, OCTAVE, DREAD) and threat/vulnerability pairs.
How to read this page
Every original slide is shown unchanged. Yellow marks on a slide point to a numbered note: hover or tap a mark to jump to its note, and hover a note to see its marks. Questions tagged Past exam appeared on a real paper; Prediction questions are likely angles, not confirmed. Pick an answer to each question: a wrong pick tells you why it is wrong, so you can try again.
All 53 slides
- 1 Slide 1
- 2 Intended Learning Outcomes
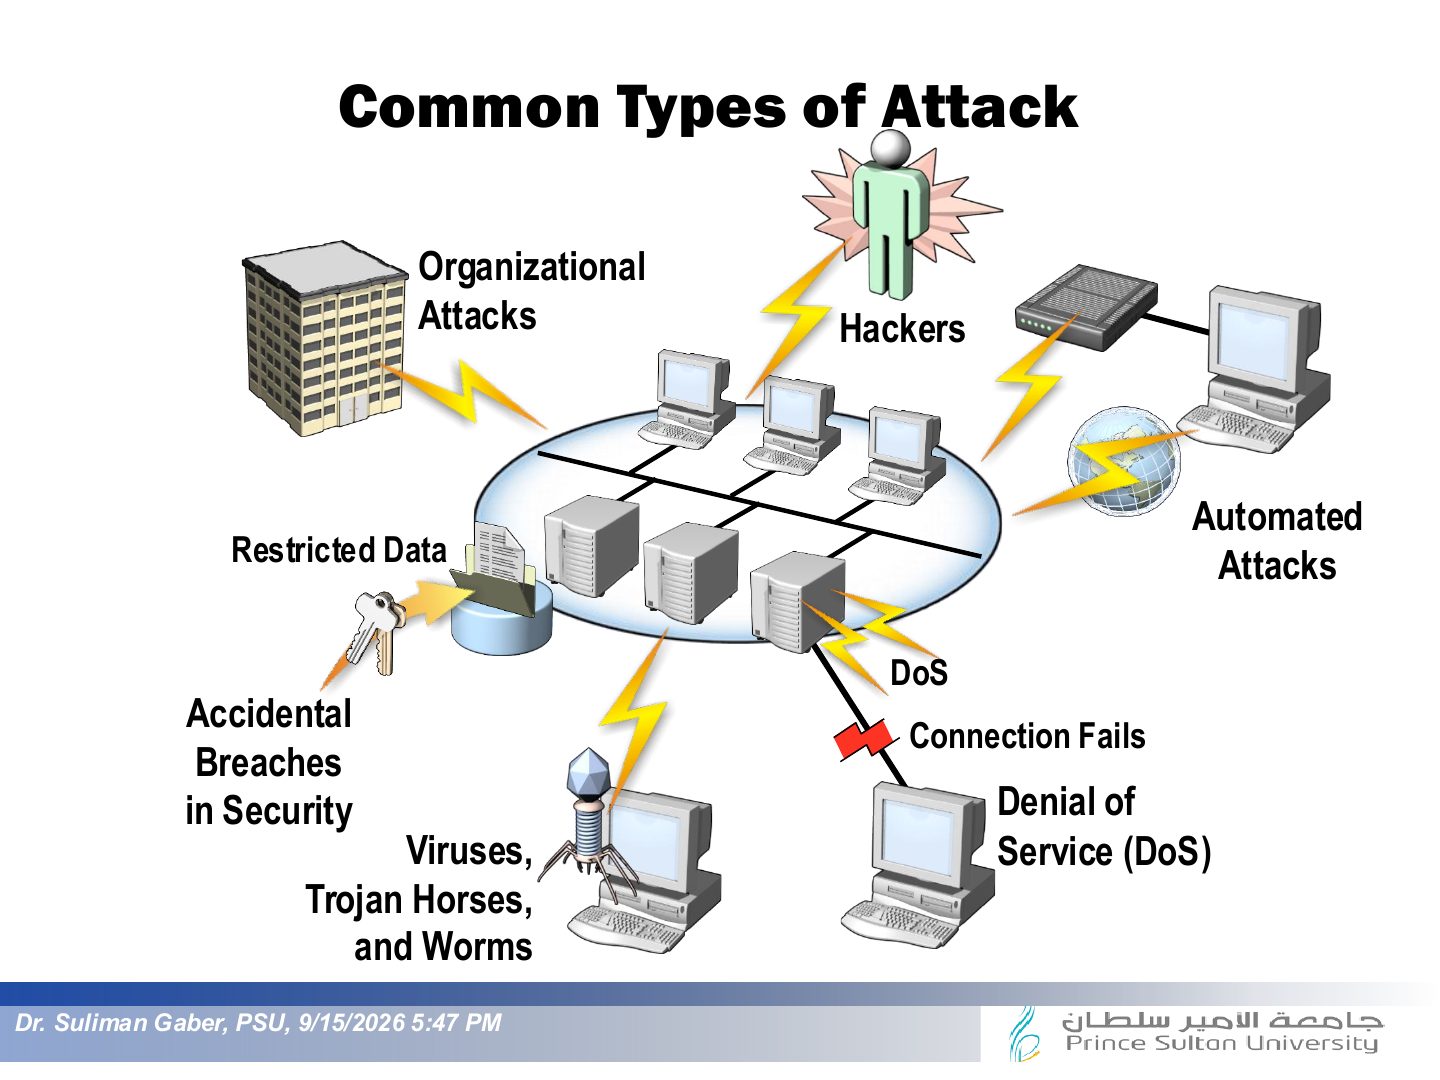
- 3 Common Types of Attack
- 4 Introduction
- 5 Introduction
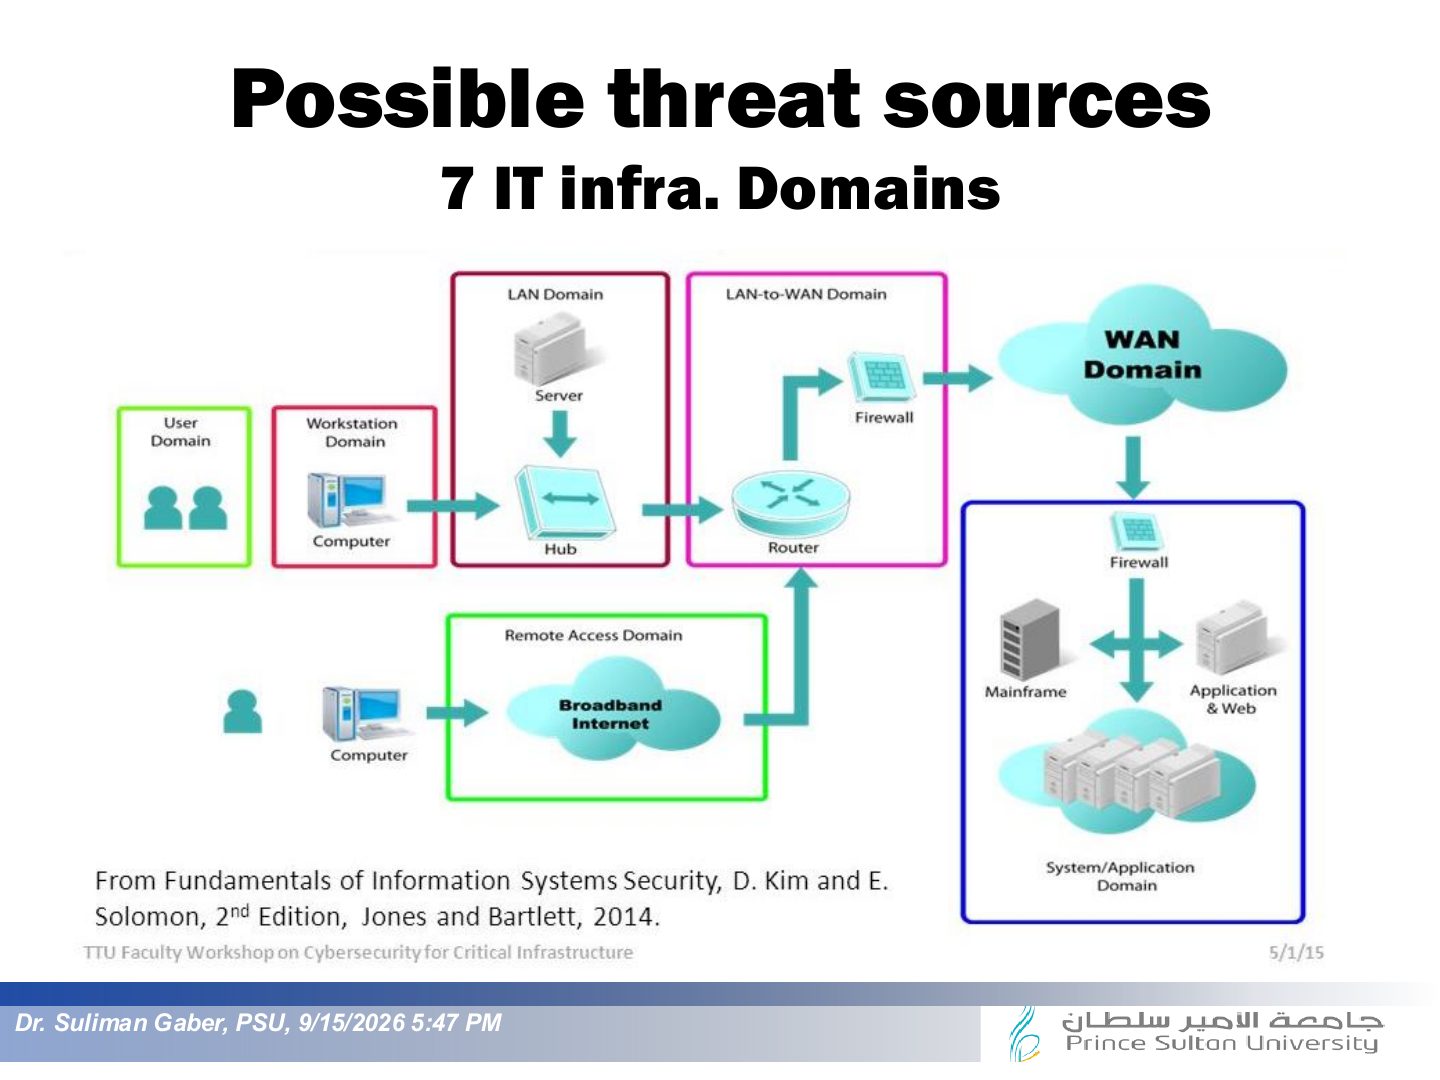
- 6 Possible threat sources
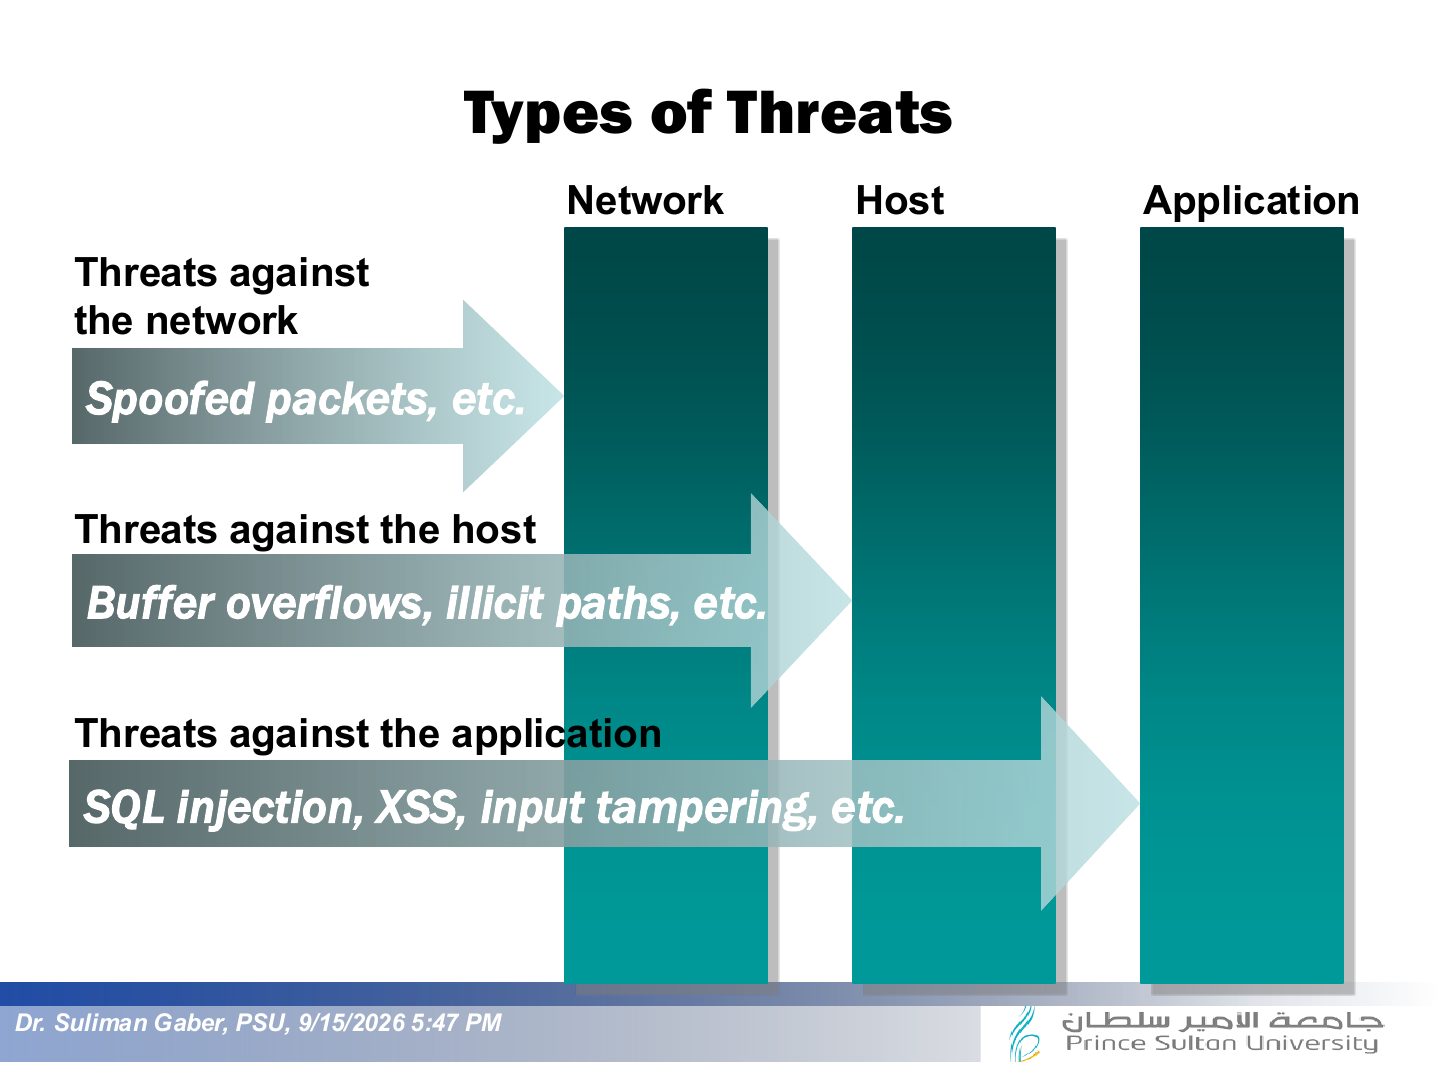
- 7 Types of Threats
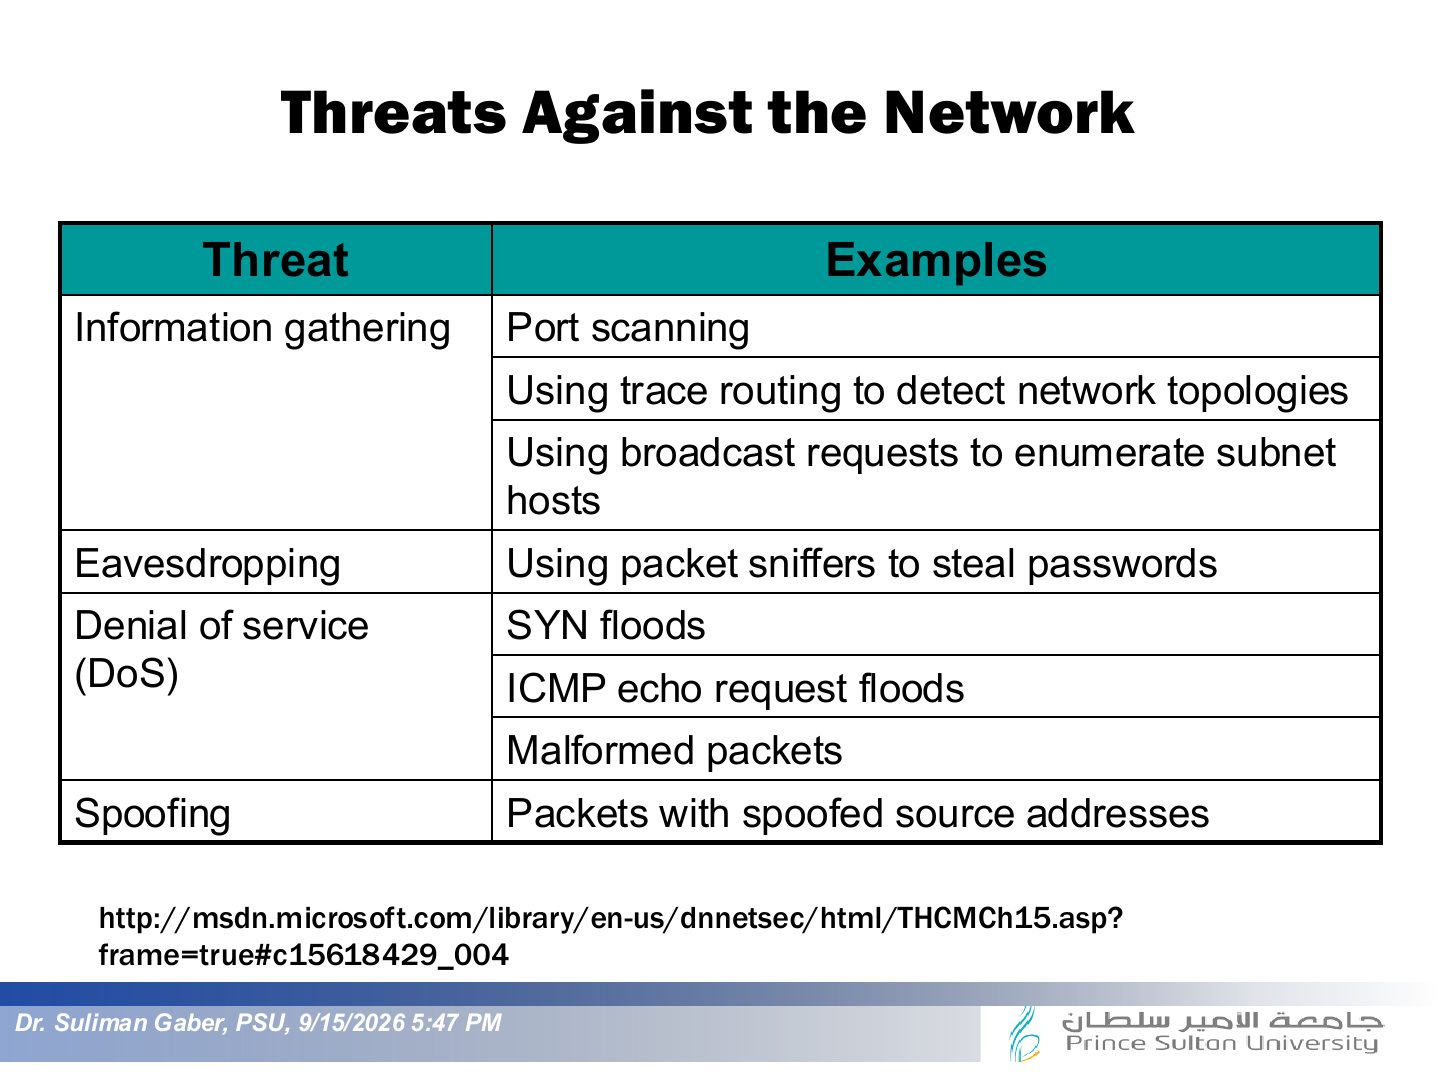
- 8 Threats Against the Network
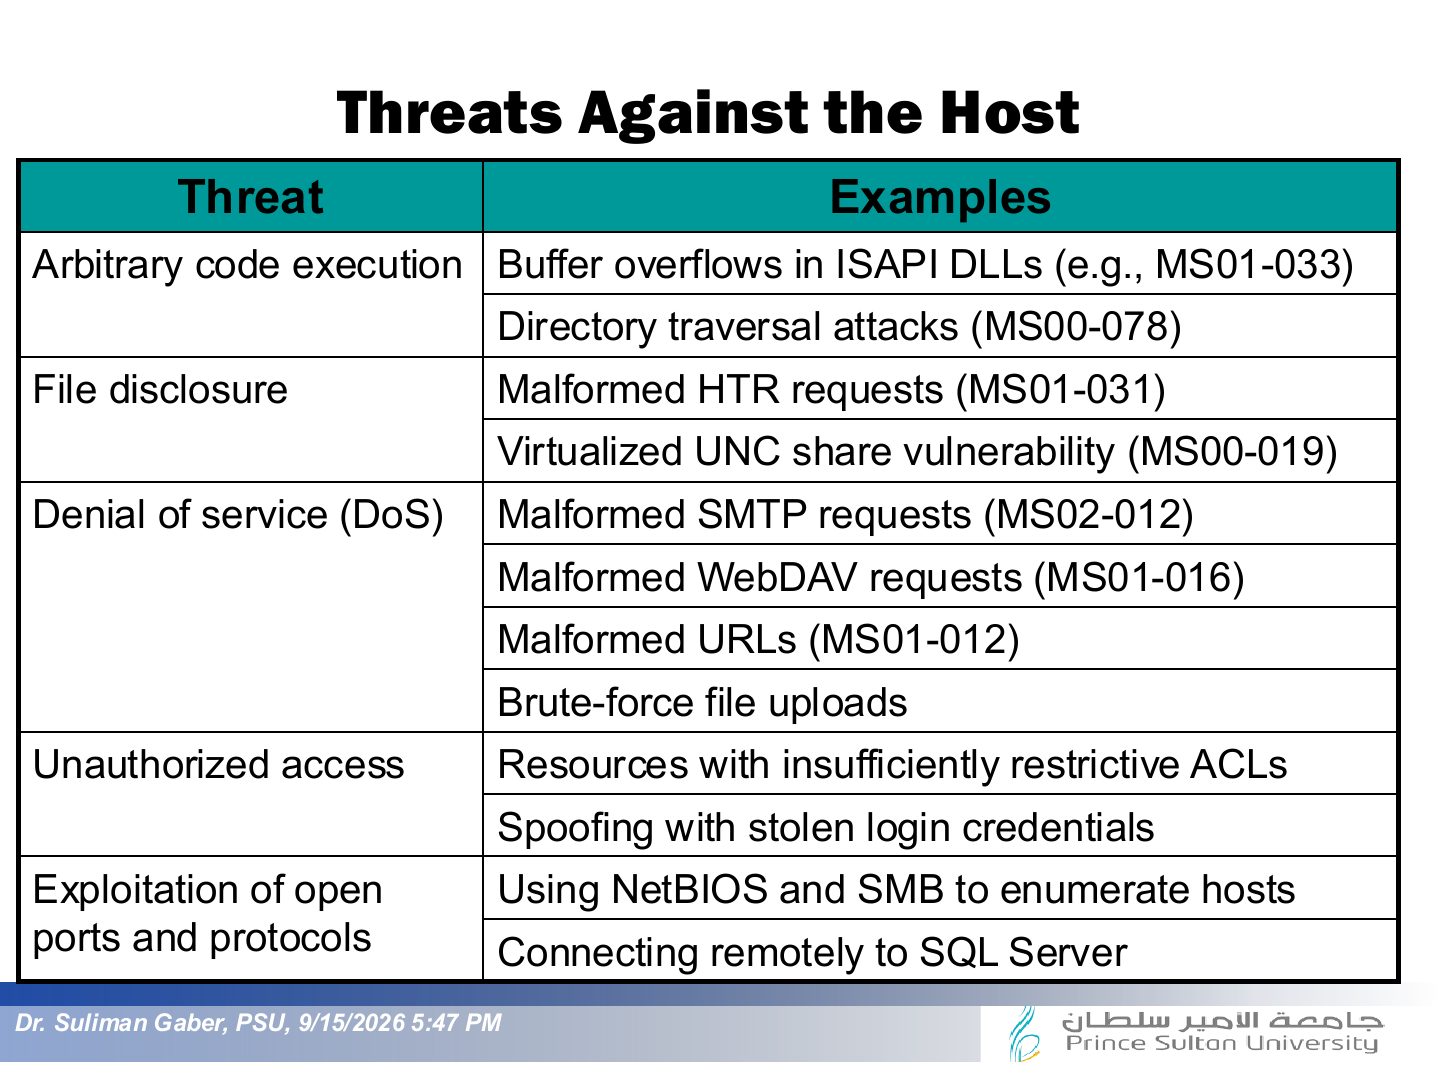
- 9 Threats Against the Host
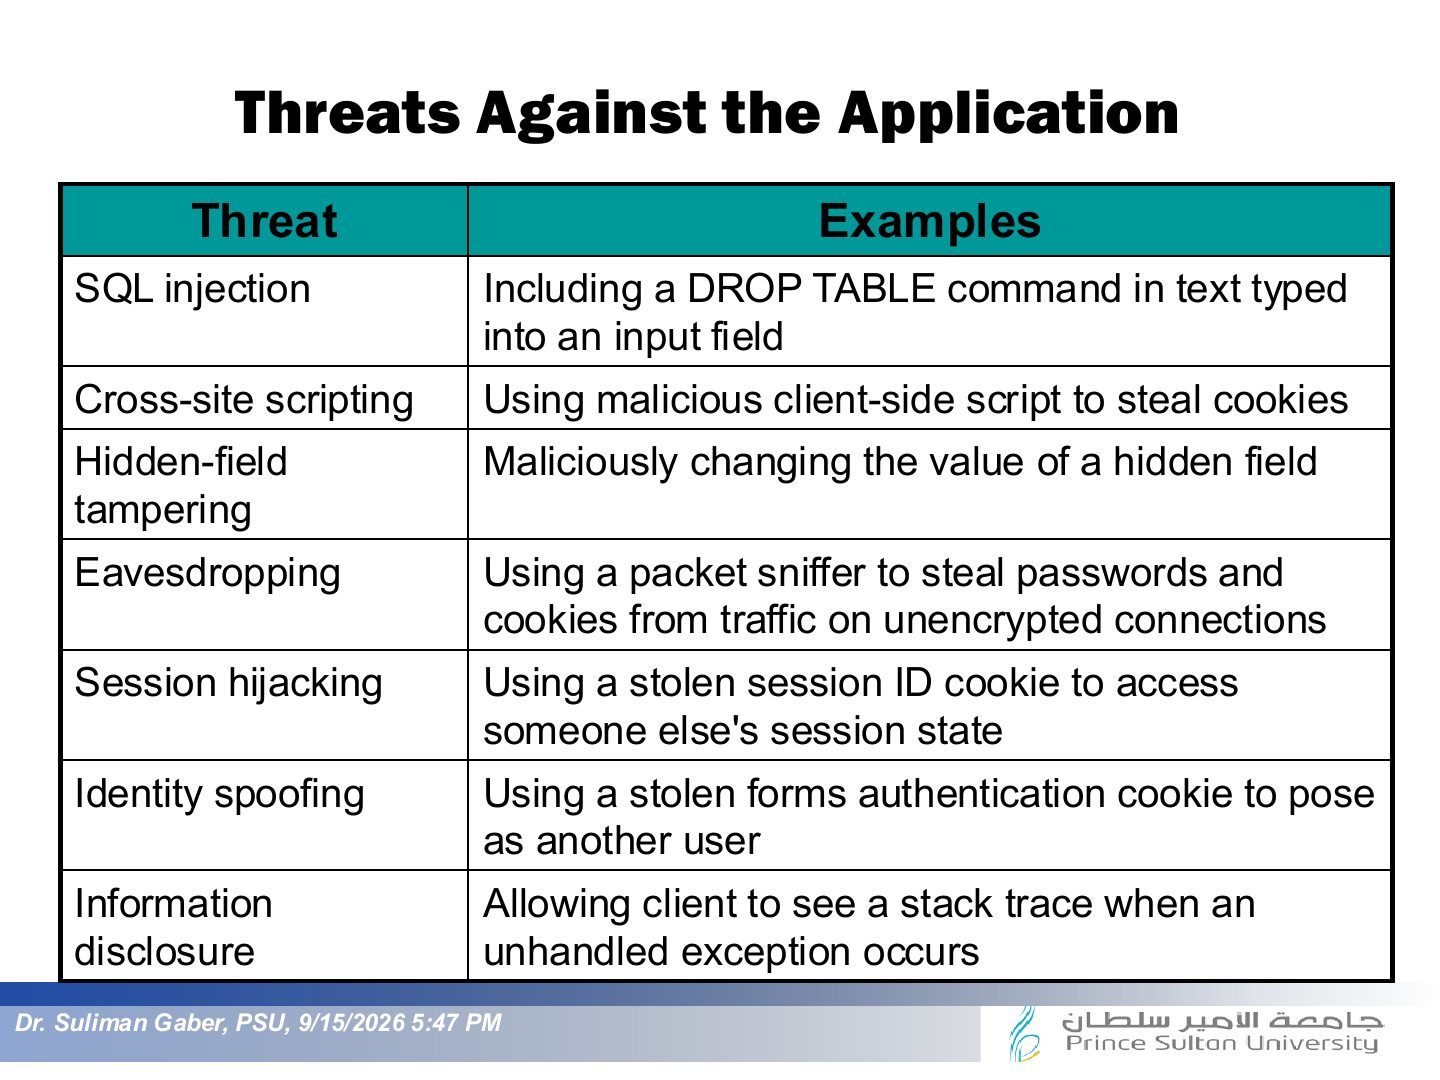
- 10 Threats Against the Application
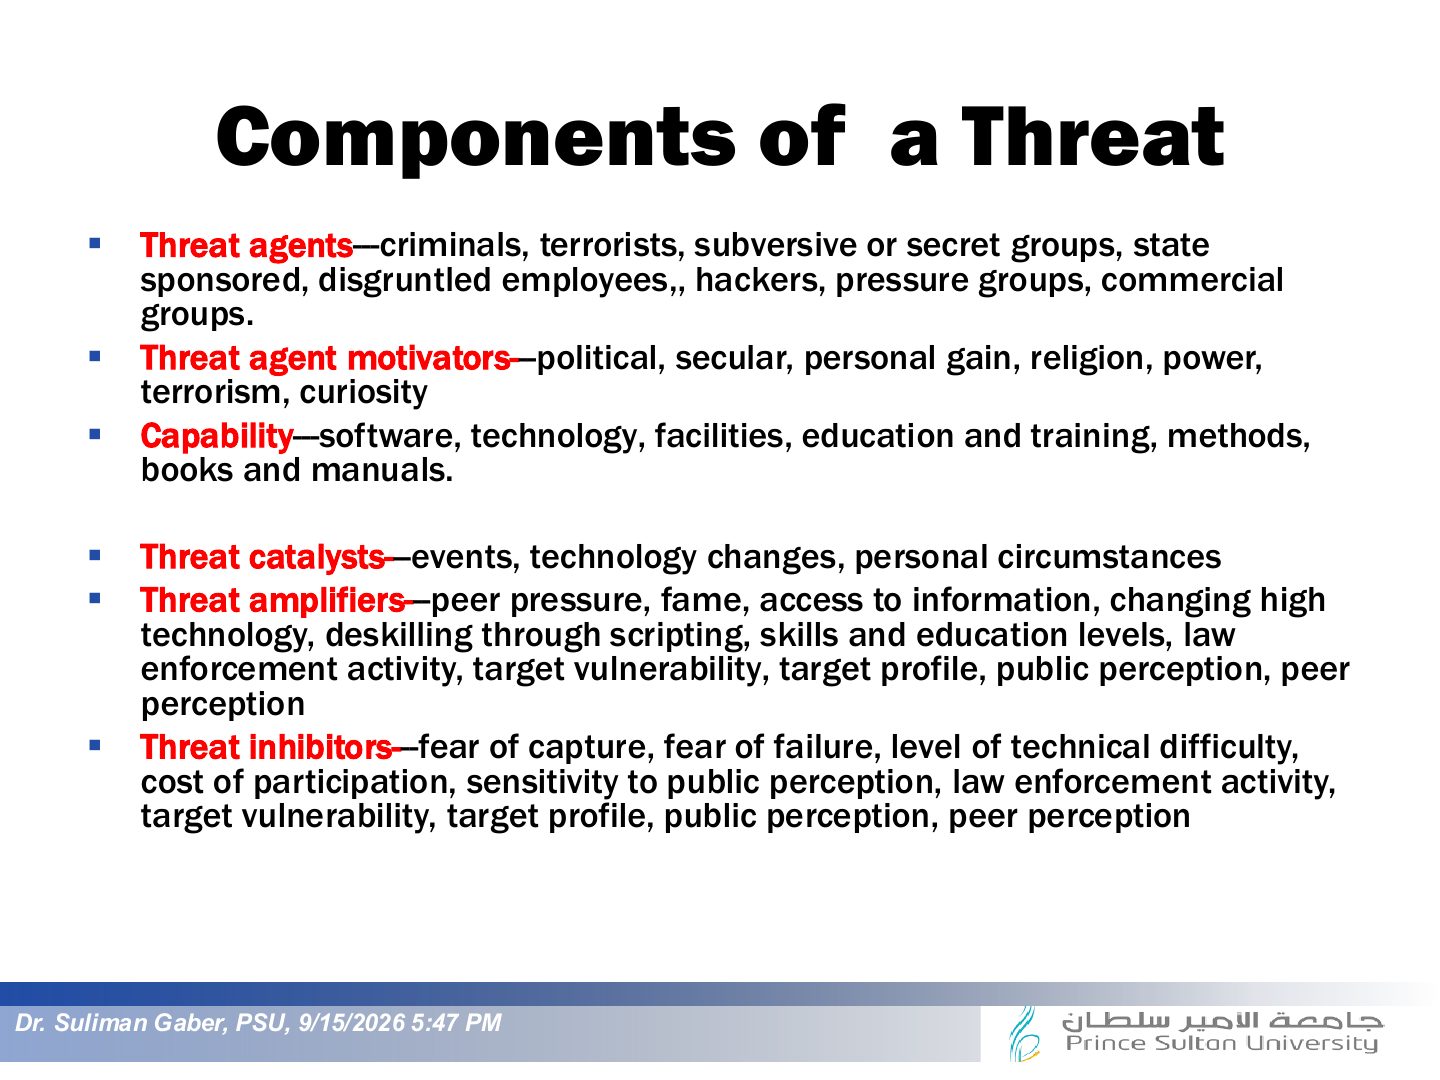
- 11 Components of a Threat
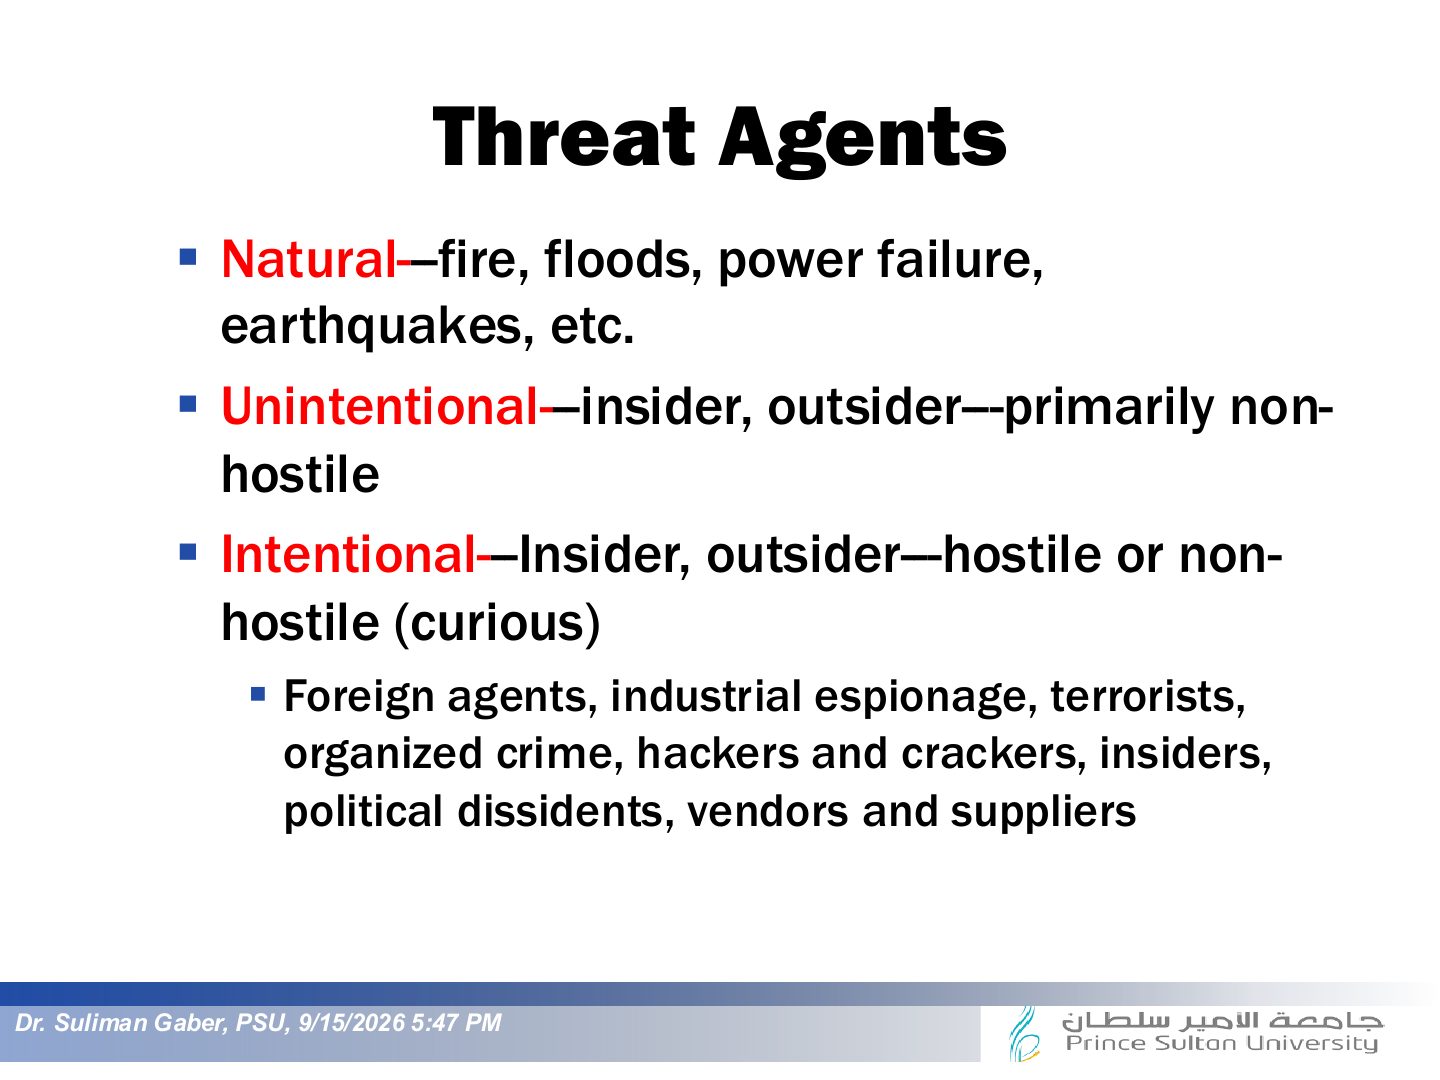
- 12 Threat Agents
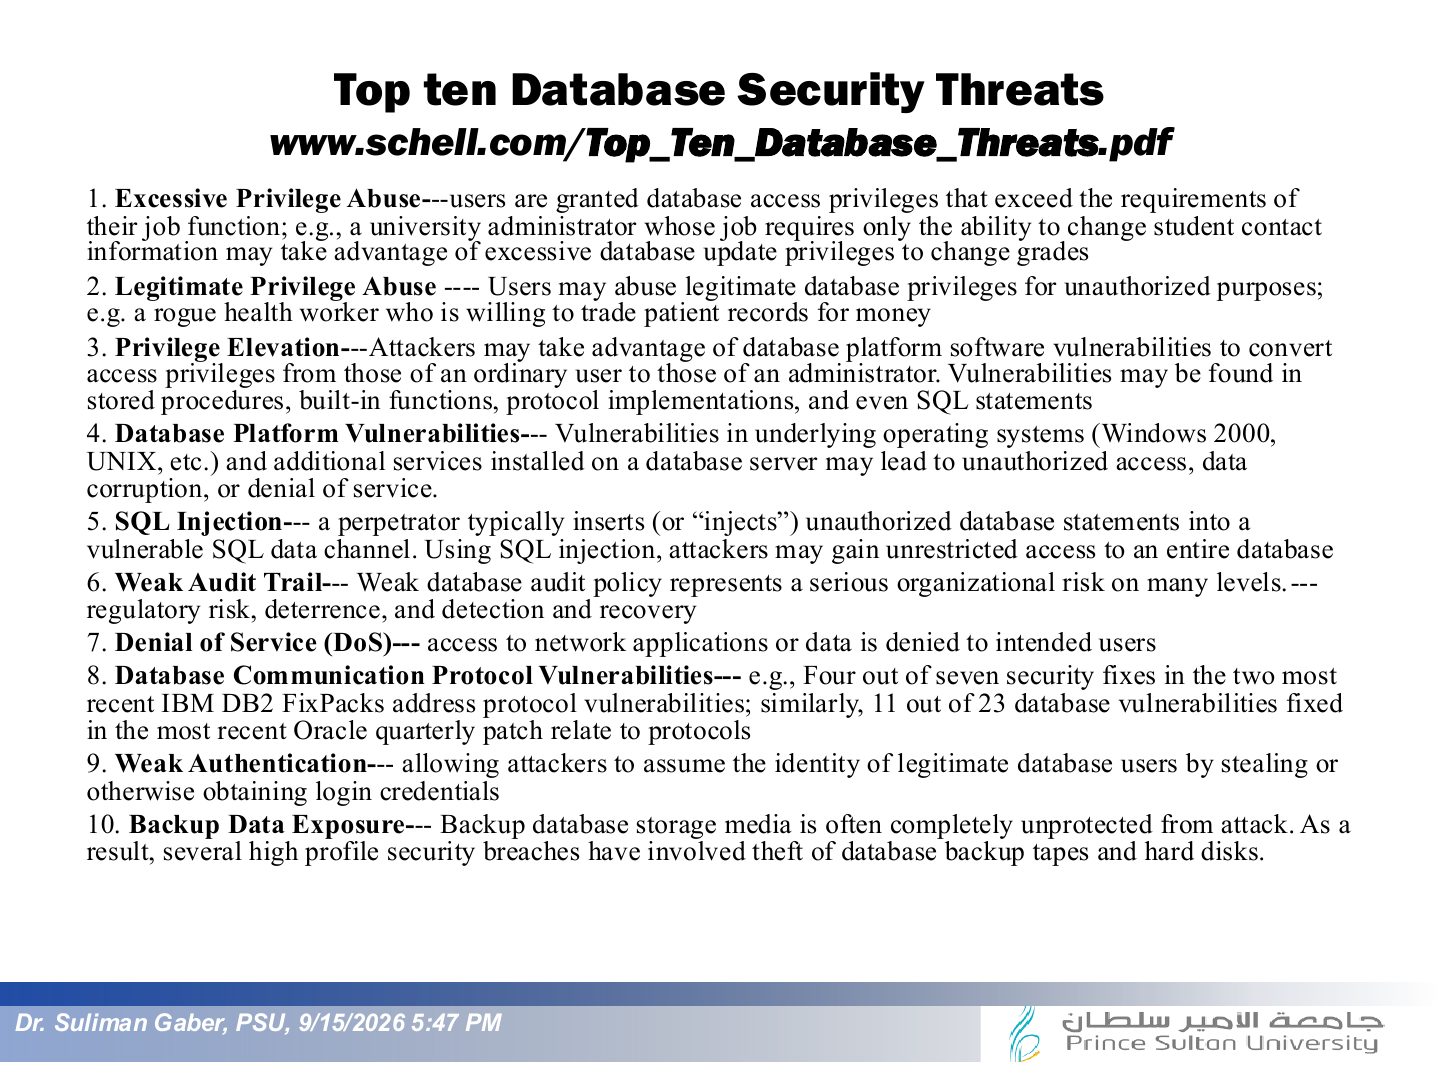
- 13 Top ten Database Security Threats
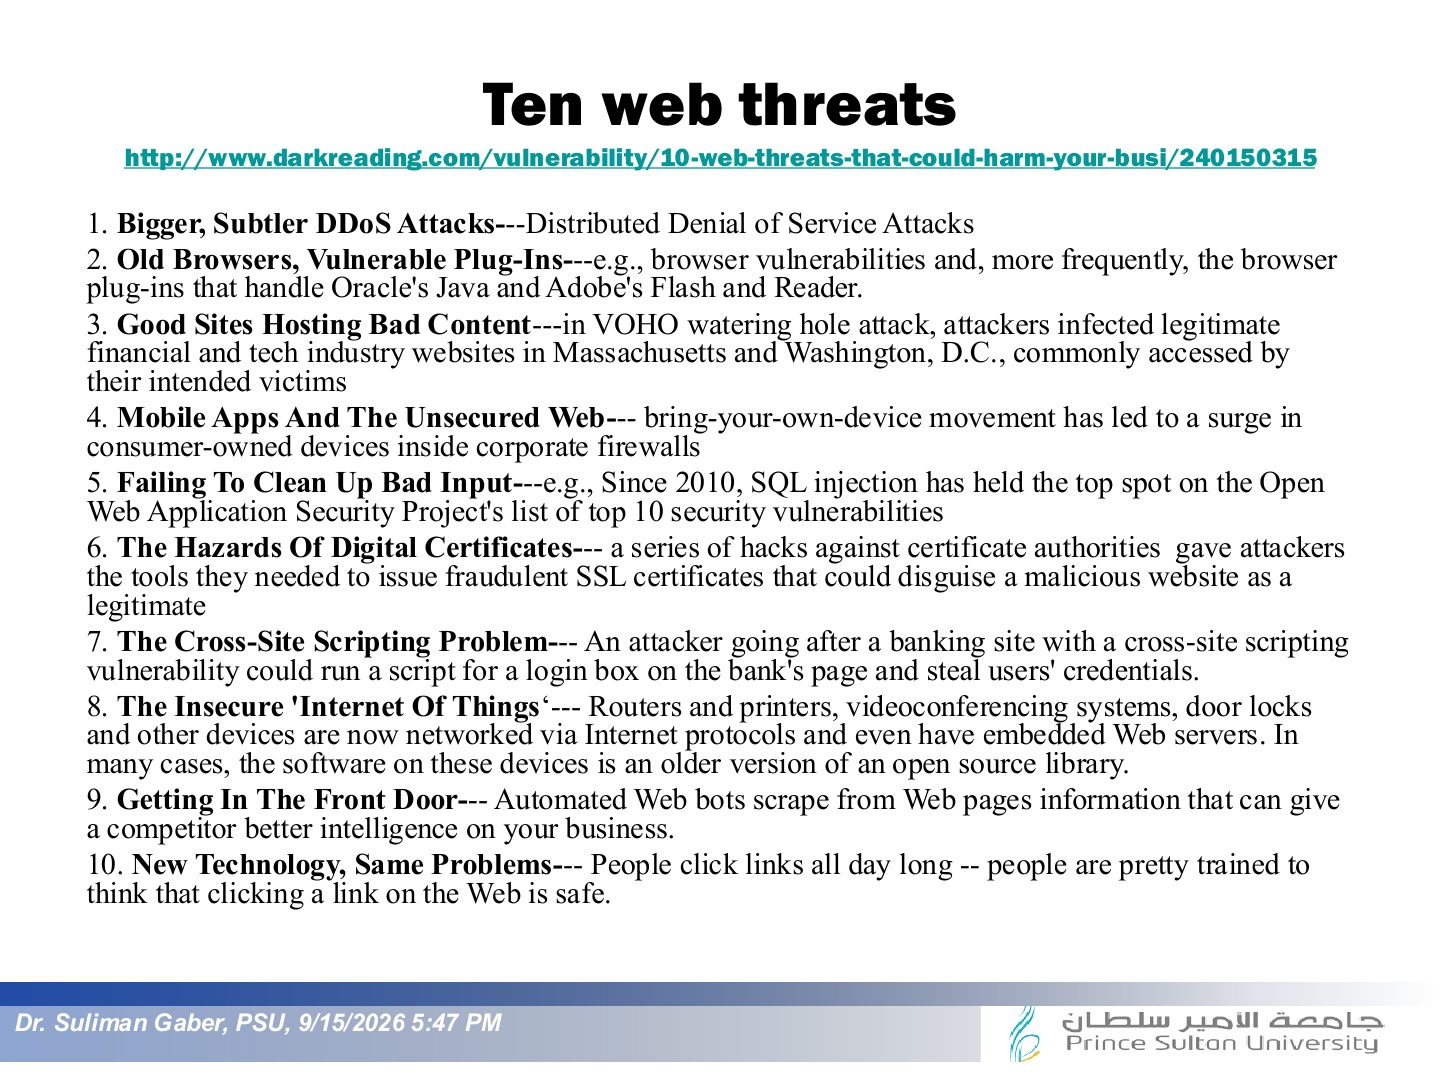
- 14 Ten web threats
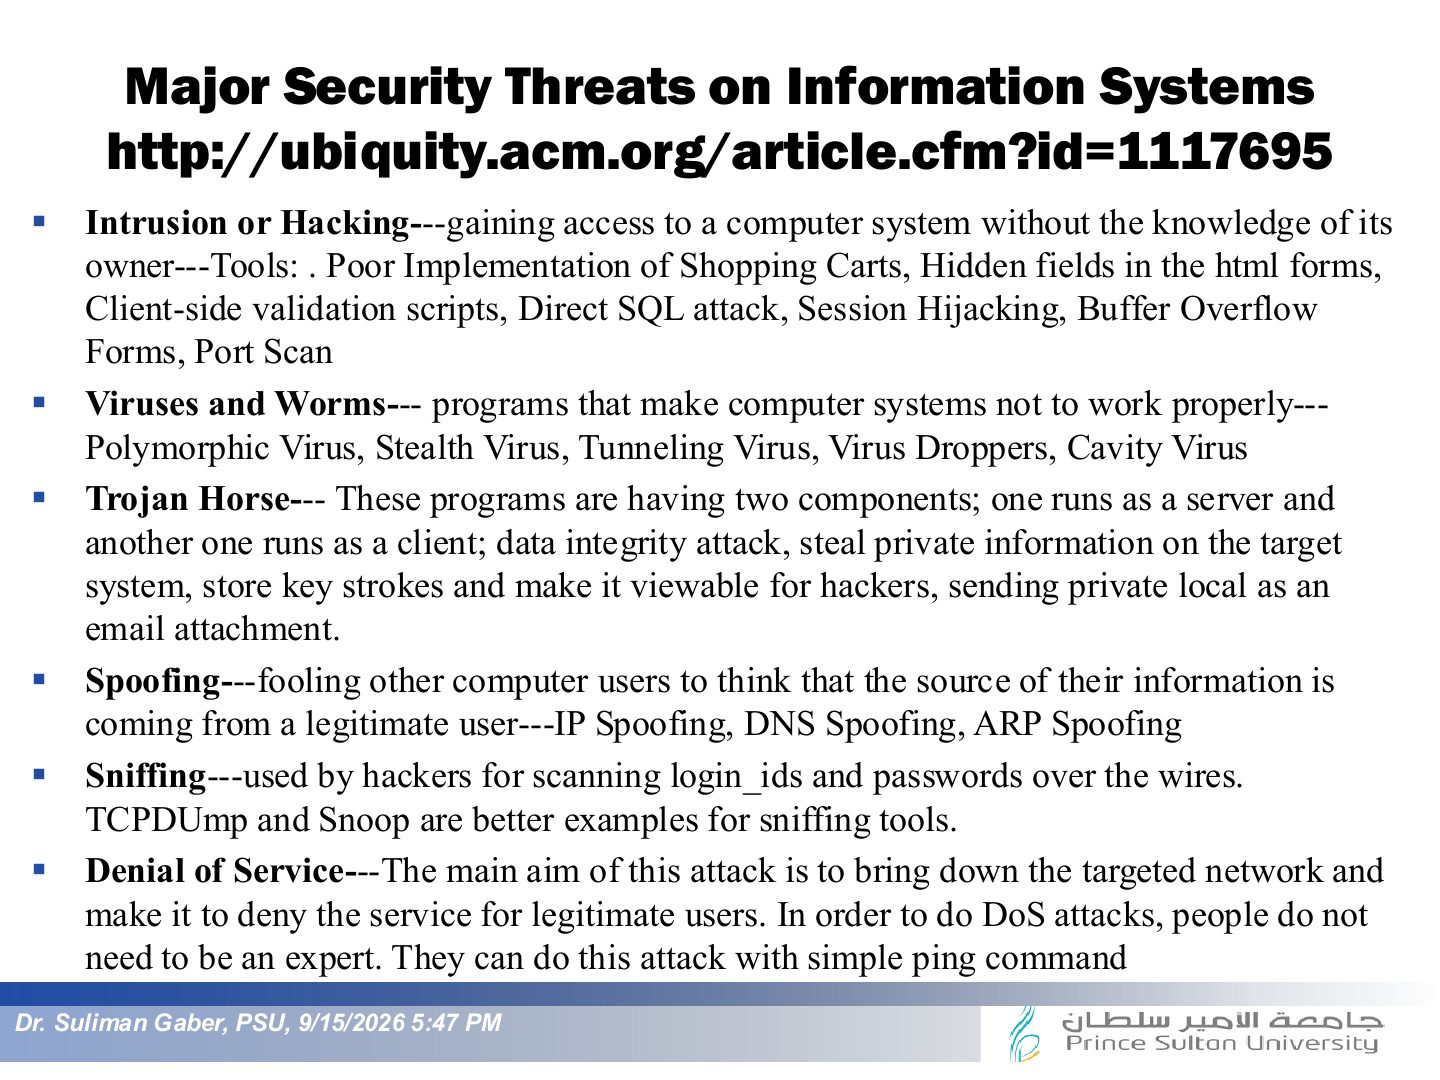
- 15 Major Security Threats on Information Systems http://ubiquity.acm.org/article.cfm?id=1117695
- 16 Vulnerabilities
- 17 How do the vulnerabilities manifest?
- 18 Examples of Information Security Vulnerabilities
- 19 Examples of Information Security Vulnerabilities (Cont.)
- 20 Common Vulnerabilities and Exposures (CVE) List
- 21 Common Vulnerabilities and Exposures (CVE) List
- 22 Example on CVE
- 23 Threat Modeling
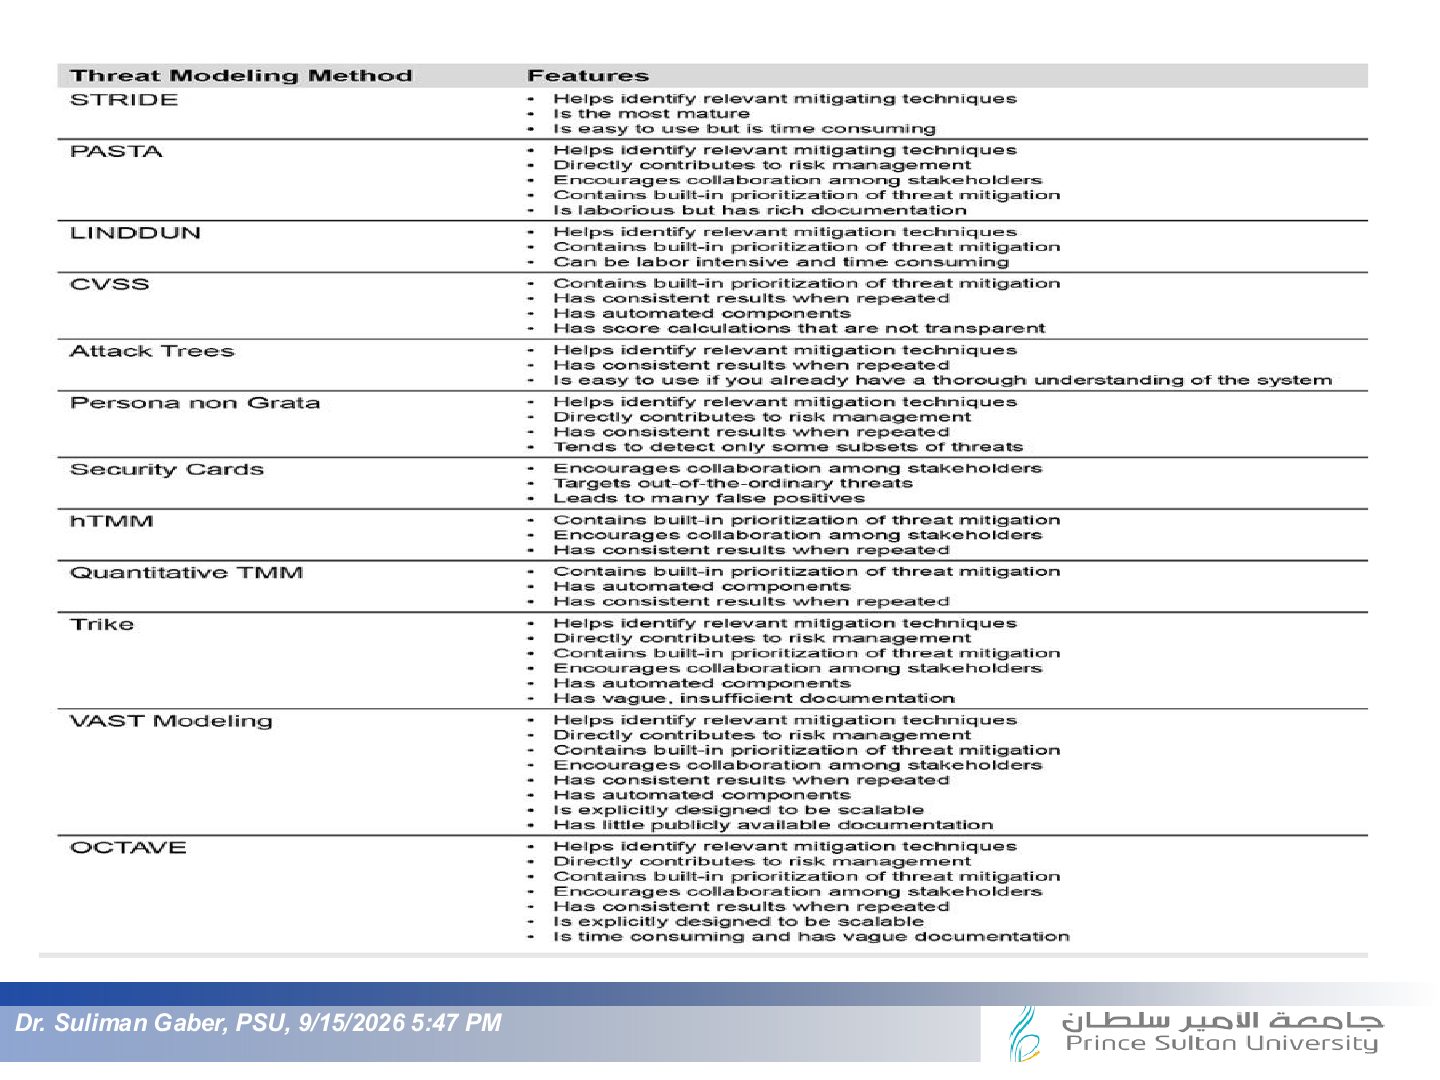
- 24 12 threat models
- 25 STRIDE and Associated Derivations
- 26 STRIDE and Associated Derivations
- 27 STRIDE and Associated Derivations
- 28 PASTA
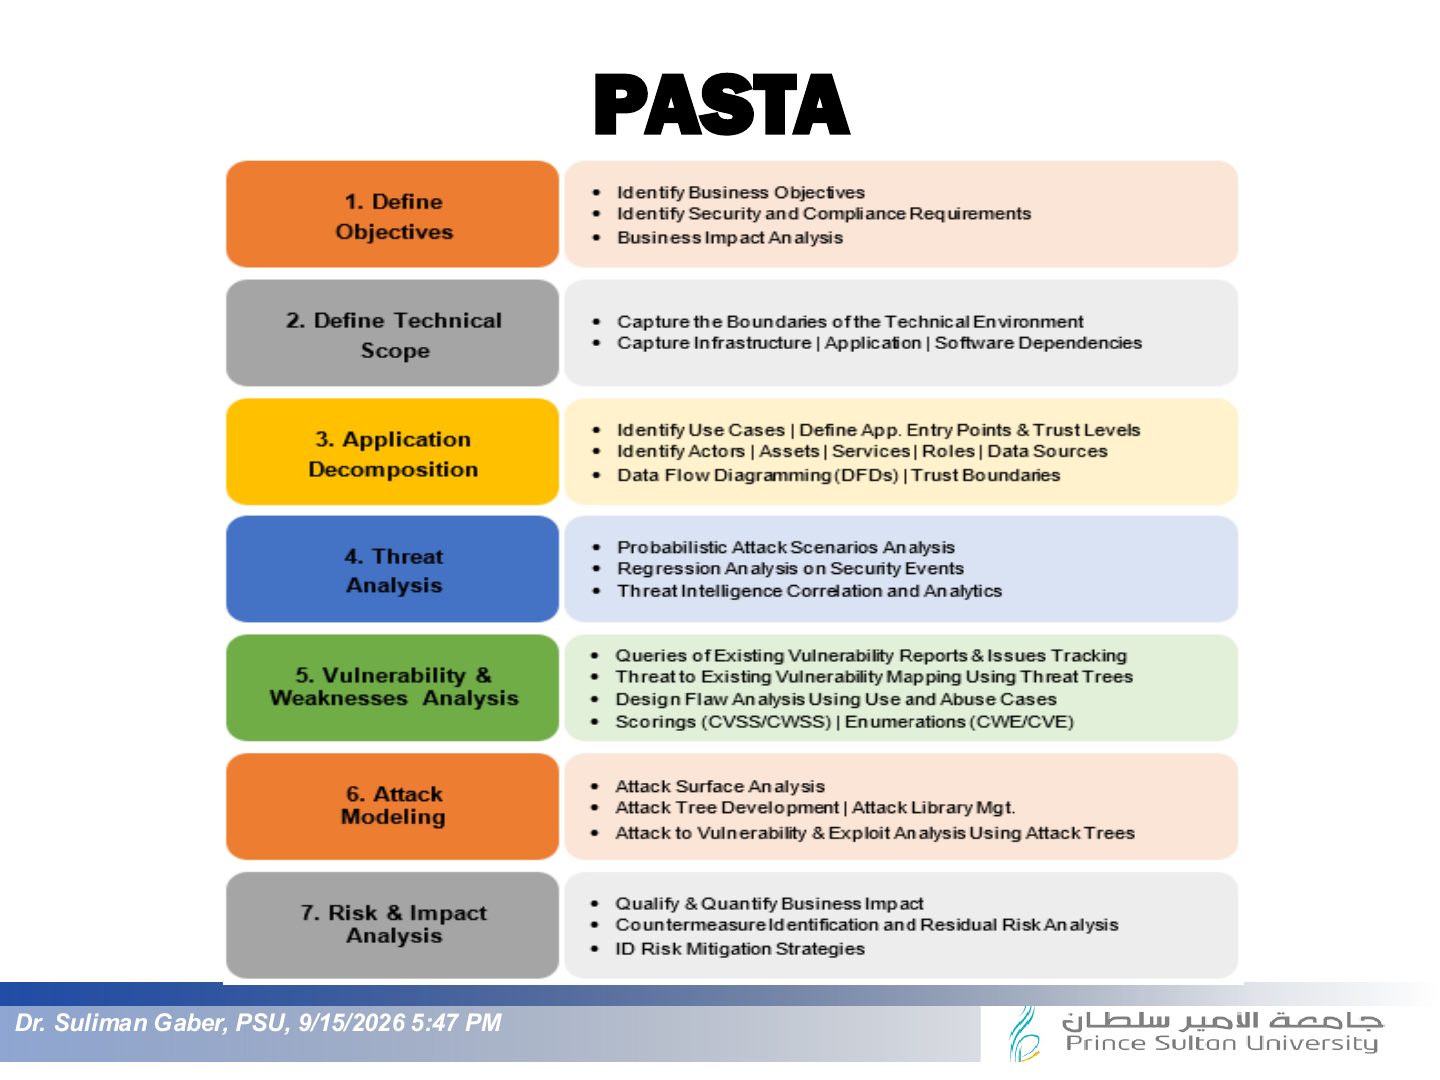
- 29 PASTA
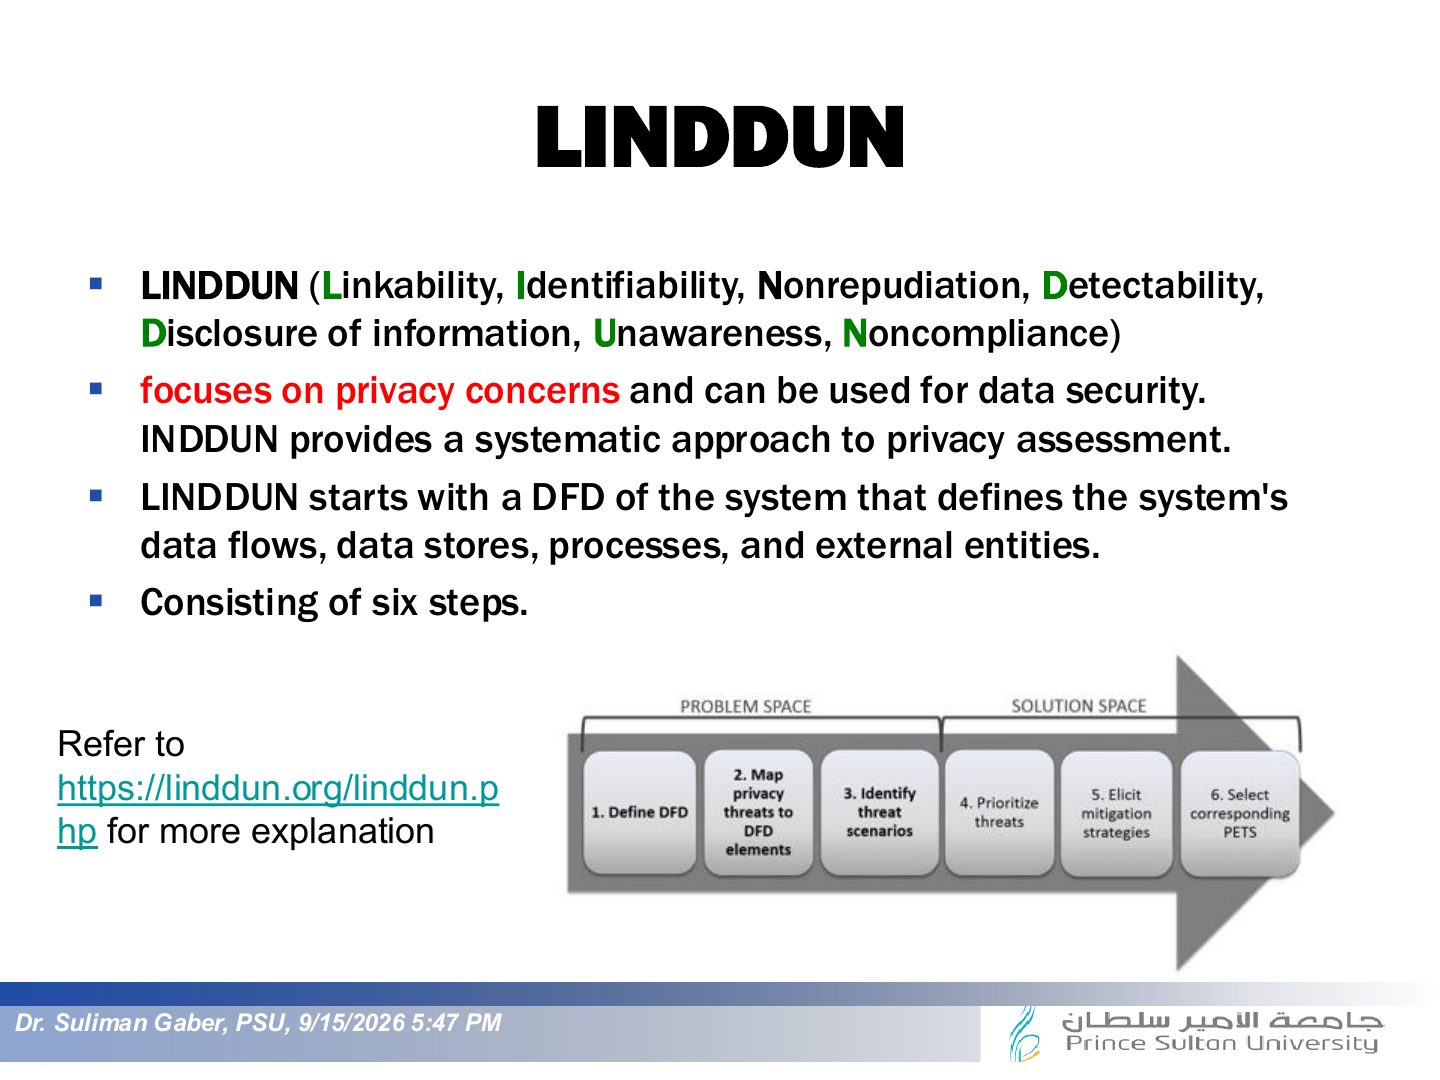
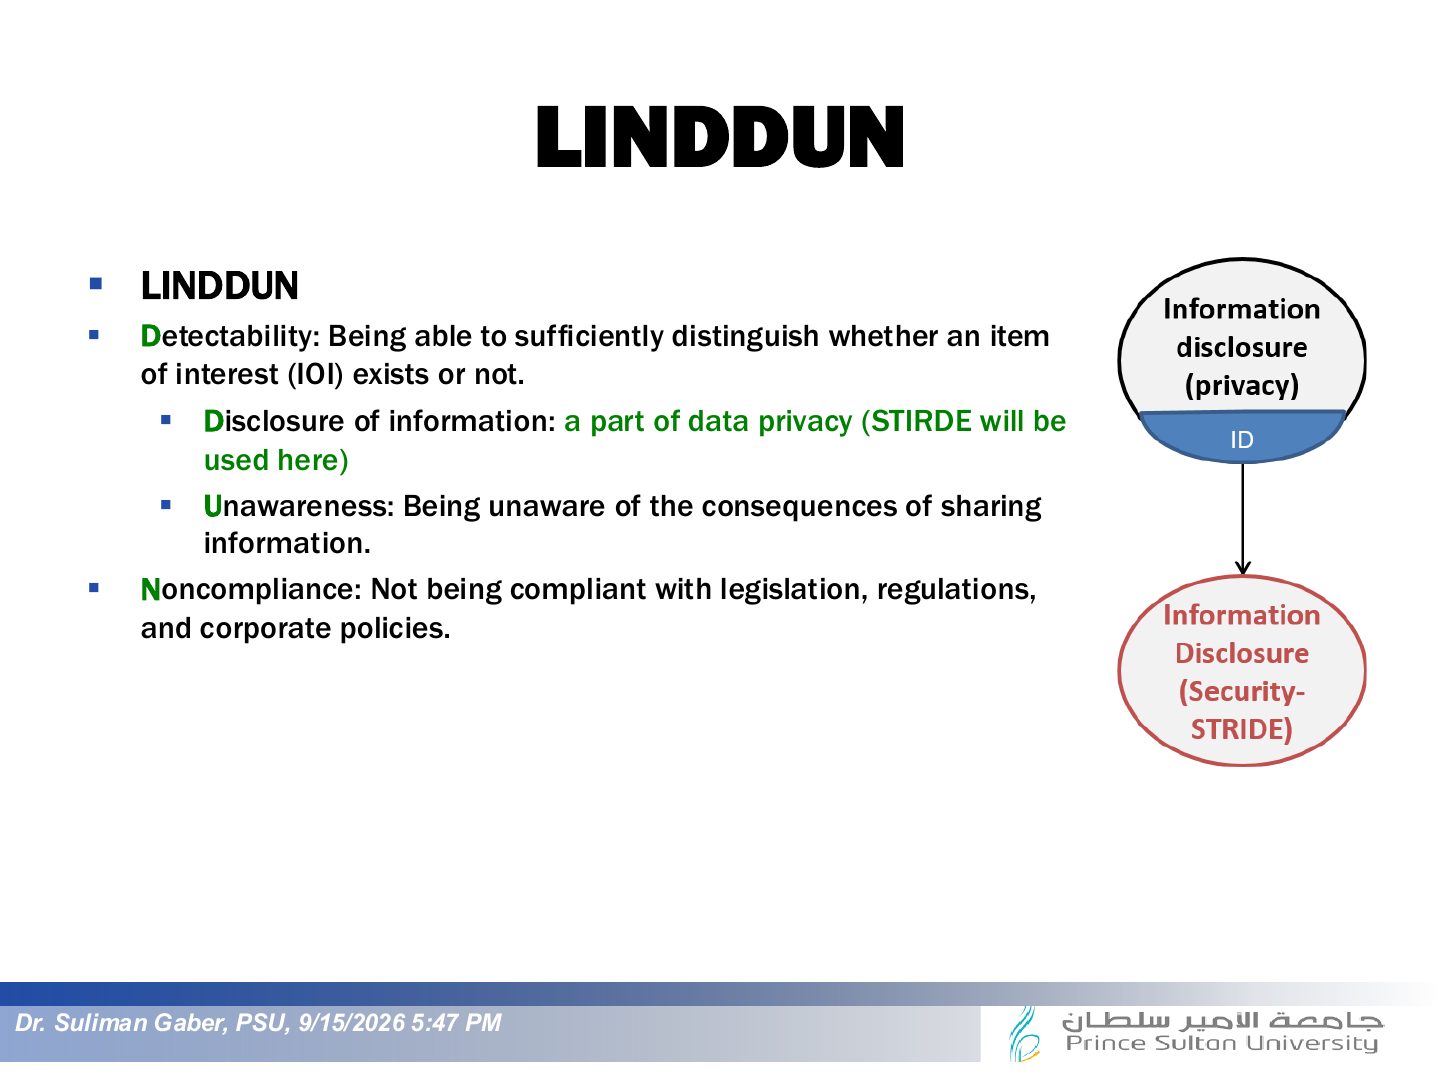
- 30 LINDDUN
- 31 LINDDUN
- 32 LINDDUN
- 33 Common Vulnerability Scoring System (CVSS)
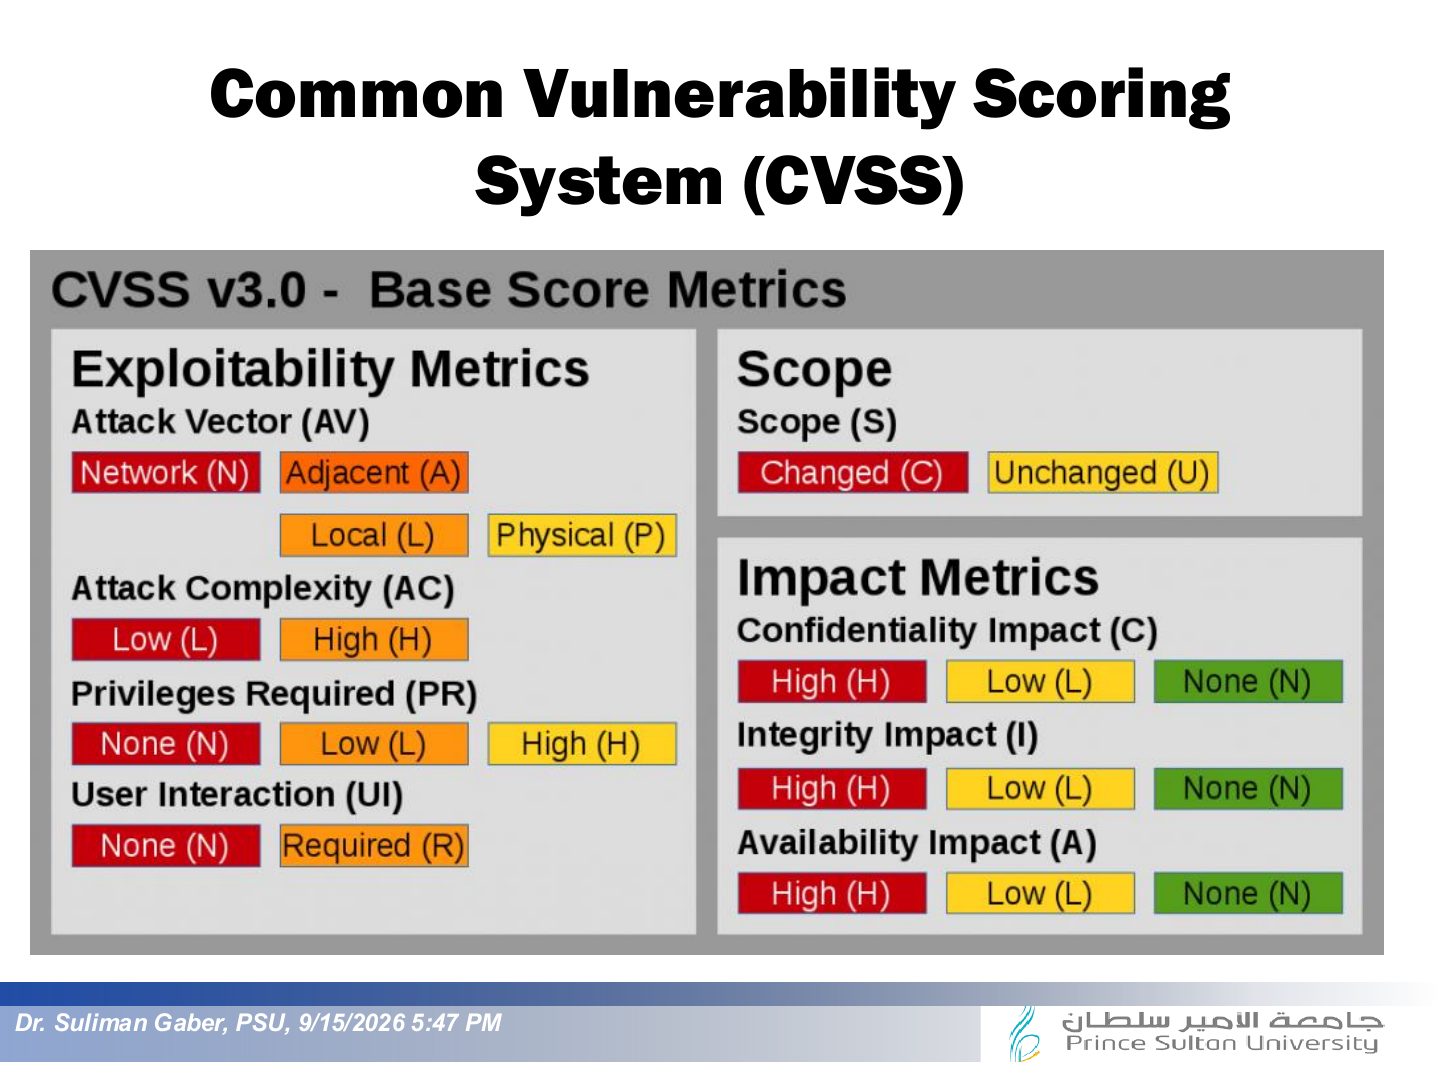
- 34 Common Vulnerability Scoring System (CVSS)
- 35 Threats Analysis (Attack Tree)
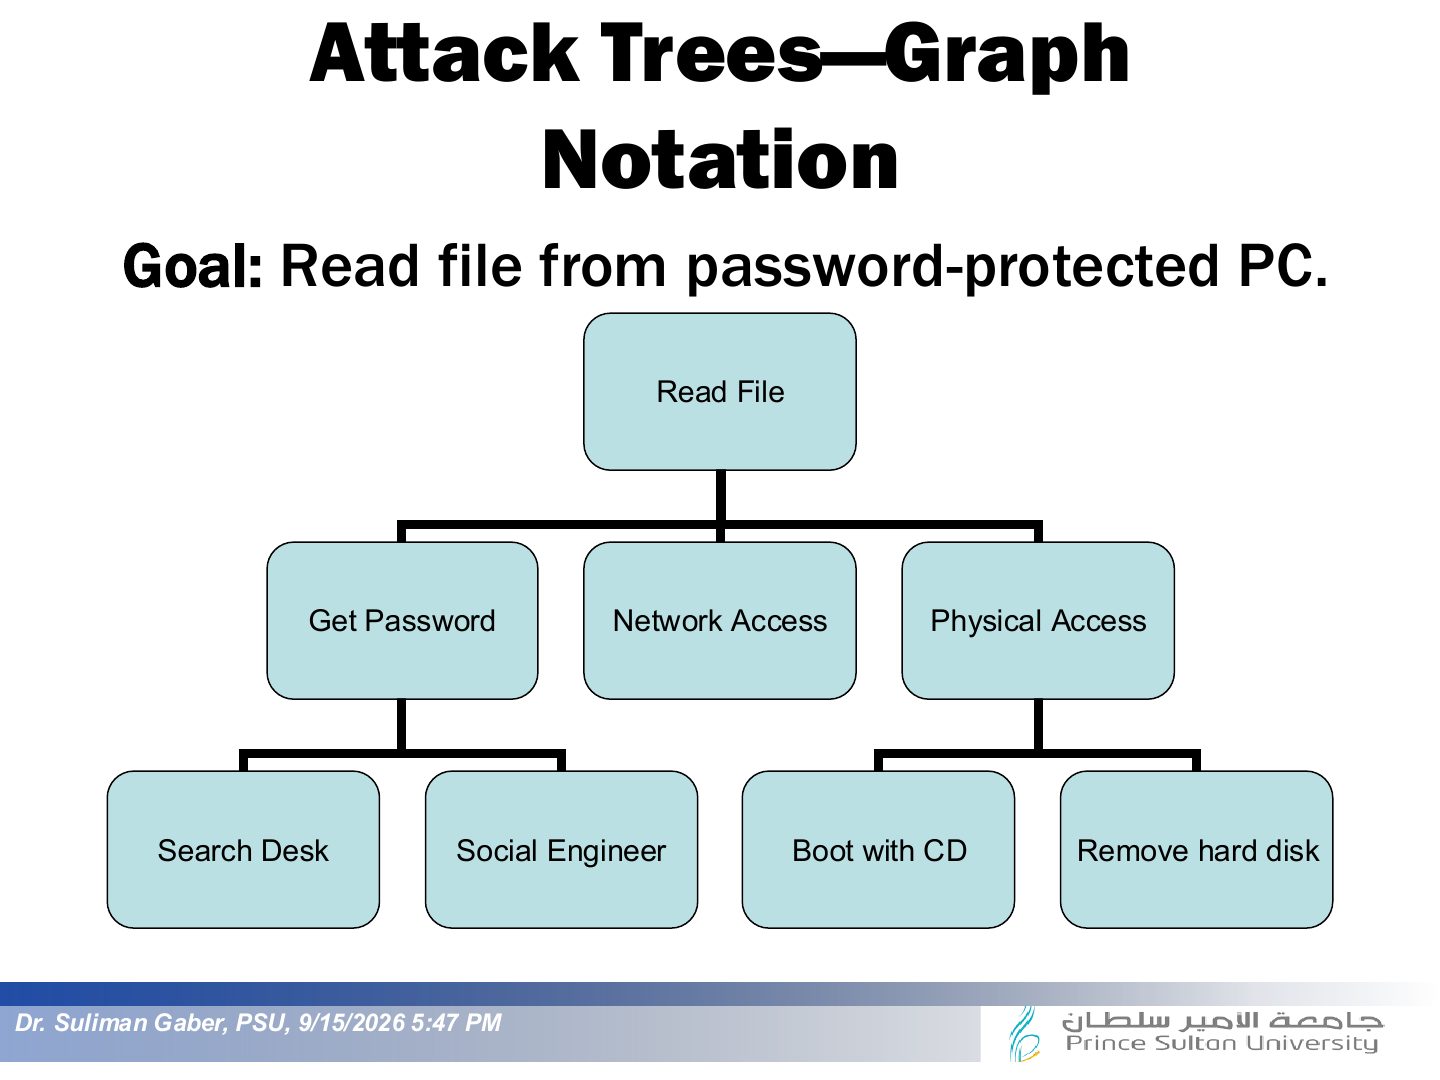
- 36 Attack Trees — Graph Notation
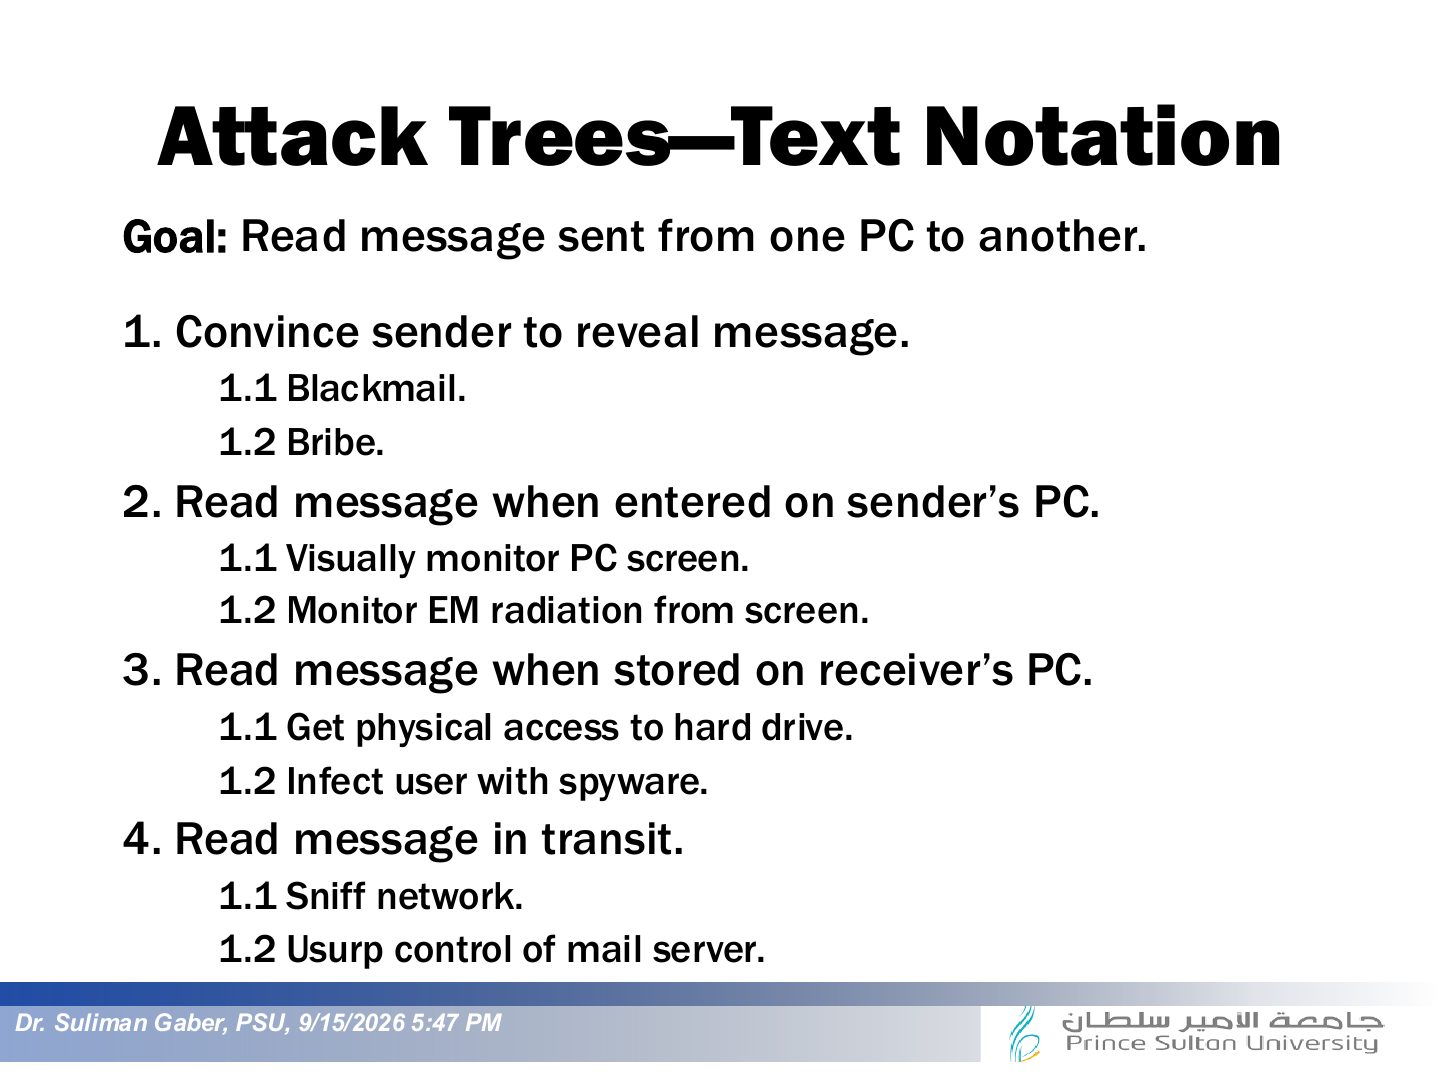
- 37 Attack Trees — Text Notation
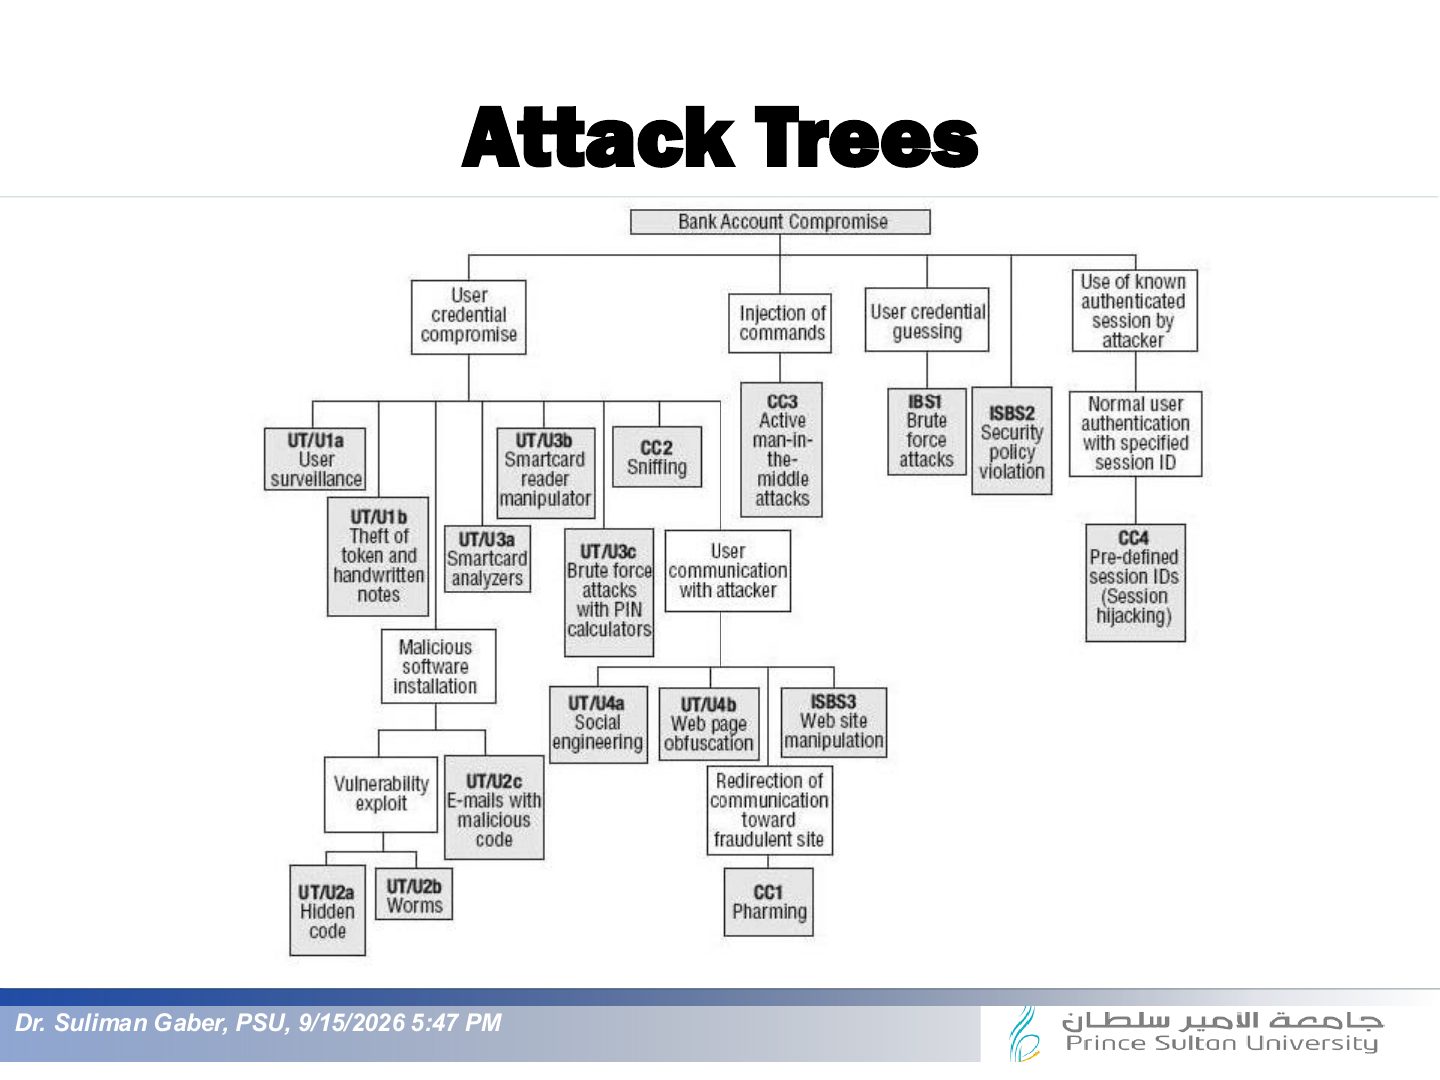
- 38 Attack Trees
- 39 Persona non Grata
- 40 Security Cards
- 41 Slide 41
- 42 hTMM
- 43 Quantitative Threat Modeling Method
- 44 Slide 44
- 45 Trike
- 46 Visual, Agile, and Simple Threat modeling (VAST)
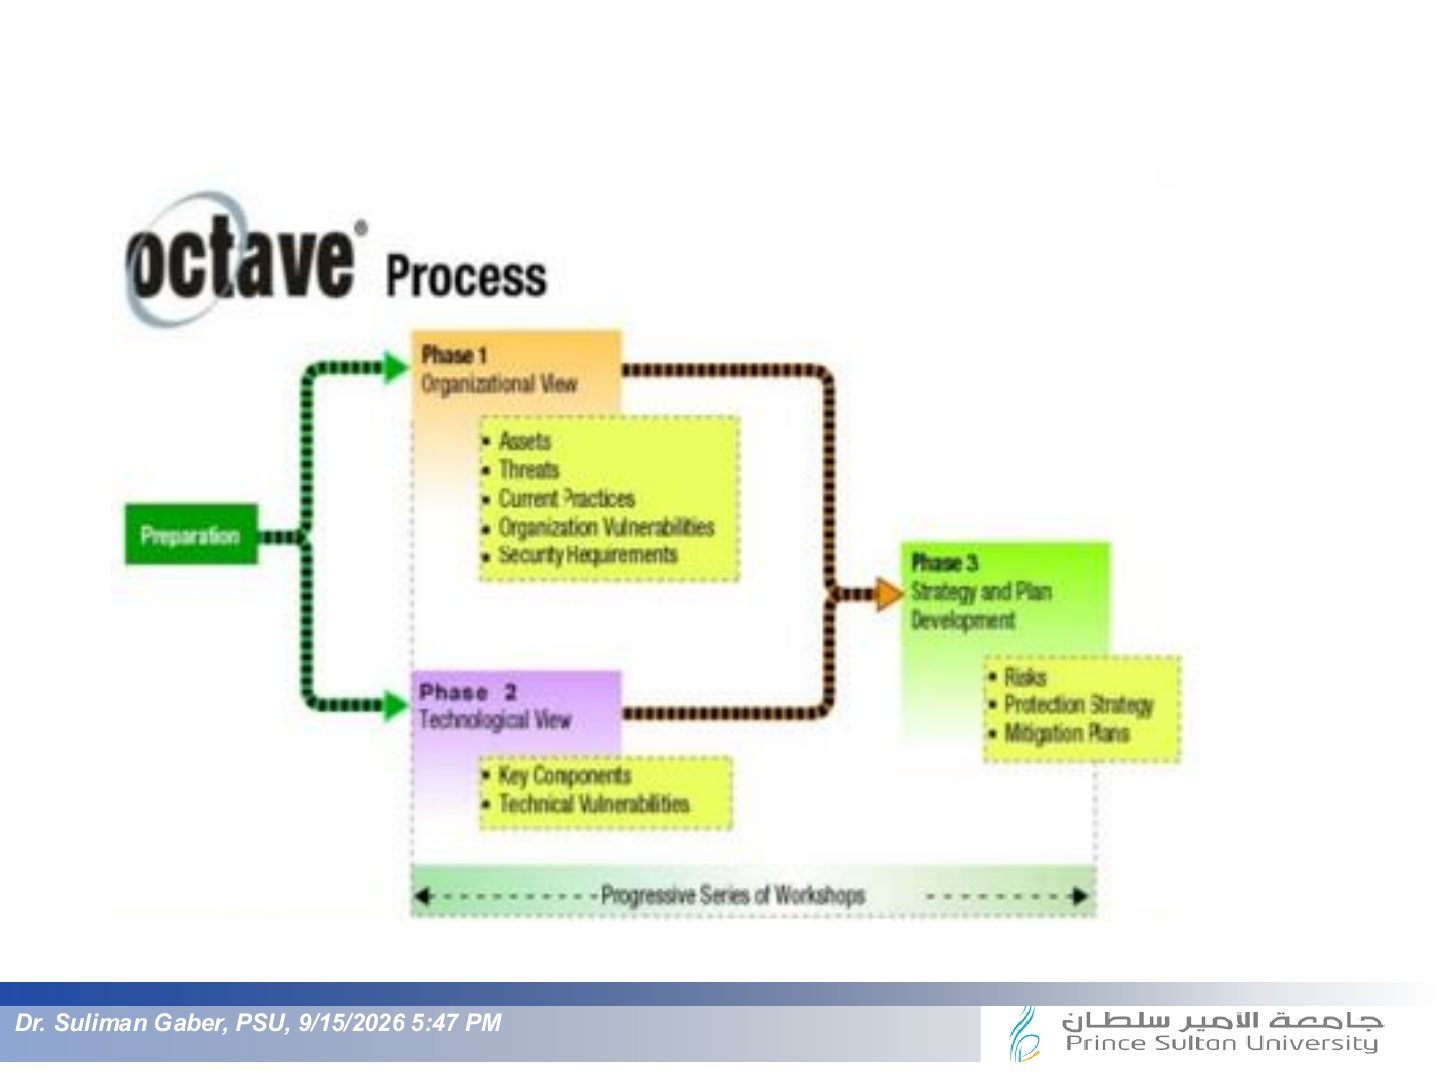
- 47 OCTAVE
- 48 Slide 48
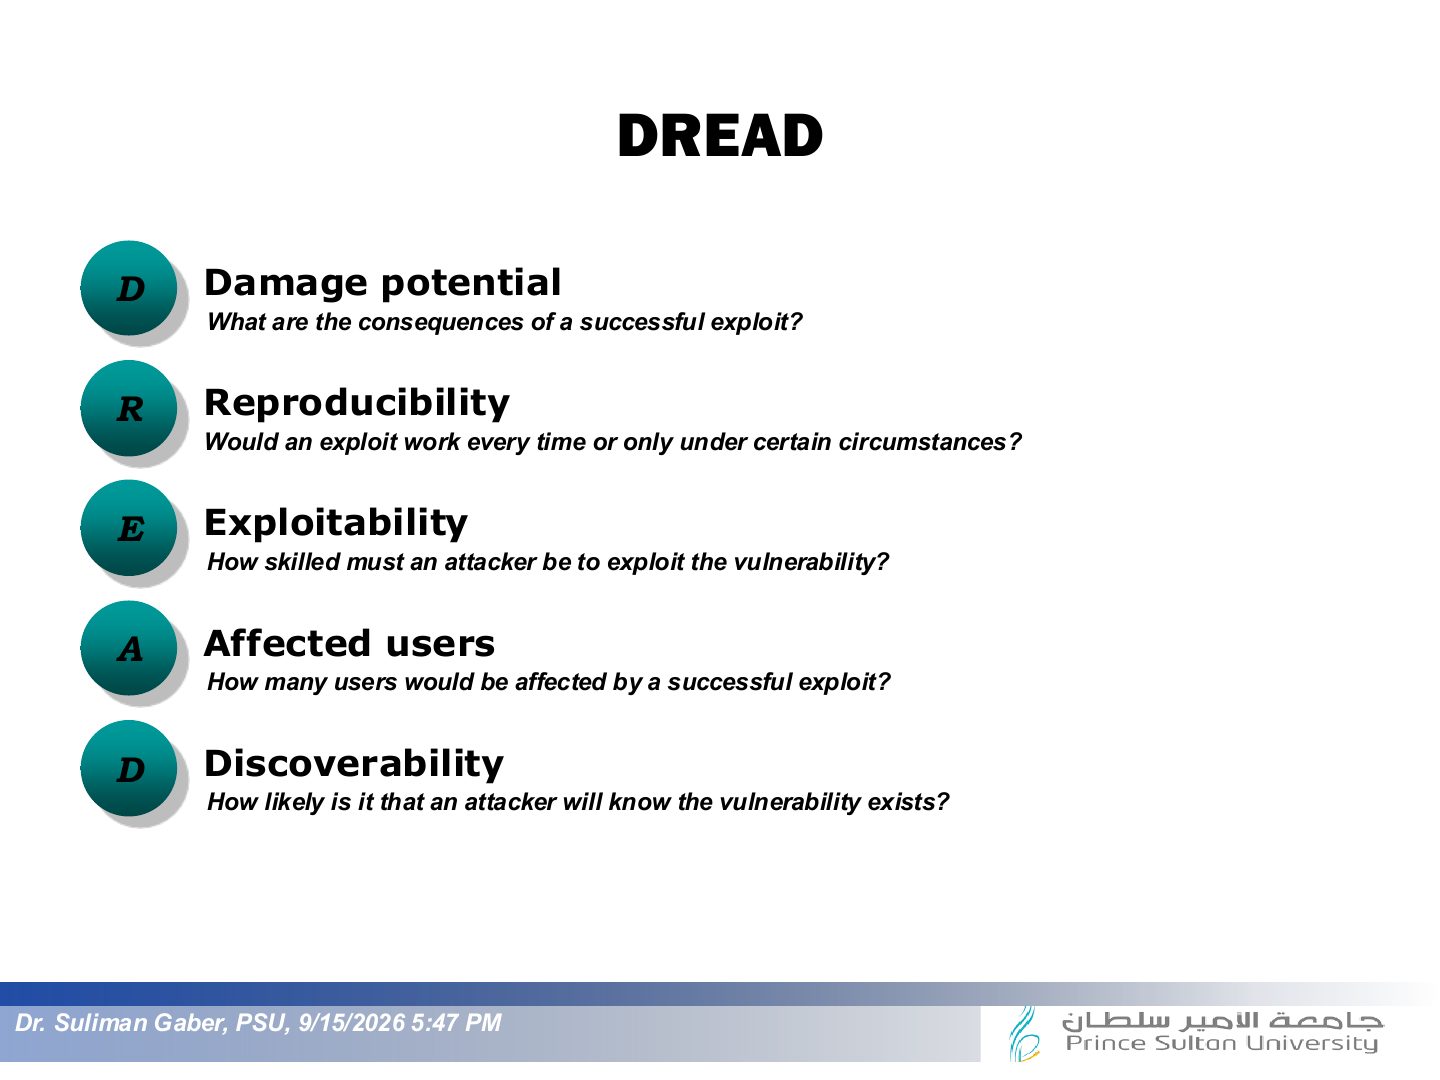
- 49 DREAD
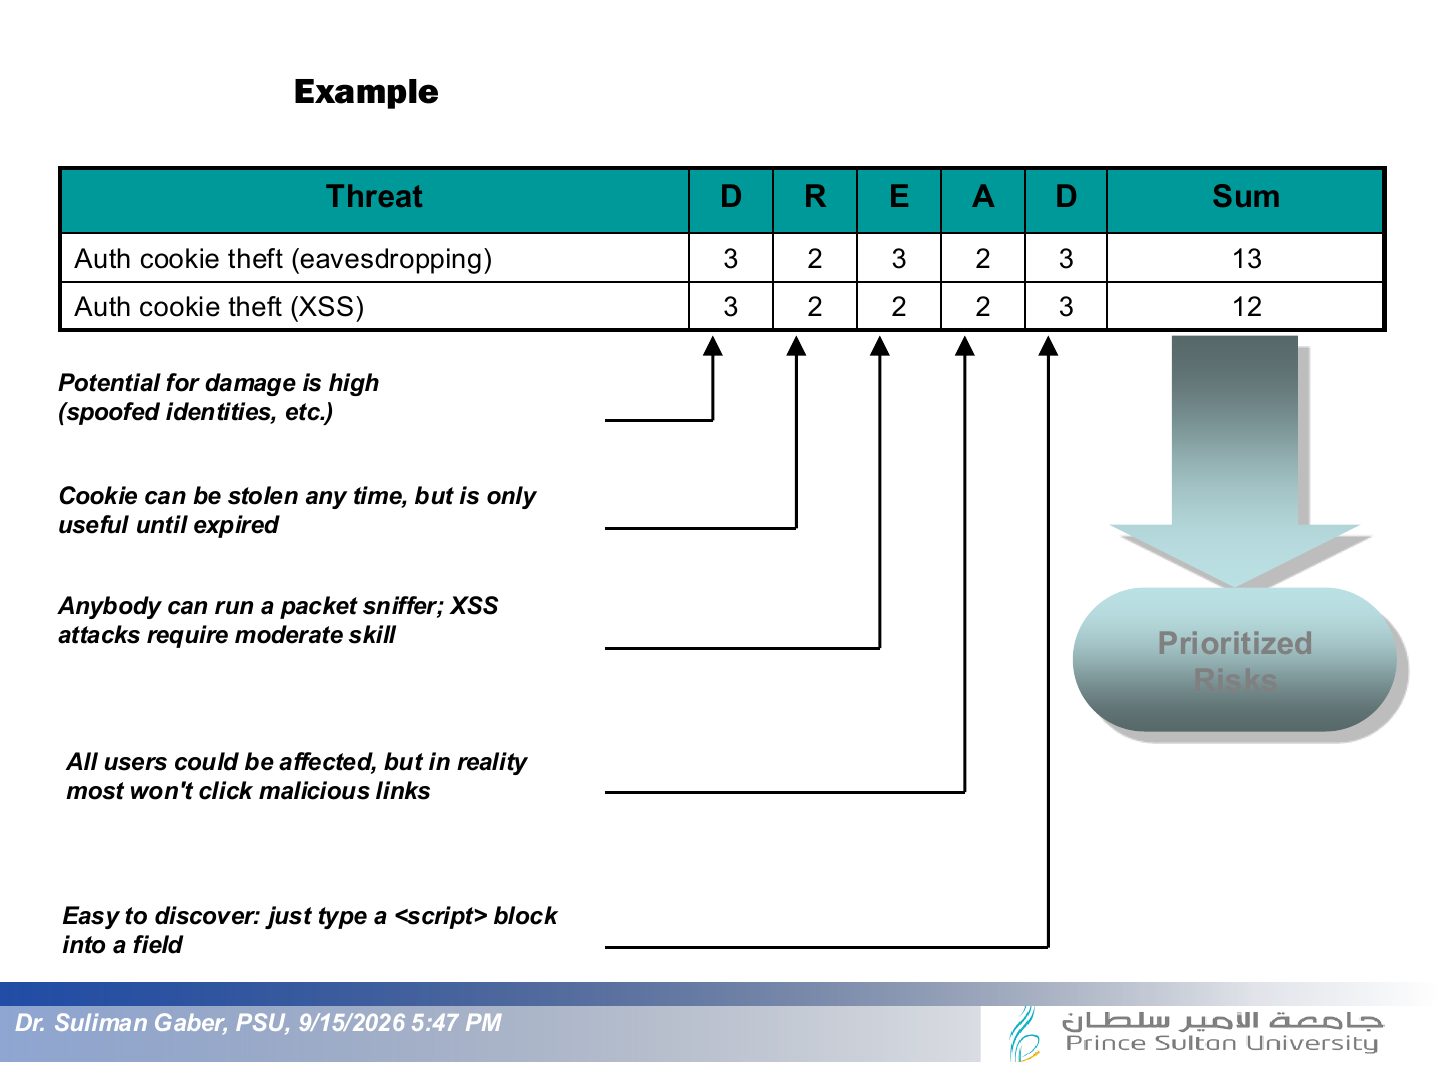
- 50 Example
- 51 Slide 51
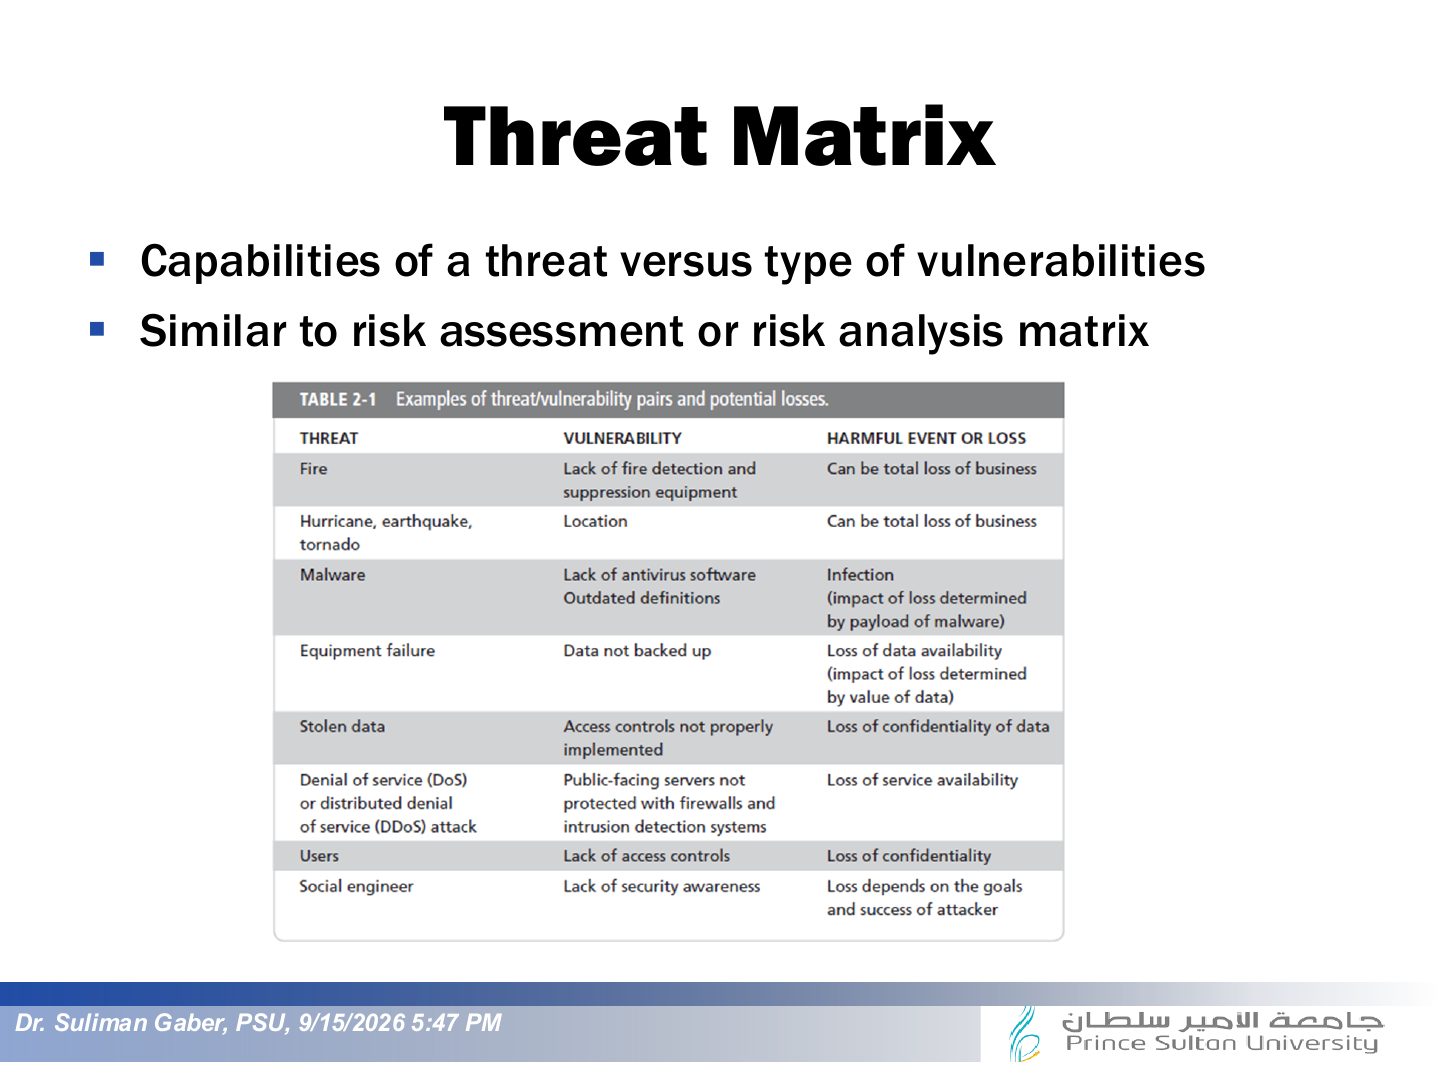
- 52 Threat/Vulnerability Pairs
- 53 Threat Matrix
Slide 1
Intended Learning Outcomes
Common Types of Attack
Introduction
Introduction
Possible threat sources
Notes
Threat sources: human (intentional or accidental), natural, environmental, technical.
Types of Threats
Exam angle
SQL injection is a(n) ____ threat.
Threats Against the Network
Threats Against the Host
Threats Against the Application
Components of a Threat
Threat Agents
Notes
Threat agent: the actor (hacker, insider, malware) that carries out the threat.
Top ten Database Security Threats
Ten web threats
Major Security Threats on Information Systems http://ubiquity.acm.org/article.cfm?id=1117695
Vulnerabilities
Notes
Vulnerabilities come from design flaws, misconfiguration, missing patches, weak processes and people.
How do the vulnerabilities manifest?
Examples of Information Security Vulnerabilities
Examples of Information Security Vulnerabilities (Cont.)
Common Vulnerabilities and Exposures (CVE) List
Notes
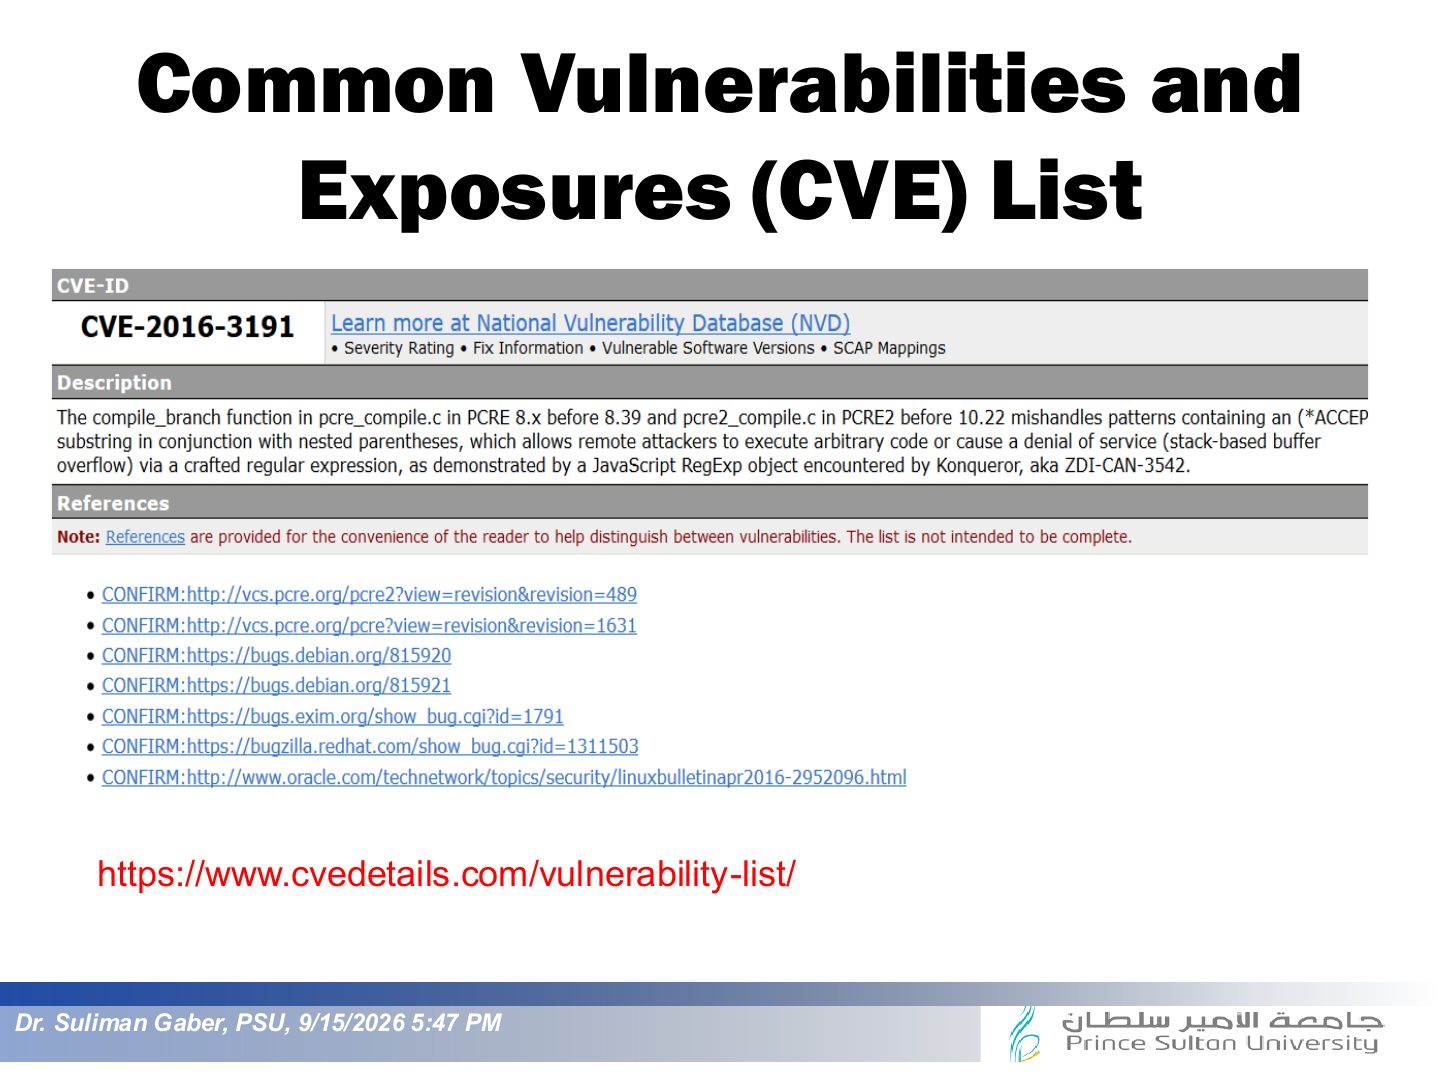
CVE: a public dictionary of known vulnerabilities, each with a CVE-ID (CVE-YEAR-NUMBER).
Exam angle
CVE provides:
- Scores come from CVSS.
Common Vulnerabilities and Exposures (CVE) List
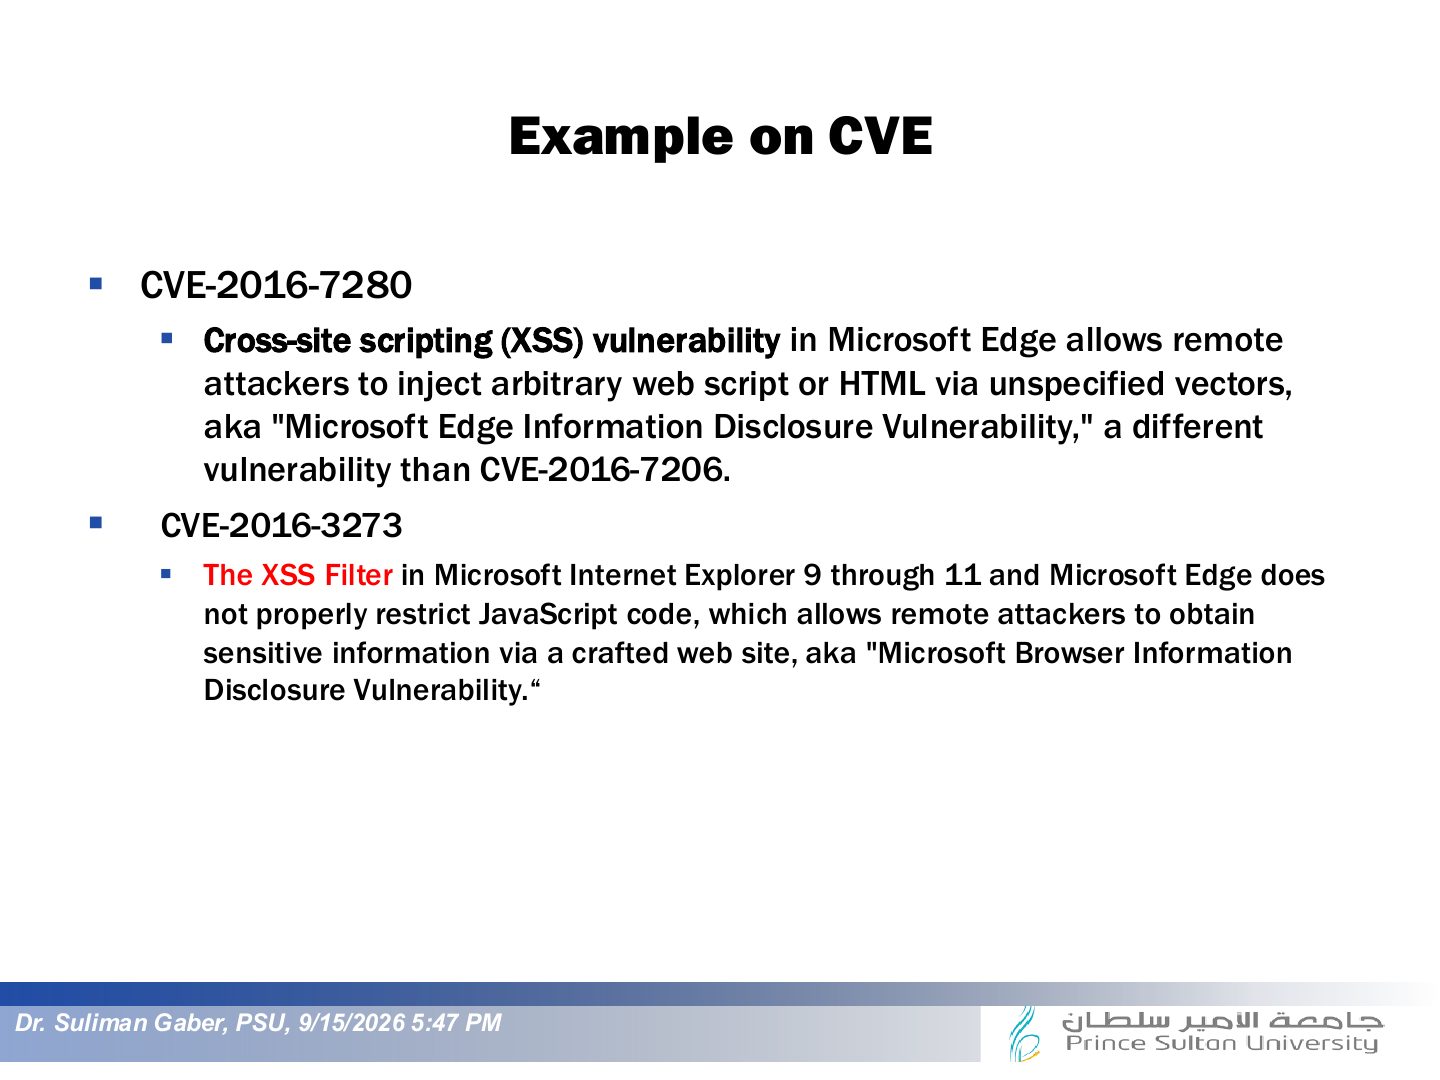
Example on CVE
Threat Modeling
Notes
Threat modeling: identify what can go wrong in a system and how to address it, early in design.
12 threat models
STRIDE and Associated Derivations
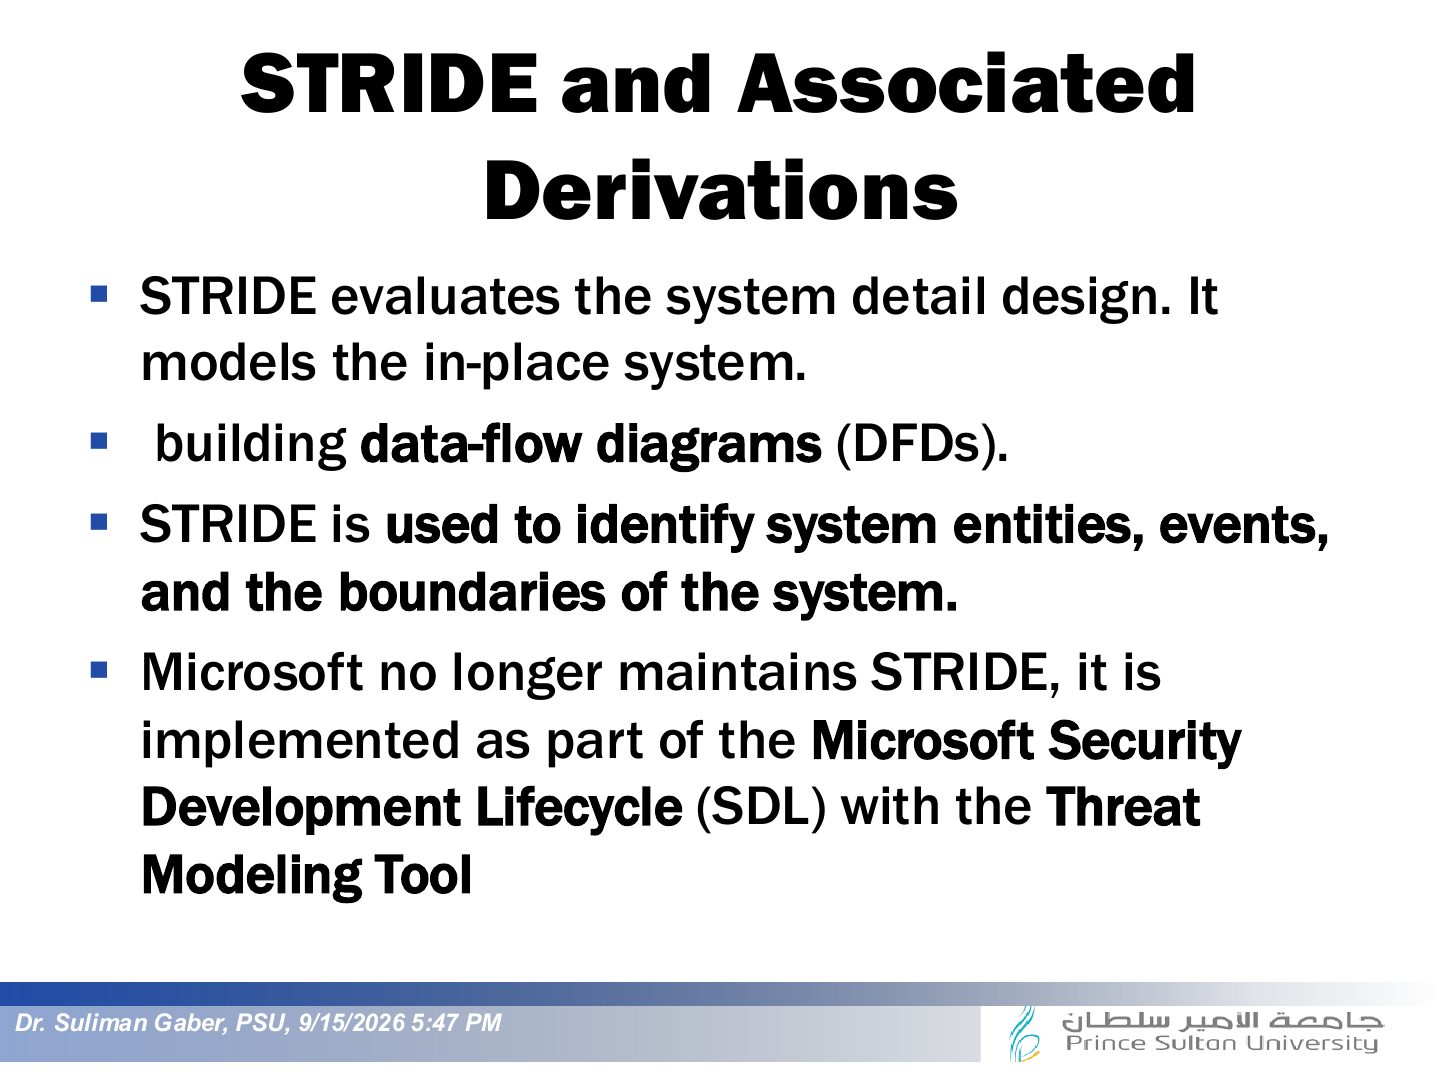
Notes
STRIDE: Spoofing, Tampering, Repudiation, Information disclosure, Denial of service, Elevation of privilege (each breaks one property).
Memory trick Spoofing↔authentication, Tampering↔integrity, Repudiation↔non-repudiation, Info disclosure↔confidentiality, DoS↔availability, EoP↔authorization.
Exam angle
threat modeling an Azure App Service app
In STRIDE, "Tampering" violates:
Microsoft’s threat-modeling method for an app is:
STRIDE and Associated Derivations
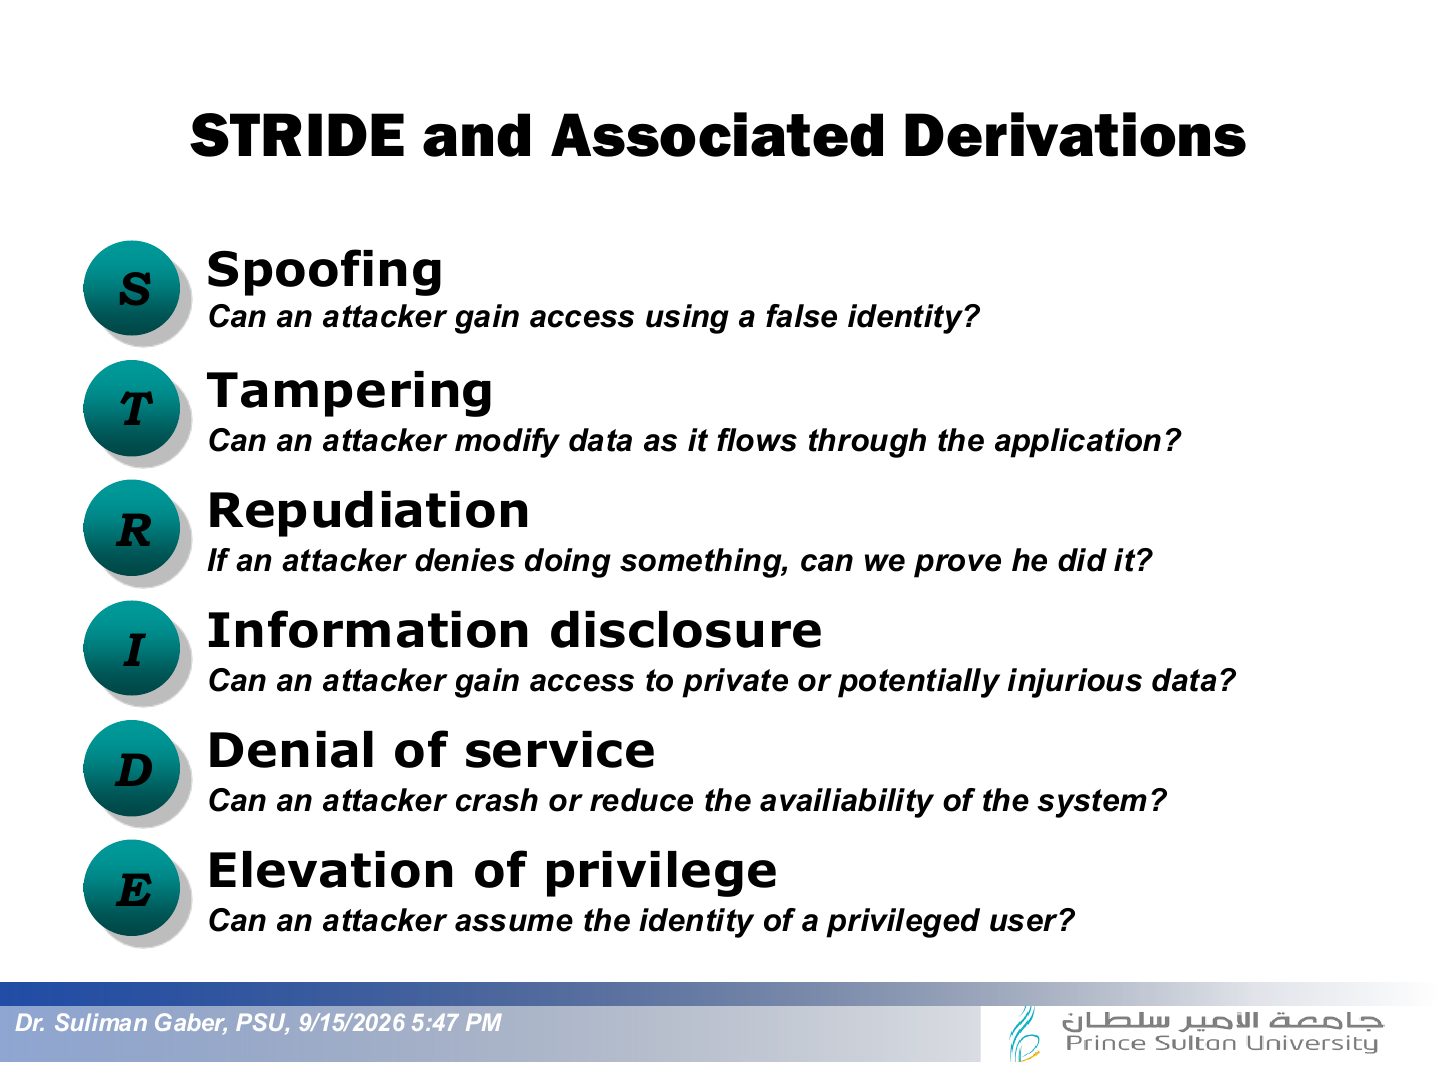
STRIDE and Associated Derivations
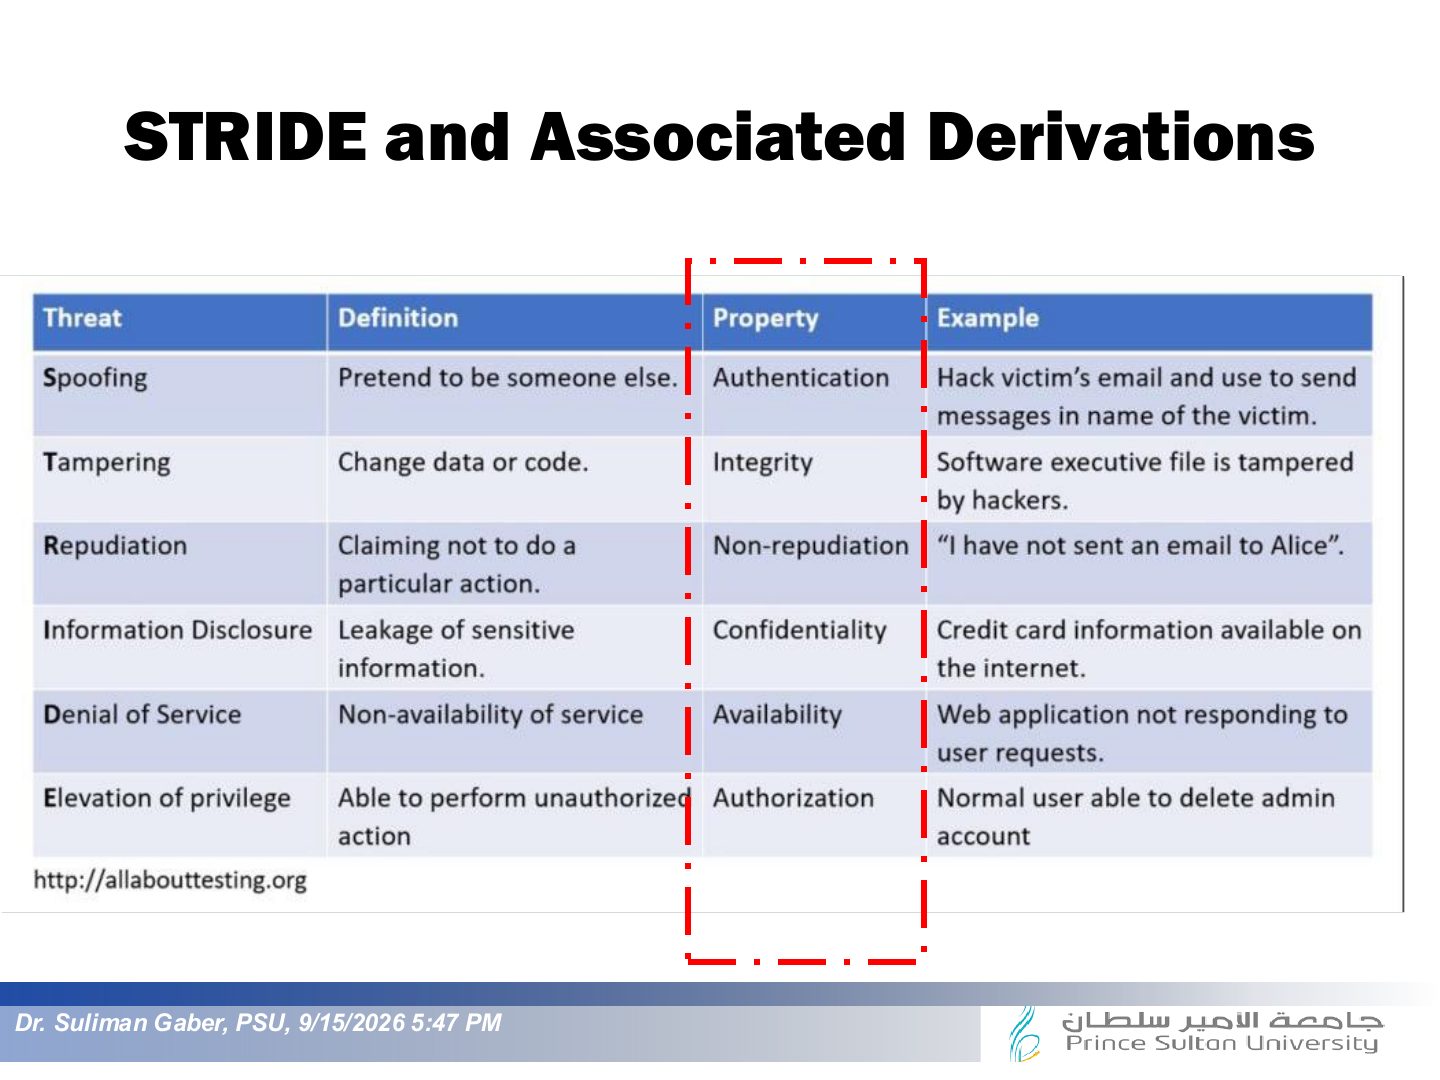
PASTA
PASTA
LINDDUN
Notes
LINDDUN: privacy threats (Linkability, Identifiability, Non-repudiation, Detectability, Disclosure, Unawareness, Non-compliance).
Exam angle
Which method focuses on PRIVACY threats?
LINDDUN
LINDDUN
Common Vulnerability Scoring System (CVSS)
Notes
CVSS: scores a vulnerability’s severity 0–10 (base, temporal, environmental metrics).
Common Vulnerability Scoring System (CVSS)
Threats Analysis (Attack Tree)
Attack Trees — Graph Notation
Attack Trees — Text Notation
Attack Trees
Persona non Grata
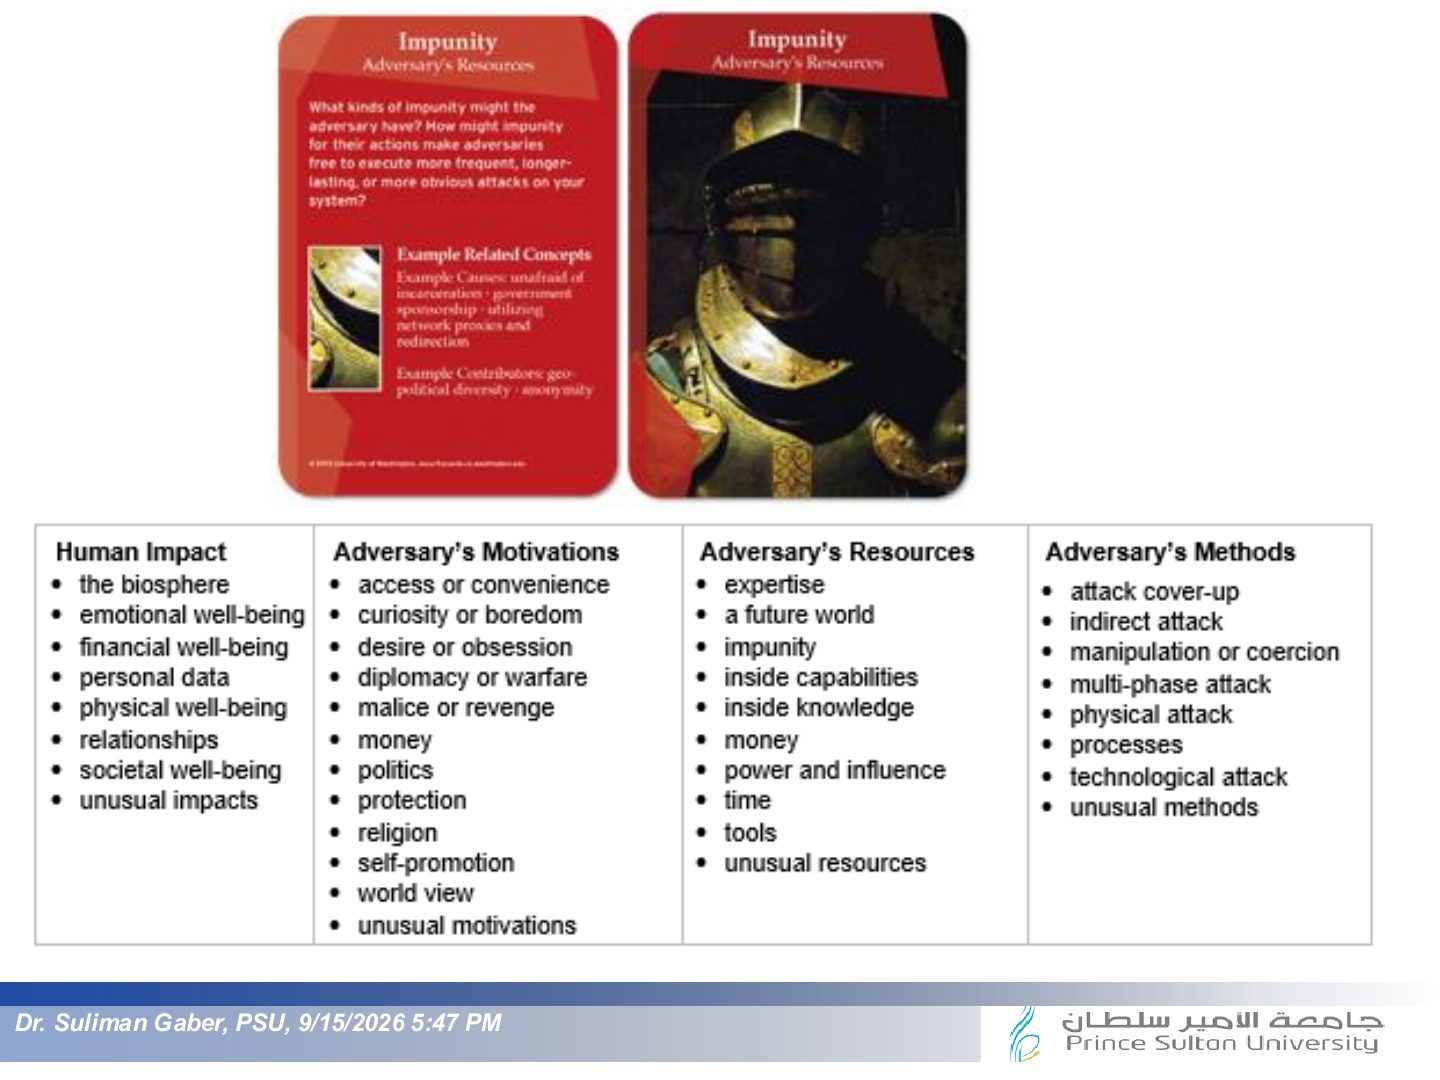
Security Cards
Slide 41
hTMM
Quantitative Threat Modeling Method
Slide 44
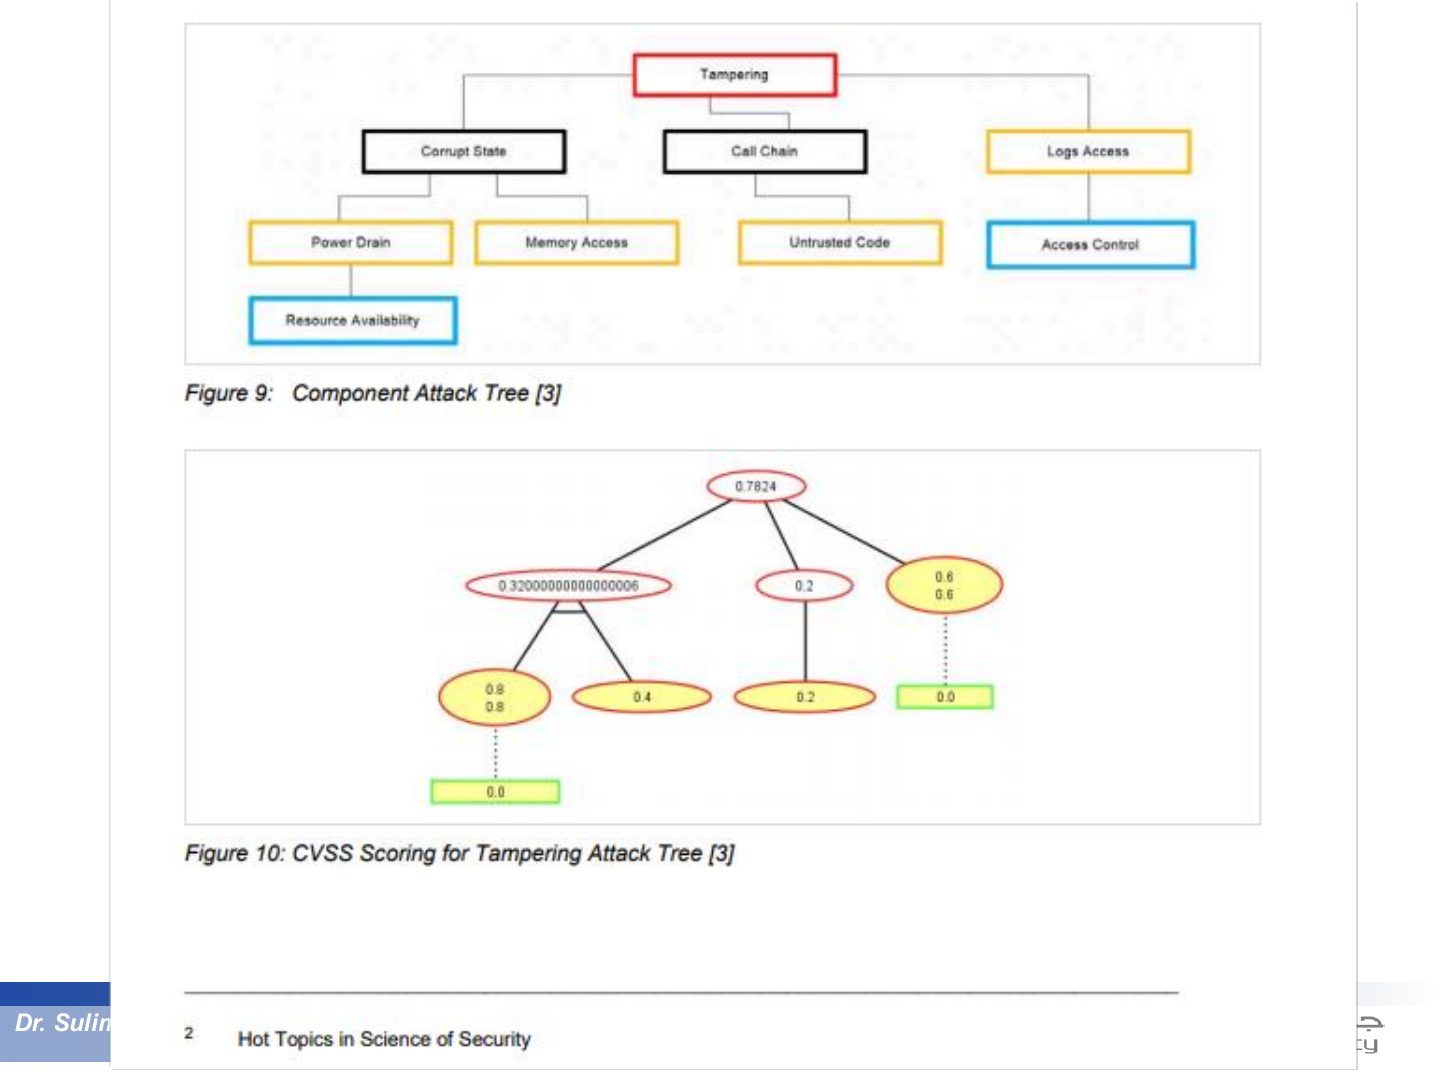
Trike
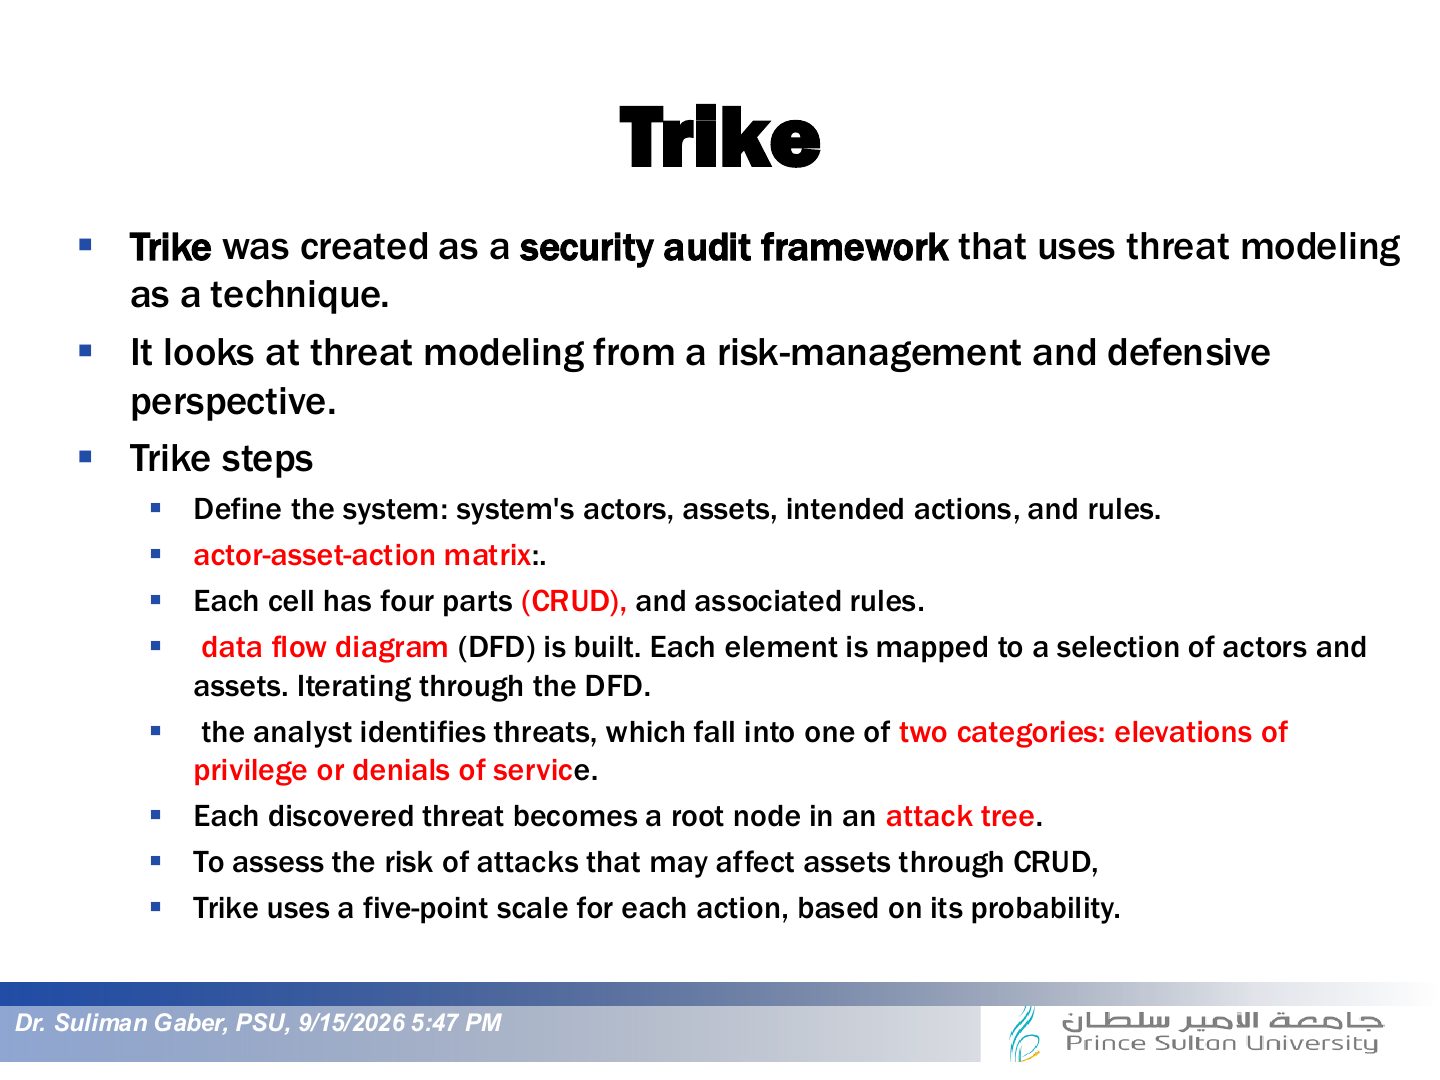
Visual, Agile, and Simple Threat modeling (VAST)
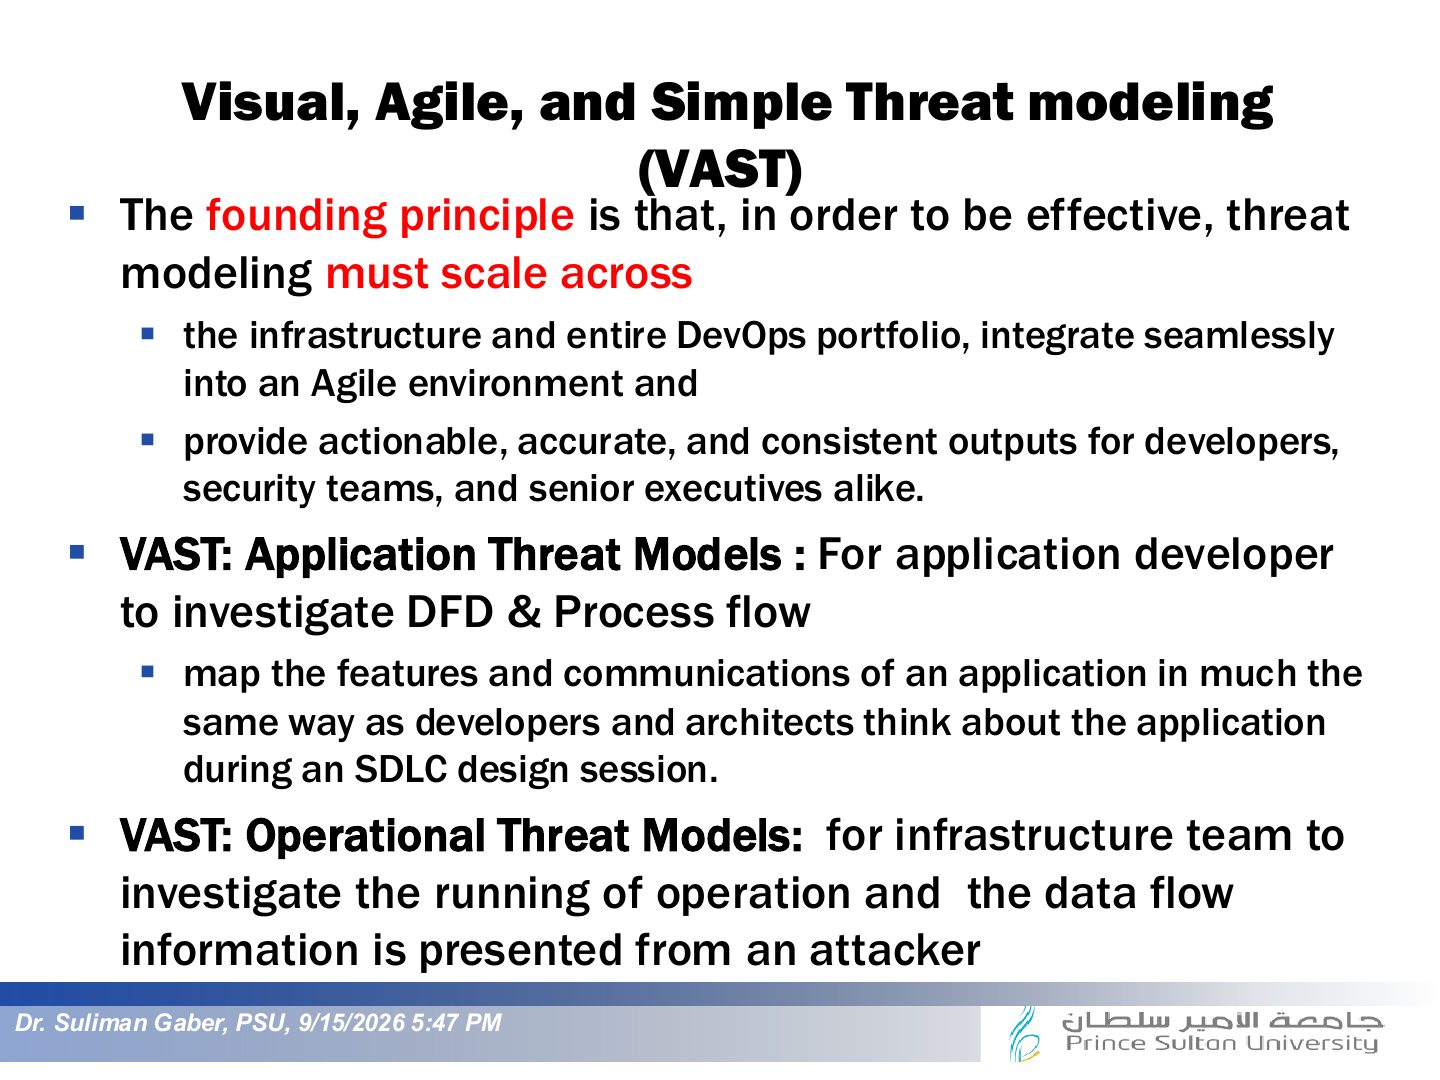
OCTAVE
Notes
OCTAVE: organizational, self-directed risk assessment of operational risk (Carnegie Mellon).
Slide 48
DREAD
Exam angle
The "R" in DREAD stands for:
Example
Slide 51
Threat/Vulnerability Pairs
Notes
Threat/vulnerability pair: a threat matters only if a matching vulnerability exists (and vice versa).
Threat Matrix