the framework for compliance, risk and IT alignment
Security Risk Management, Governance and Control
Why cyber risk matters to the business, IT risk vs. IT value (Risk IT, Val IT, COBIT), the CIA triad, business-driven security, cybersecurity management and governance, security blueprints, the policy hierarchy (policies, standards, procedures, baselines, guidelines) and planning horizons.
How to read this page
Every original slide is shown unchanged. Yellow marks on a slide point to a numbered note: hover or tap a mark to jump to its note, and hover a note to see its marks. Questions tagged Past exam appeared on a real paper; Prediction questions are likely angles, not confirmed. Pick an answer to each question: a wrong pick tells you why it is wrong, so you can try again.
All 34 slides
- 1 Slide 1
- 2 Intended Learning Outcomes
- 3 Agenda
- 4 Risks in Business
- 5 Why Care About Cyber Risk?
- 6 Why Care About Cyber Risk?
- 7 Why Care About Cyber Risk?
- 8 Manage and Capitalize on Risk
- 9 IT Risk and IT Value
- 10 Risk IT Extends Val IT and COBIT
- 11 Where IT Risk Fits In
- 12 Cybersecurity TRIAD
- 13 Business-Driven Security
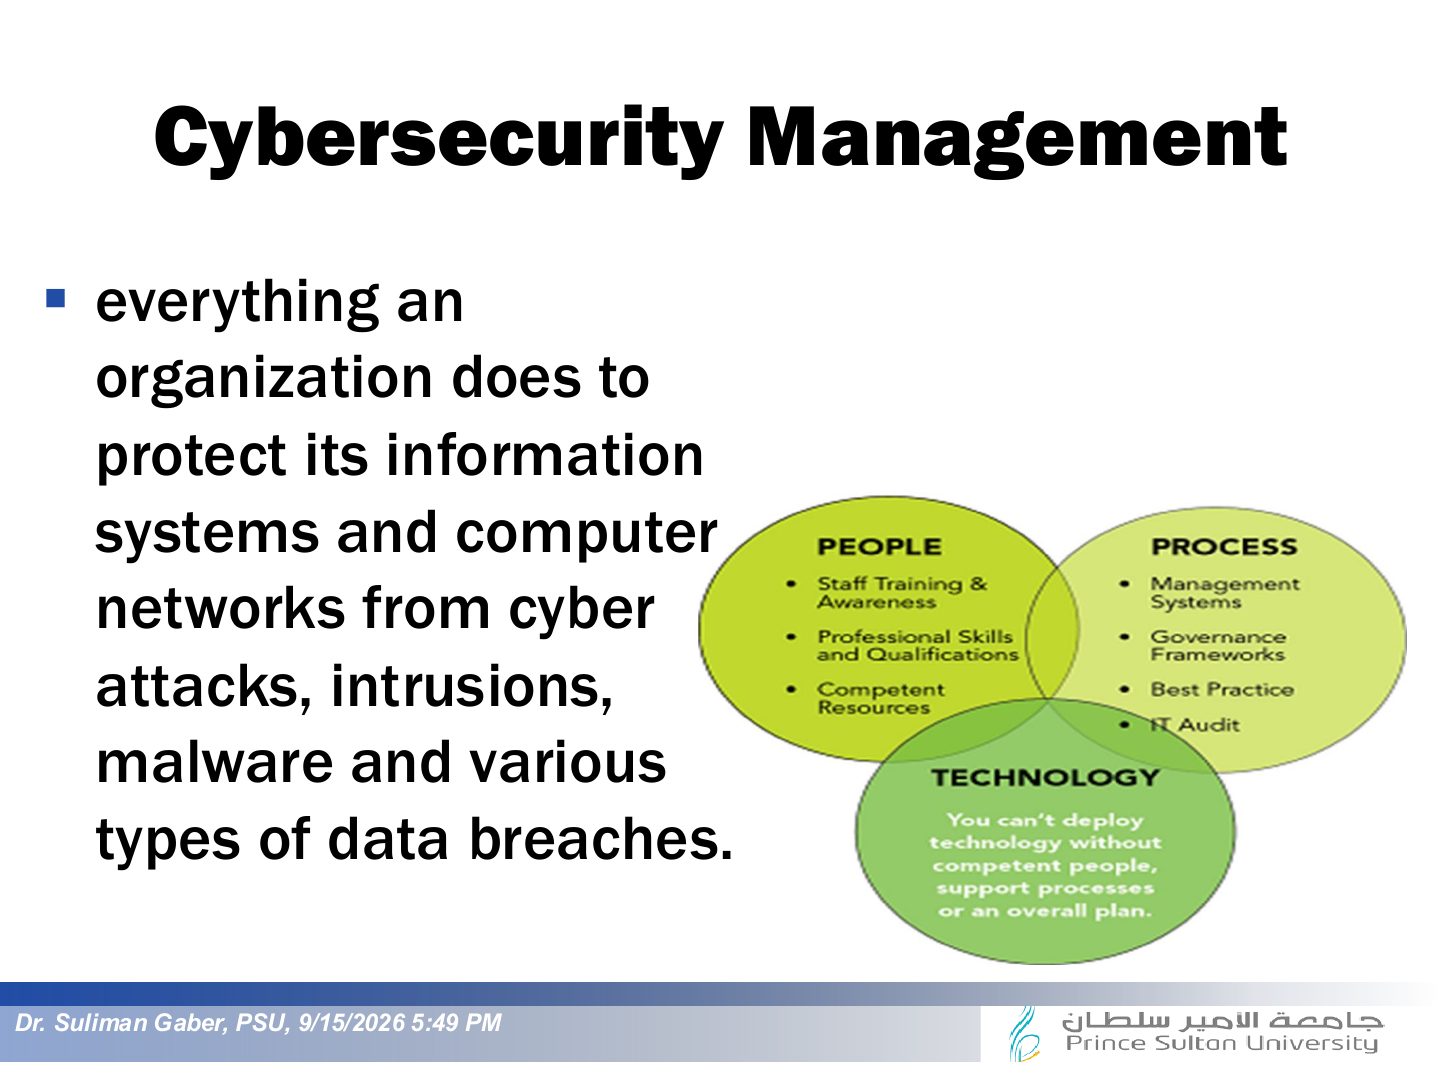
- 14 Cybersecurity Management
- 15 Organizational & Business Requirements
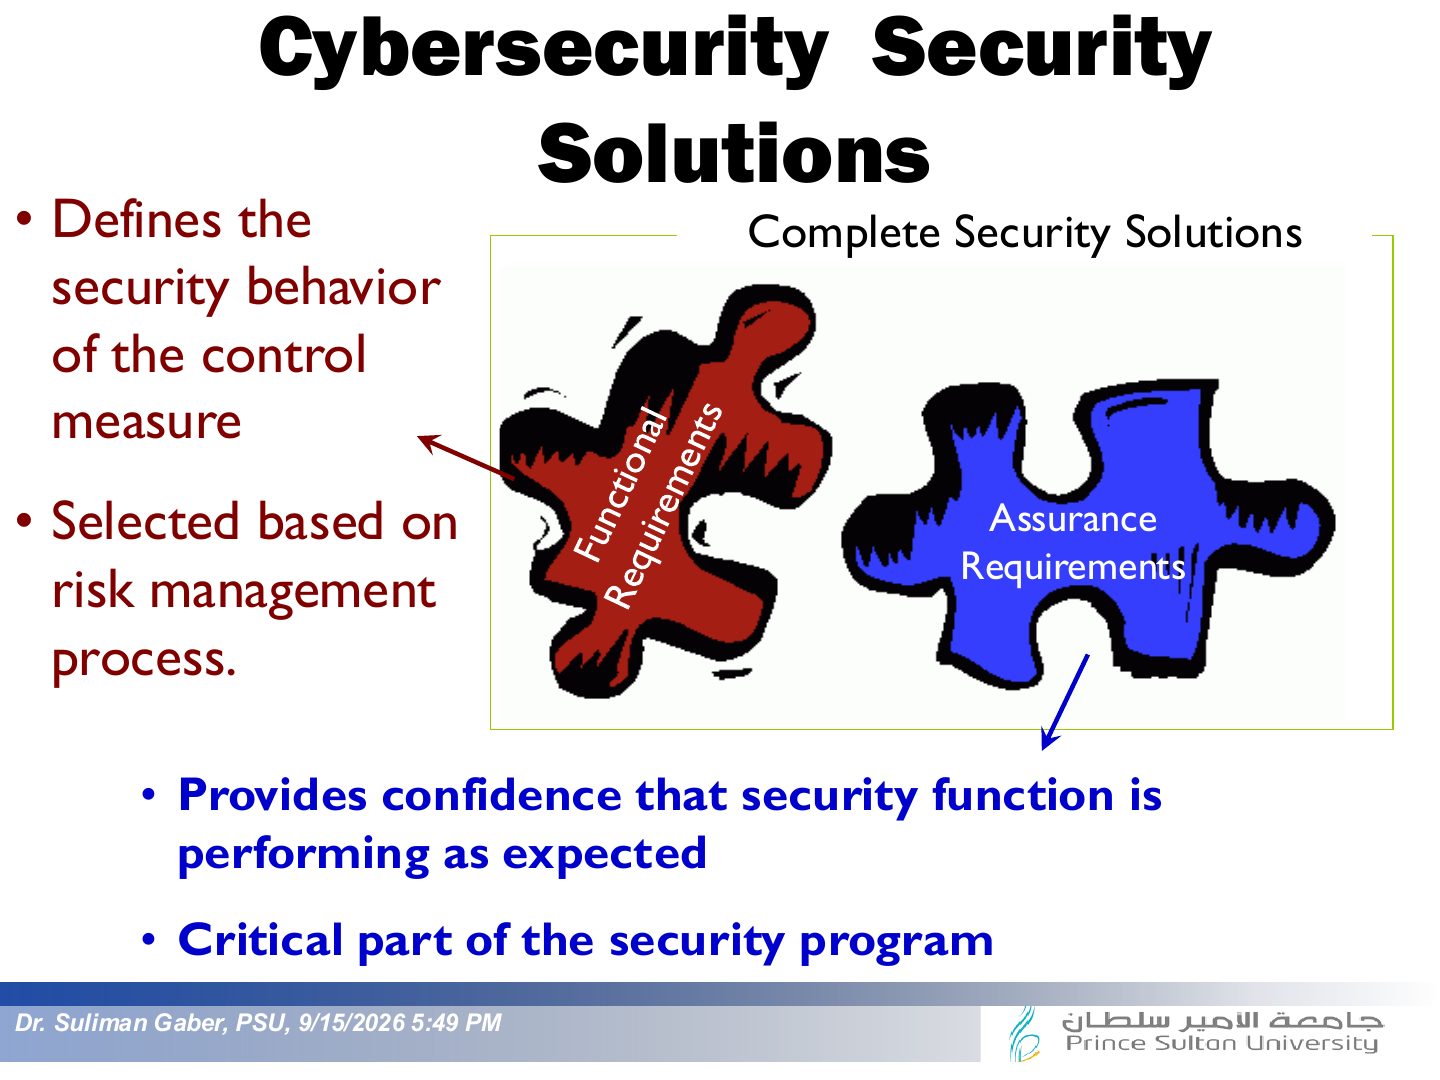
- 16 Cybersecurity Security Solutions
- 17 Cybersecurity Management
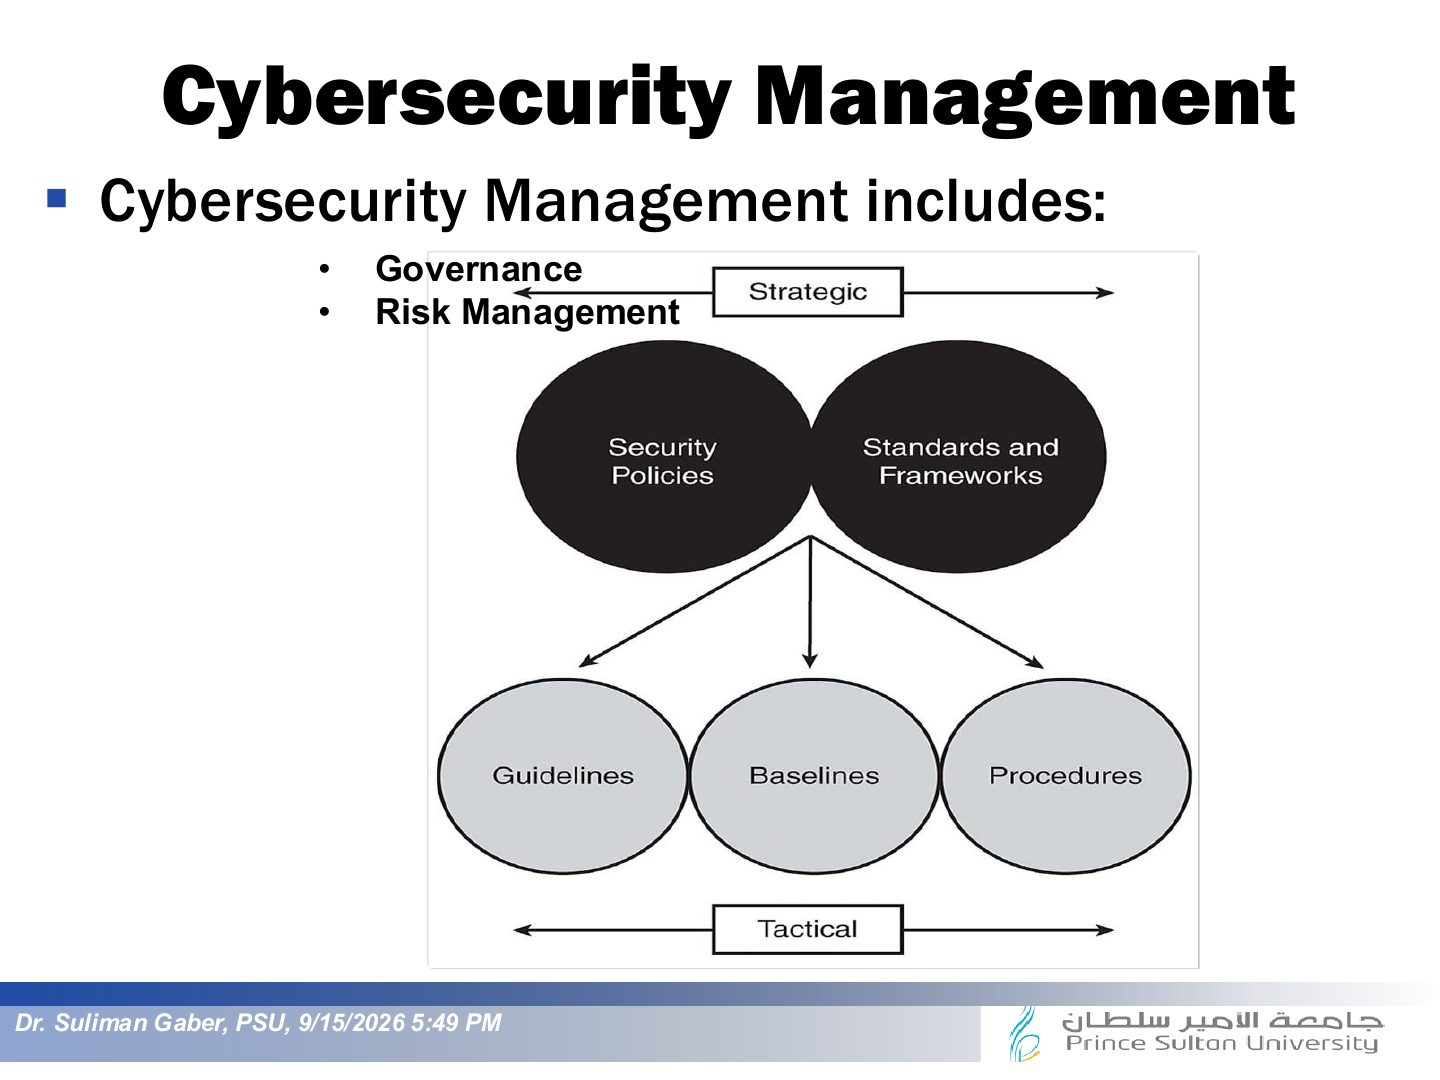
- 18 Cybersecurity Management
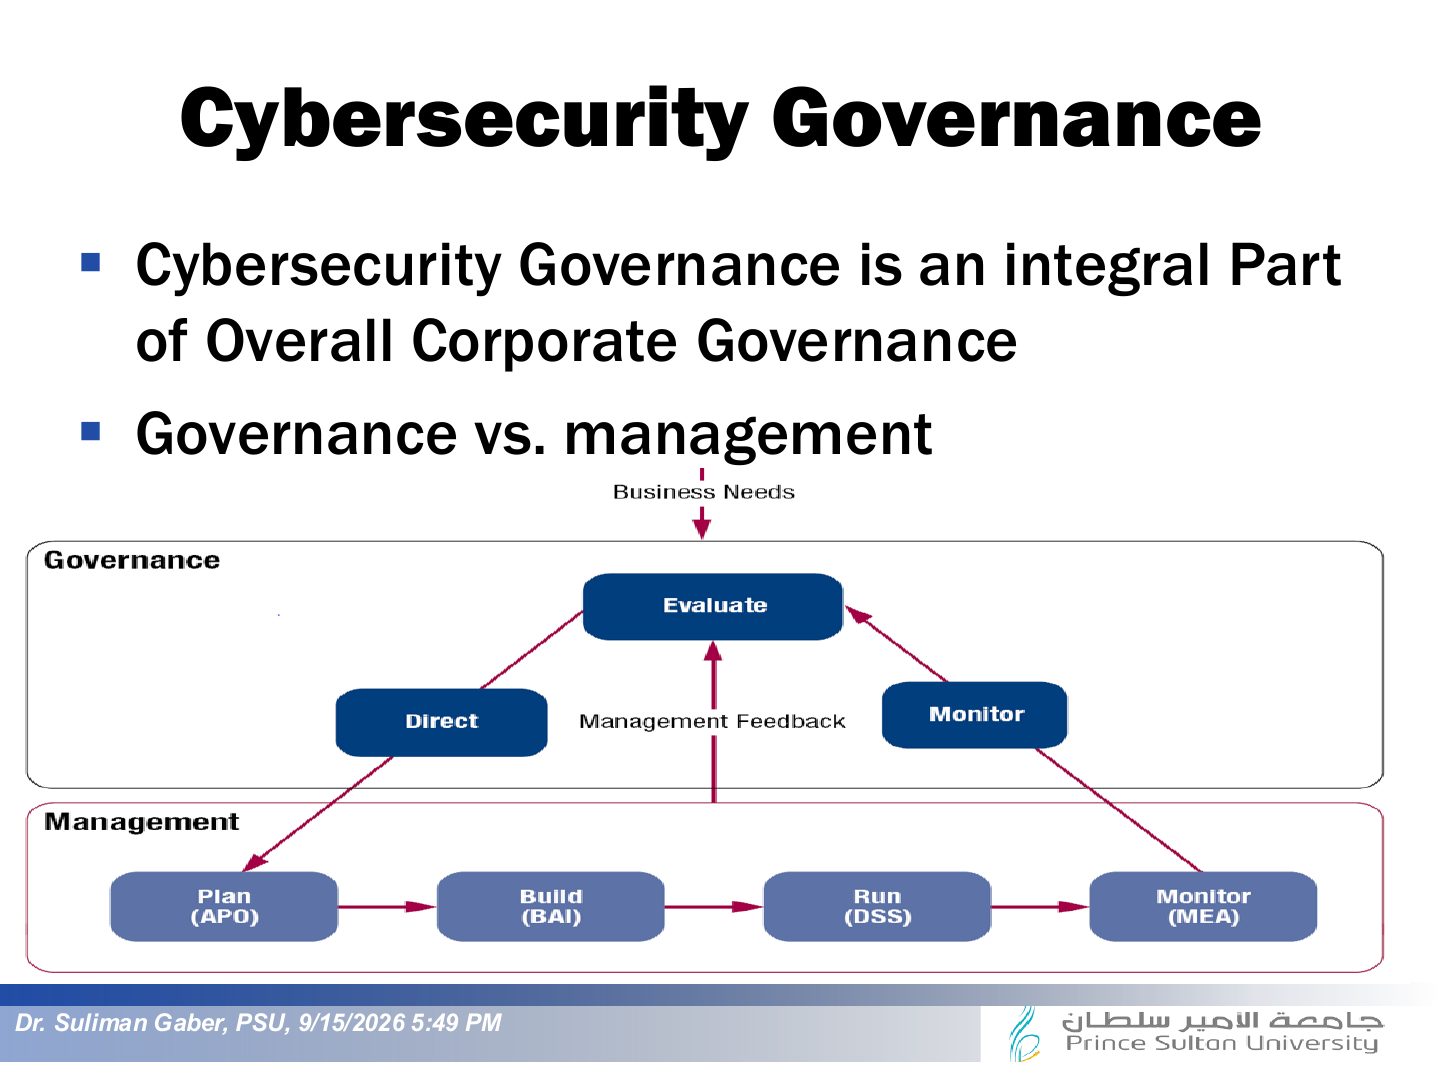
- 19 Cybersecurity Governance
- 20 Slide 20
- 21 Cybersecurity Governance
- 22 Security Blueprints
- 23 Policy Overview
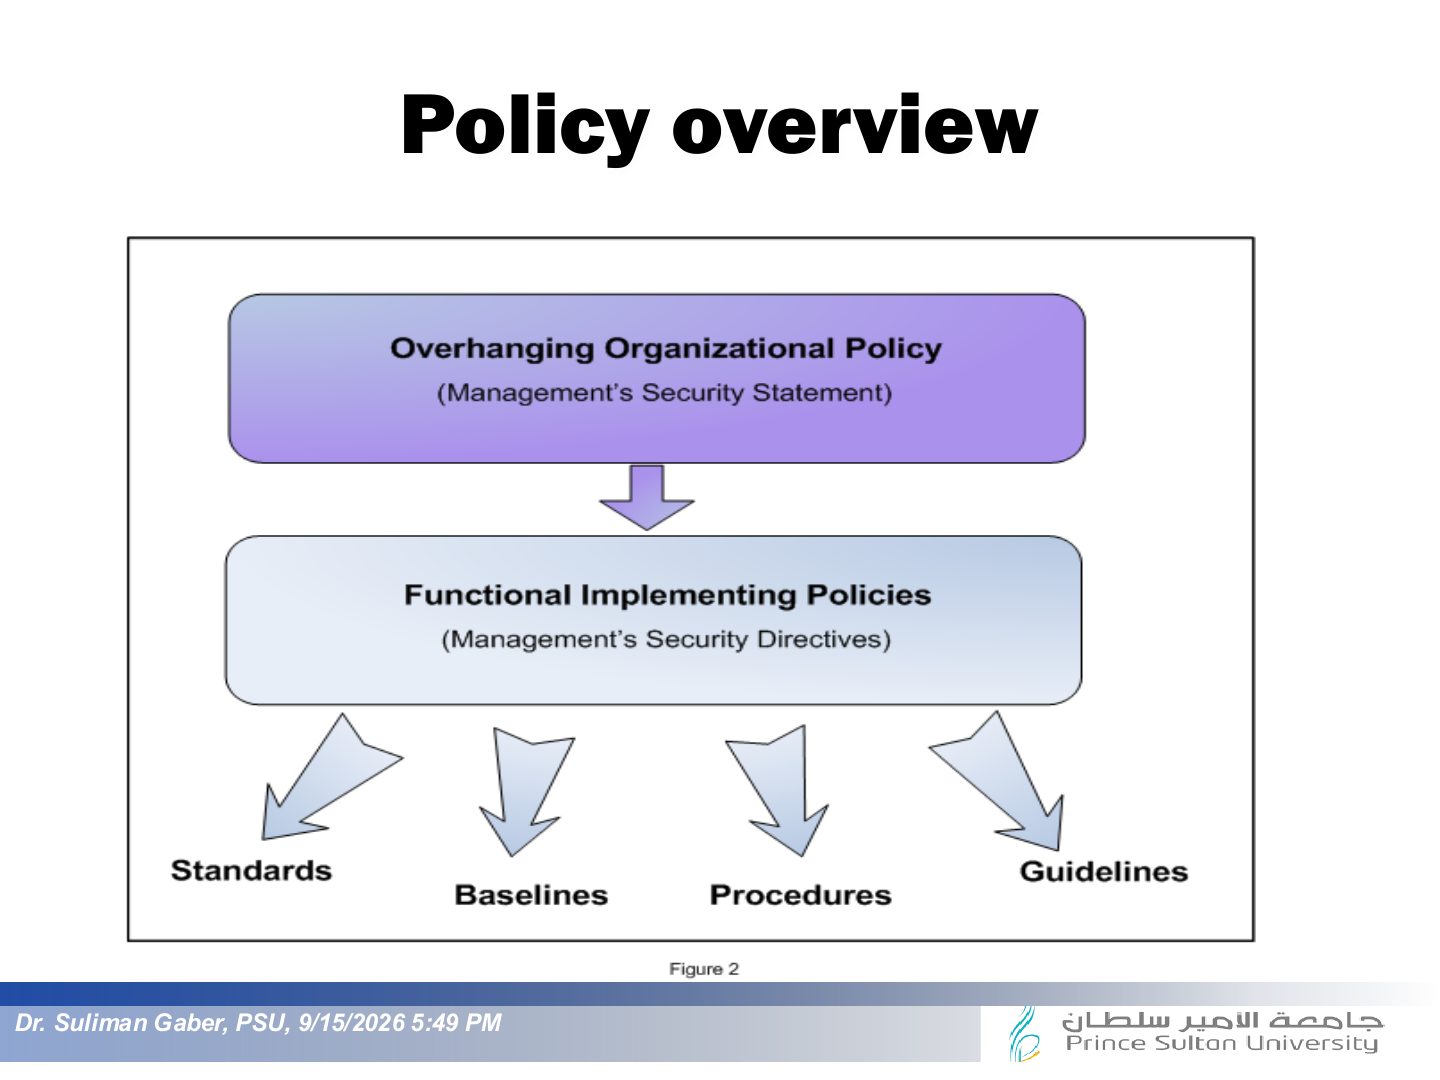
- 24 Policy overview
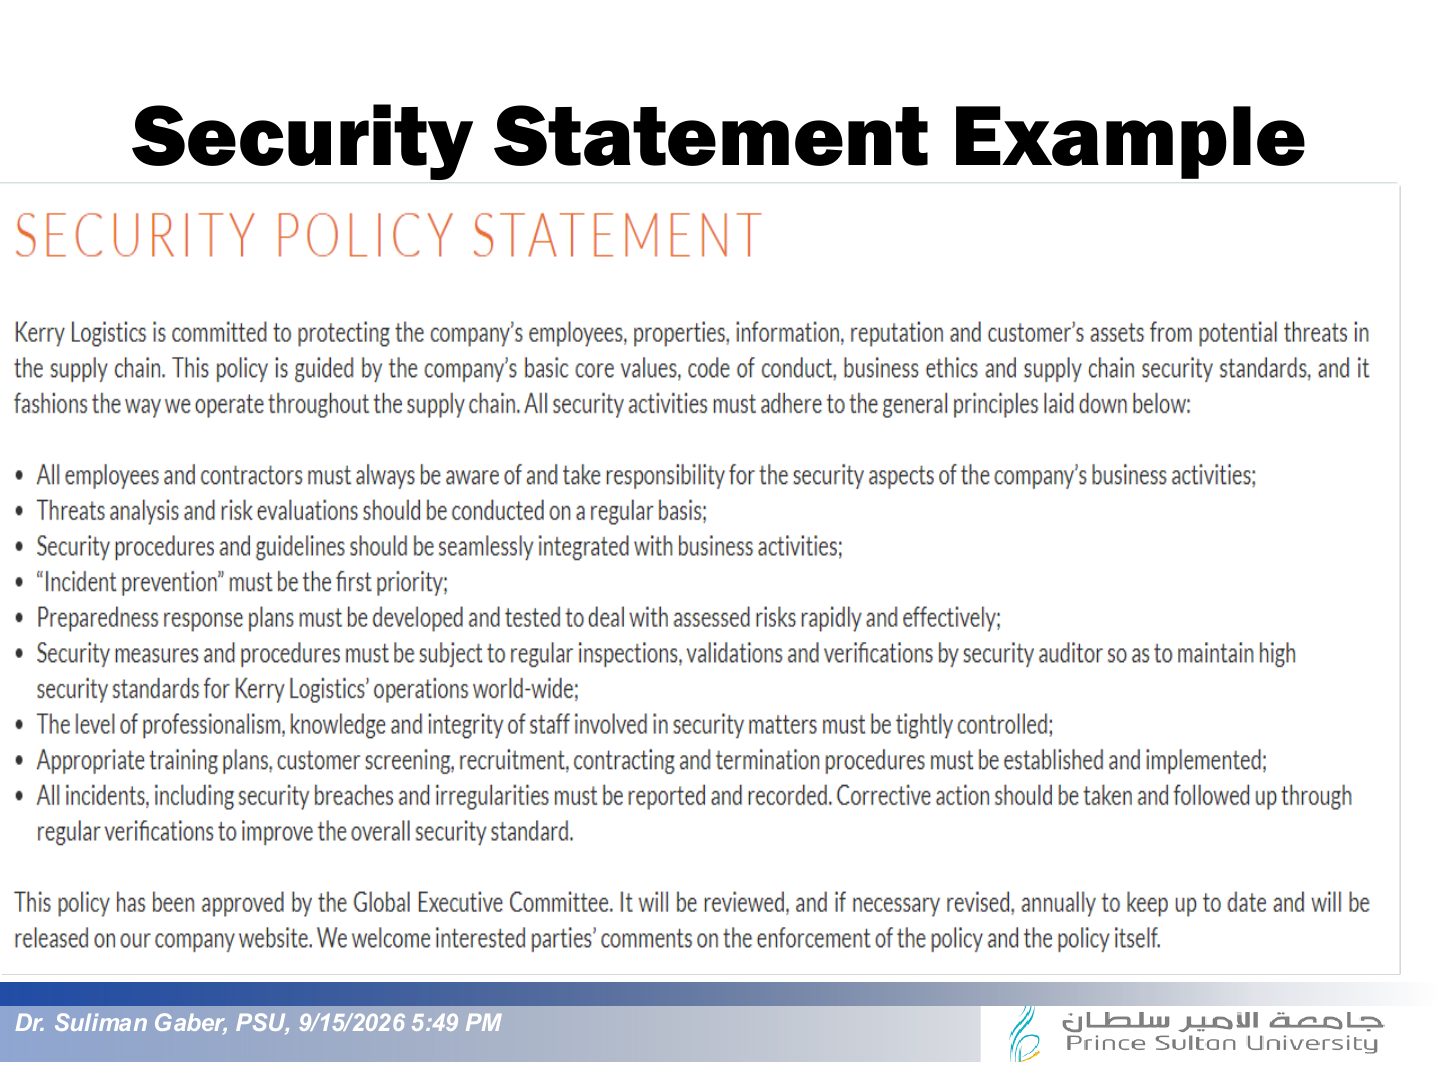
- 25 Security Statement Example
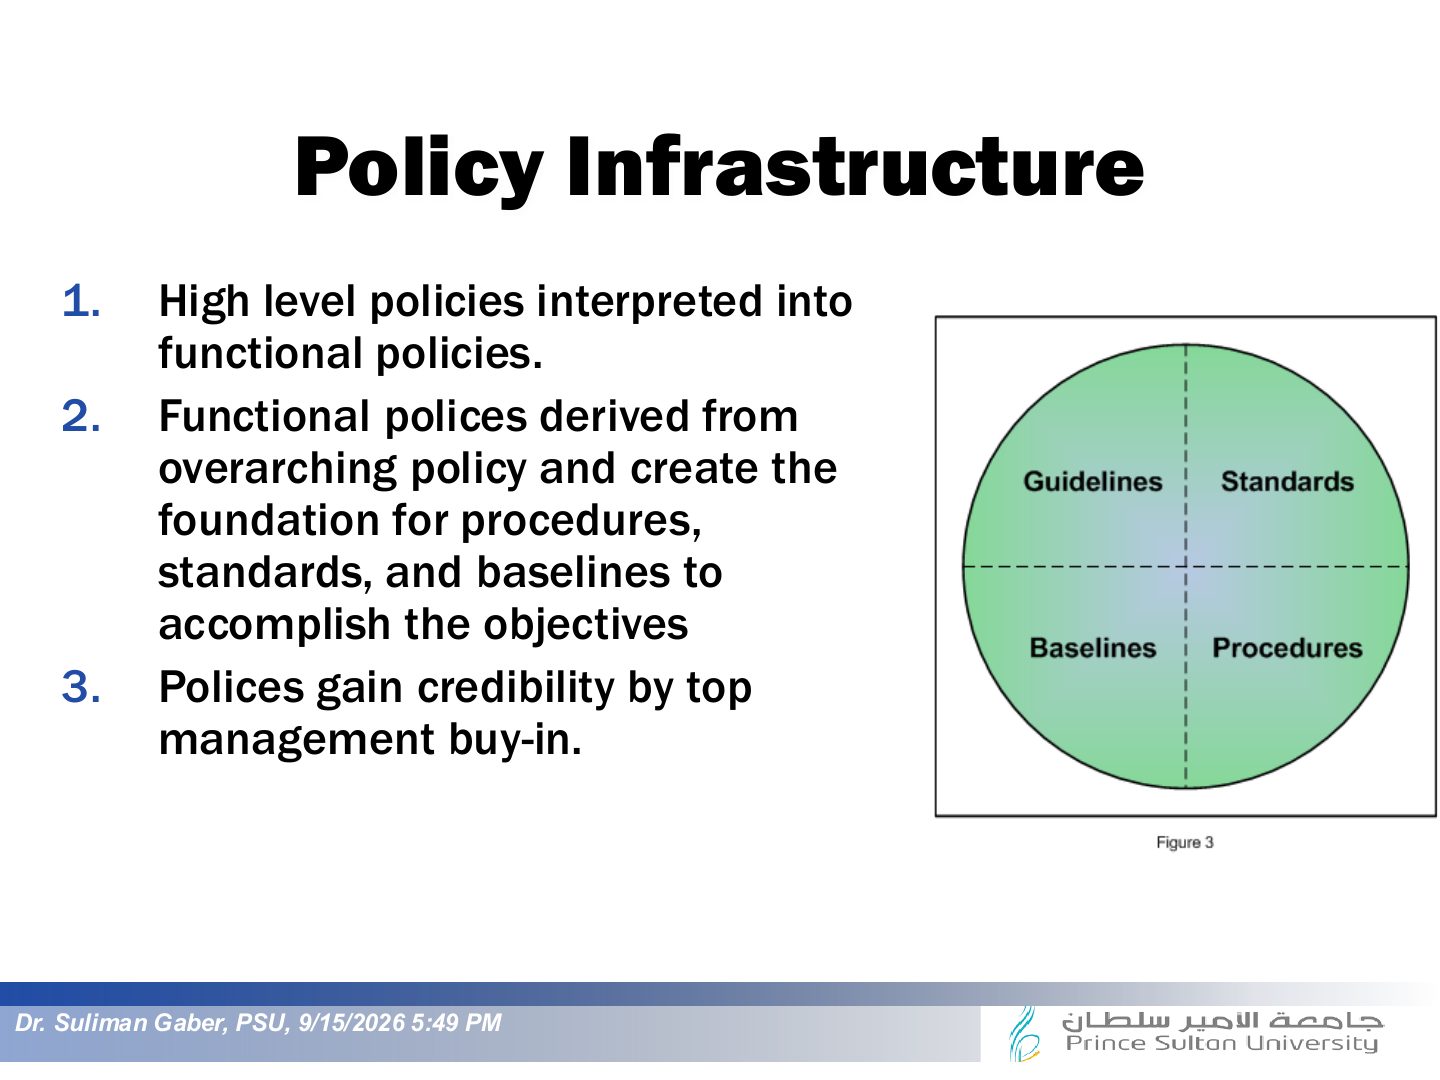
- 26 Policy Infrastructure
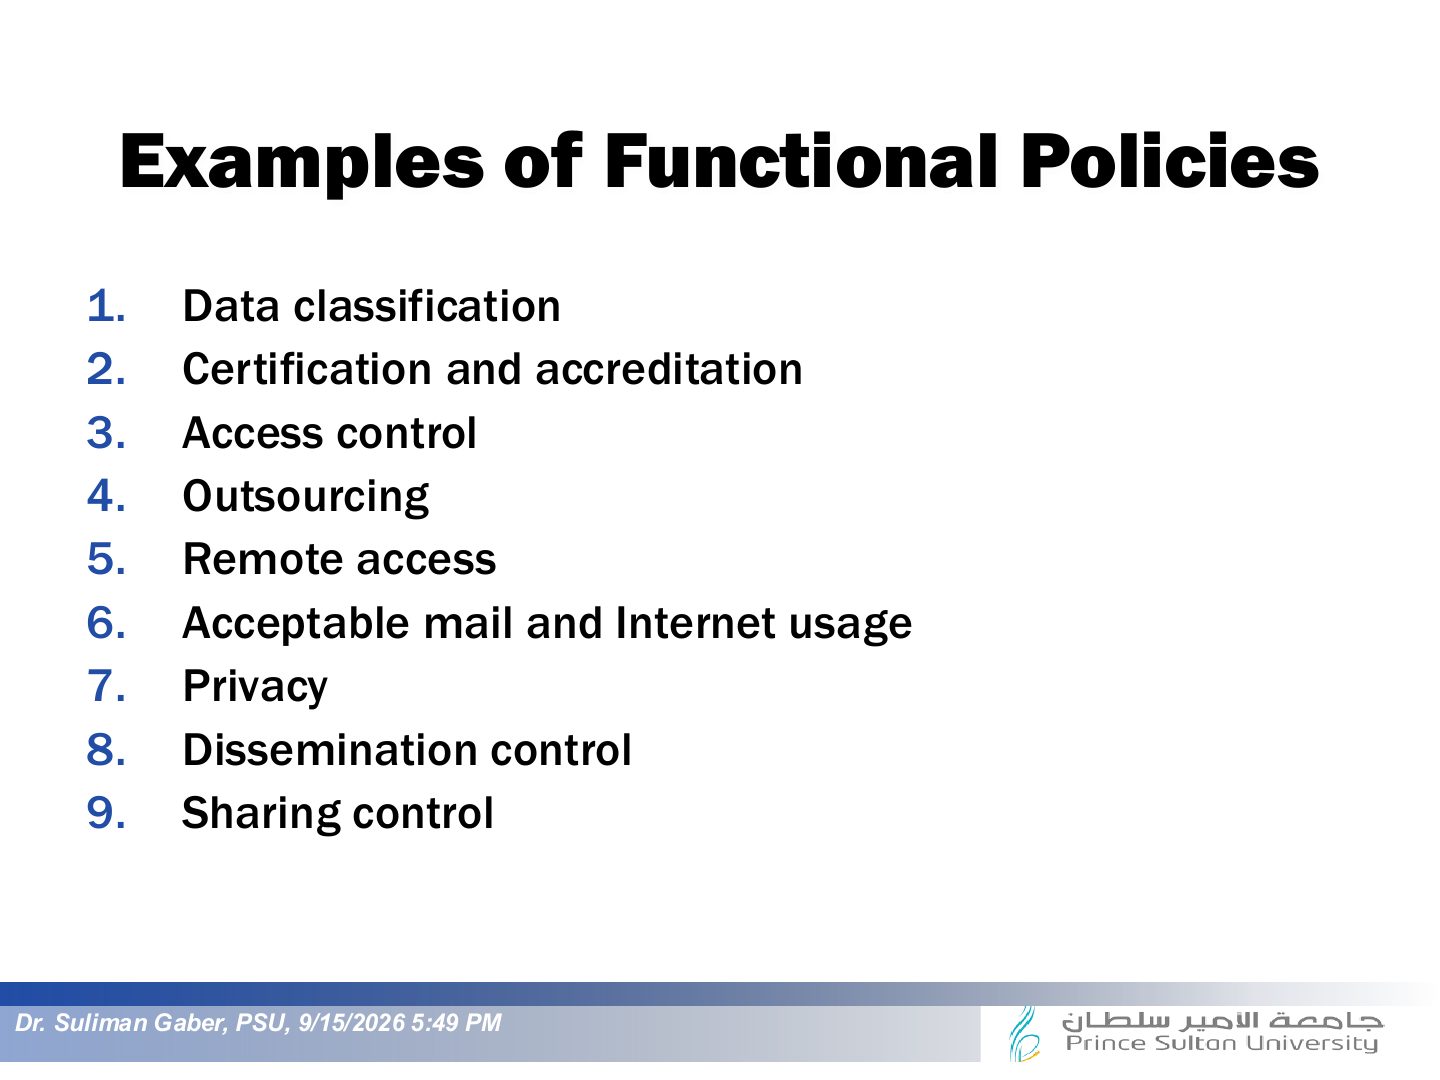
- 27 Examples of Functional Policies
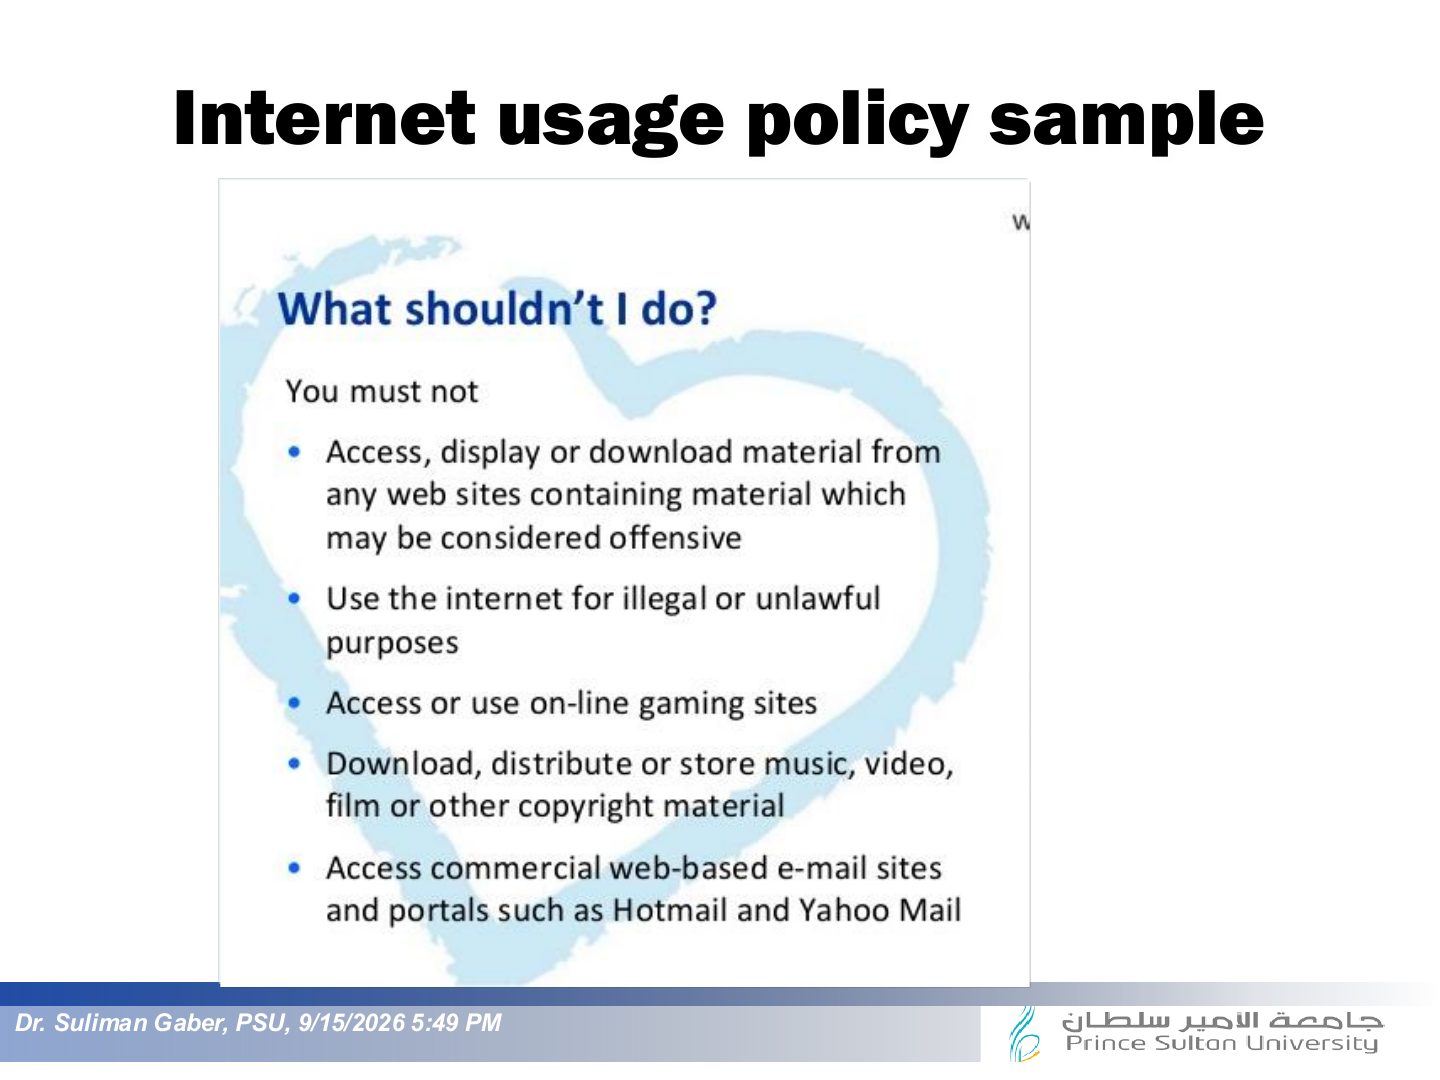
- 28 Internet usage policy sample
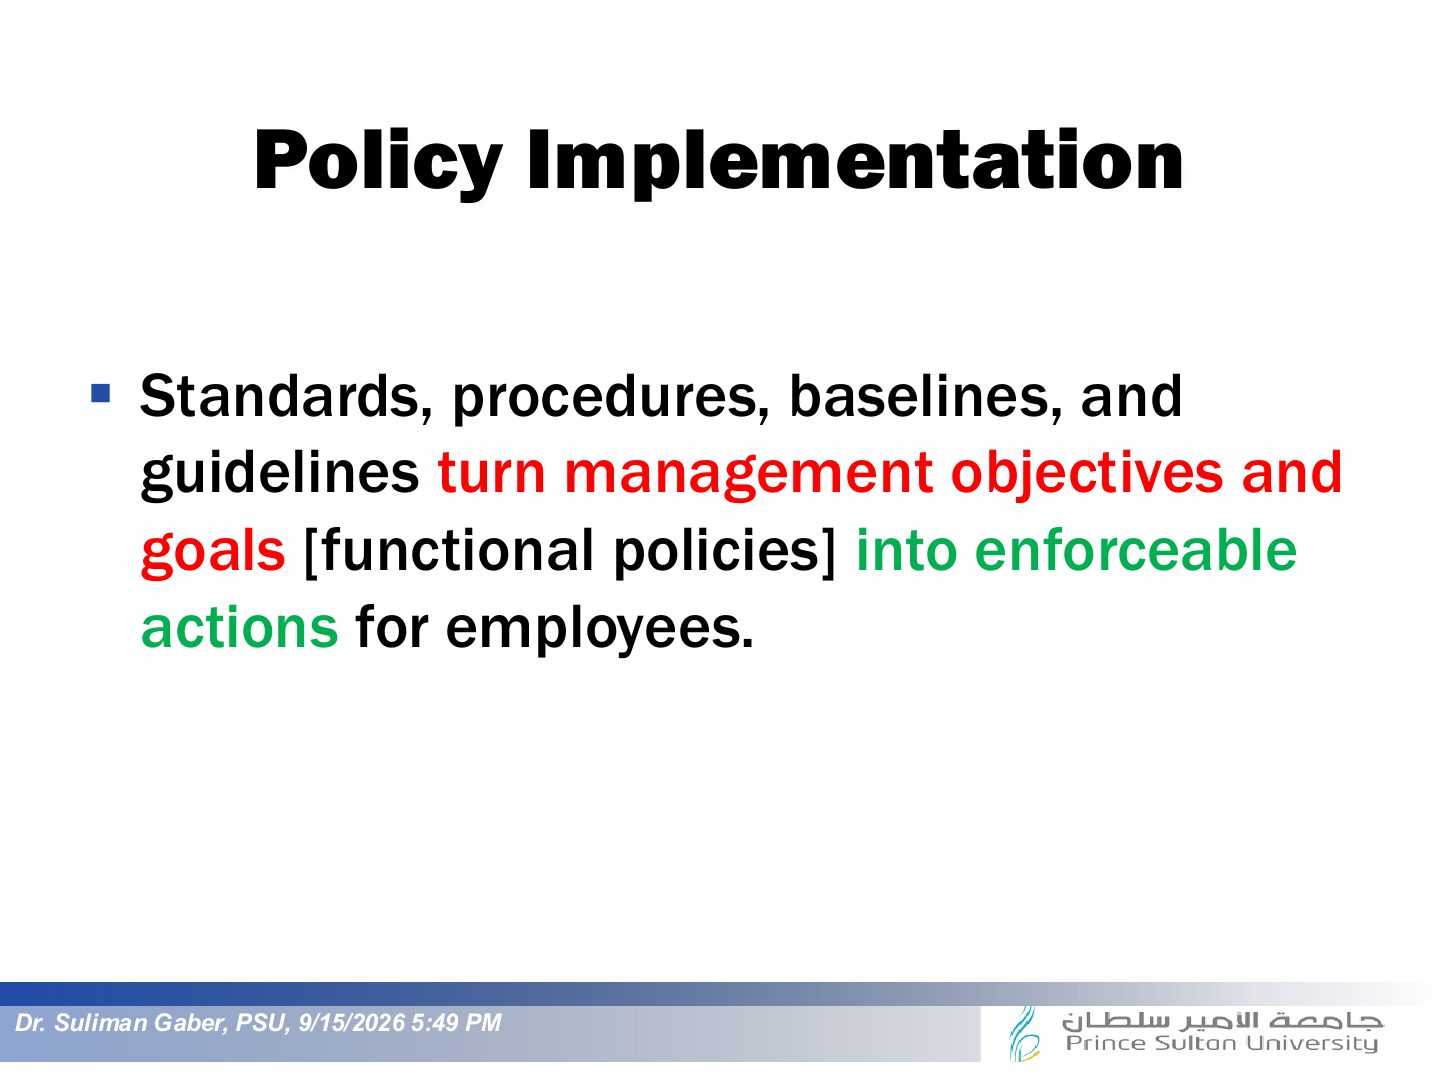
- 29 Policy Implementation
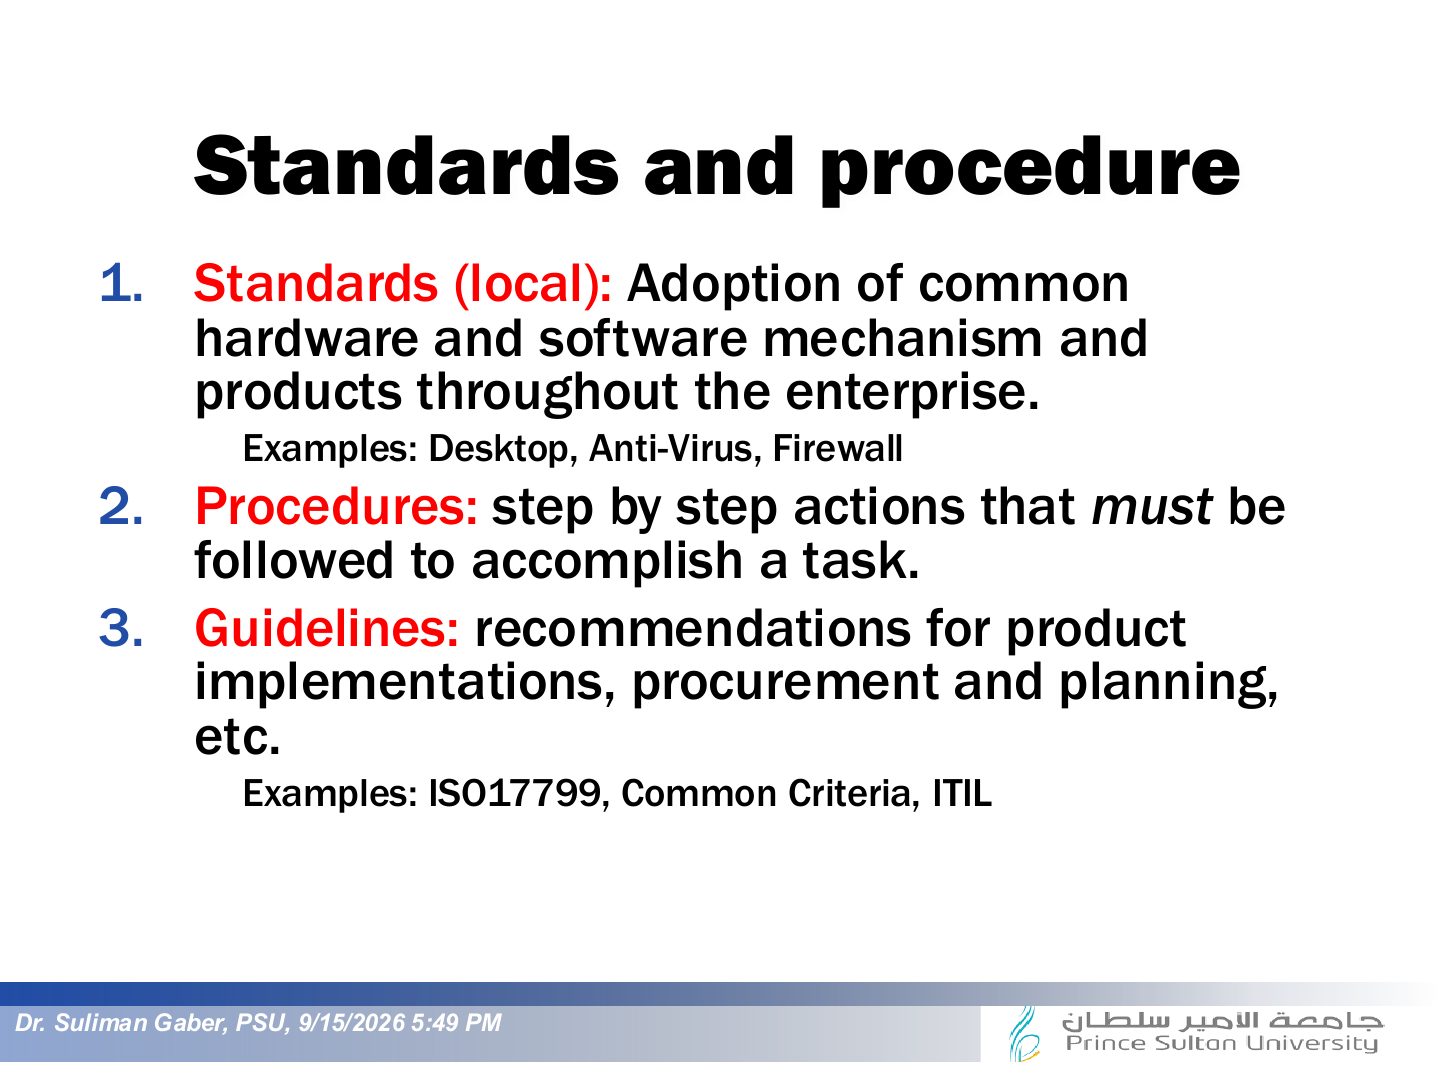
- 30 Standards and procedure
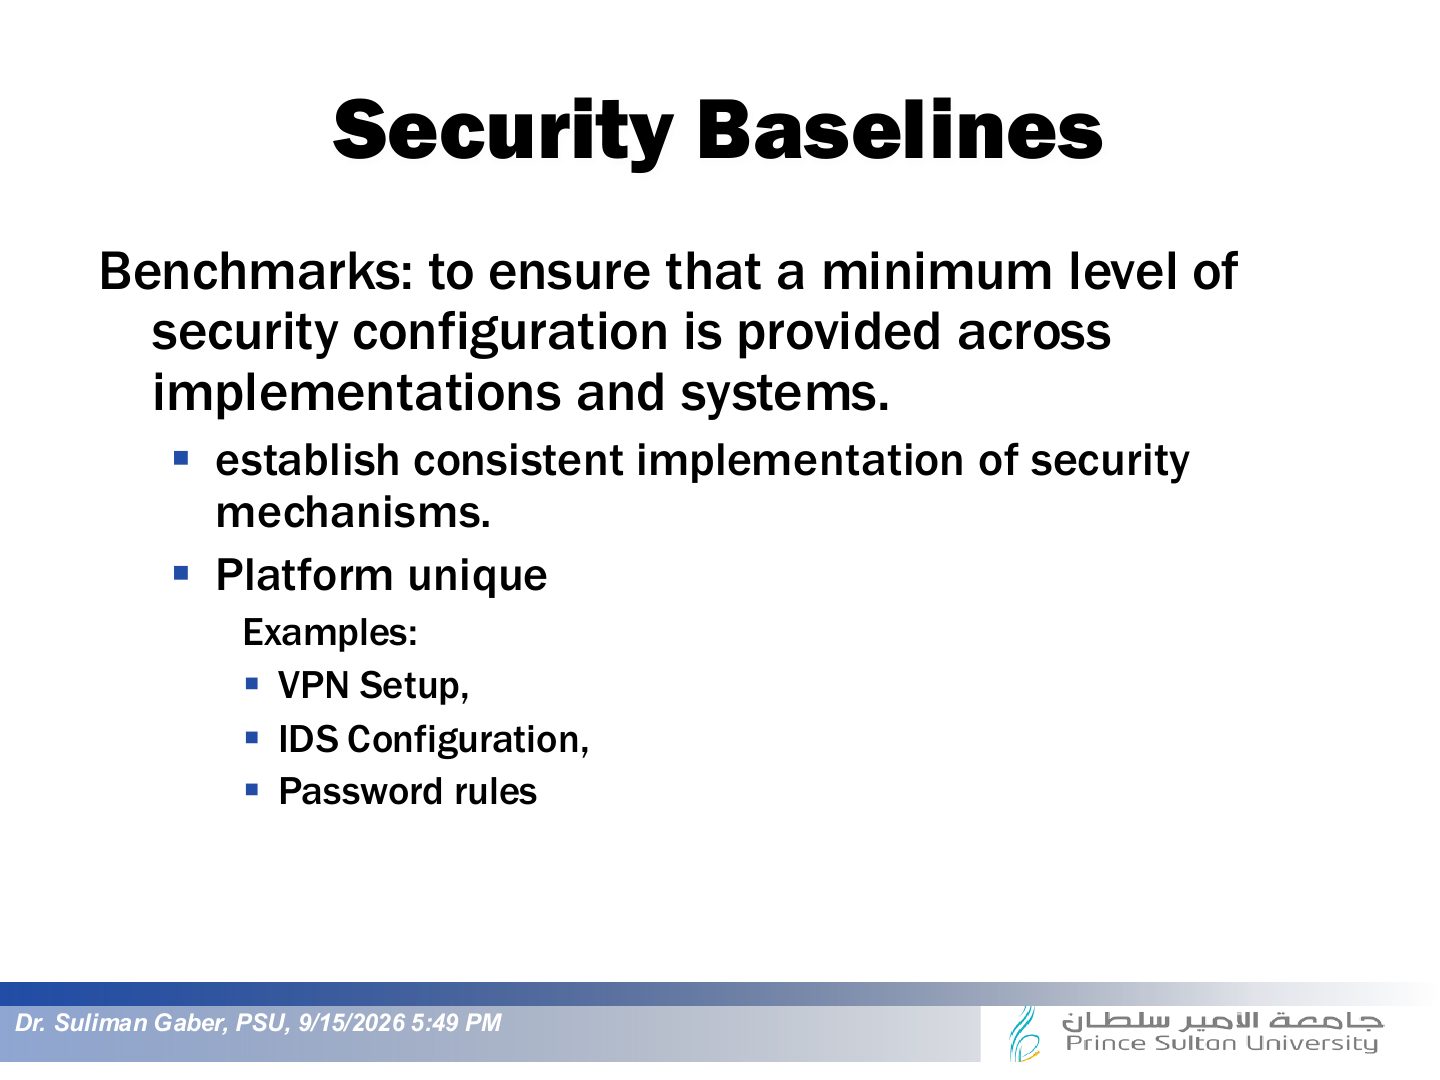
- 31 Security Baselines
- 32 Three Levels of security planning
- 33 Risk Management
- 34 Slide 34
Slide 1
Intended Learning Outcomes
Agenda
Risks in Business
Notes
Every business decision carries risk; security exists to support business goals, not the other way round.
Why Care About Cyber Risk?
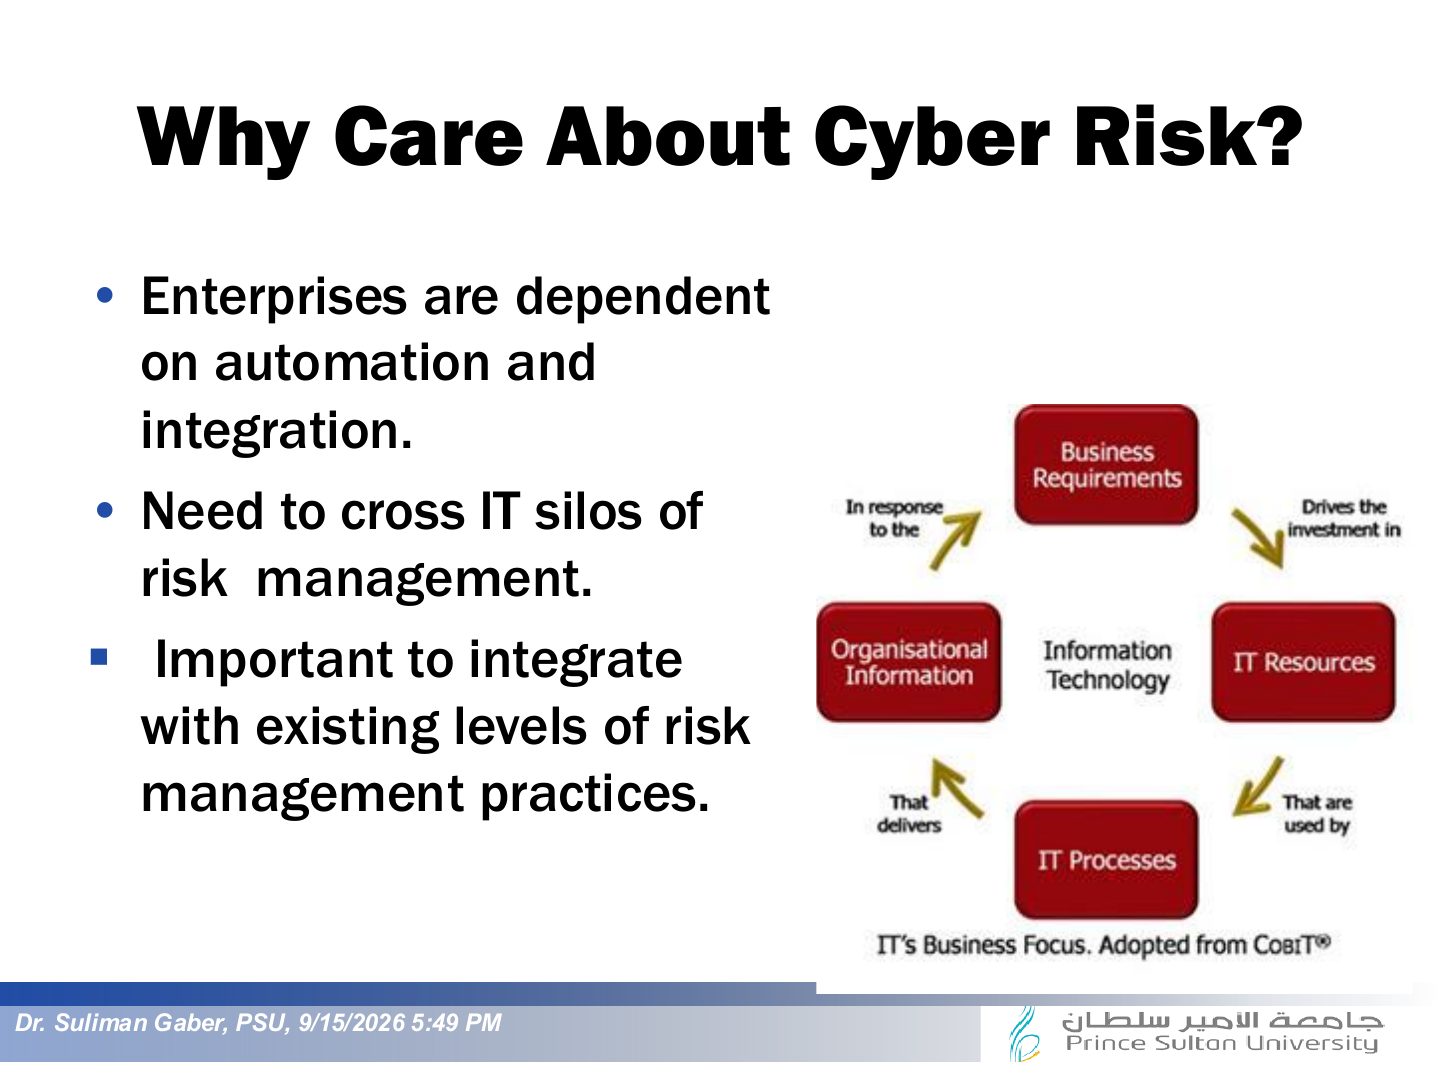
Why Care About Cyber Risk?
Why Care About Cyber Risk?
Manage and Capitalize on Risk
IT Risk and IT Value
Notes
IT risk is the flip side of IT value: managing risk protects the value IT creates.
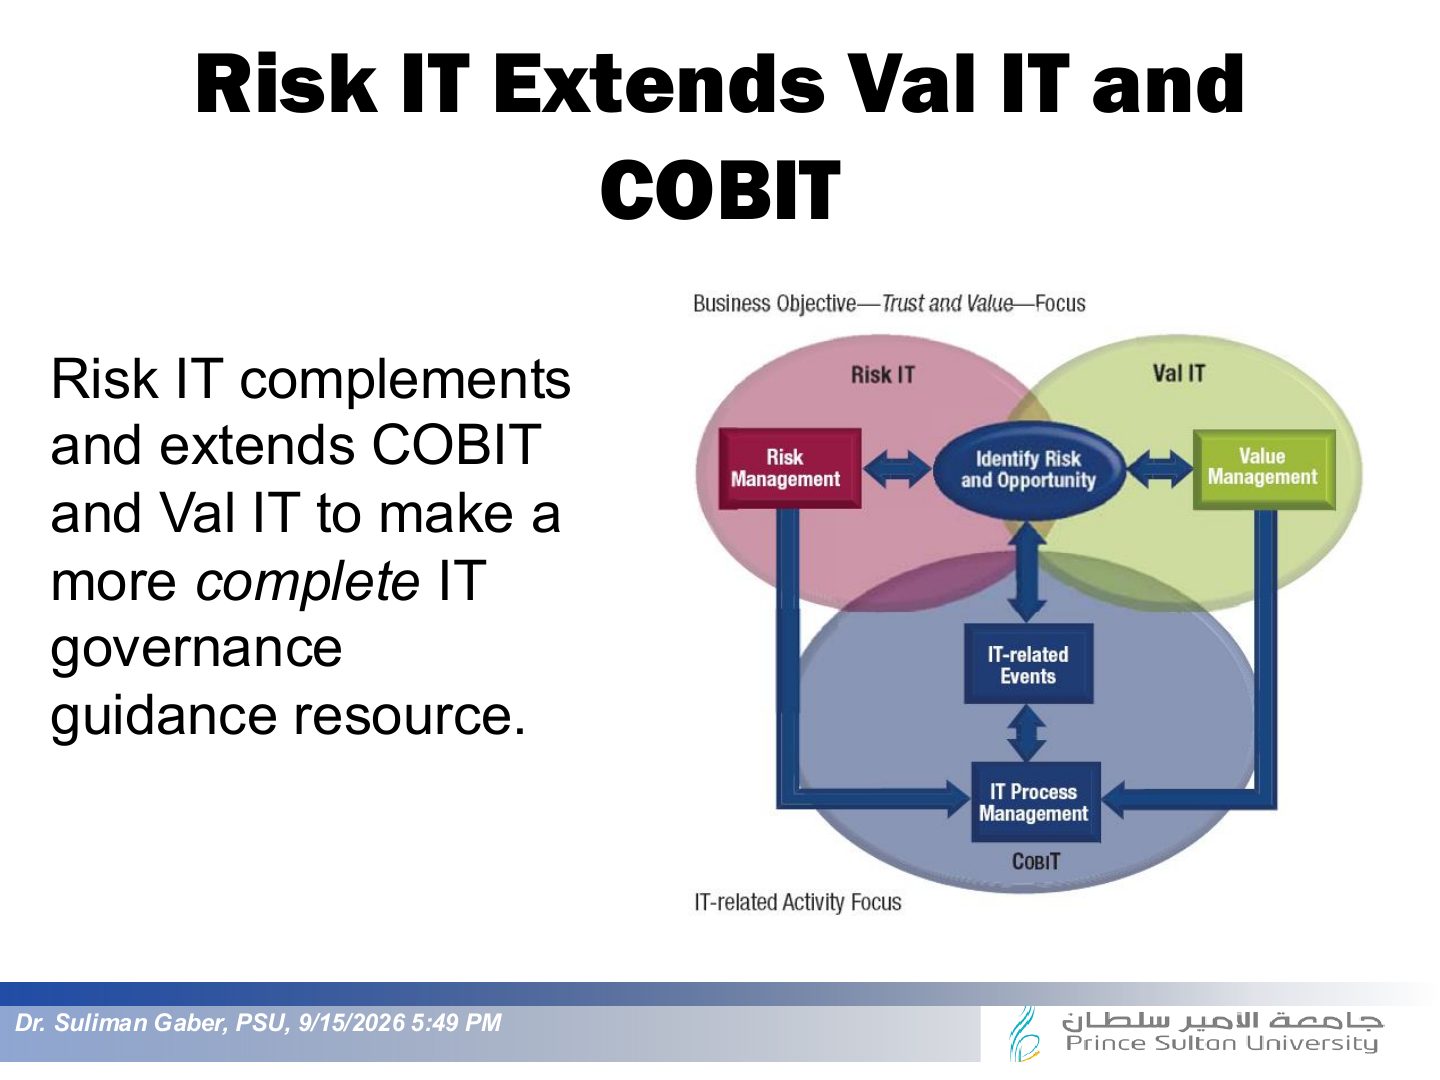
Risk IT Extends Val IT and COBIT
Notes
Risk IT extends Val IT and COBIT (ISACA frameworks) to cover IT-related business risk.
Exam angle
Which framework helps organizations with regulatory compliance, risk management and aligning IT strategy with business goals?
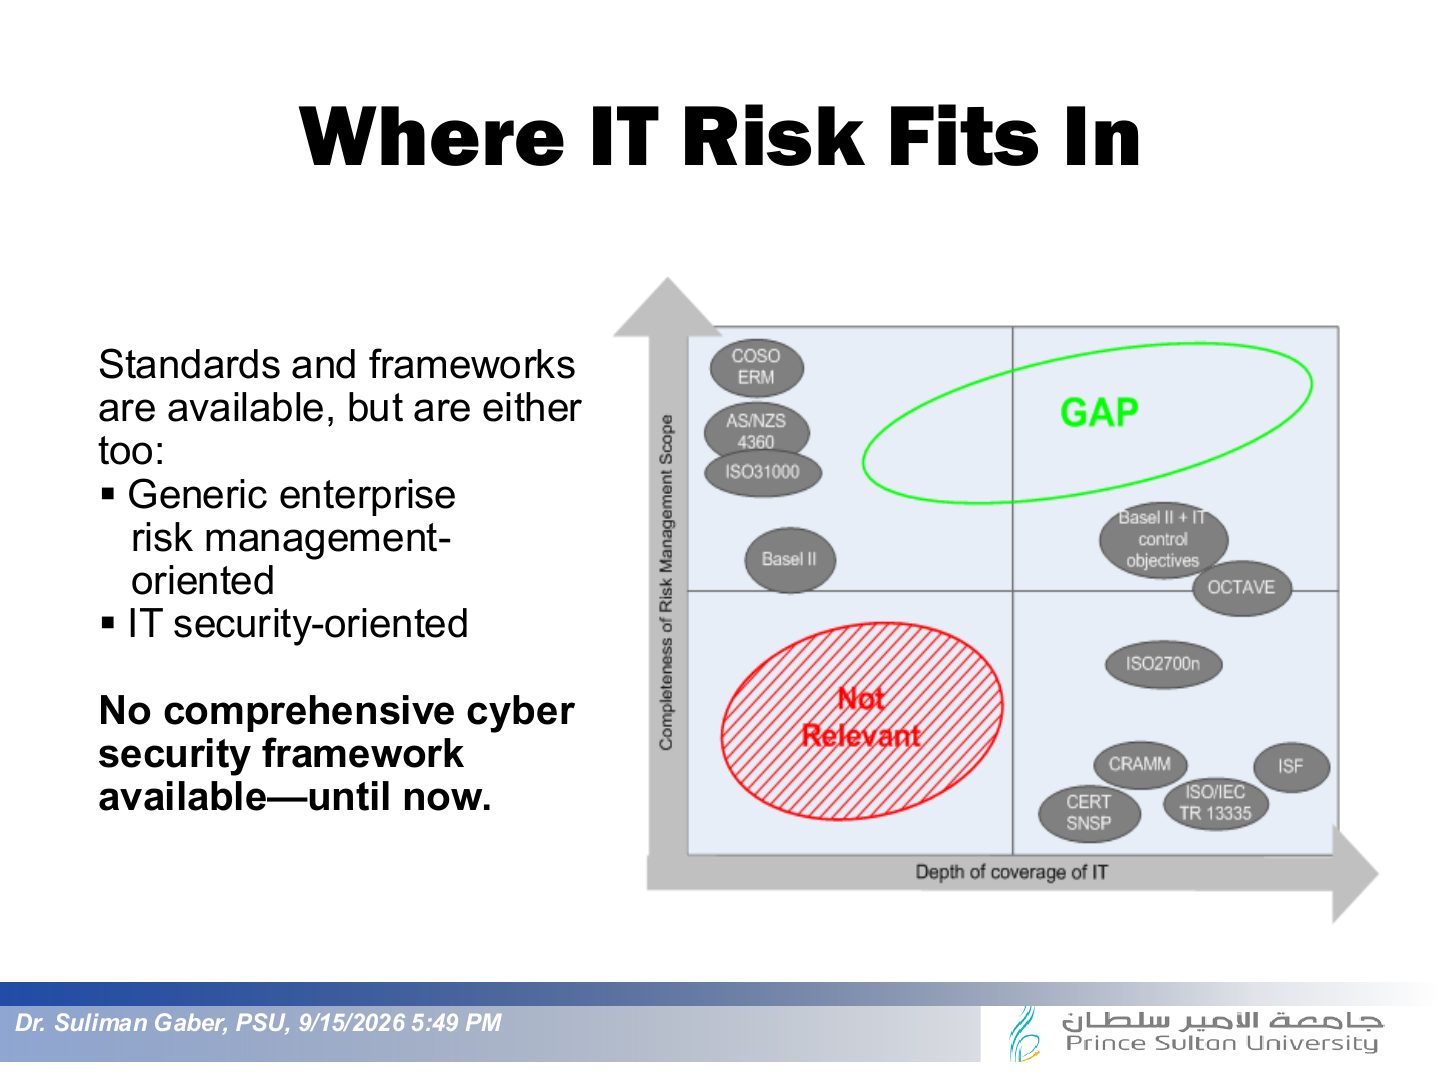
Where IT Risk Fits In
Cybersecurity TRIAD
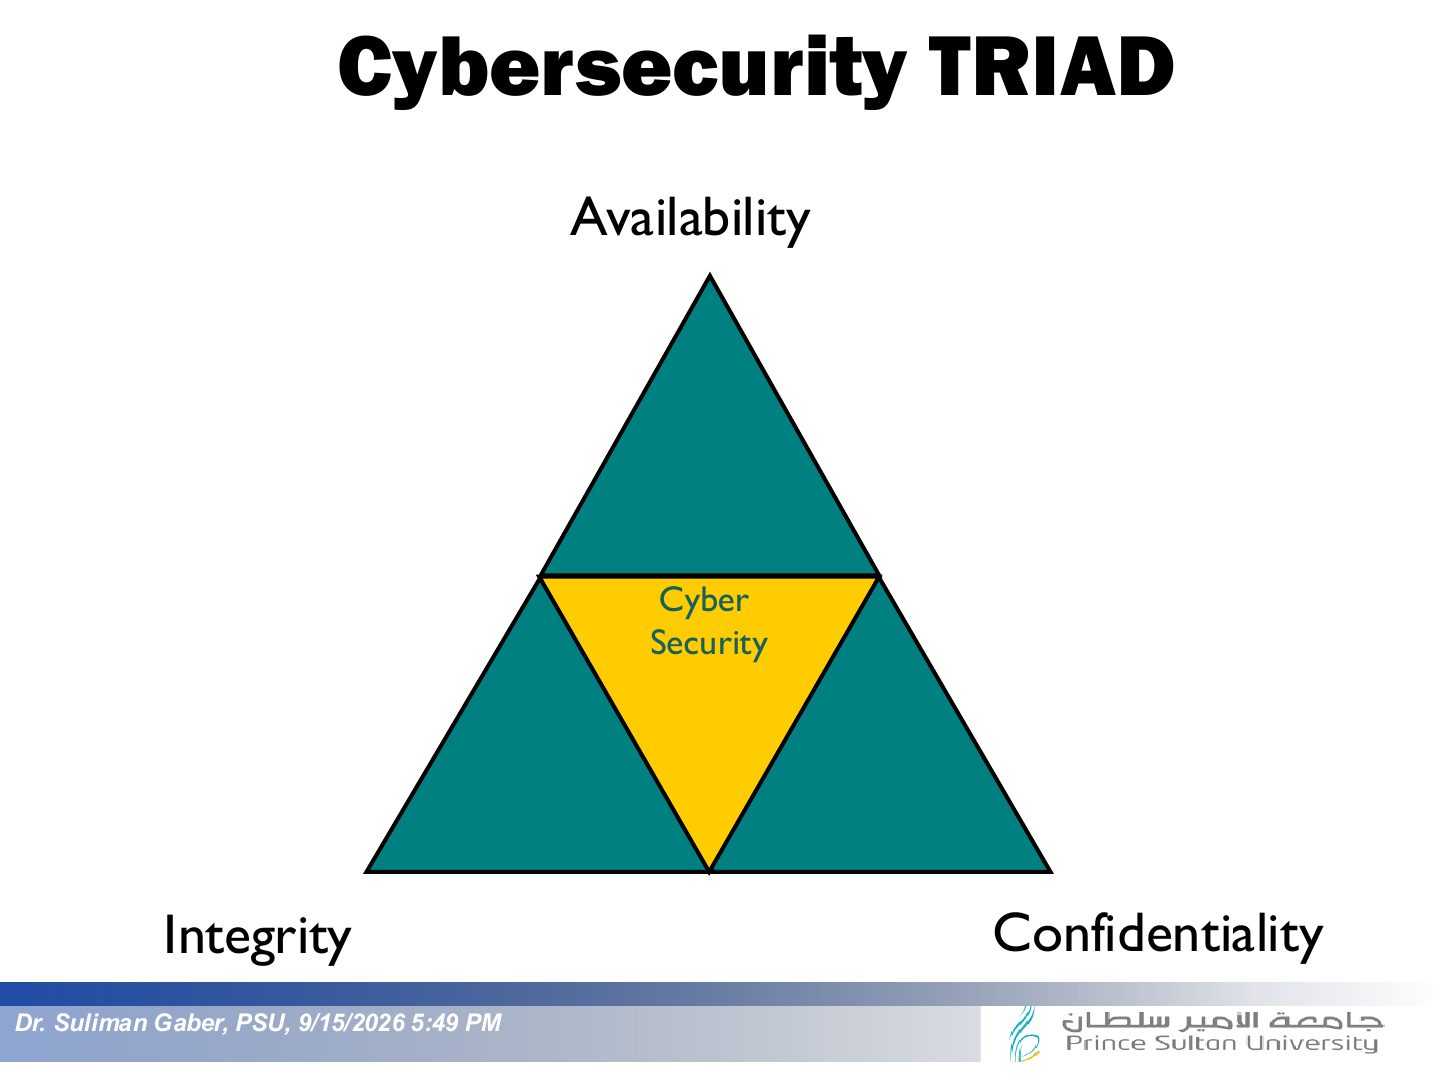
Notes
CIA triad: Confidentiality (only authorized people see it), Integrity (not altered improperly), Availability (there when needed).
Exam angle
only those supposed to access the data can
Making sure only those who are supposed to access the data can access it is:
Business-Driven Security
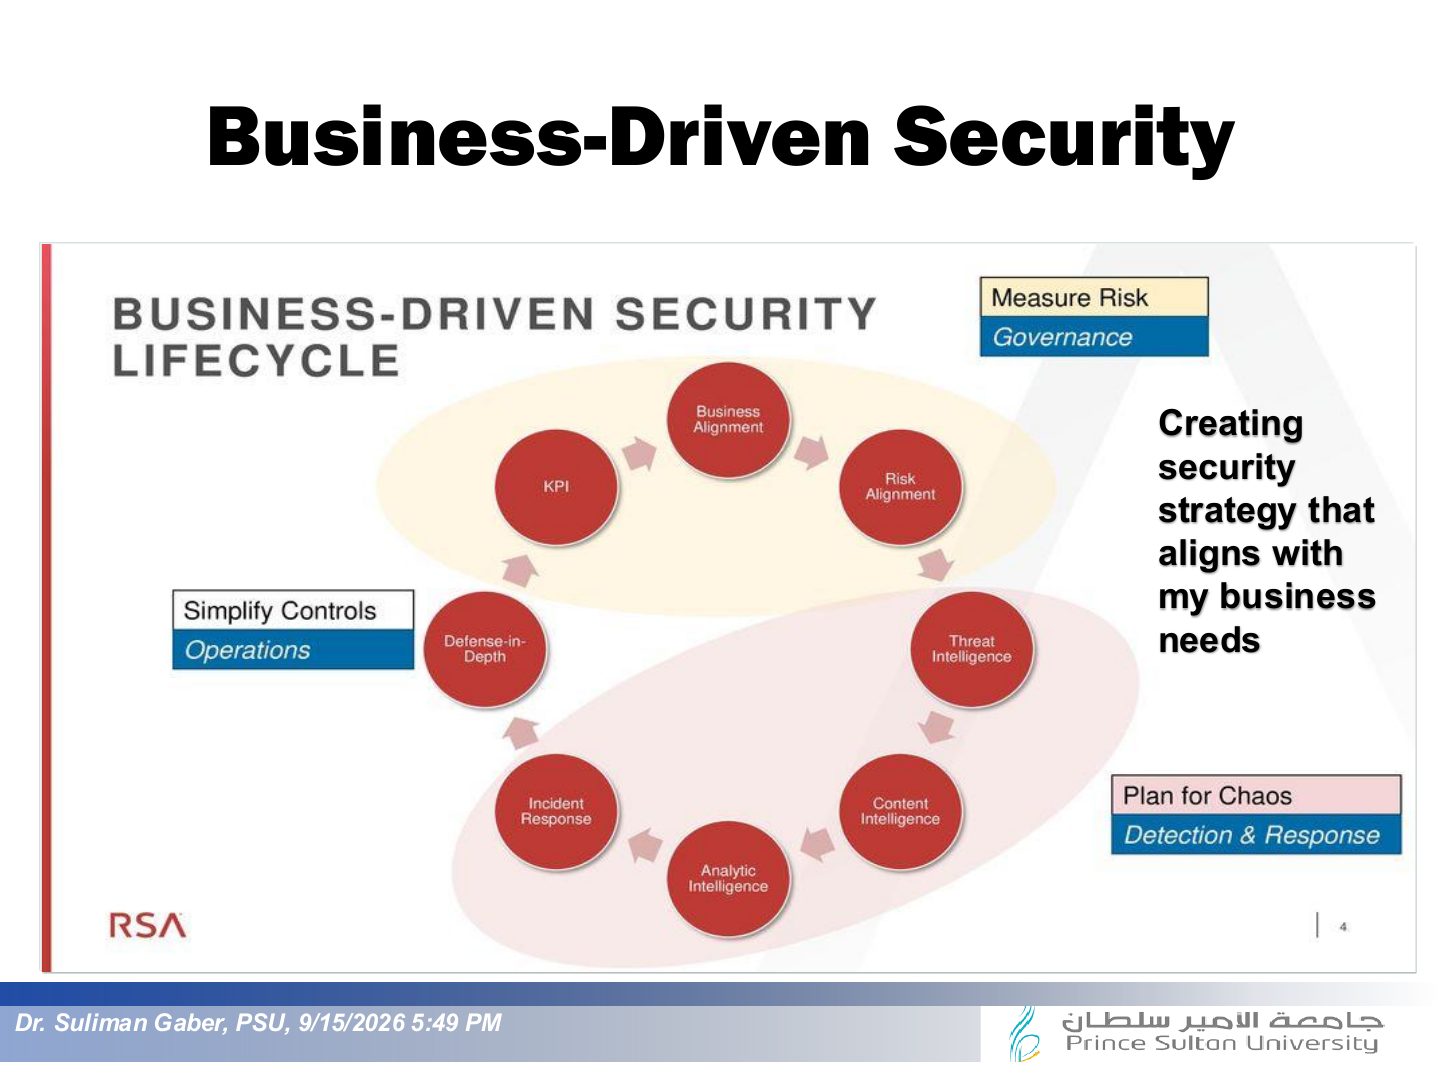
Notes
Business-driven security: start from business requirements and risk appetite, then choose controls.
Cybersecurity Management
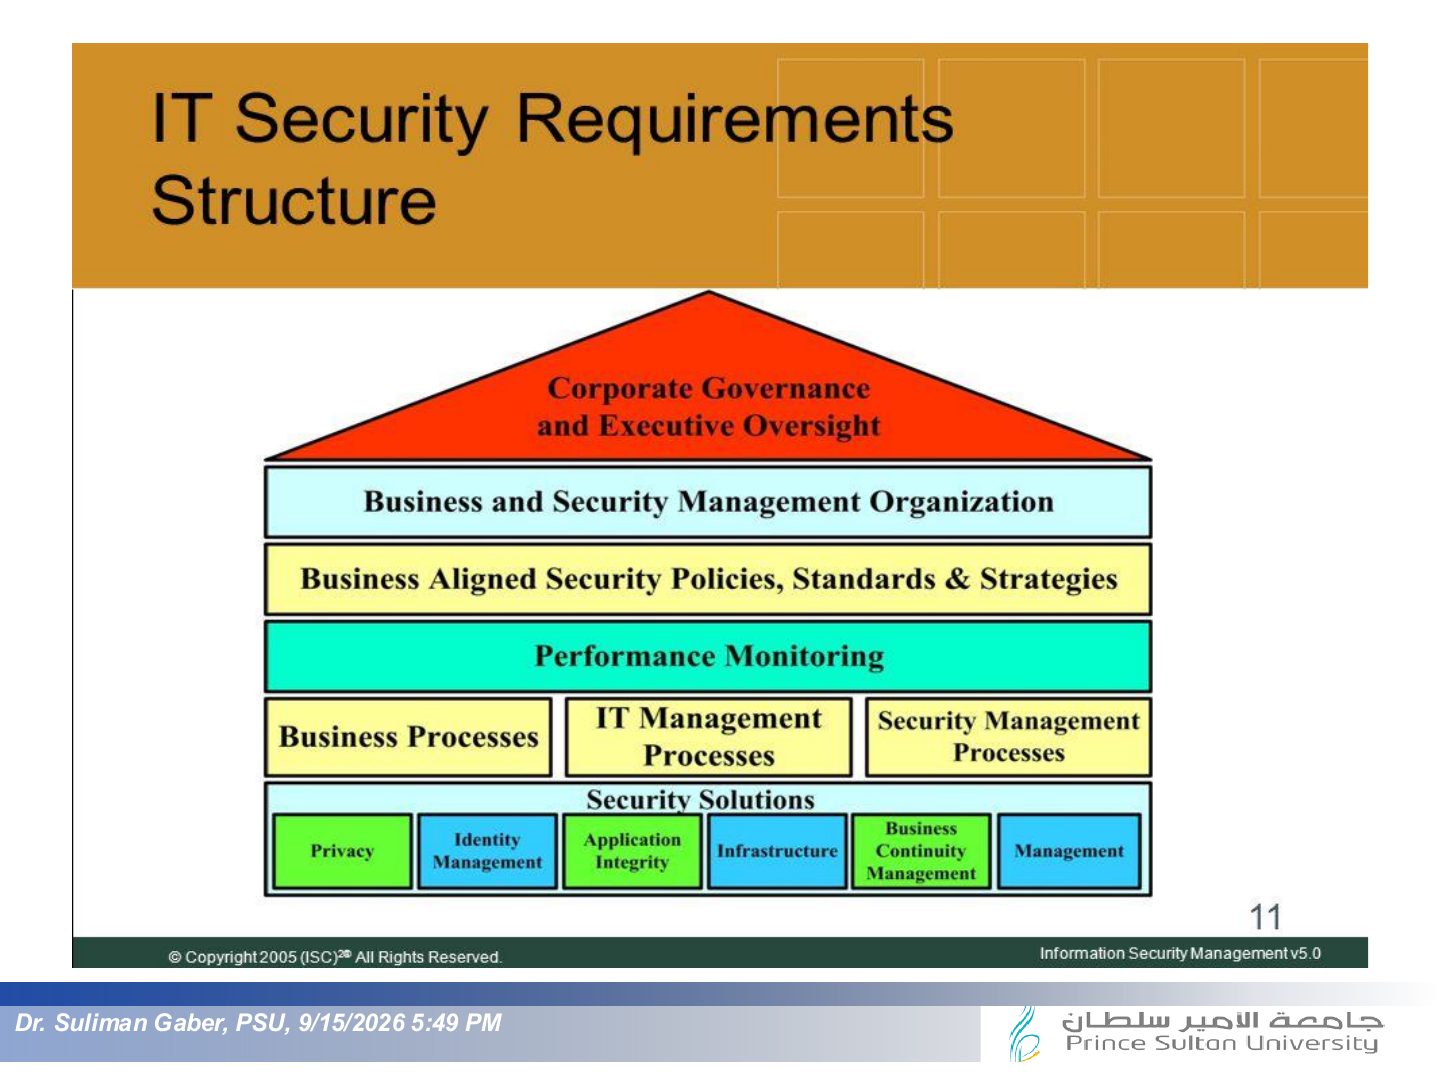
Notes
Management support is the most important factor for a successful security program.
Exam angle
the most important factor for security to succeed
The most important factor in ensuring security succeeds in an organization is:
Organizational & Business Requirements
Cybersecurity Security Solutions
Cybersecurity Management
Cybersecurity Management
Cybersecurity Governance
Notes
Governance: the board and executives set direction, accountability and oversight; management executes.
Exam angle
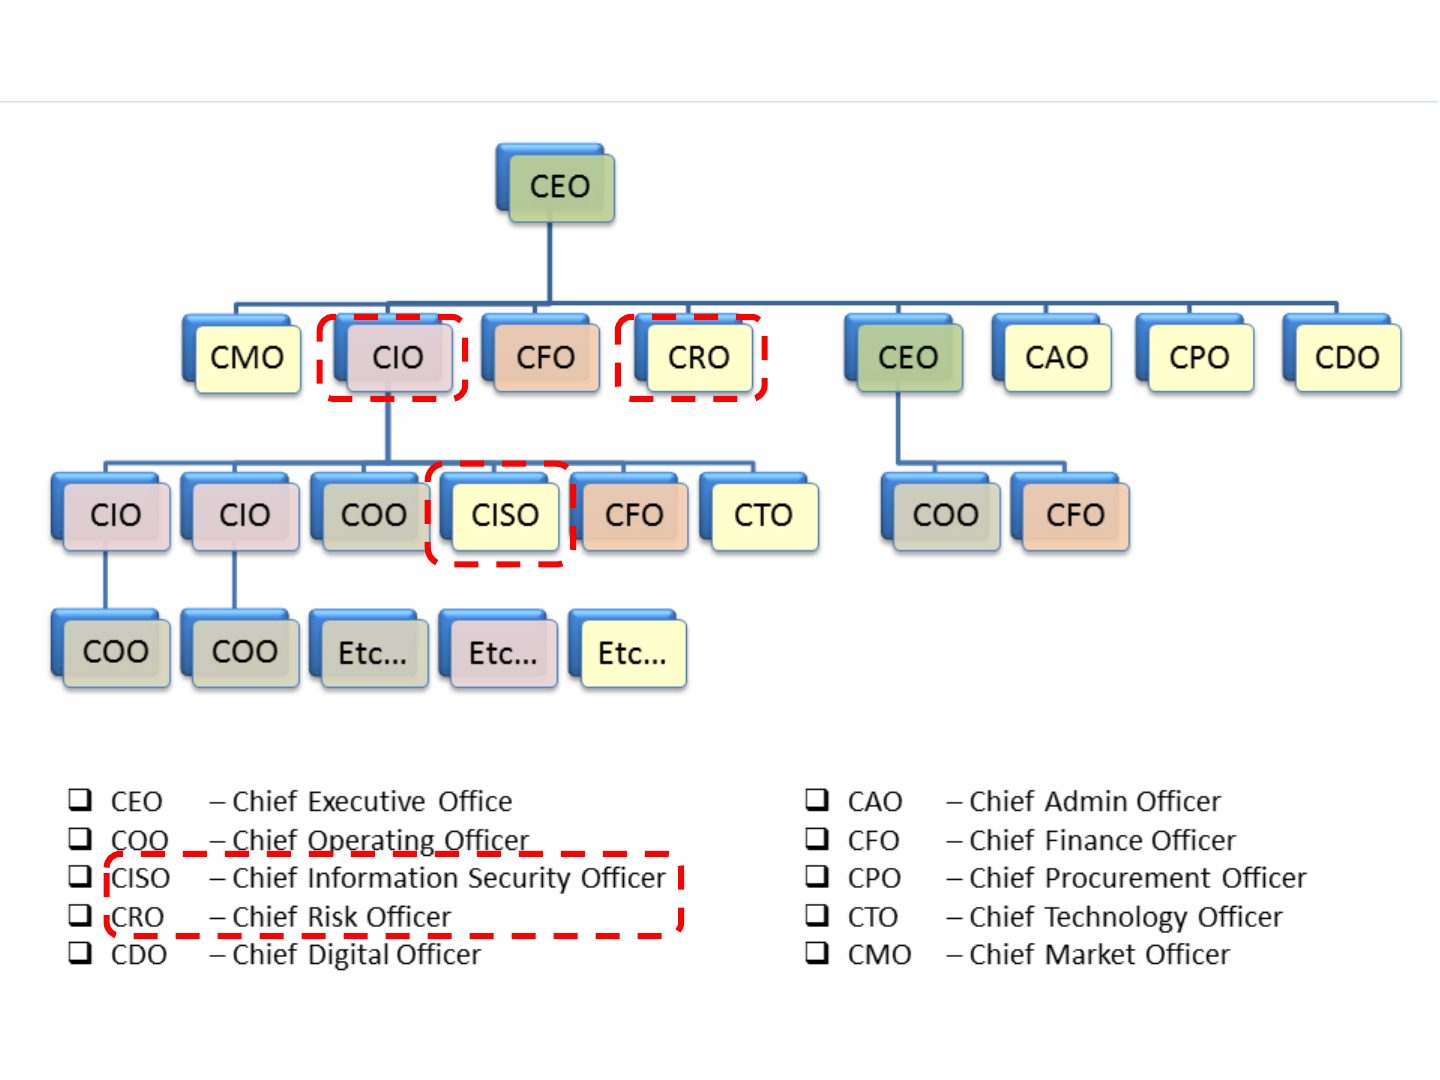
who should be involved in security risk management
Why should executives and IT/security teams communicate well?
Compare with the model answer
Executives own the business risk and the budget; IT/security understand the threats and controls. Without shared understanding, security spending won’t match business priorities and executives can’t make informed risk decisions.
Slide 20
Cybersecurity Governance
Notes
Data owner (a senior manager) decides the classification level of information; the custodian implements the protection.
Trap Owner DECIDES classification; custodian (IT) IMPLEMENTS controls; auditors MEASURE effectiveness.
Exam angle
who decides the classification level
Related question: the person in charge of a data domain
Who has primary responsibility for determining the classification level of information?
Who should measure the effectiveness of information-security controls?
Security Blueprints
Policy Overview
Notes
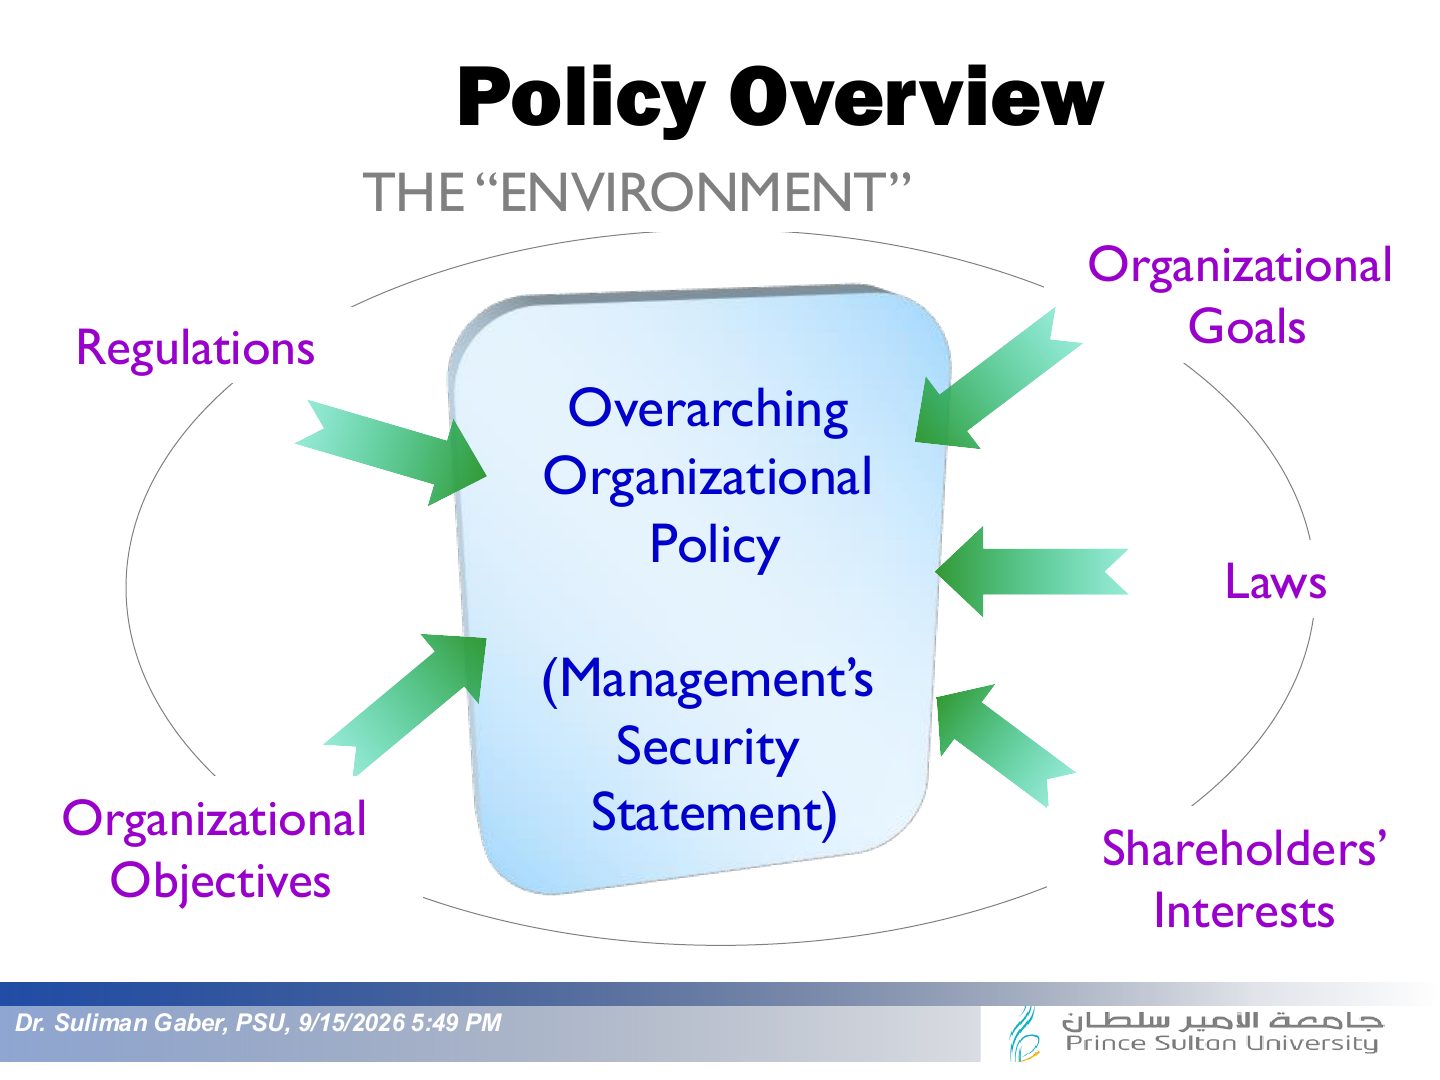
Policies: high-level management statements of what must be protected and why (mandatory, technology-neutral).
Exam angle
what security policies are
Security policies are best described as:
Policy overview
Security Statement Example
Policy Infrastructure
Notes
Hierarchy: policy (why) → standards (mandatory what) → procedures (step-by-step how) → baselines (minimum level) → guidelines (optional advice).
Memory trick Policy = WHY, Standard = WHAT (mandatory), Procedure = HOW, Baseline = MINIMUM, Guideline = SHOULD.
Exam angle
Detailed step-by-step instructions for a task are:
Recommended but optional actions are:
Examples of Functional Policies
Notes
Data classification groups data by sensitivity (e.g. public, internal, confidential, secret) so each level gets suitable controls.
Internet usage policy sample
Policy Implementation
Standards and procedure
Security Baselines
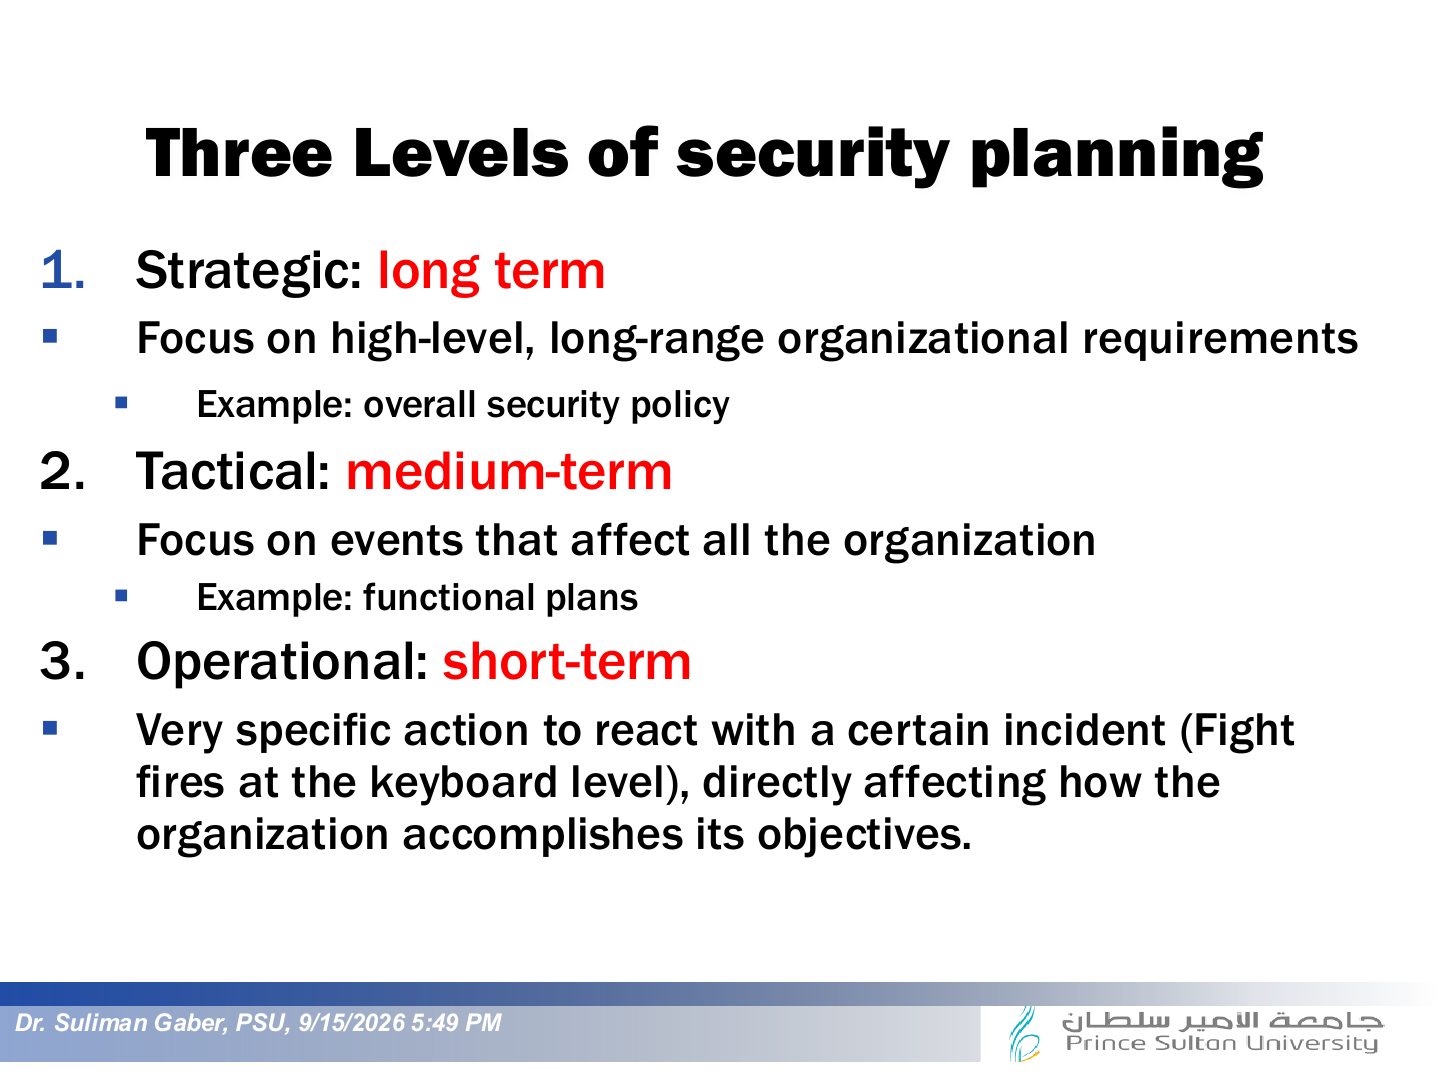
Three Levels of security planning
Notes
Planning horizons: strategic (long term, 3–5 years), tactical (mid term, 6 months–1 year or more), operational (short term, day to day to ~6 months).
Exam angle
Renee’s one-to-six-month plan
A short-term security plan with a one- to six-month horizon is:
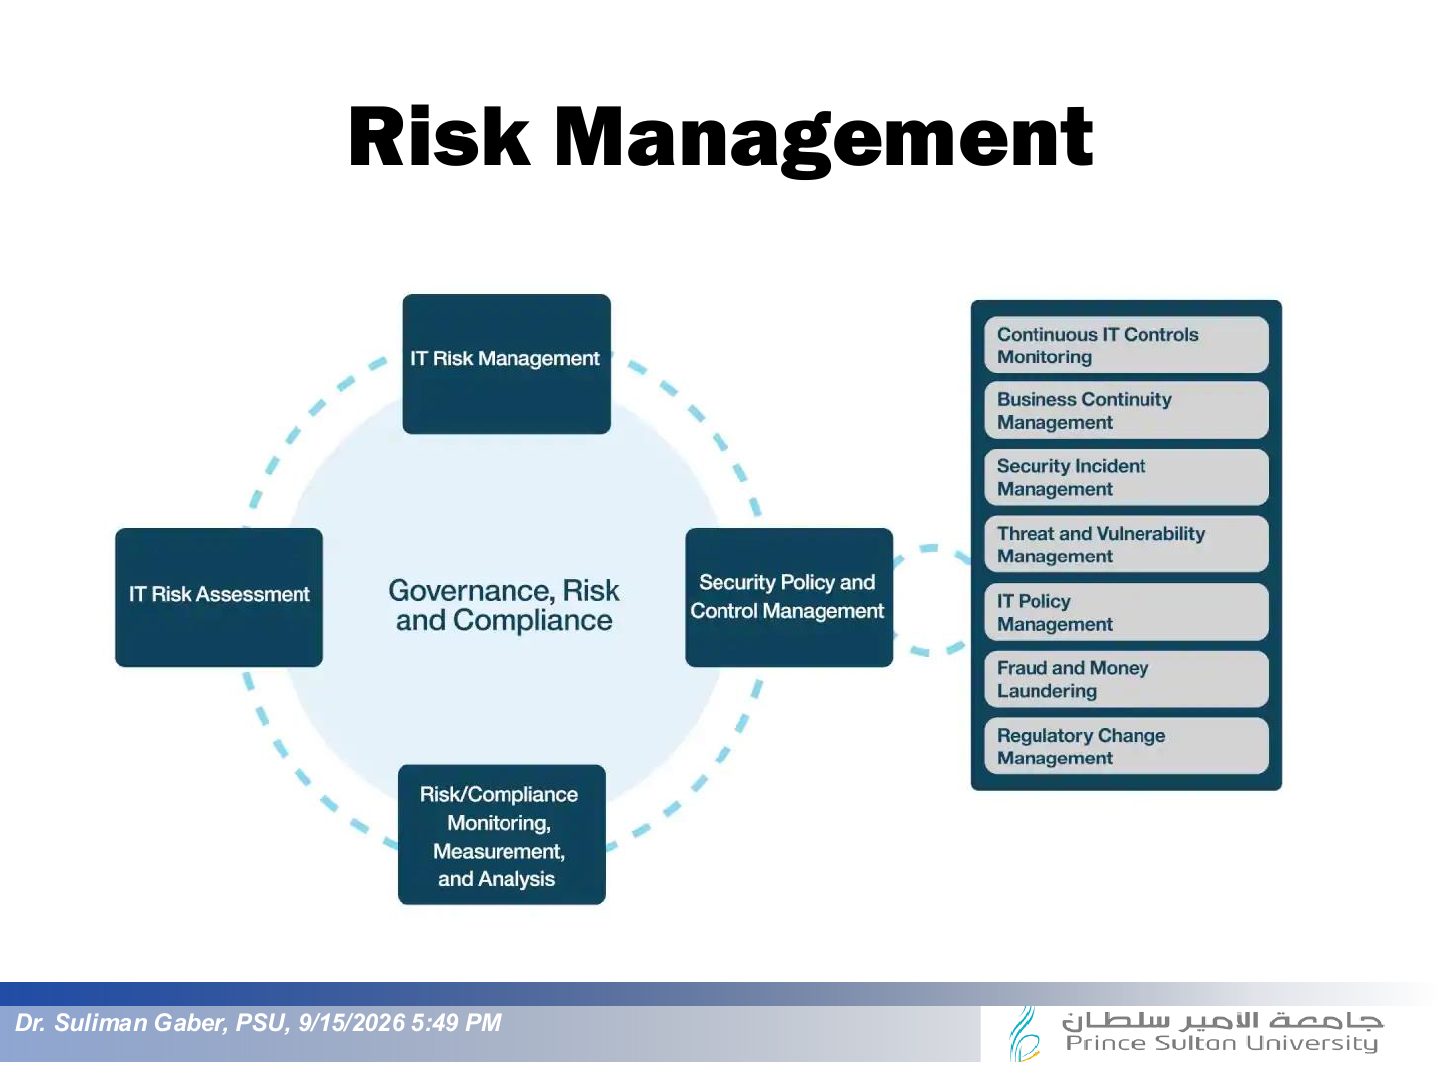
Risk Management
Notes
Functionality = what a security mechanism does; assurance = the confidence that it does it correctly.
Exam angle
functionality vs. assurance
Security functionality defines what a mechanism does; assurance defines:
Slide 34