MCQ · exact privileges, no additions = least privilege
Security Design Models and Capabilities
Security architecture principles (security by design, least privilege, default deny, separation of duties, zero trust, micro-segmentation…), architecture flaws (covert channels, maintenance hooks), process isolation and protection rings, and the security models: TCB, access control matrix, take-grant, Bell-LaPadula, Biba. Both Final 221 papers asked about least privilege, isolation, take-grant and Bell-LaPadula.
How to read this page
Every original slide is shown unchanged. Yellow marks on a slide point to a numbered note: hover or tap a mark to jump to its note, and hover a note to see its marks. Questions tagged Past exam appeared on a real paper; Prediction questions are likely angles, not confirmed. Pick an answer to each question: a wrong pick tells you why it is wrong, so you can try again.
All 31 slides
- 1 Security Design Models and Capabilities
- 2 Slide 2
- 3 Security Architecture principles
- 4 Why Security Design Matters
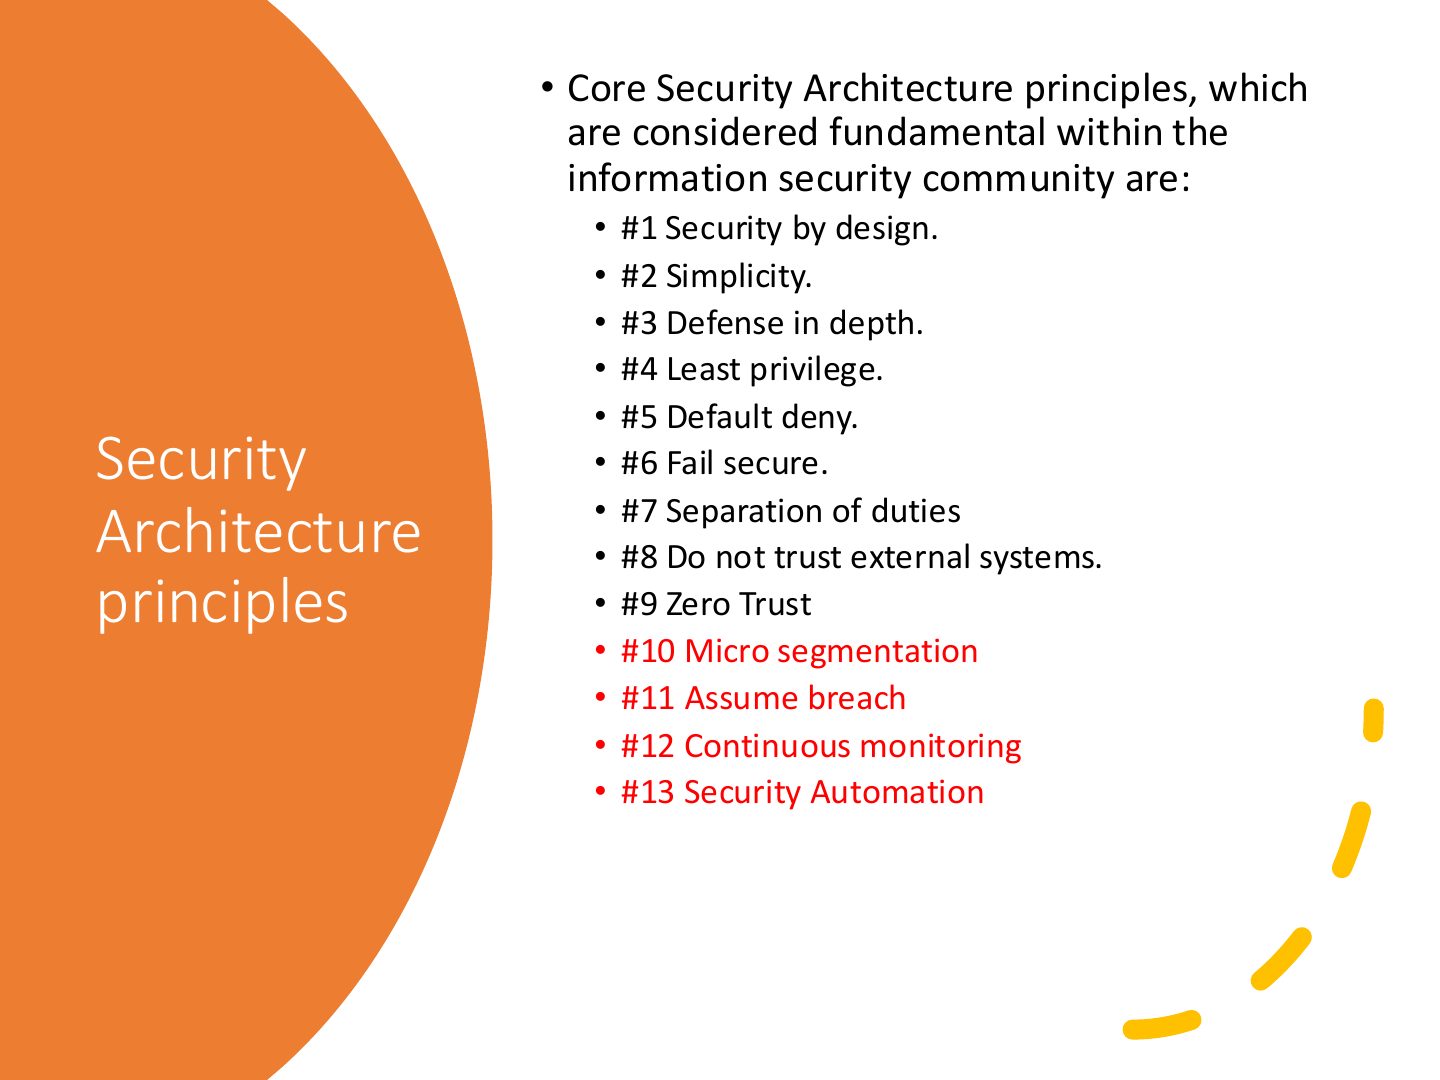
- 5 • Core Security Architecture principles, which are considered fundamental within the information security community are:
- 6 Security Architecture principles
- 7 Security Architecture principles
- 8 Security Architecture principles
- 9 Security Architecture principles
- 10 Security Architecture principles
- 11 Security Architecture principles
- 12 Security Architecture principles
- 13 Security Architecture principles
- 14 Security Architecture principles
- 15 Security Architecture principles
- 16 Security Architecture principles
- 17 Common Architecture Flaws and Security Issues 1/2
- 18 Common Architecture Flaws and Security Issues 1/2
- 19 Techniques for Ensuring Confidentiality, Integrity, and Availability
- 20 Techniques for Ensuring Confidentiality, Integrity, and Availability
- 21 Techniques for Ensuring Confidentiality, Integrity, and Availability
- 22 Techniques for Ensuring Confidentiality, Integrity, and Availability
- 23 Techniques for Ensuring Confidentiality, Integrity, and Availability
- 24 Security Models
- 25 Security Models
- 26 Security Models
- 27 Access Control Matrix
- 28 Take-Grant Model
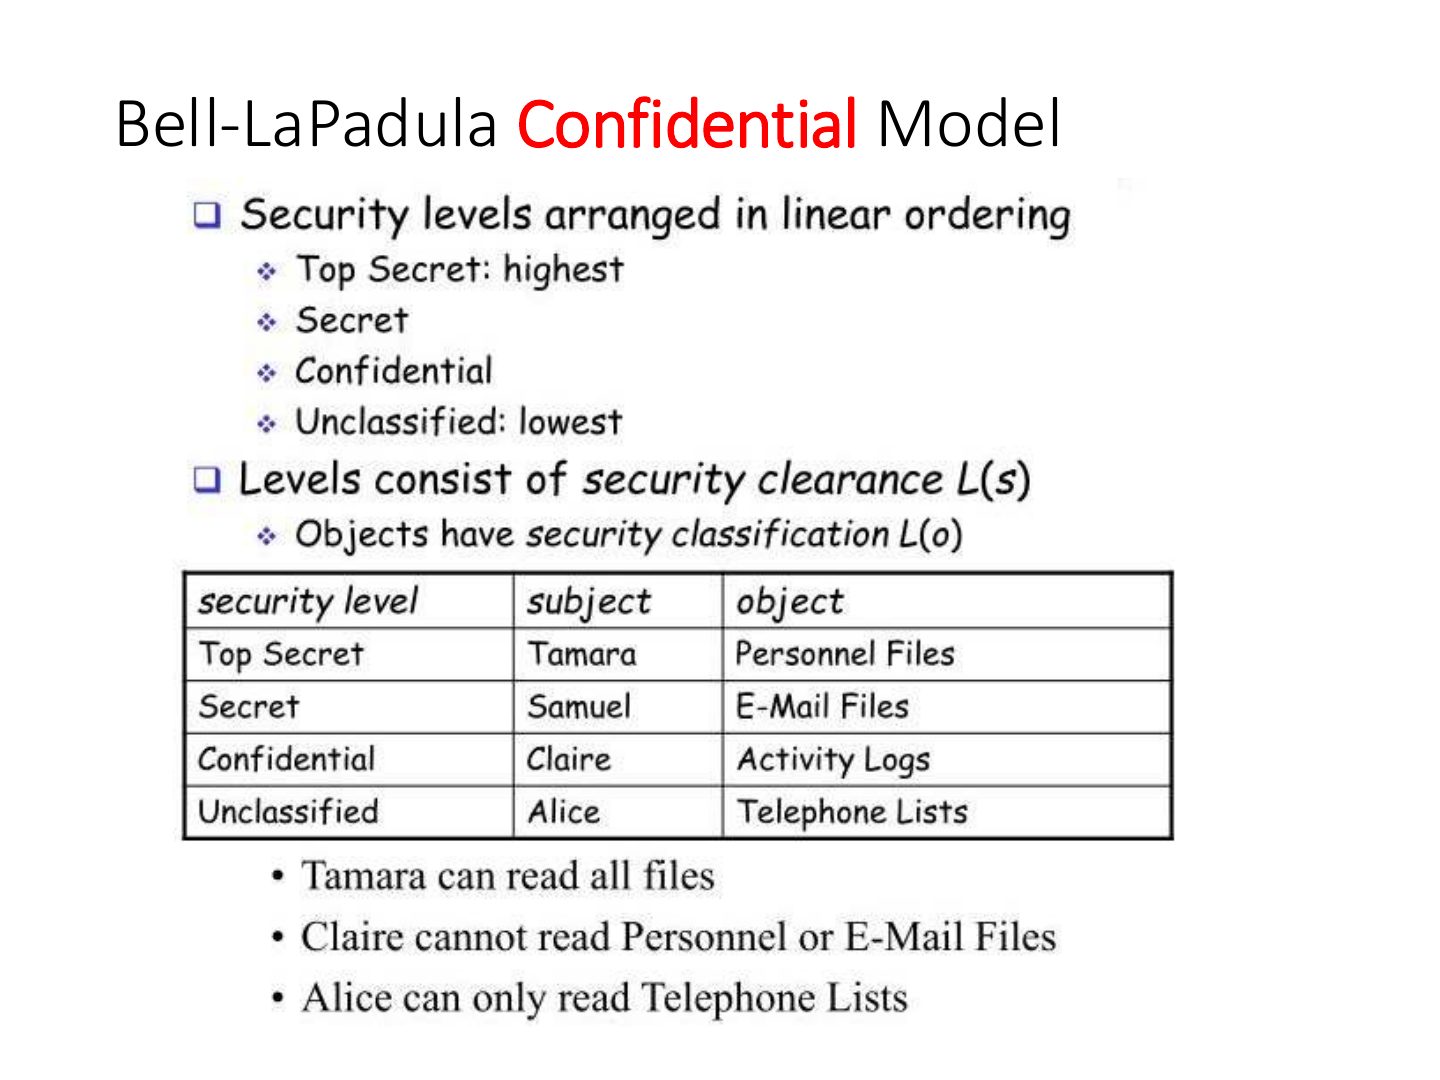
- 29 Bell-LaPadula Confidential Model
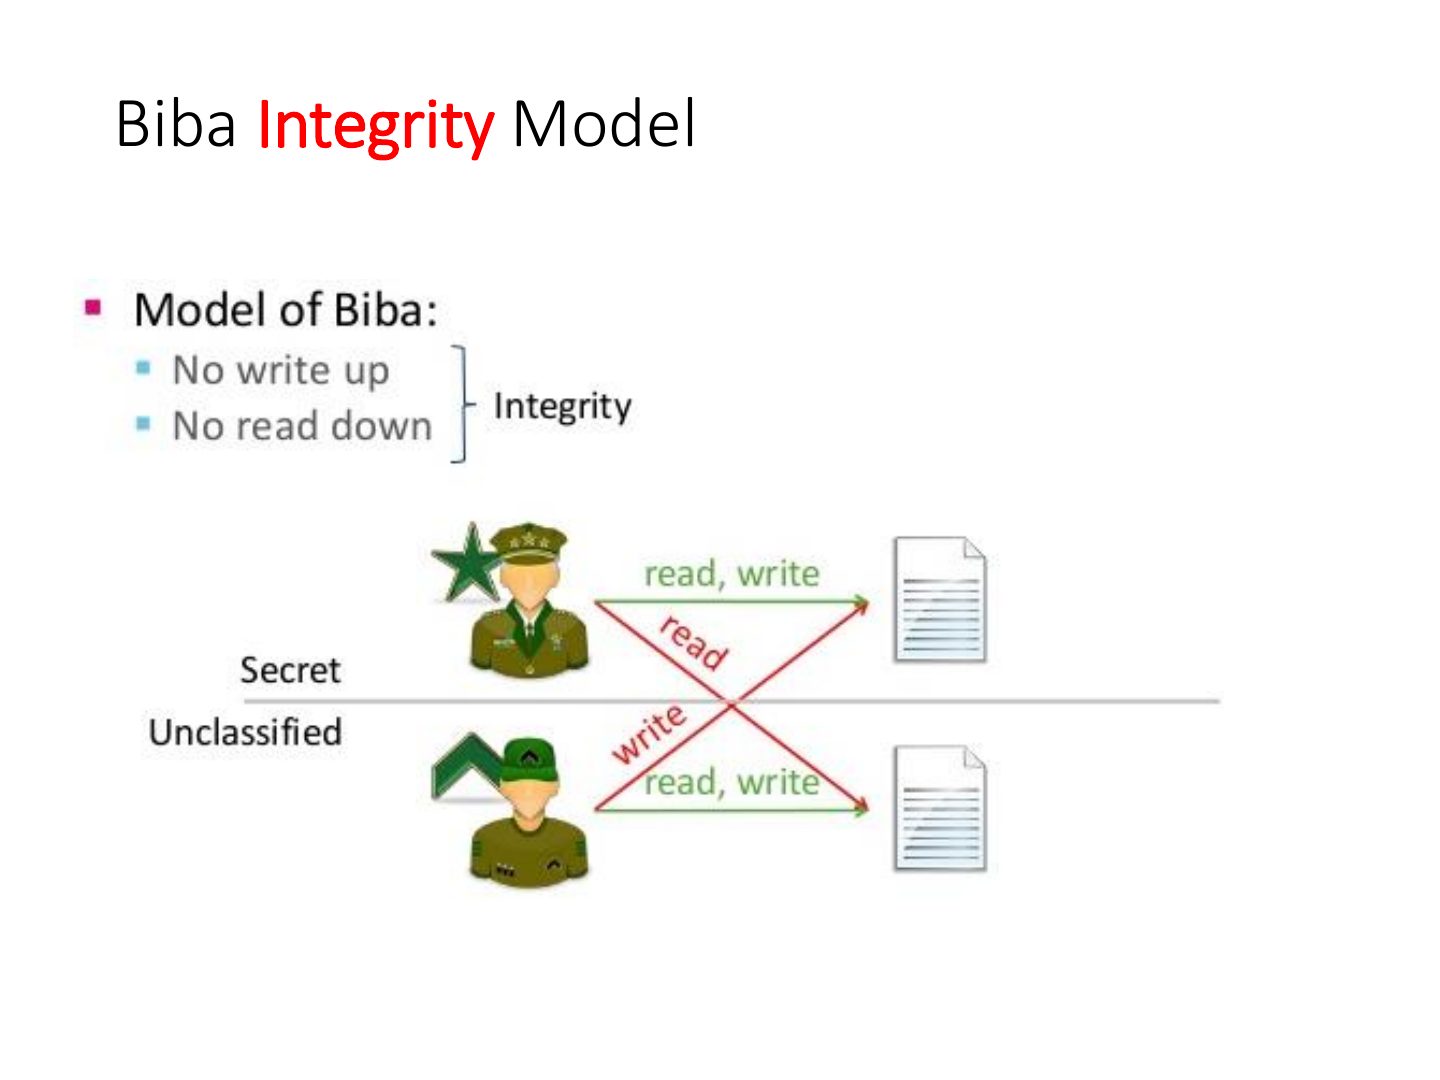
- 30 Biba Integrity Model
- 31 Slide 31
Security Design Models and Capabilities
Notes
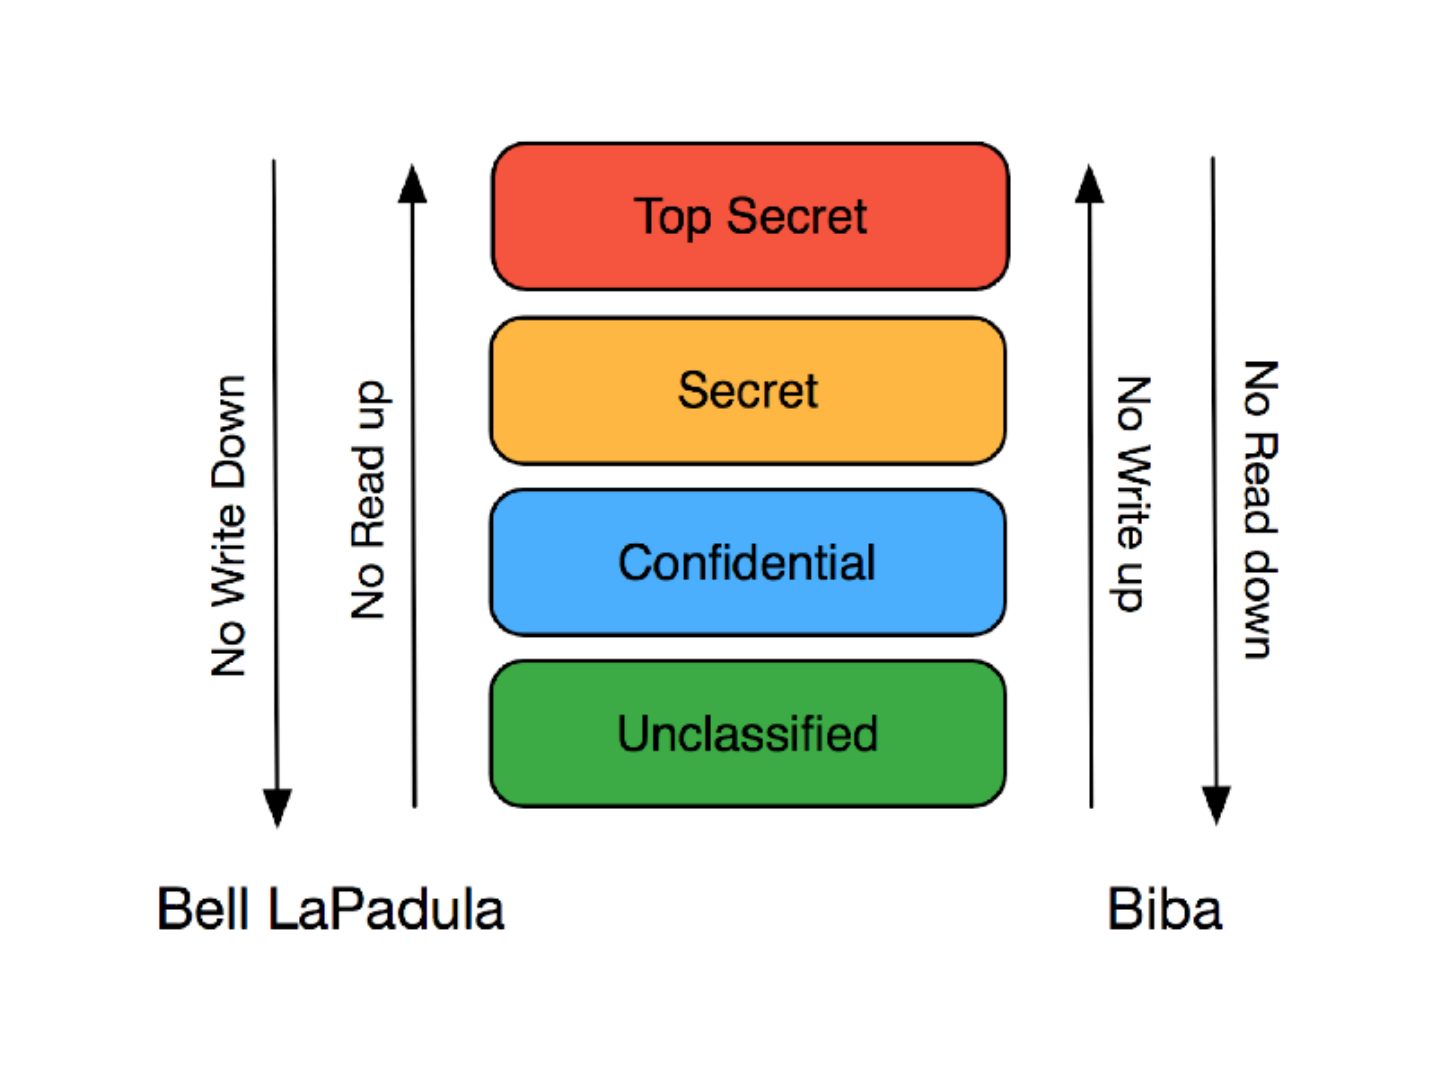
Tip Bell-LaPadula (CONFIDENTIALITY): no read up (simple), no write down (*-property). Biba (INTEGRITY): no read down, no write up. Mnemonic: BLP protects secrets from leaking down; Biba stops dirt flowing up.
Slide 2
Notes
Learning objectives.
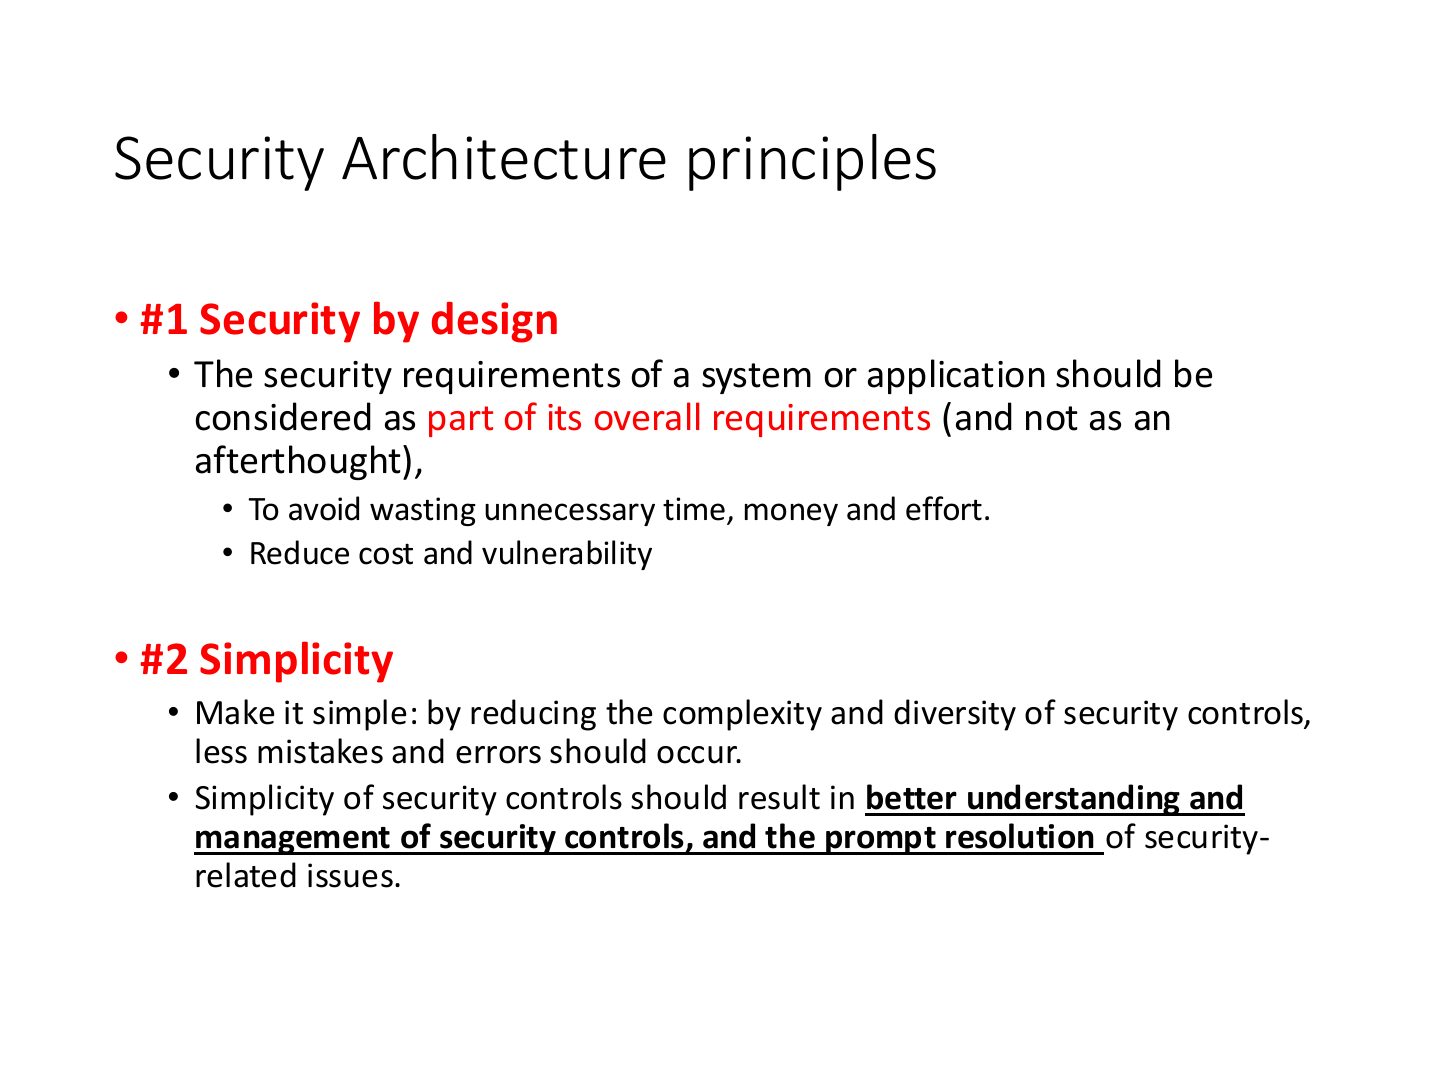
Security Architecture principles
Why Security Design Matters
• Core Security Architecture principles, which are considered fundamental within the information security community are:
Security Architecture principles
Security Architecture principles
Notes
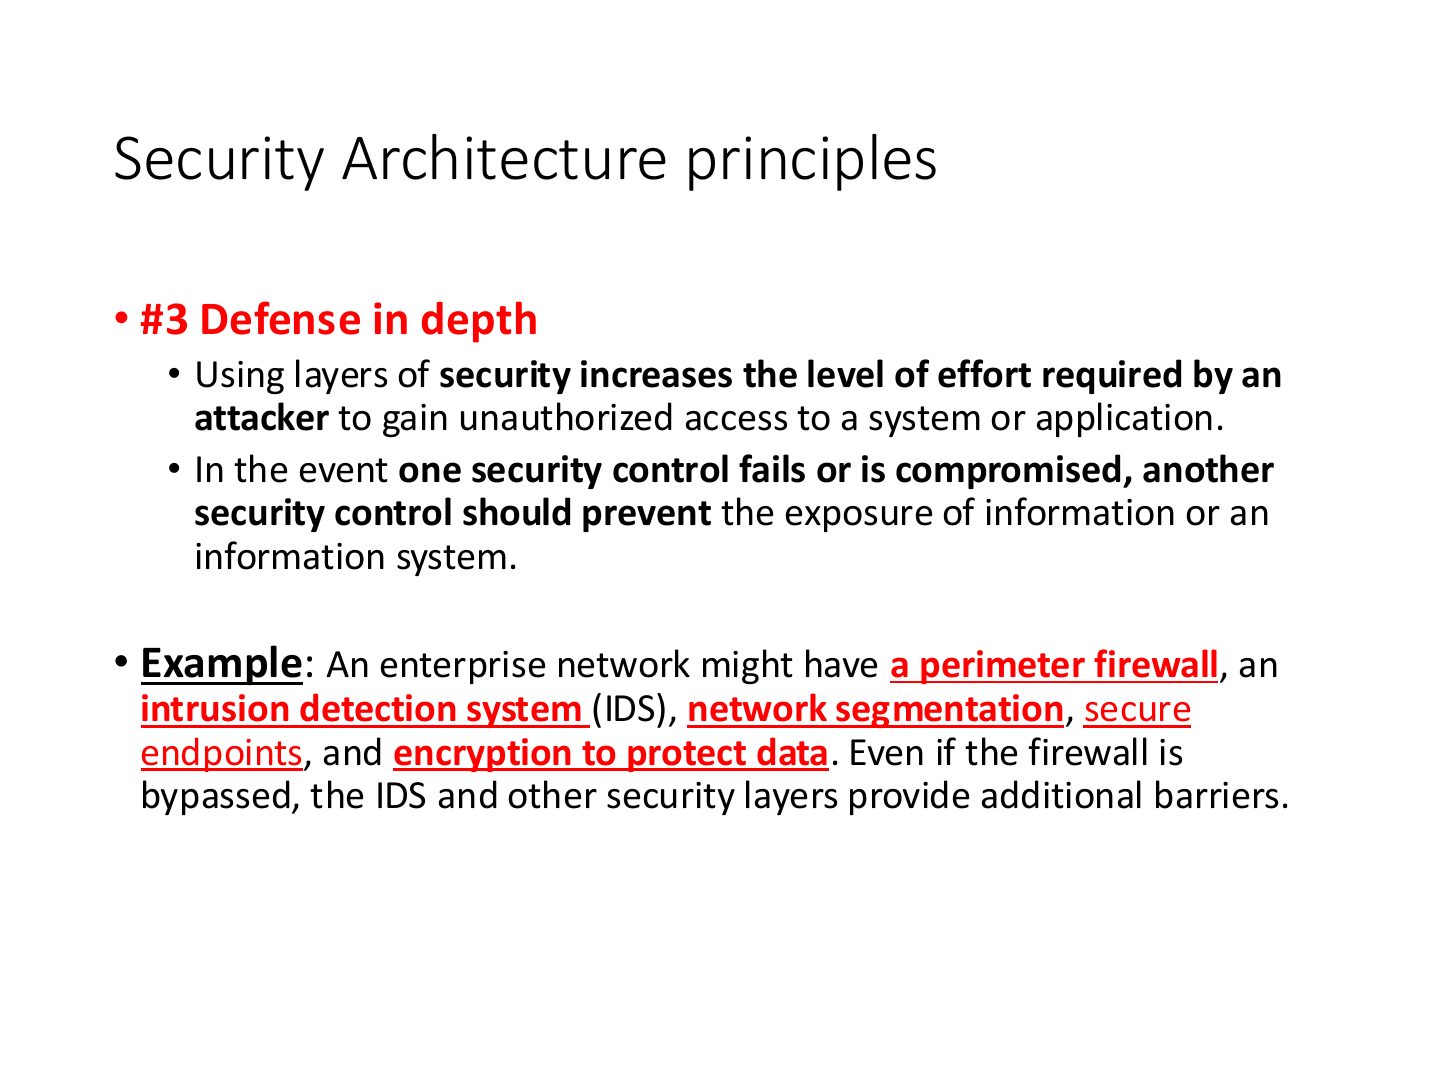
Seen again Ch 1, slide 9: Defence in depth
Security Architecture principles
Exam angle
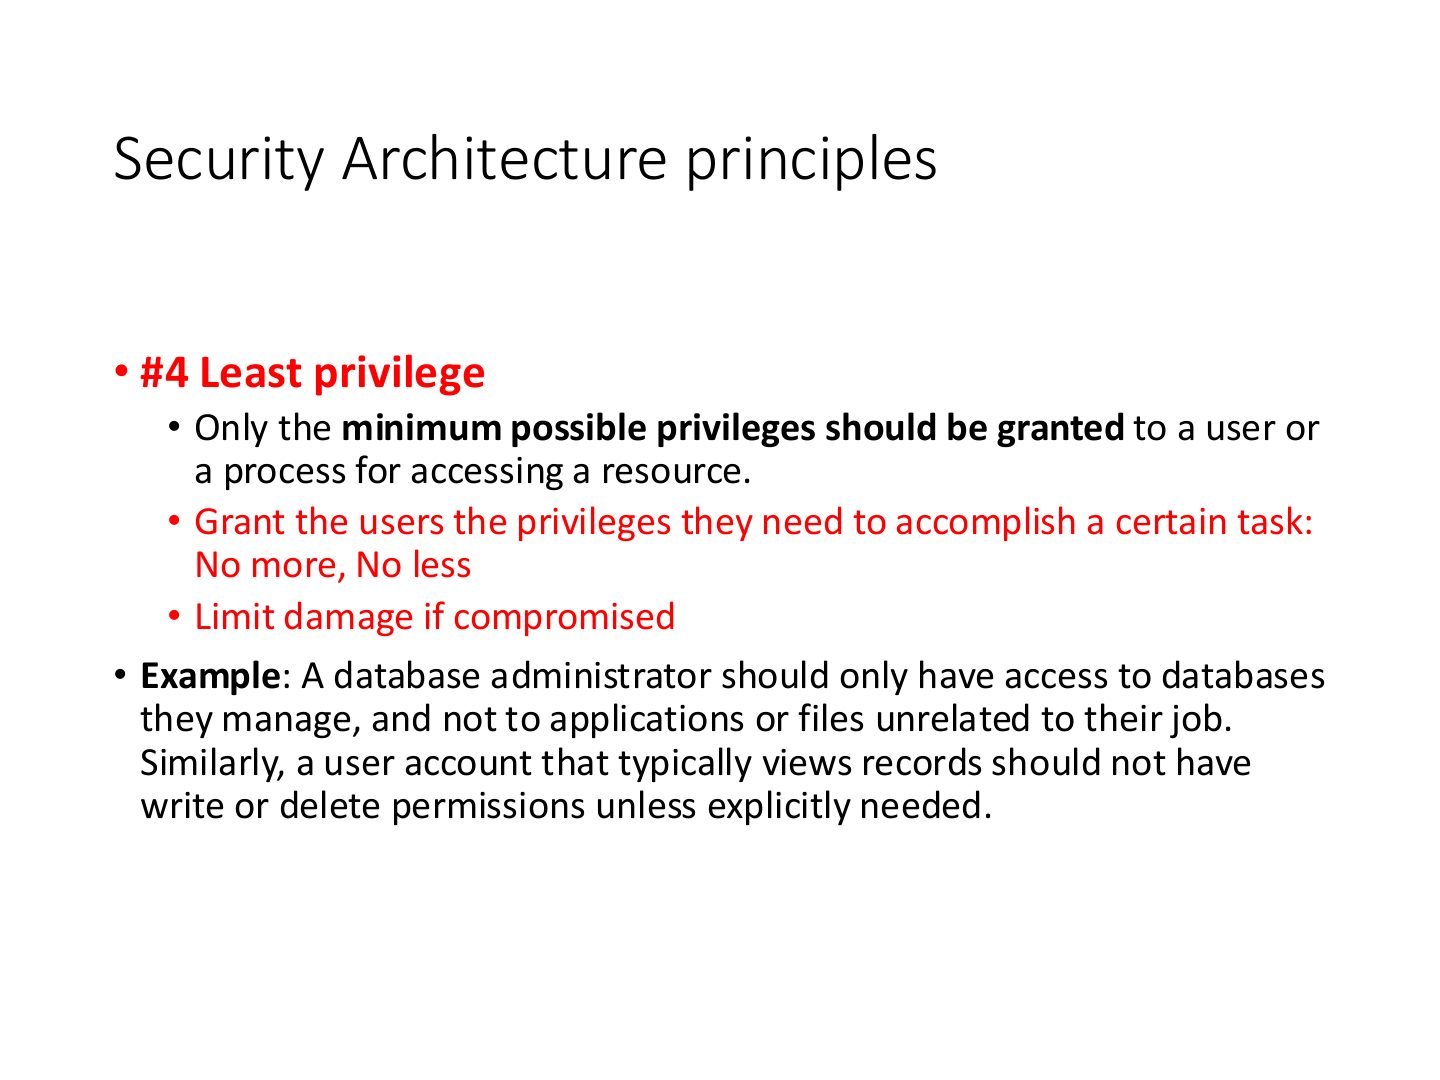
Granting users exactly the privileges they need for a task, nothing more, is:
- Final 221 A.
Security Architecture principles
Notes
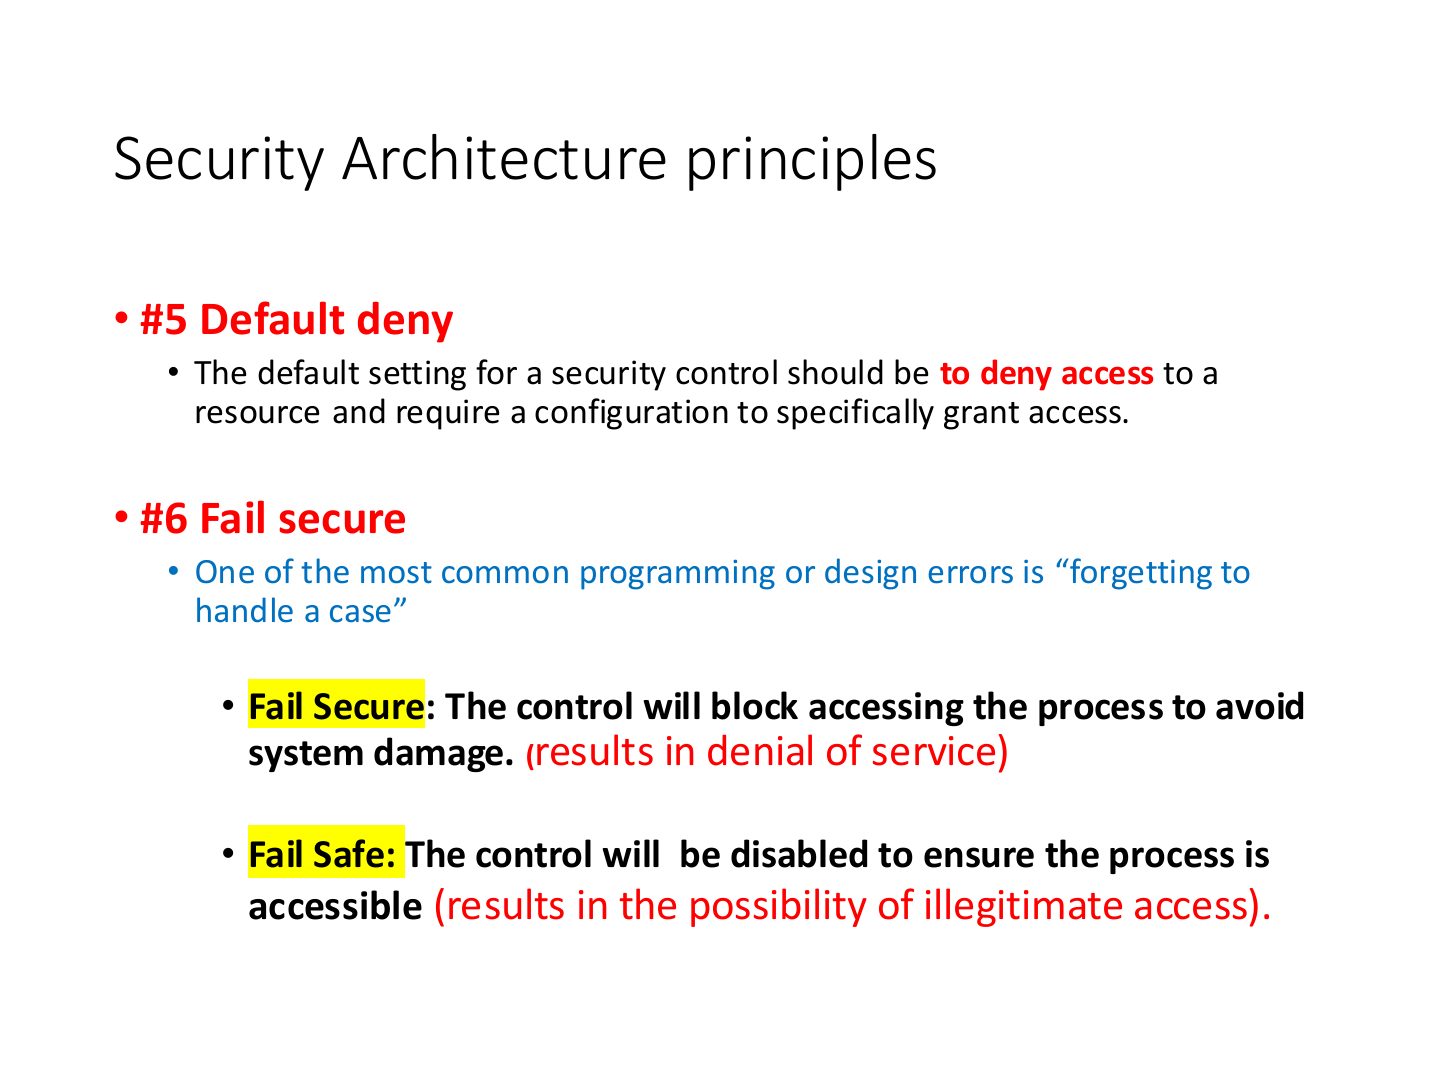
#5 Default deny: access is denied unless explicitly granted. #6 Fail securely.
Security Architecture principles
Notes
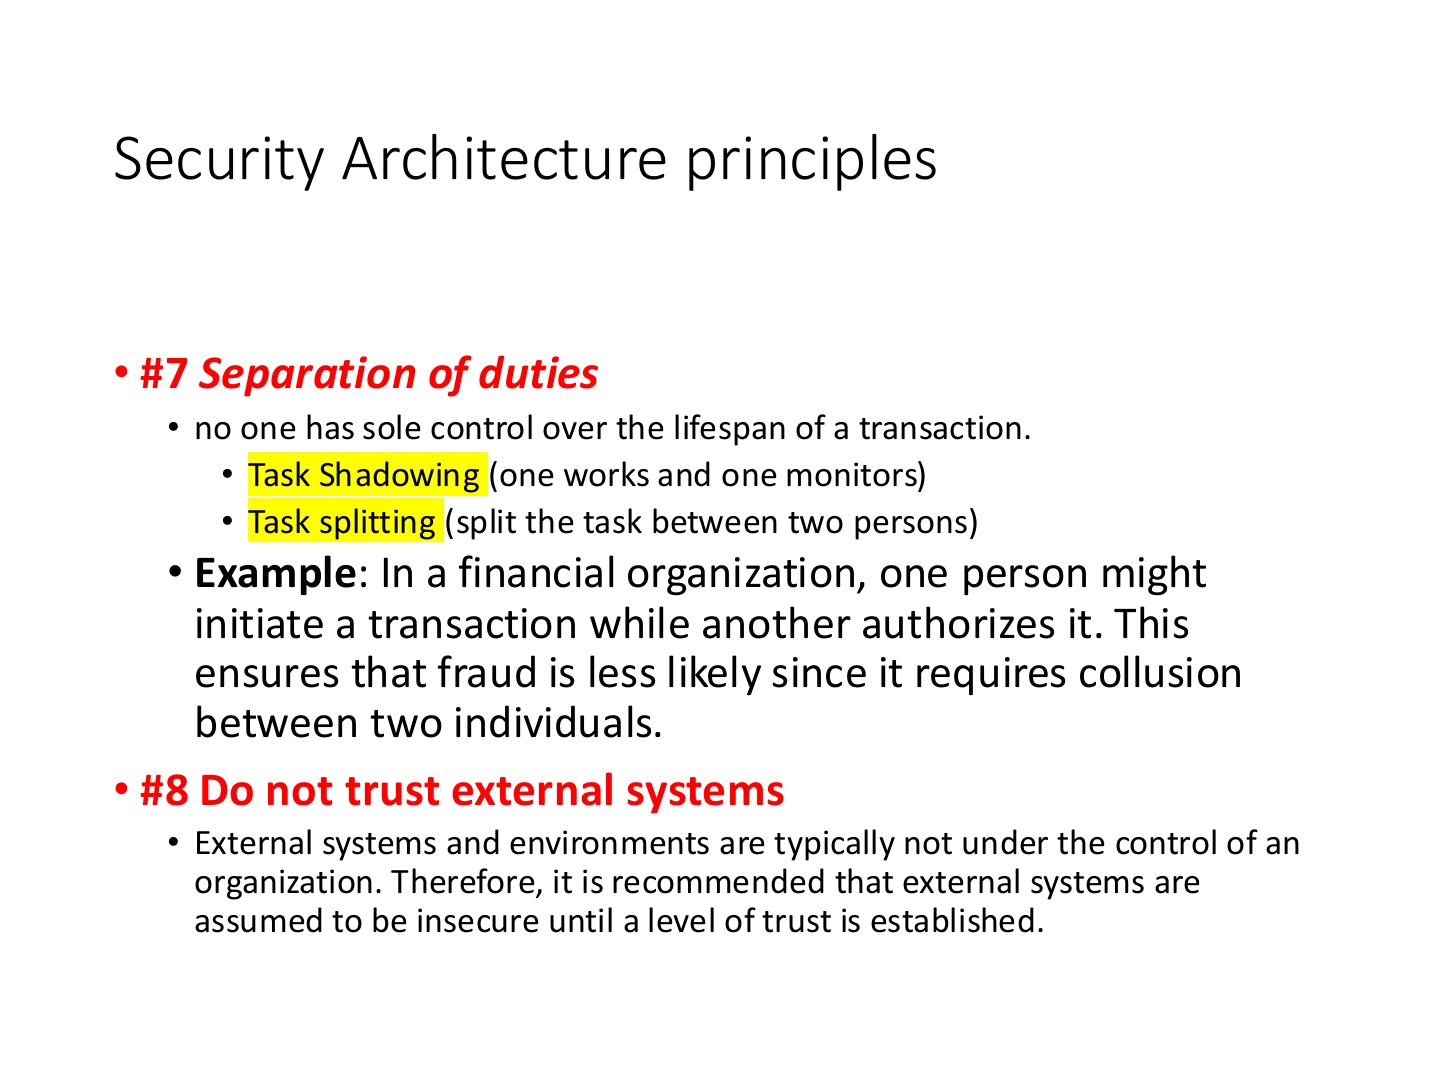
#7 Separation of duties: no single person controls a whole transaction (cashier needs a supervisor to refund).
Exam angle
Related question: match · supervisor approval for refunds
A cashier needs a supervisor’s approval to cancel a bill and refund. This applies:
Security Architecture principles
Exam angle
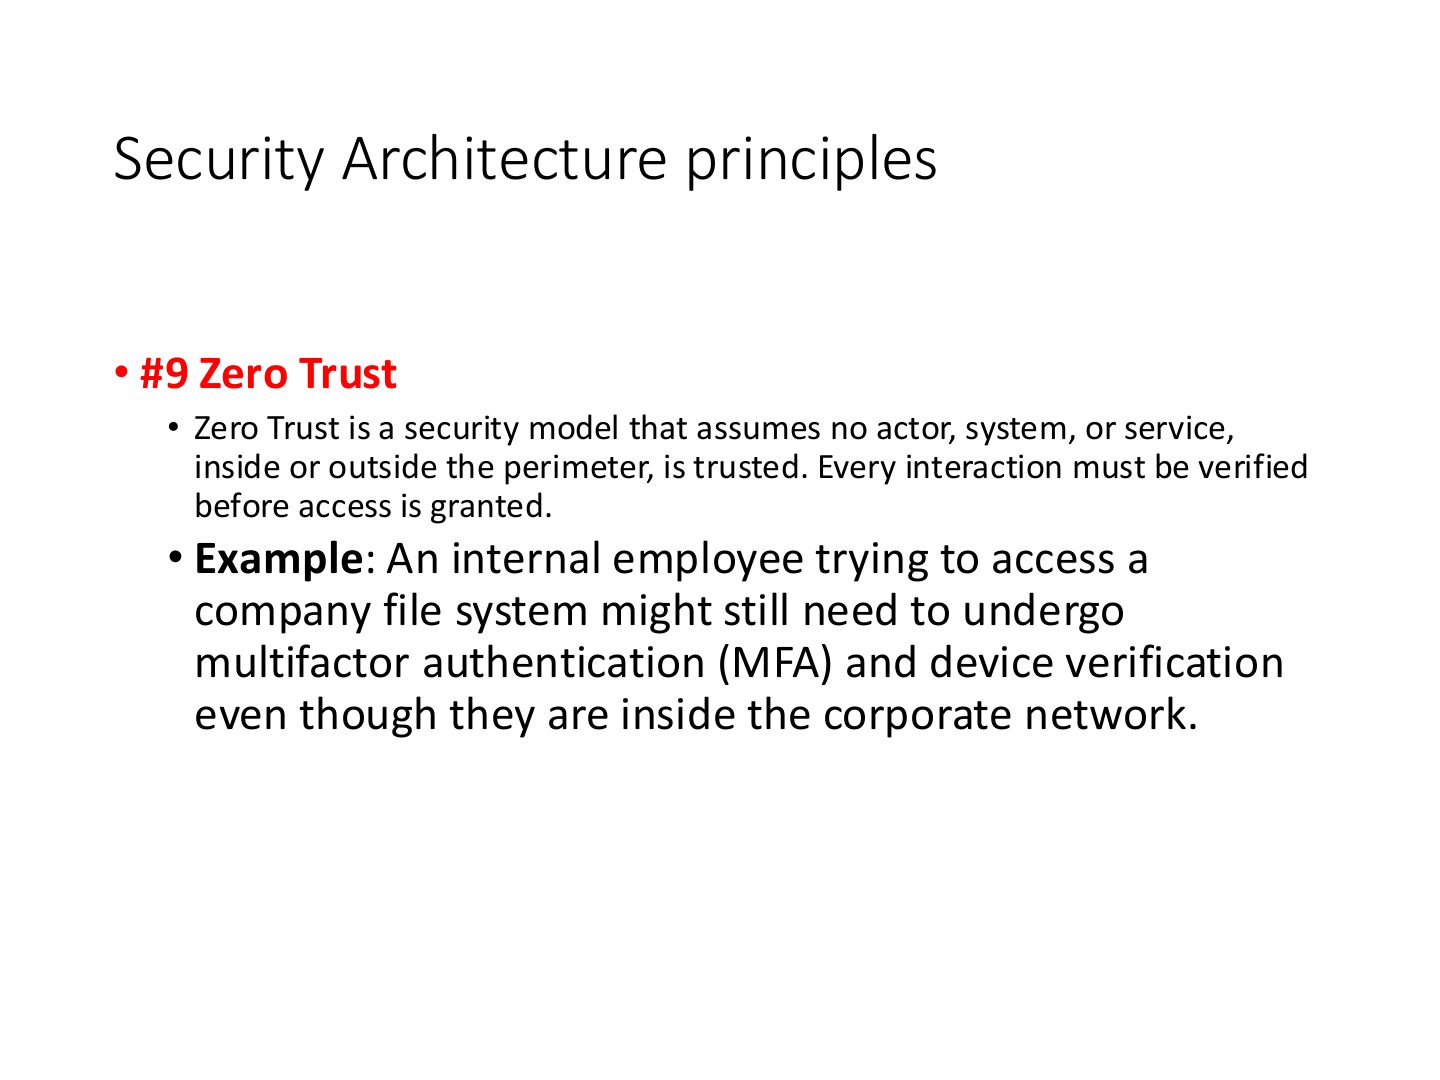
Which model assumes no user or device is trusted, even inside the network?
Security Architecture principles
Security Architecture principles
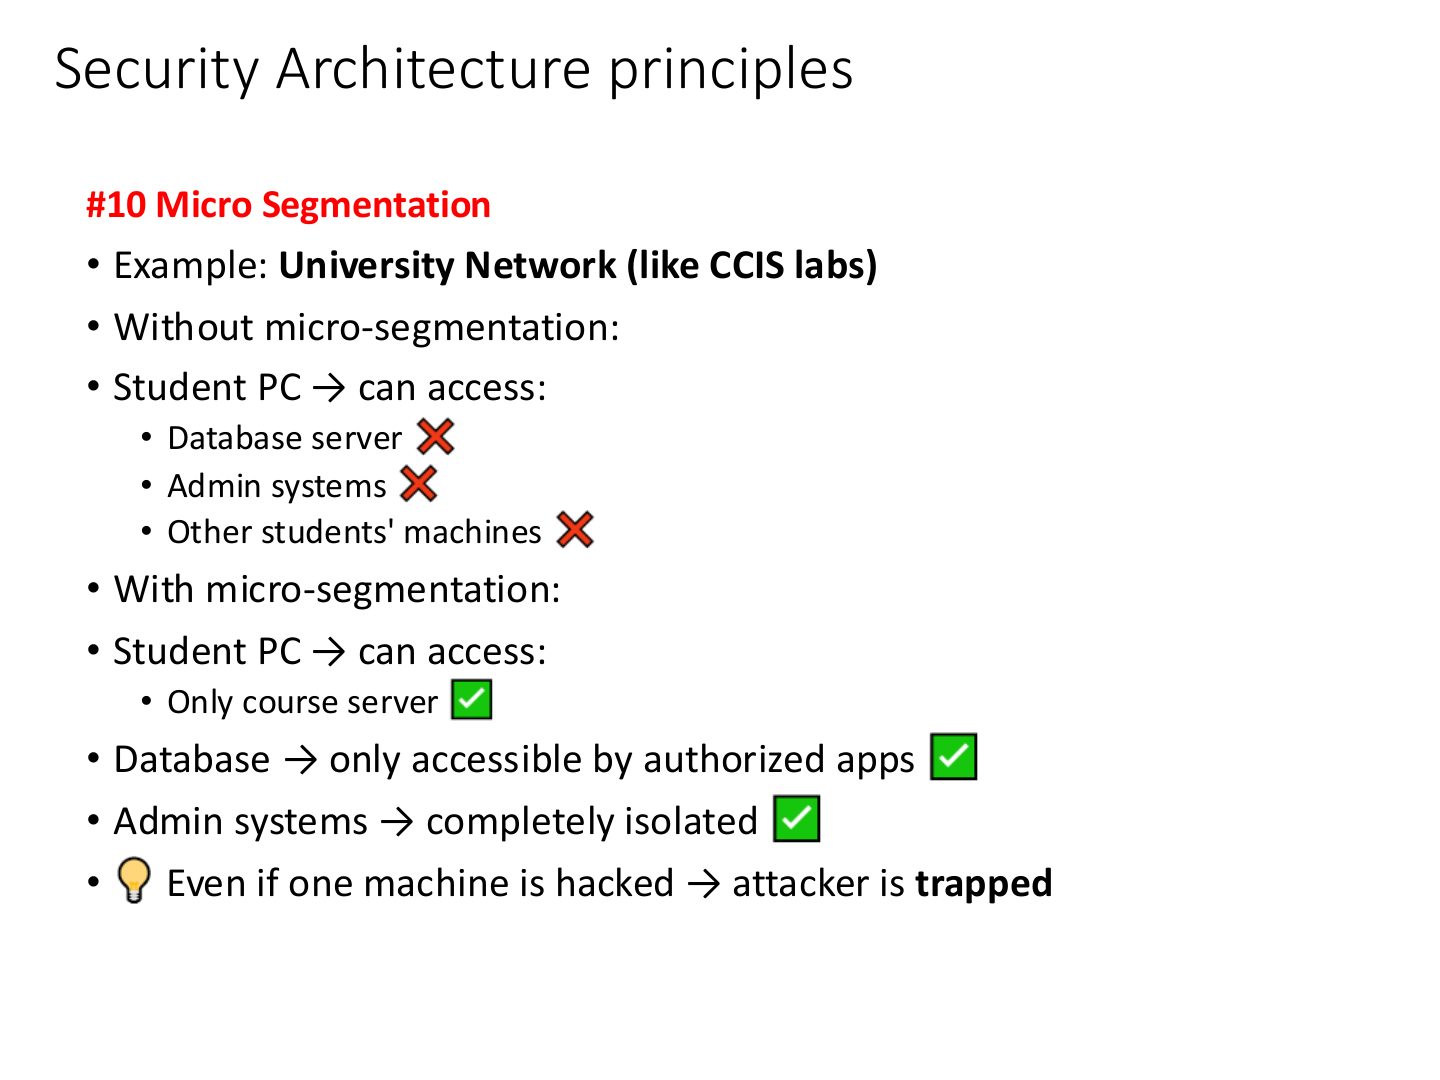
Security Architecture principles
Security Architecture principles
Security Architecture principles
Common Architecture Flaws and Security Issues 1/2
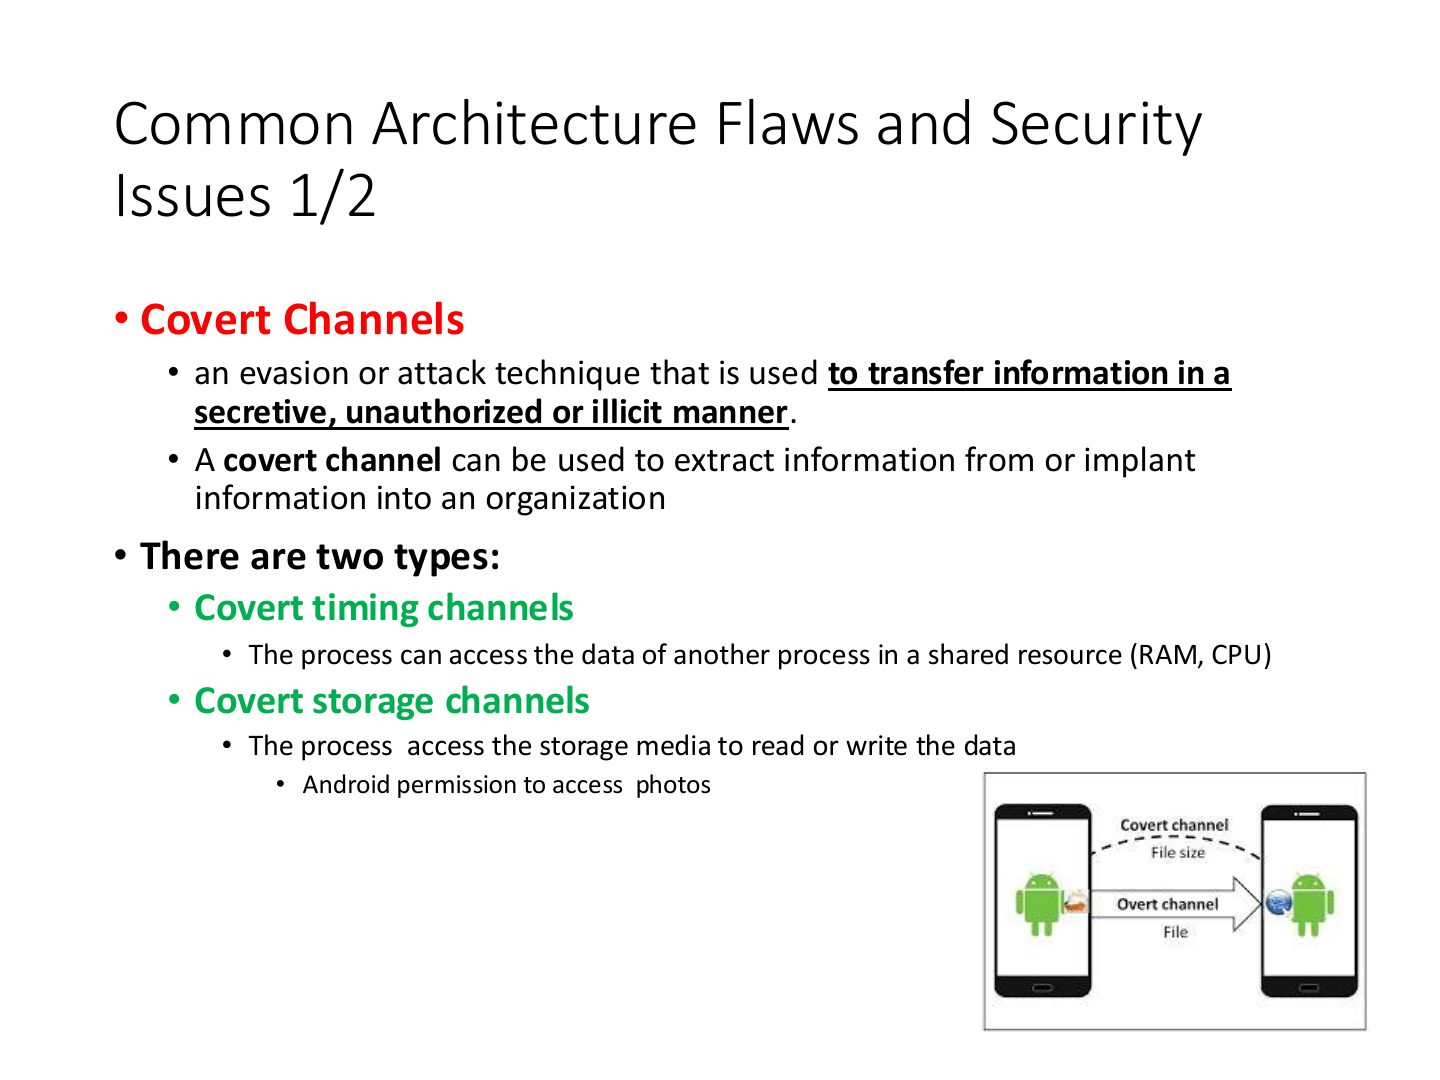
Notes
Covert channel: transferring information secretly through an unintended path (timing, storage).
Exam angle
Transferring information through an unintended, secret path is a:
Common Architecture Flaws and Security Issues 1/2
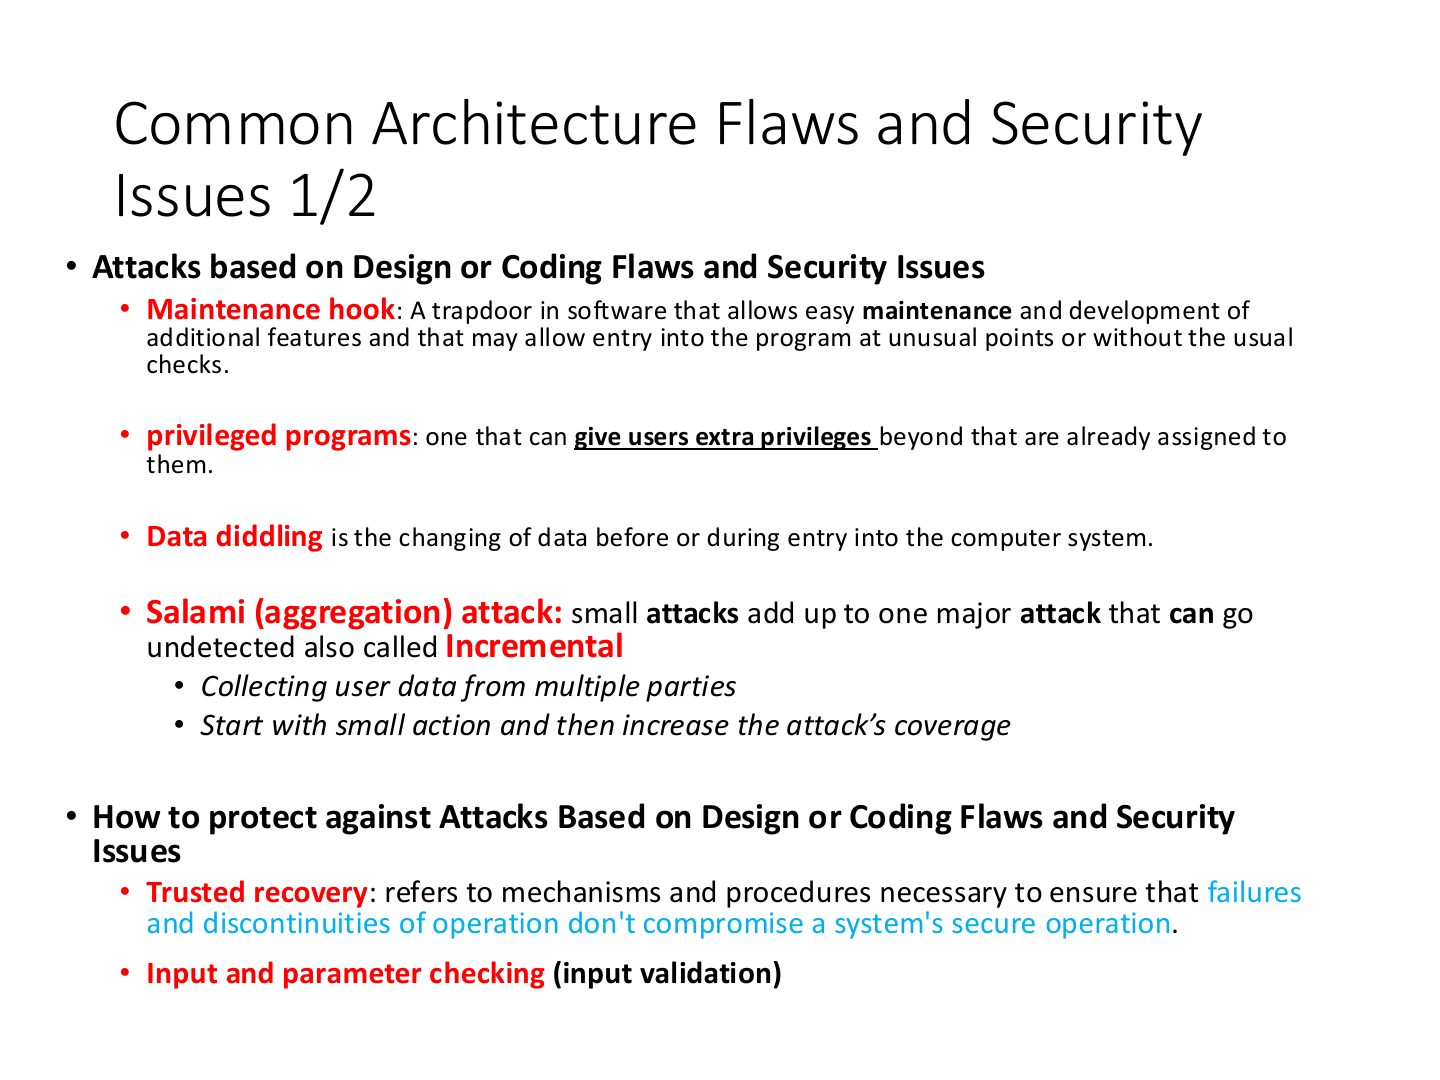
Notes
Maintenance hook (backdoor/trapdoor): a hidden entry point left by developers; also TOCTOU, buffer overflows.
Exam angle
A hidden entry point left in software for easy maintenance is a:
Techniques for Ensuring Confidentiality, Integrity, and Availability
Techniques for Ensuring Confidentiality, Integrity, and Availability
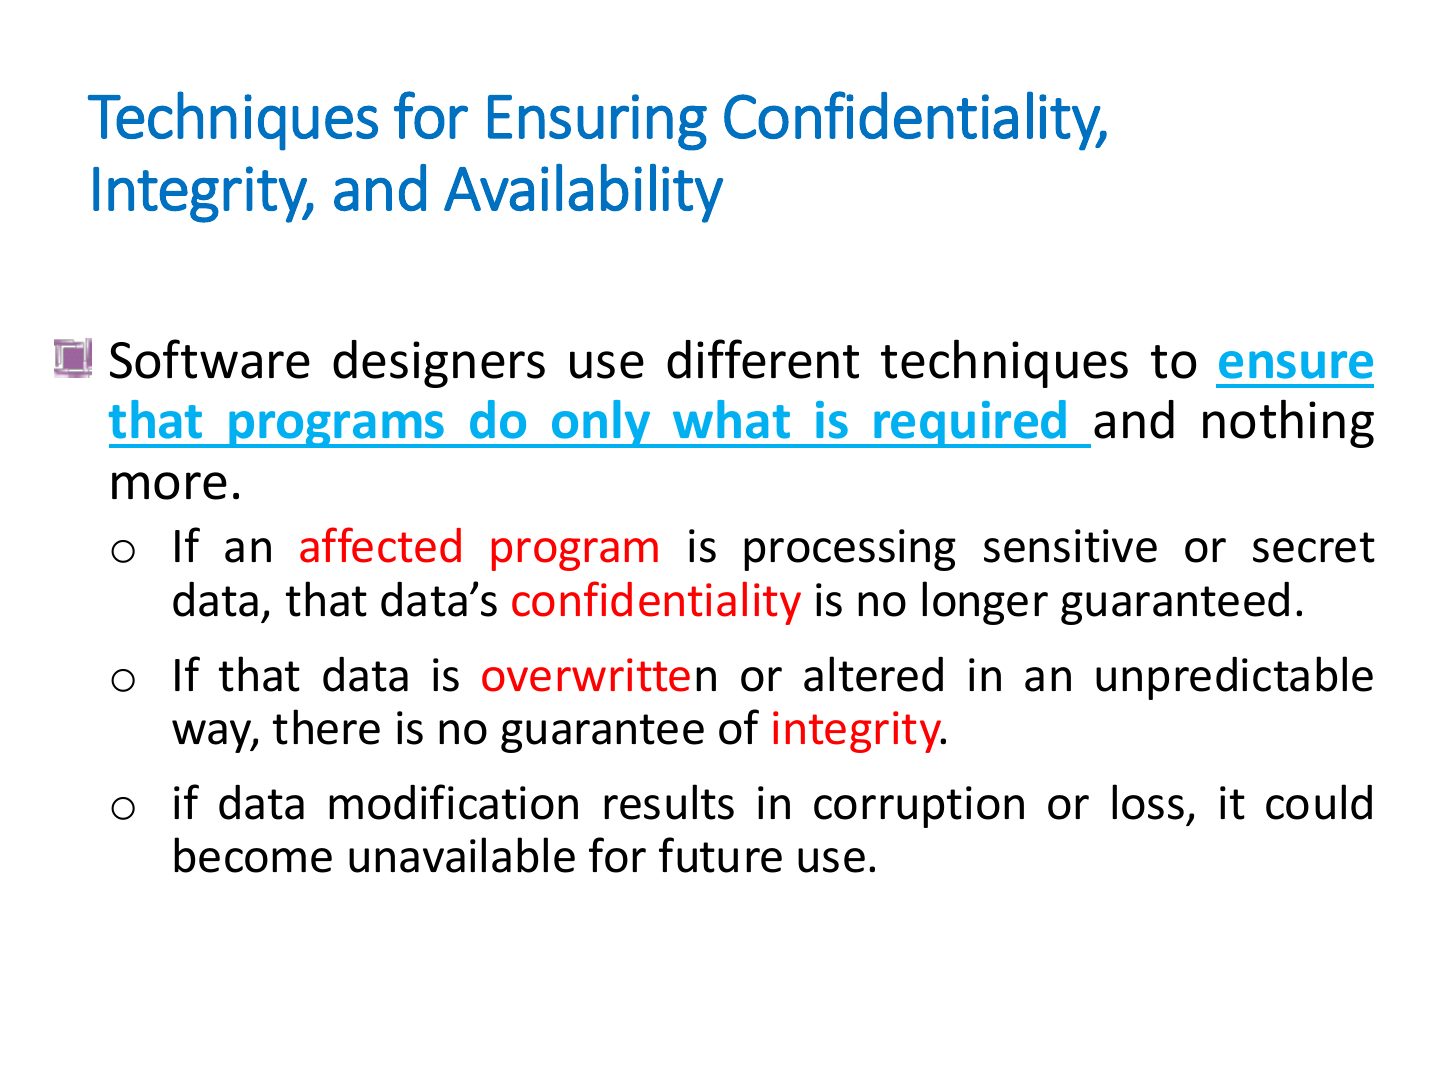
Techniques for Ensuring Confidentiality, Integrity, and Availability
Notes
Concepts: confinement, bounds, isolation, controls, trust and assurance.
Techniques for Ensuring Confidentiality, Integrity, and Availability
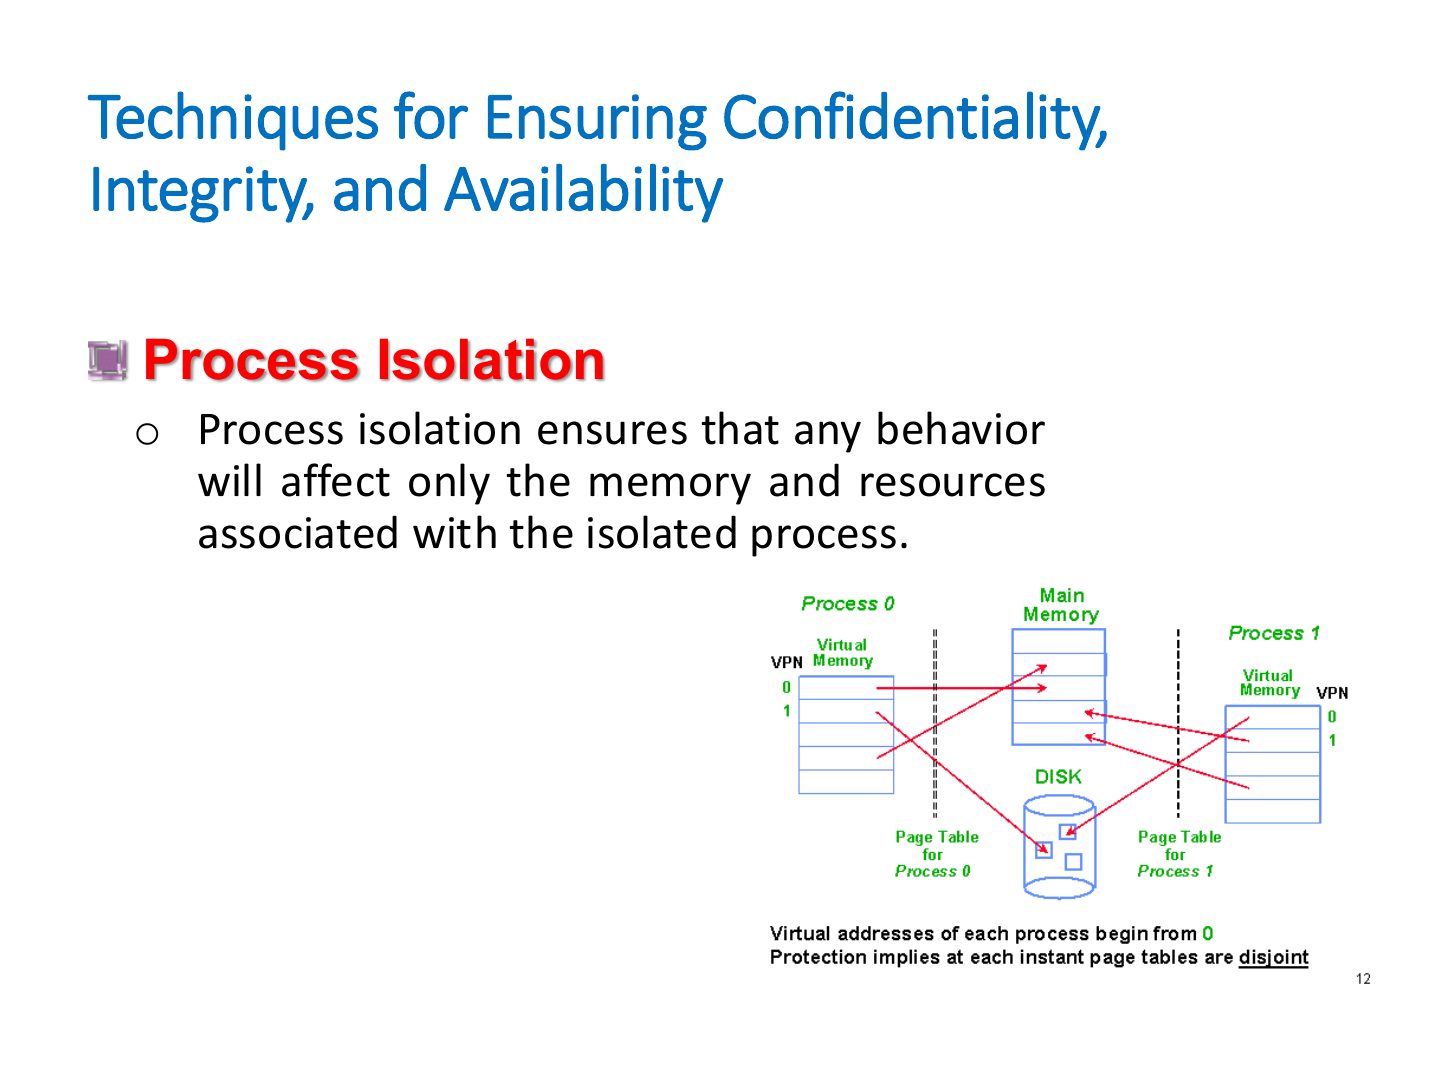
Notes
Process isolation: a process may only read and write its own memory locations and resources.
Exam angle
MCQ · process restricted to certain memory locations
Allowing a process to read and write only certain memory locations and resources is:
- Final 221 A.
Techniques for Ensuring Confidentiality, Integrity, and Availability
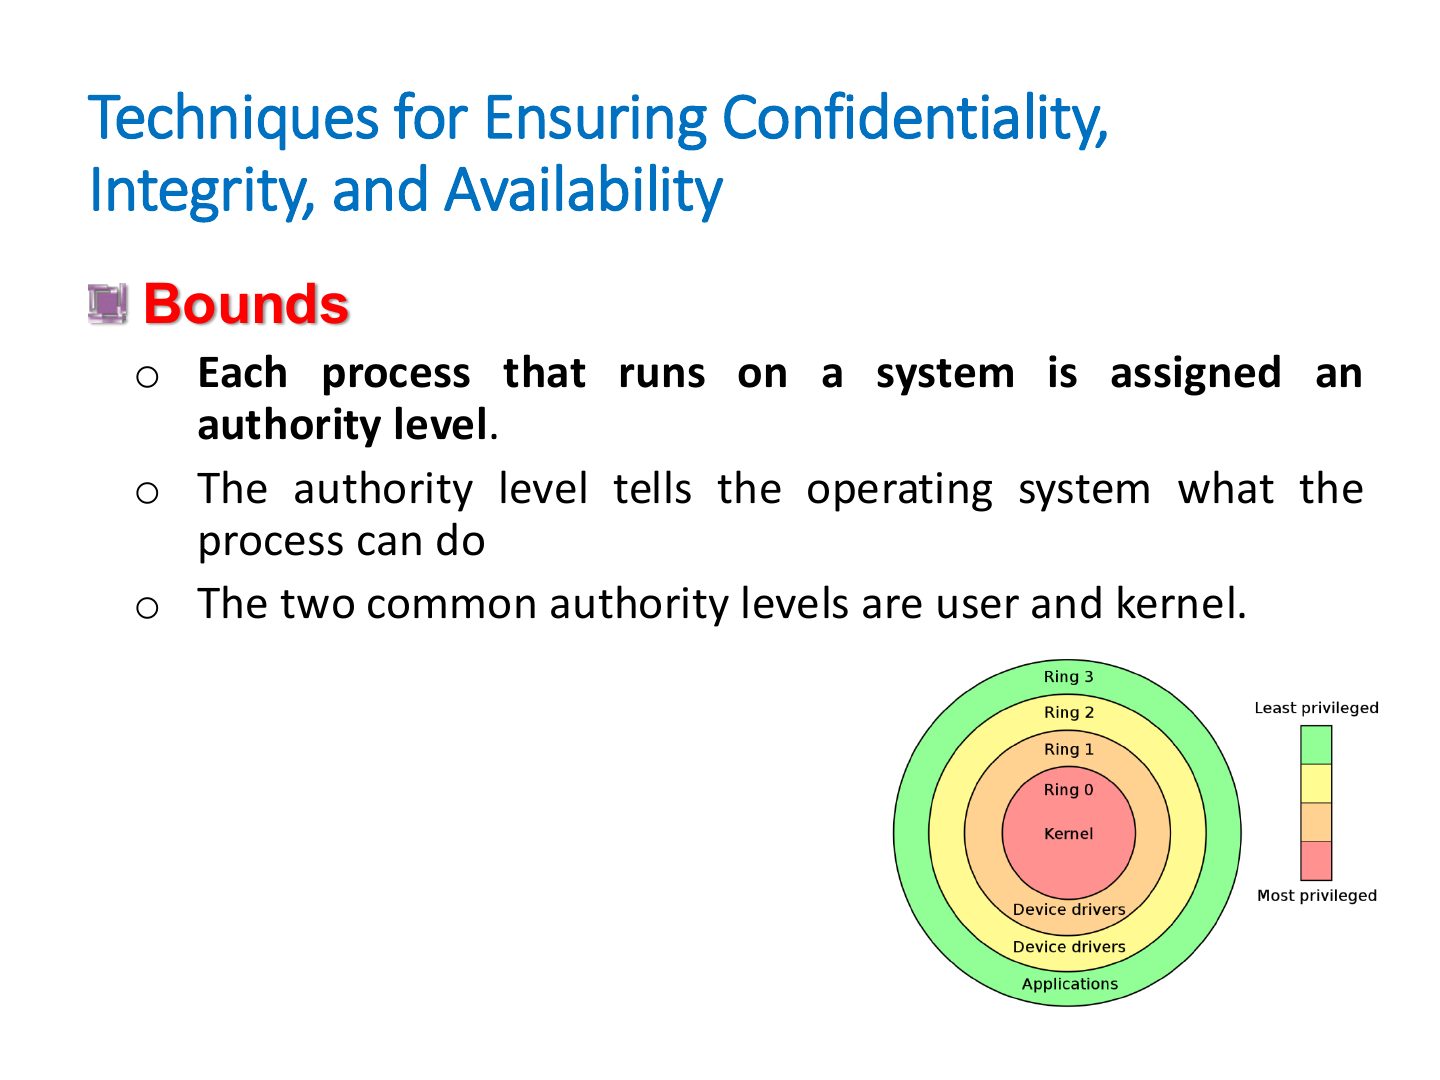
Notes
Each process gets an authority level (protection rings): ring 0 = kernel (most privileged); user processes run in outer rings.
Exam angle
MCQ · processes in ring 0 vs ring 3
MCQ · problem state = user mode
Processes in _ can access more resources and interact with the OS more directly than processes in _.
- Final 221 B.
Operating in the “problem state” means running in:
- Final 221 B.
Security Models
Security Models
Security Models
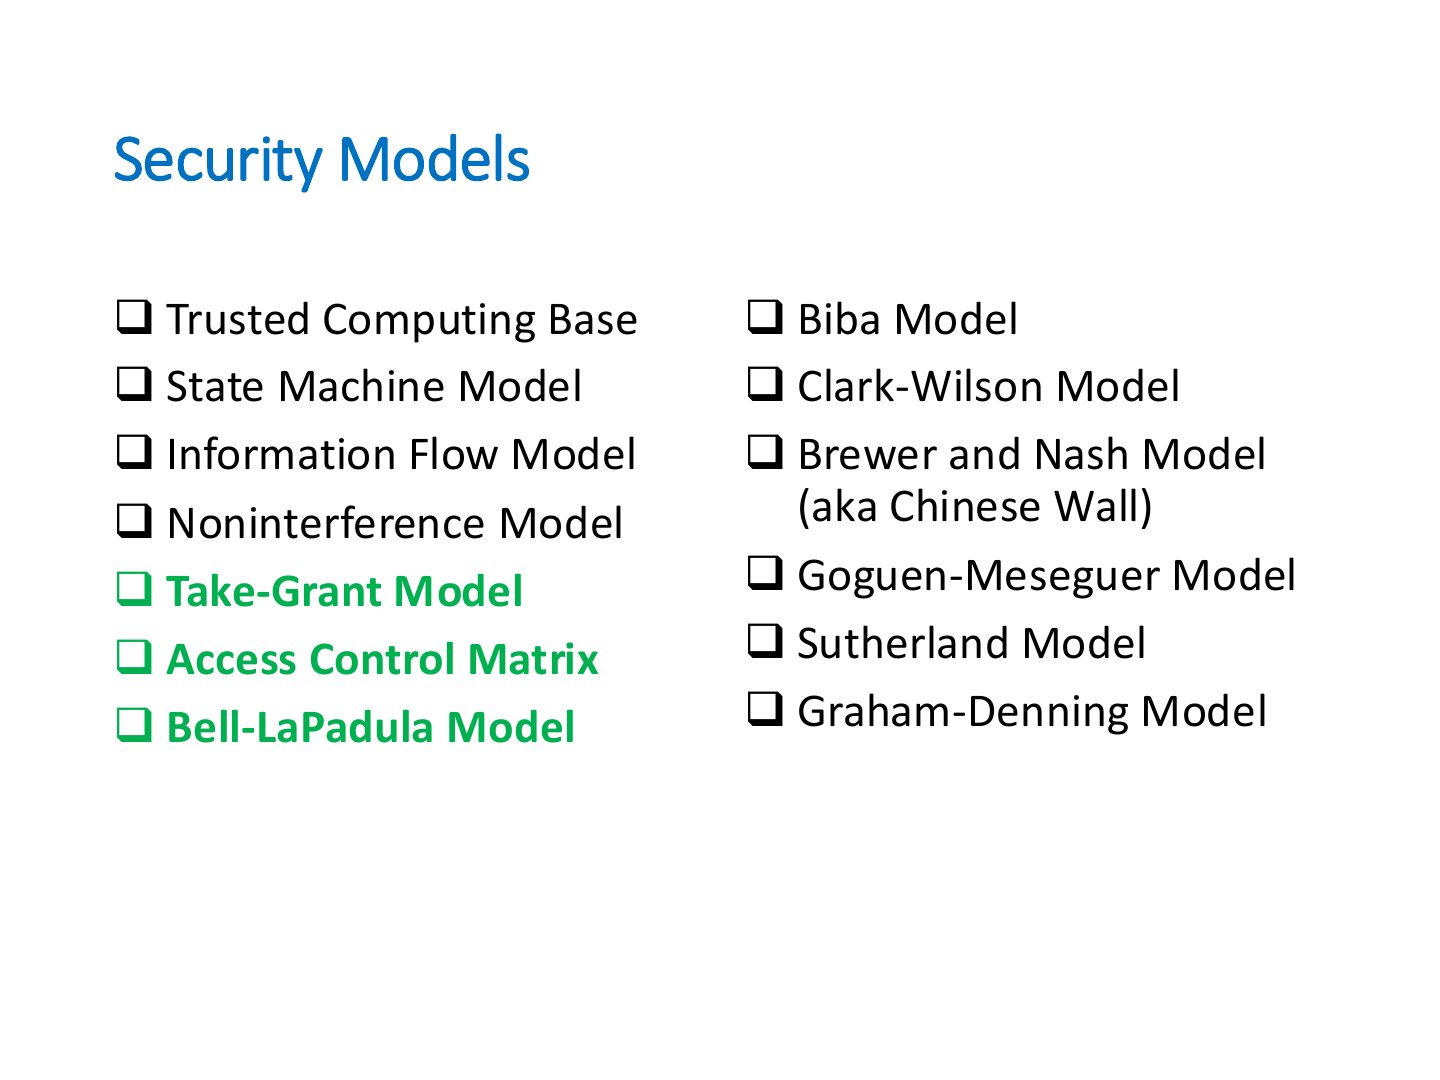
Exam angle
Related question: MCQ · conflict-of-interest model = Brewer-Nash
Which model prevents conflicts of interest (e.g., a consultant serving two competitors)?
- Final 221 B.
Access Control Matrix
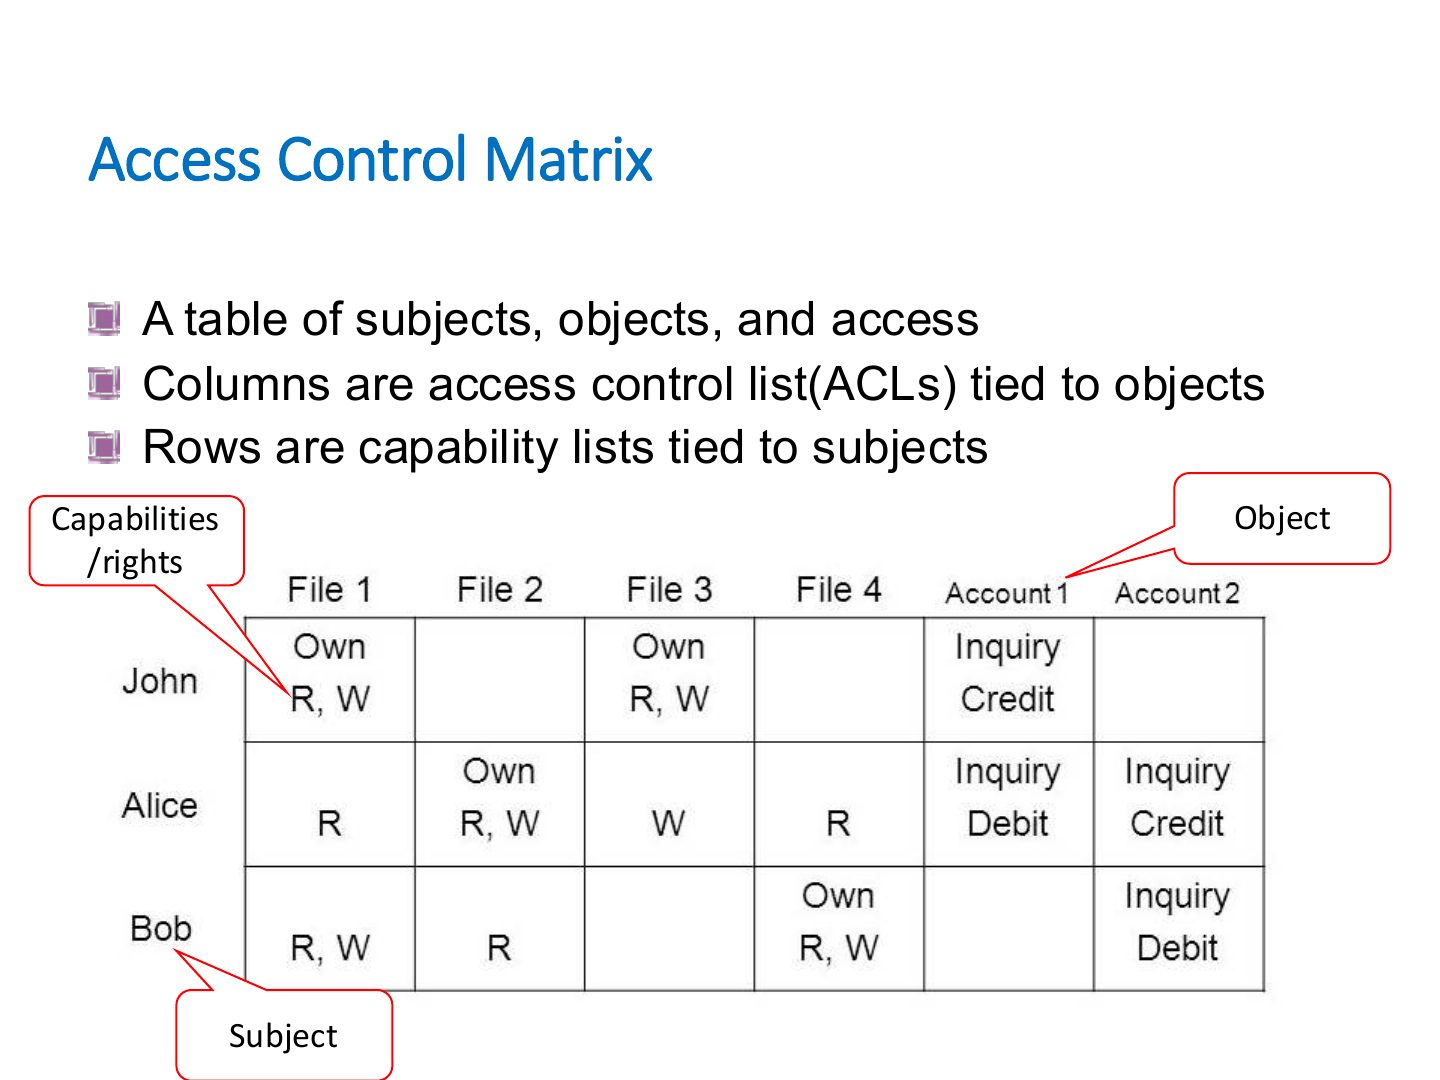
Exam angle
In an access control matrix, a column tied to an object is a(n):
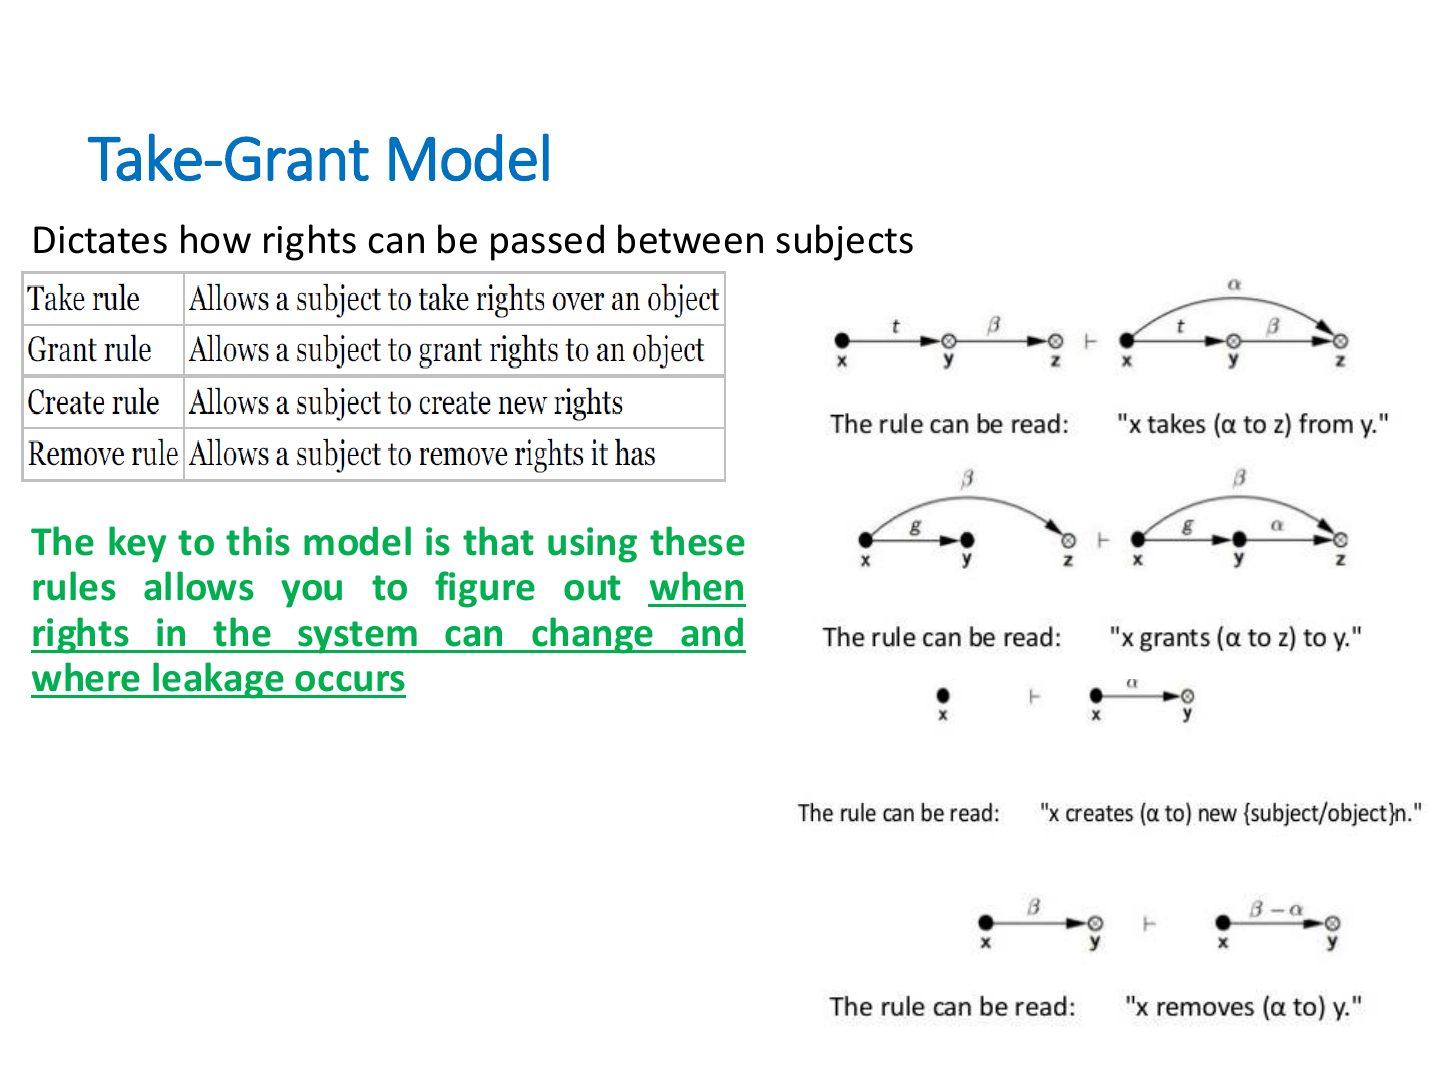
Take-Grant Model
Notes
Take-Grant: how rights pass between subjects (take, grant, create, remove); lets you find where rights can leak.
Exam angle
MCQ · model to find leakage of rights = take-grant
Which access-control model lets you reason about rights and find whether a leakage of rights can occur?
- Final 221 A.
Bell-LaPadula Confidential Model
Notes
Tip Bell-LaPadula (CONFIDENTIALITY): no read up (simple), no write down (*-property). Biba (INTEGRITY): no read down, no write up. Mnemonic: BLP protects secrets from leaking down; Biba stops dirt flowing up.
Exam angle
Bell-LaPadula question
Under Bell-LaPadula, a SECRET user may NOT:
- No read up.
Bell-LaPadula’s *-property forbids:
Biba Integrity Model
Notes
Tip Bell-LaPadula (CONFIDENTIALITY): no read up (simple), no write down (*-property). Biba (INTEGRITY): no read down, no write up. Mnemonic: BLP protects secrets from leaking down; Biba stops dirt flowing up.
Exam angle
The Biba model protects:
Slide 31
Notes
End.